#1

 silverhack/monkey365
基于 PowerShell 的 Microsoft 365、Azure 和 Entra ID 安全评估框架。扫描错误配置、CIS 基准合规性和云安全态势,并提供结构化报告。
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…

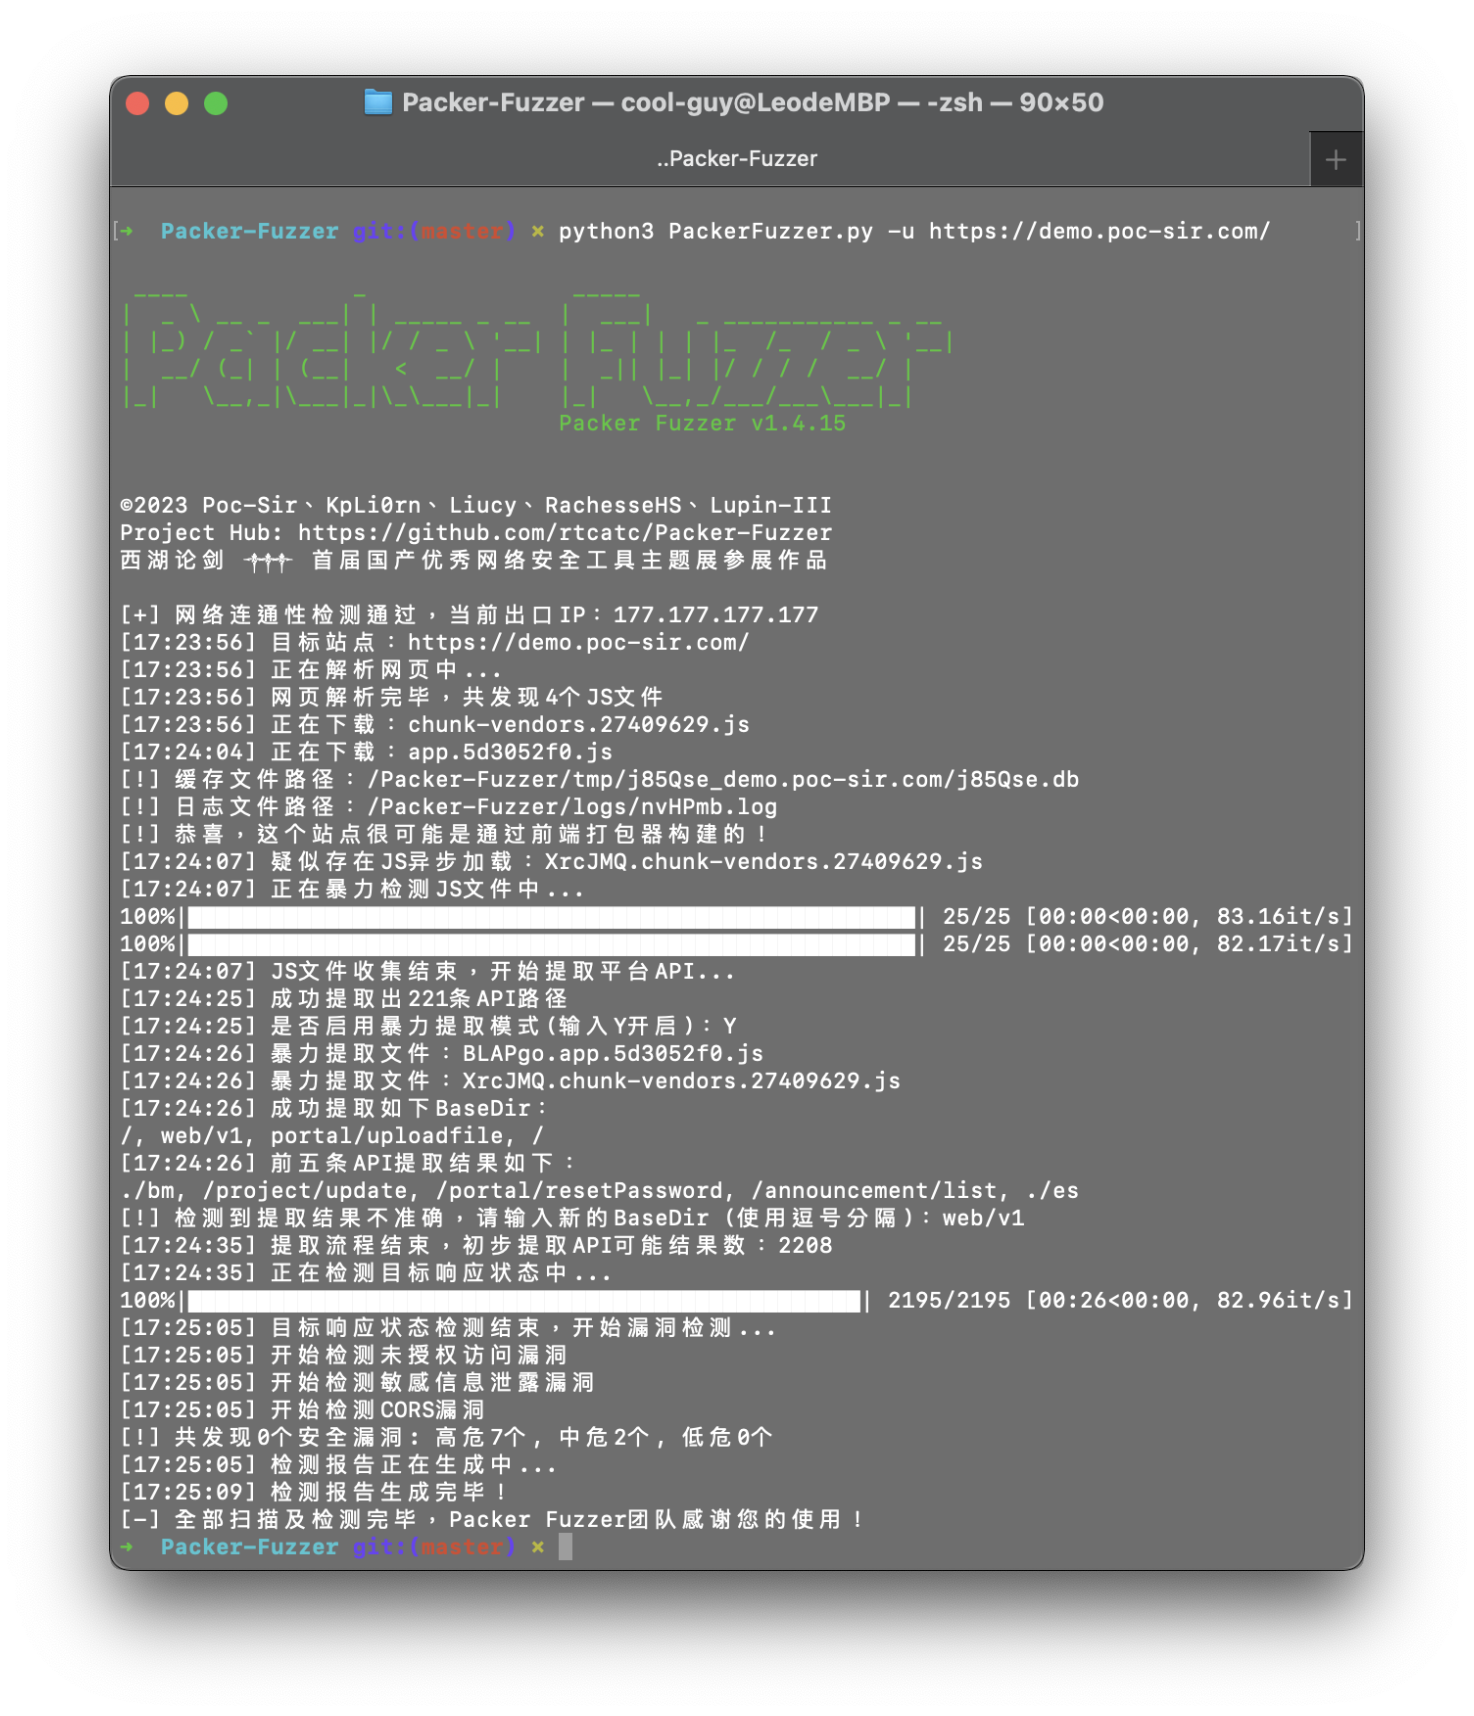 rtcatc/packer-fuzzer
Packer Fuzzer 是一个快速高效的扫描器,用于检测由 JavaScript 模块打包器(如 Webpack)构建的网站的安全性。
 swisskyrepo/graphqlmap
php7 和 php8 的安全模块 - 消除 bugclasses 并对其余部分进行虚拟补丁!
 aboutcode-org/vulnerablecode
开源漏洞数据库,聚合来自多个来源的CVE数据,提供Web界面和API。使用包URL(PURL)将漏洞映射到特定软件包,实现准确的依赖扫描。
 0sec-labs/0
Open-source cybersecurity harness to build and deploy sovereign, persistent AI security agents (sentinels) that continuously find, prove and fix…
 datadog/guarddog
🐍 🔍 GuardDog 是一个用于识别恶意 PyPI 和 npm 包的 CLI 工具
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 zegl/kube-score
Kubernetes 对象分析与改进可靠性和安全性的建议。kube-score 主动防止 Kubernetes YAML 和 Charts 中的停机与错误。用于 Kubernetes 的静态代码分析。
 securecodebox/securecodebox
Kubernetes原生安全扫描编排器,通过将多个开源扫描器集成到CI/CD管道中,自动化持续漏洞检测。

 protectai/ai-exploits
一个针对负责任披露漏洞的真实世界AI/ML利用集合。
 zaproxy/community-scripts
社区提供的 ZAP 脚本与技巧合集——非常欢迎提交 pull requests!