
 #1
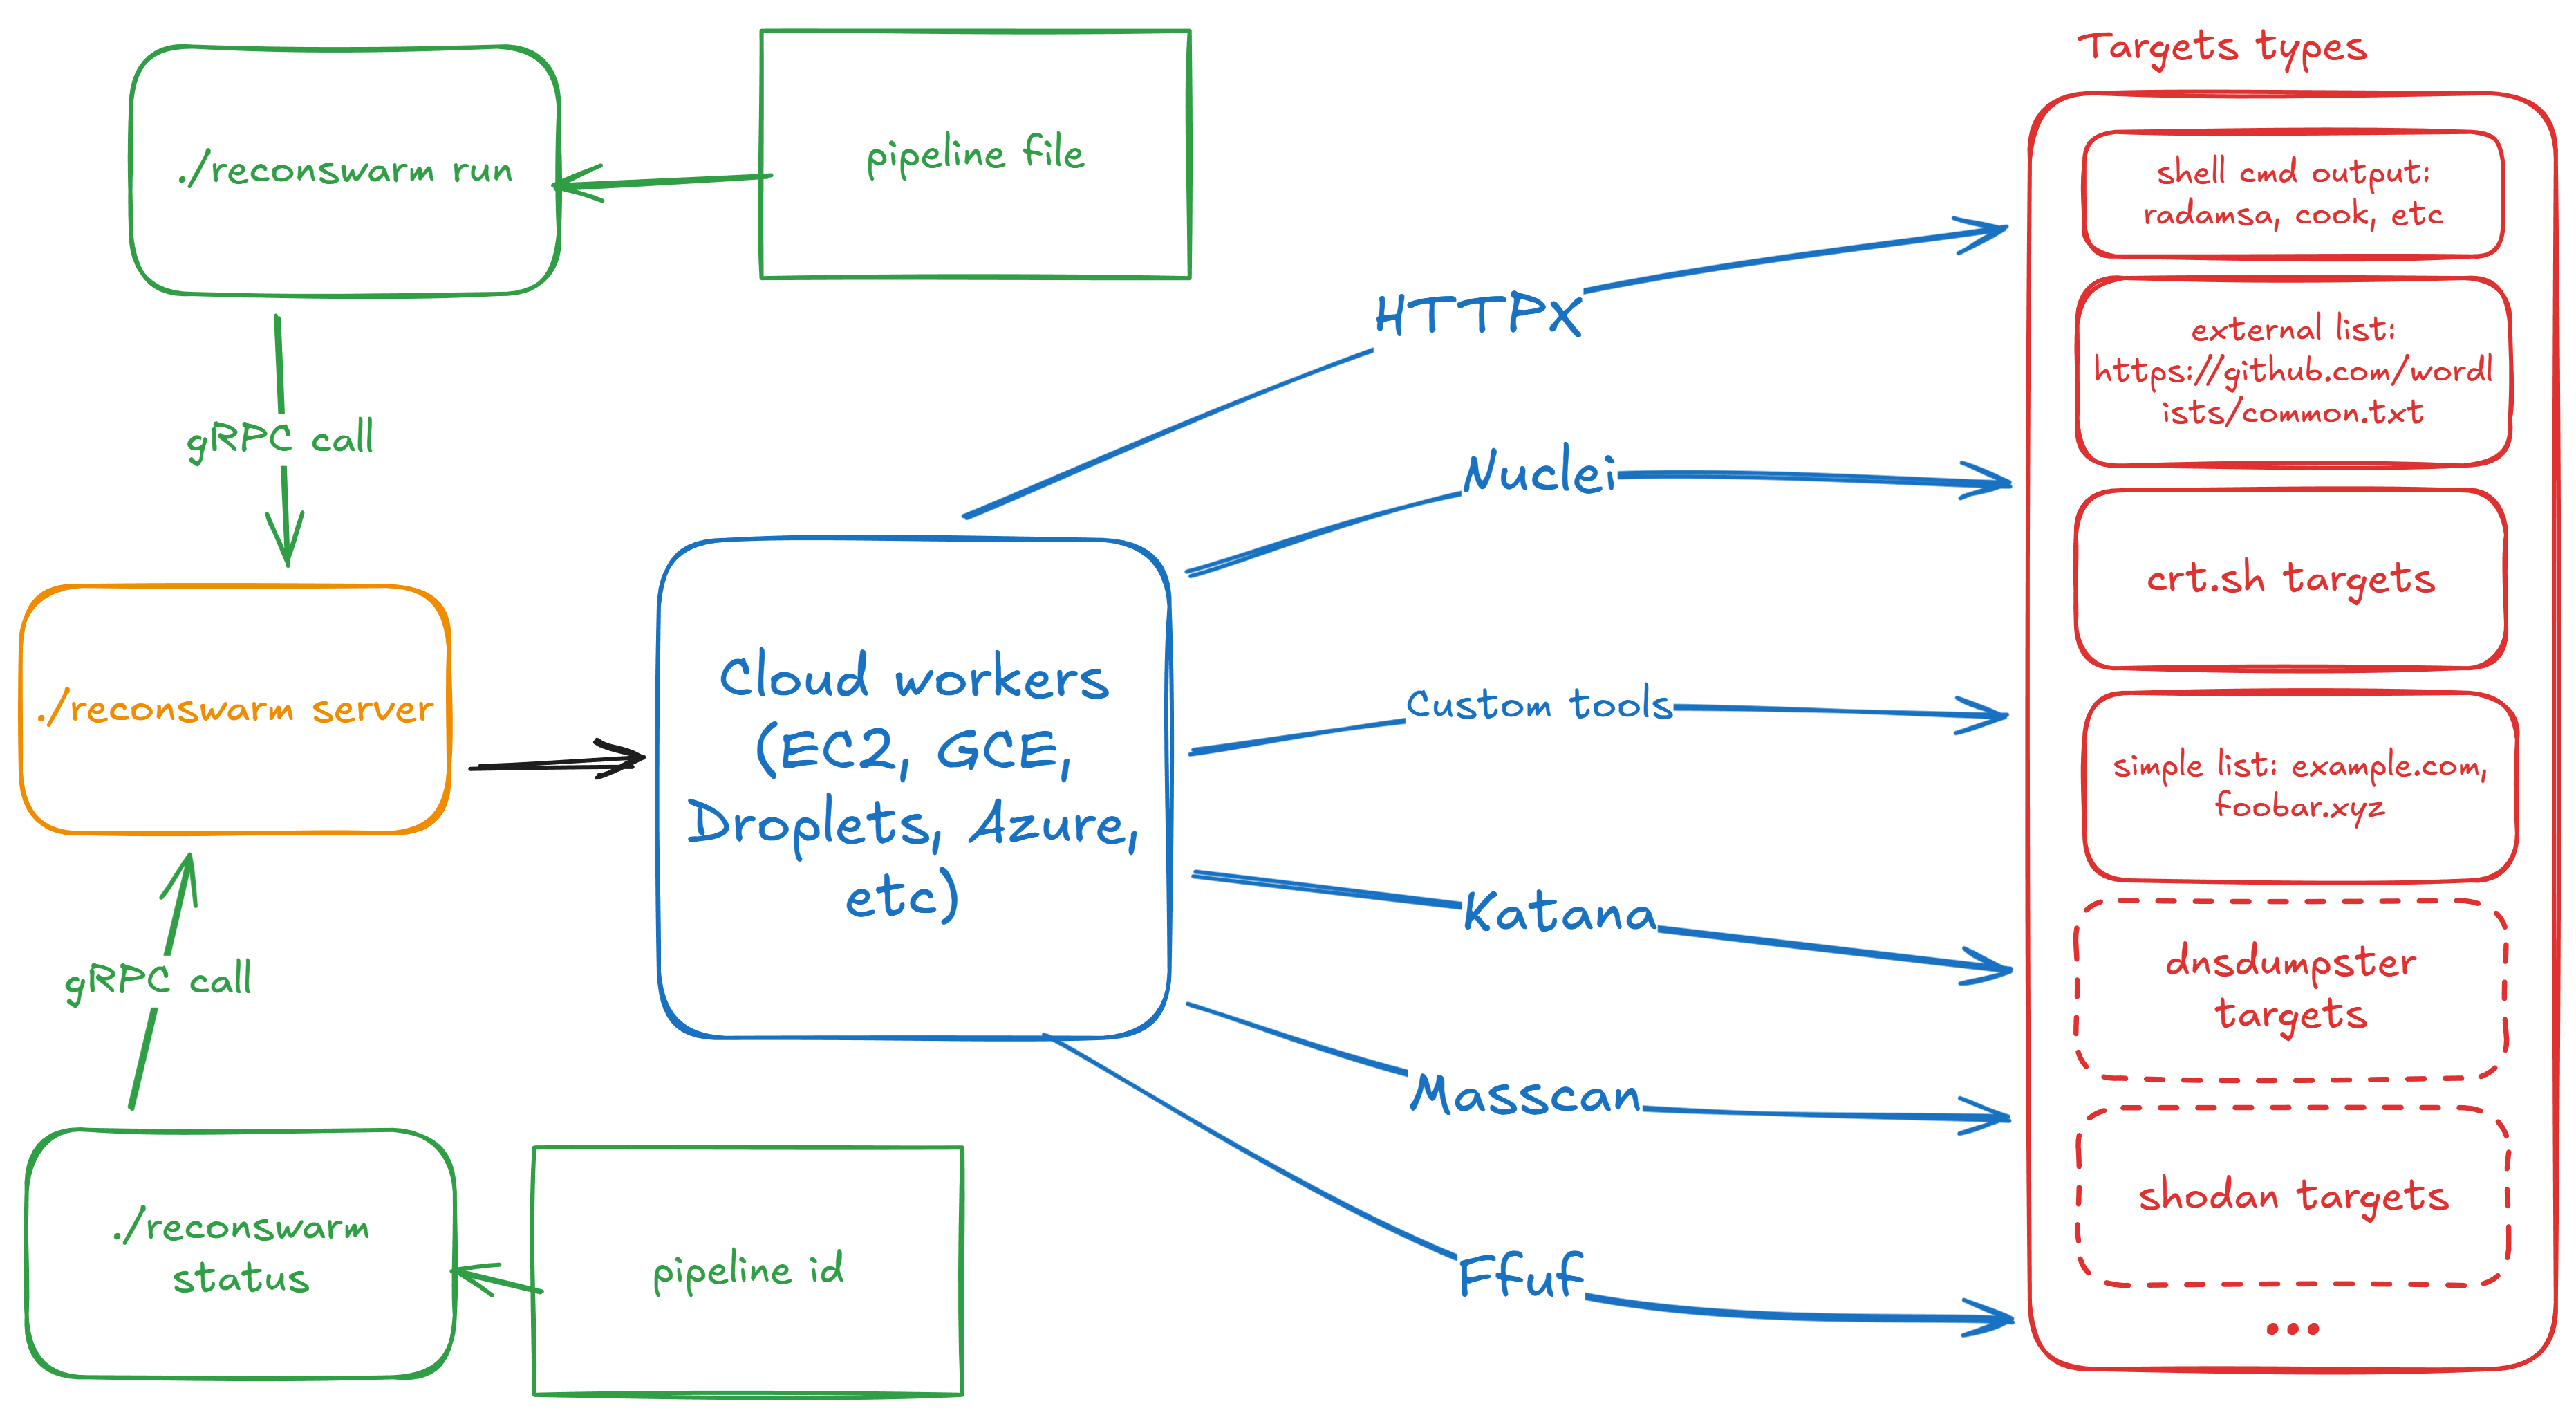
 renatus-cartesius/reconswarm
借助云的力量扩展您的侦察能力
 iulianvostrut/contexthound
静态分析CLI,用于扫描代码库中的LLM提示注入、数据泄露、越狱以及不安全的代理/工具漏洞。完全离线运行,集成CI/CD,并输出控制台、JSON和SARIF报告。
 codesource/copyfail-check
已归档,已迁移至 codesource/cve-check。用于检测 Linux 系统上 CVE-2026-31431(Copy Fail)暴露情况与缓解措施的 Shell 脚本:内核检查、模块状态、启动参数、AF_ALG 可达性以及发行版补丁状态。
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 heroku/heroku-cve-2013-0269
检查所有 Heroku 应用中的 JSON gem 是否存在易受攻击的版本

 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 moderneinc/rewrite-cve-2026-22732
OpenRewrite 配方,用于检测并修复 Spring Security 头信息抑制问题(CVE-2026-22732),通过识别 Content-Length 头信息的误用并生成主动写入头信息的配置。
 squid-protocol1/gitgalaxy
免 AST 的启发式知识图谱引擎,用于深度仓库智能分析和零信任安全扫描。可作为 GitLab CI/CD 组件集成,阻止恶意代码,并将 SARIF 遥测数据导出至 GitLab Security Dashboard。
 knqyf263/go-mal-pkgs
一款用于检测恶意 Go 包的安全工具,通过将 go.sum 中的校验和与原始源代码进行核对验证。
 g0dse11/detecttrace
开源检测工程工具,可端到端追踪安全检测并识别首个失败阶段。
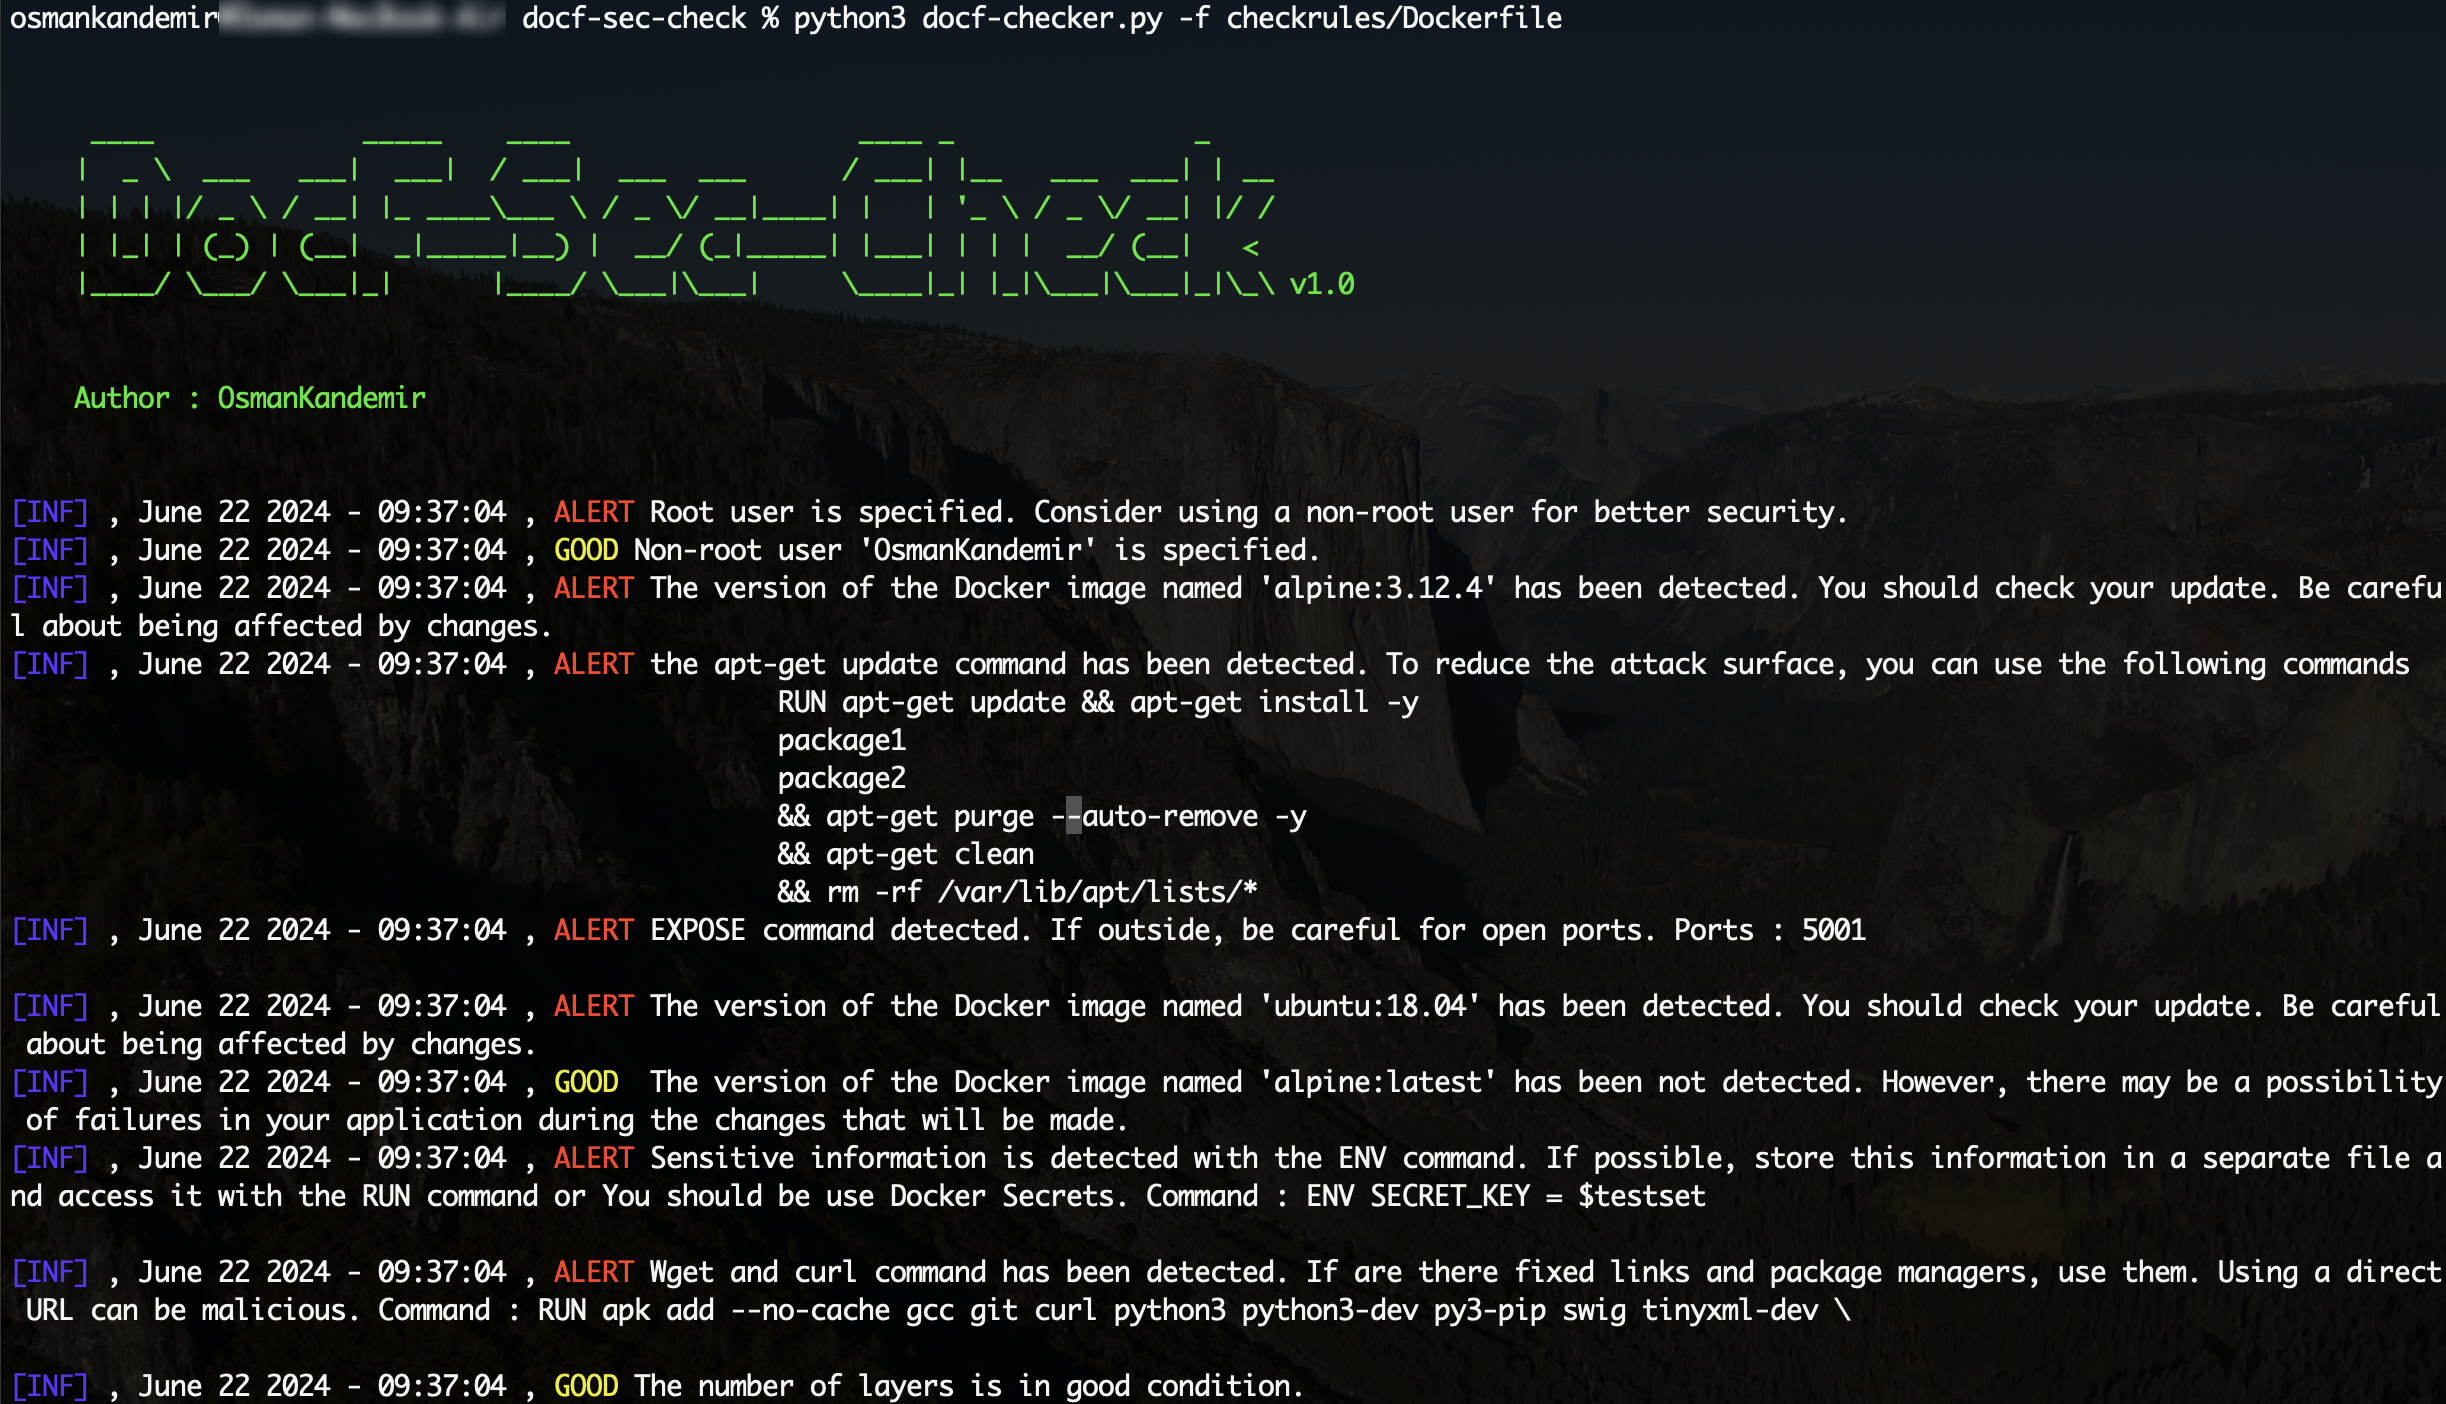 osmankandemir/docf-sec-check
静态分析工具,扫描Dockerfile中的不安全命令和配置问题,提供可操作的安全通知以强化容器构建。
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 aquasecurity/trivy-module-wordpress
用于 WordPress 的 Trivy 示例模块
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
该工具在F5 WAF上创建自定义签名集,并将其以阻断模式应用于策略。









