
 #1

 corazawaf/coraza
基于Go的Web应用防火墙库,兼容ModSecurity SecLang规则和OWASP核心规则集v4,提供实时HTTP流量检查和攻击阻断功能,适用于Web应用和API。
 kamalx06/xxeripper
黑盒XXE扫描器,通过统计基线、解析器指纹识别和OOB确认检测带内、基于错误和盲注带外注入,并支持SARIF输出。
 zjuicsr/actbench
Code for paper "ActBench: Self-Evolving Benchmark of Behavioral Safety in Cowork Agents"
 projectdiscovery/katana
下一代爬取与爬虫框架。
 hahwul/smugglex
基于 Rust 的 HTTP 请求走私扫描器。
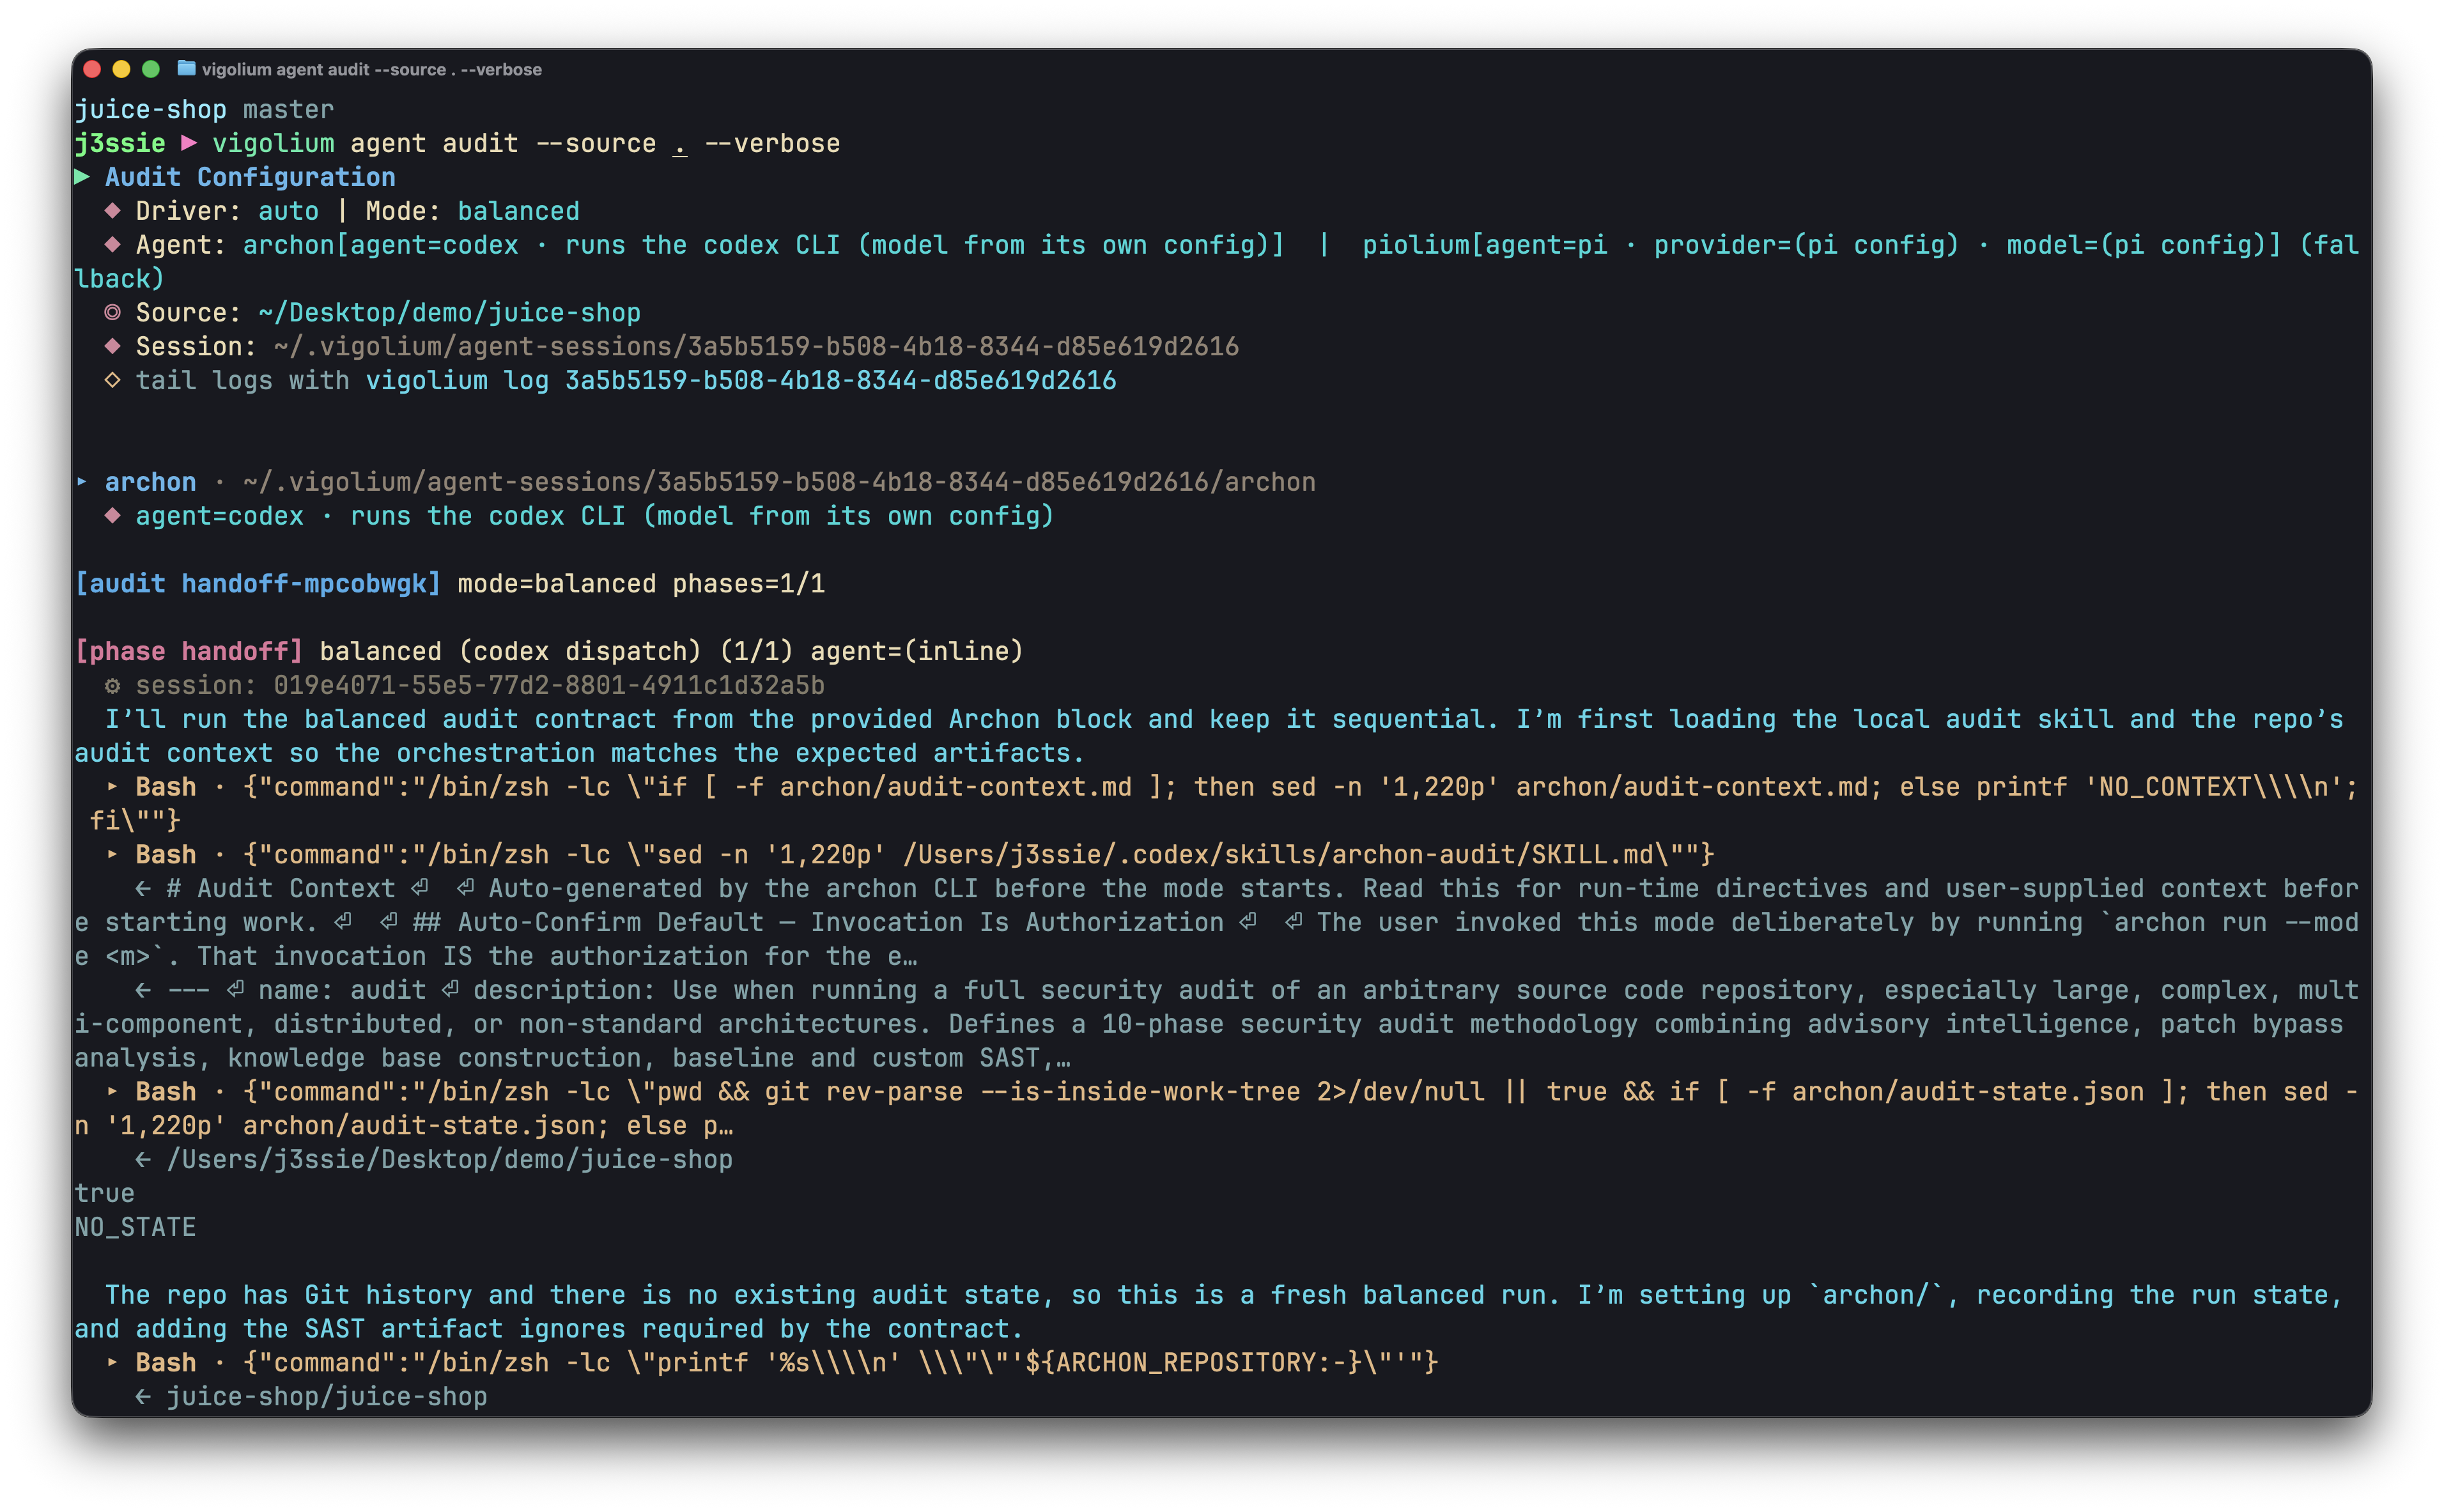 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 zaproxy/zaproxy
开源Web应用安全扫描器,支持自动化漏洞检测、手动渗透测试和API安全测试,并内置基于代理的拦截引擎。
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 wapiti-scanner/wapiti
使用 Python3 编写的 Web 漏洞扫描器
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 mda2av/http11probe
一个开放测试平台,可根据RFC 9110/9112要求、请求走私向量和畸形输入处理来探测HTTP/1.1服务器。添加您的框架,自动获得合规性结果。
 mozilla/firefox-devtools-mcp
用于 Firefox DevTools 的 Model Context Protocol 服务器 - 使 AI 助手能够通过 WebDriver BiDi 检查和操控 Firefox 浏览器
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
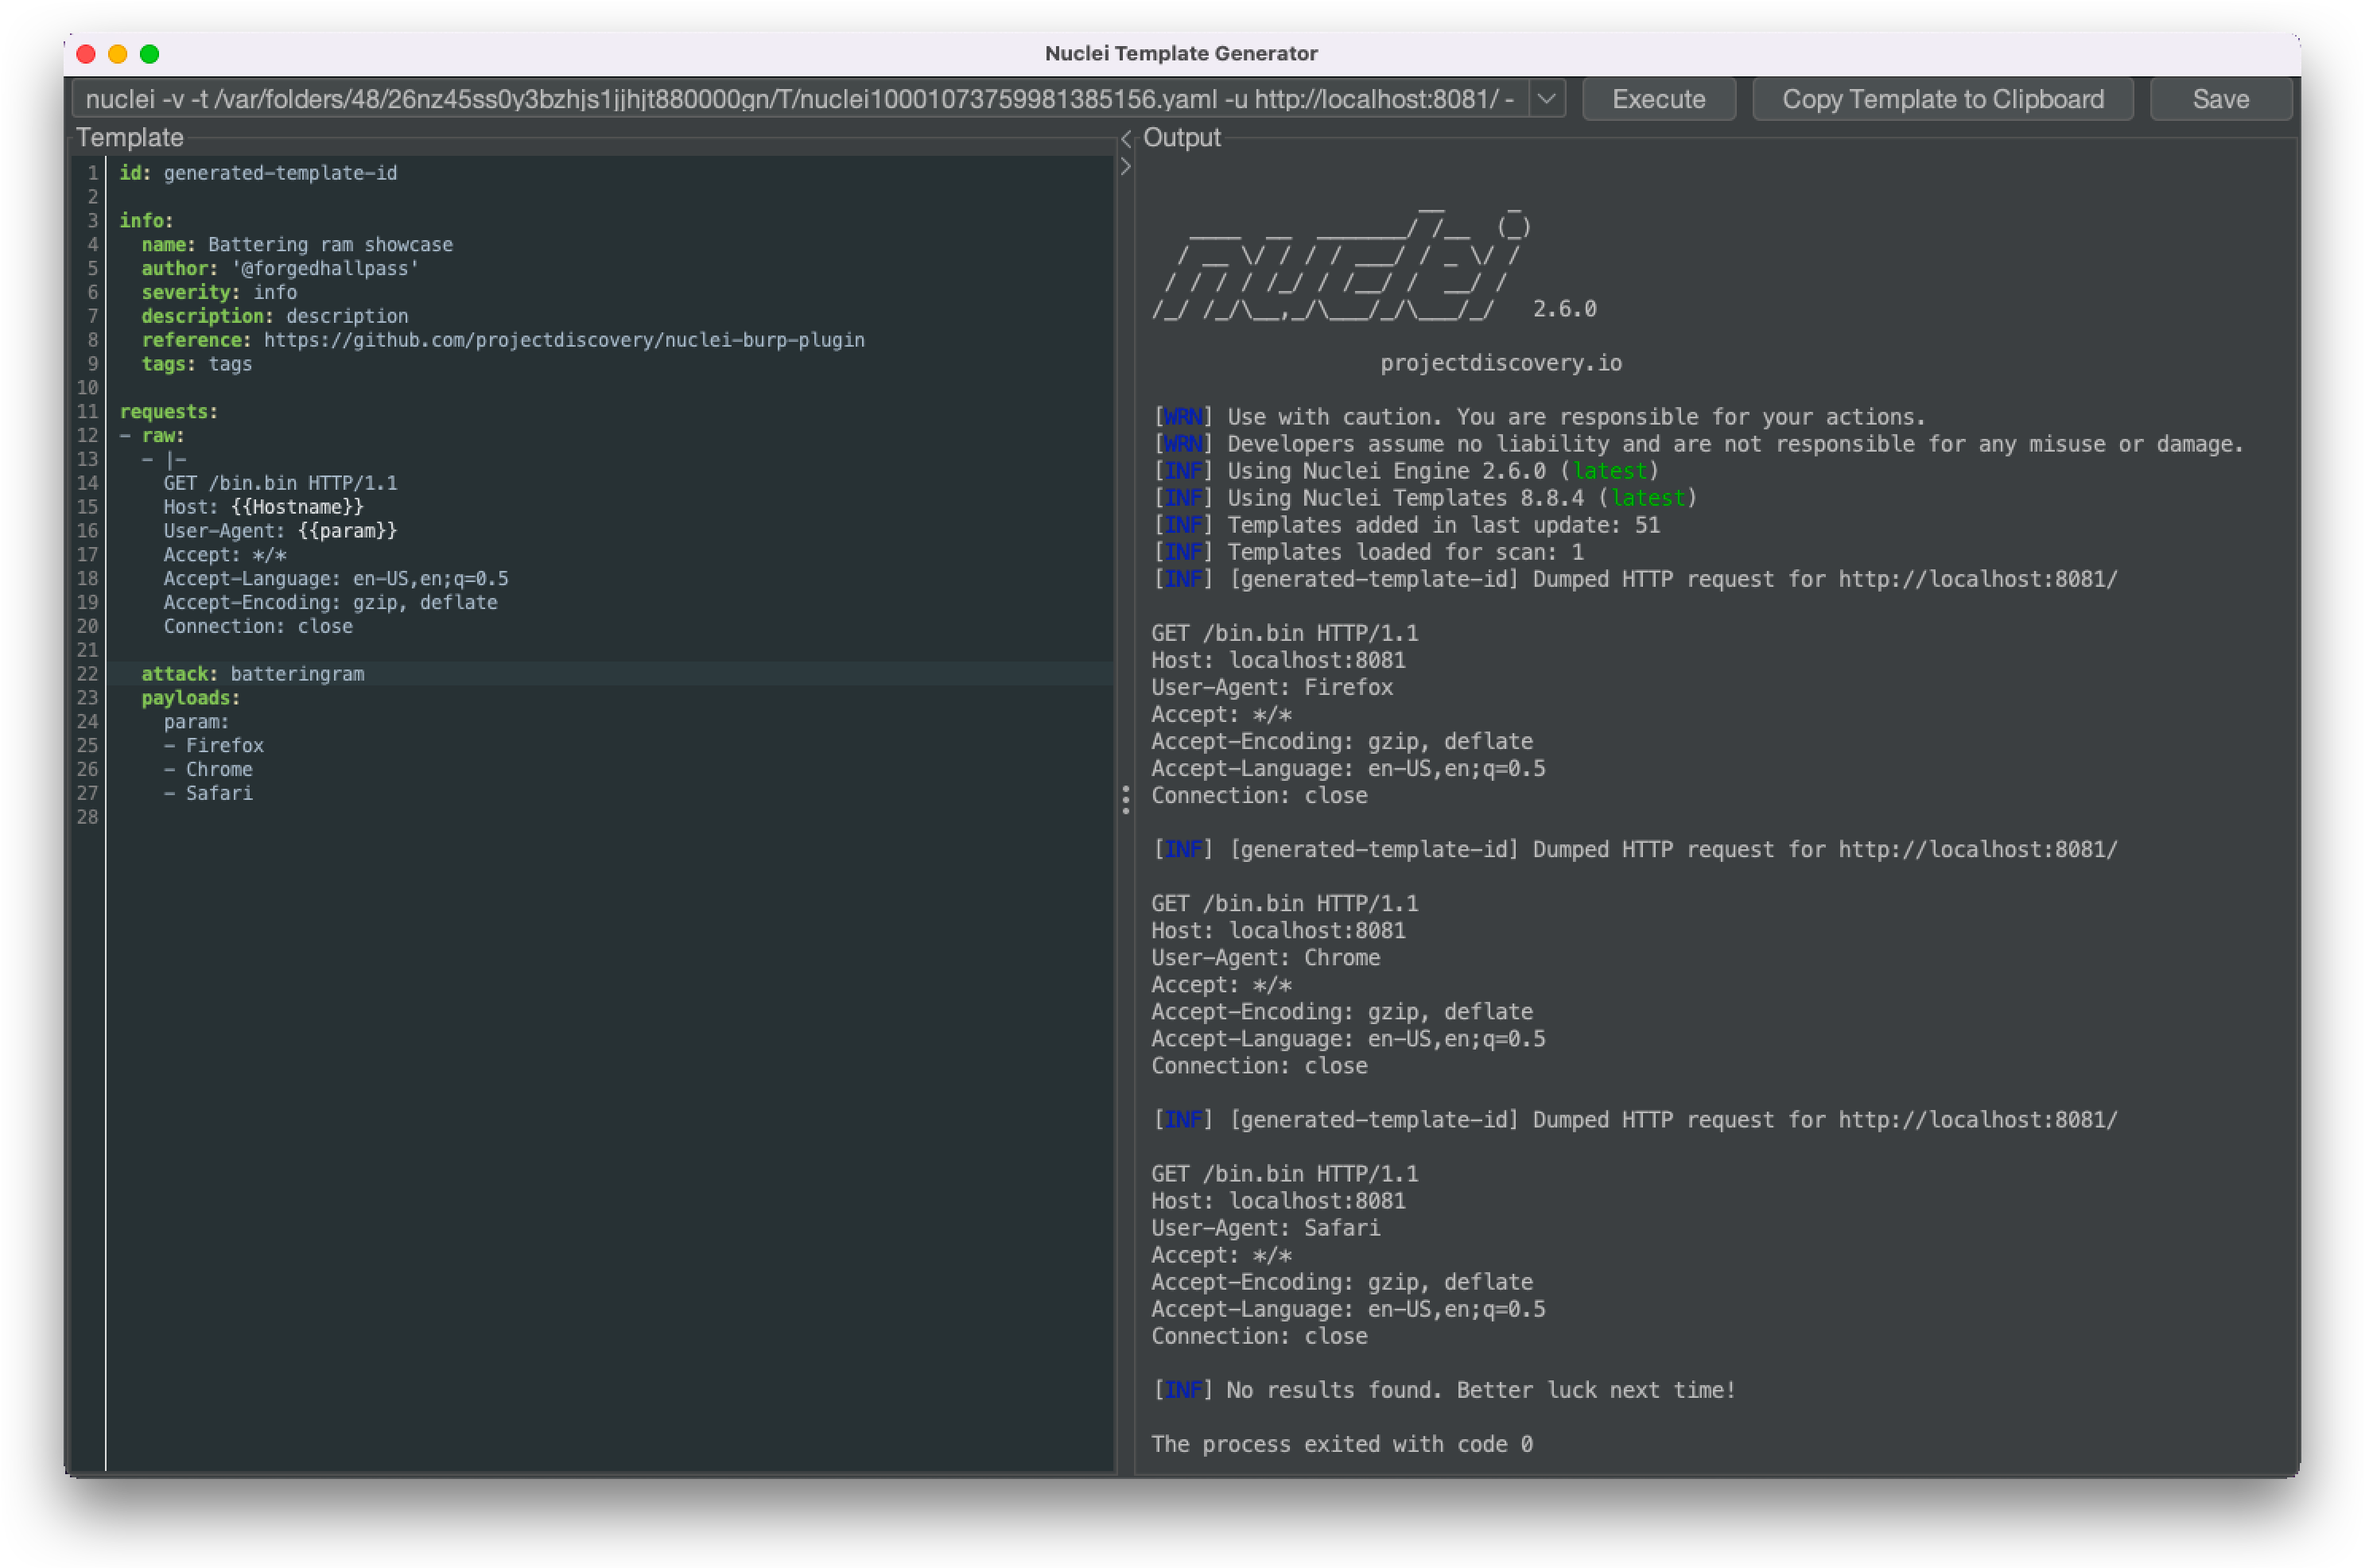 projectdiscovery/nuclei-burp-plugin
Burp Suite插件,用于直接从HTTP请求和响应生成并执行Nuclei漏洞模板,支持YAML自动补全和语法高亮。
 chaitin/safeline
自托管WAF和反向代理,可过滤恶意HTTP流量、阻止SQL注入、XSS和机器人攻击,具备速率限制和动态HTML/JS加密功能。
 forefy/reburp
一个将完整的 Montoya API 暴露为本地 REST API 的 Burp Suite 扩展,并带有 Swagger UI








