
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit 추천

 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 arkime/arkime
Arkime는 오픈 소스, 대규모, 전체 패킷 캡처, 인덱싱 및 데이터베이스 시스템입니다.
 ericzimmerman/kapefiles
이 저장소는 KAPE에서 사용할 수 있도록 커뮤니티에서 제작한 Targets 및 Modules를 모아두는 공간입니다.
wazuh/wazuh엔드포인트 및 클라우드 워크로드 전반의 위협 탐지, 로그 분석, 파일 무결성 모니터링, 취약점 평가 및 규정 준수 관리를 위한 오픈소스 XDR 및 SIEM 플랫폼입니다.
 aixisstudio/snitch
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps…
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 domainaware/parsedmarc
집계 및 포렌식 DMARC 보고서를 파싱하기 위한 Python 패키지 및 CLI
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard


 kunai-project/kunai
eBPF 기반의 Linux 보안 모니터 및 위협 헌터로, 시간 순서대로 정렬되고 컨테이너를 인식하는 이벤트를 제공하며, 인시던트 대응 및 포렌식 분석을 위한 온호스트 상관관계를 지원합니다.
 lore-hex/quill-router
안전한 LLM 프록시를 위한 TrustedRouter.com 저장소
 dobybaxter127/nimbus-vestige
클라우드 및 ID 사고 대응을 위한 포렌식 재구성 엔진
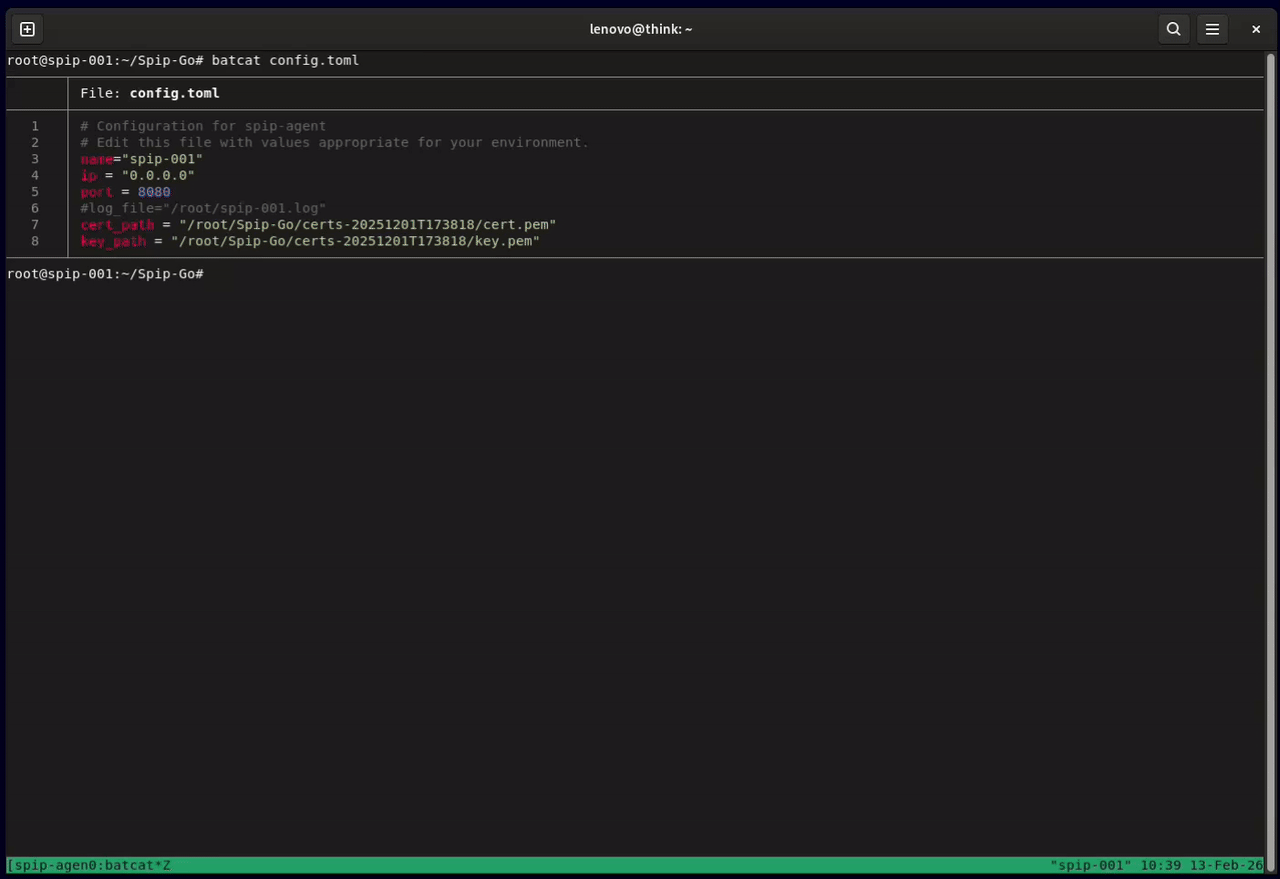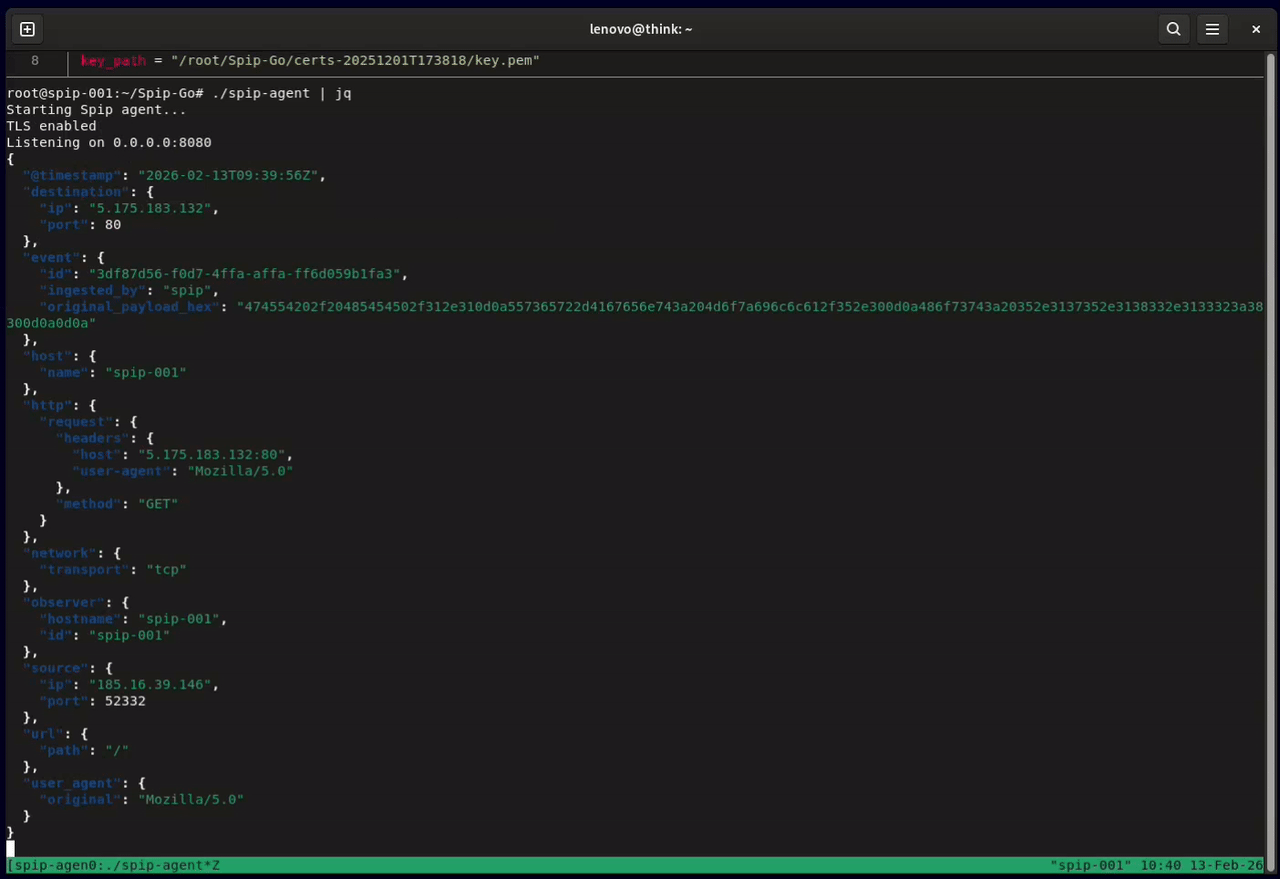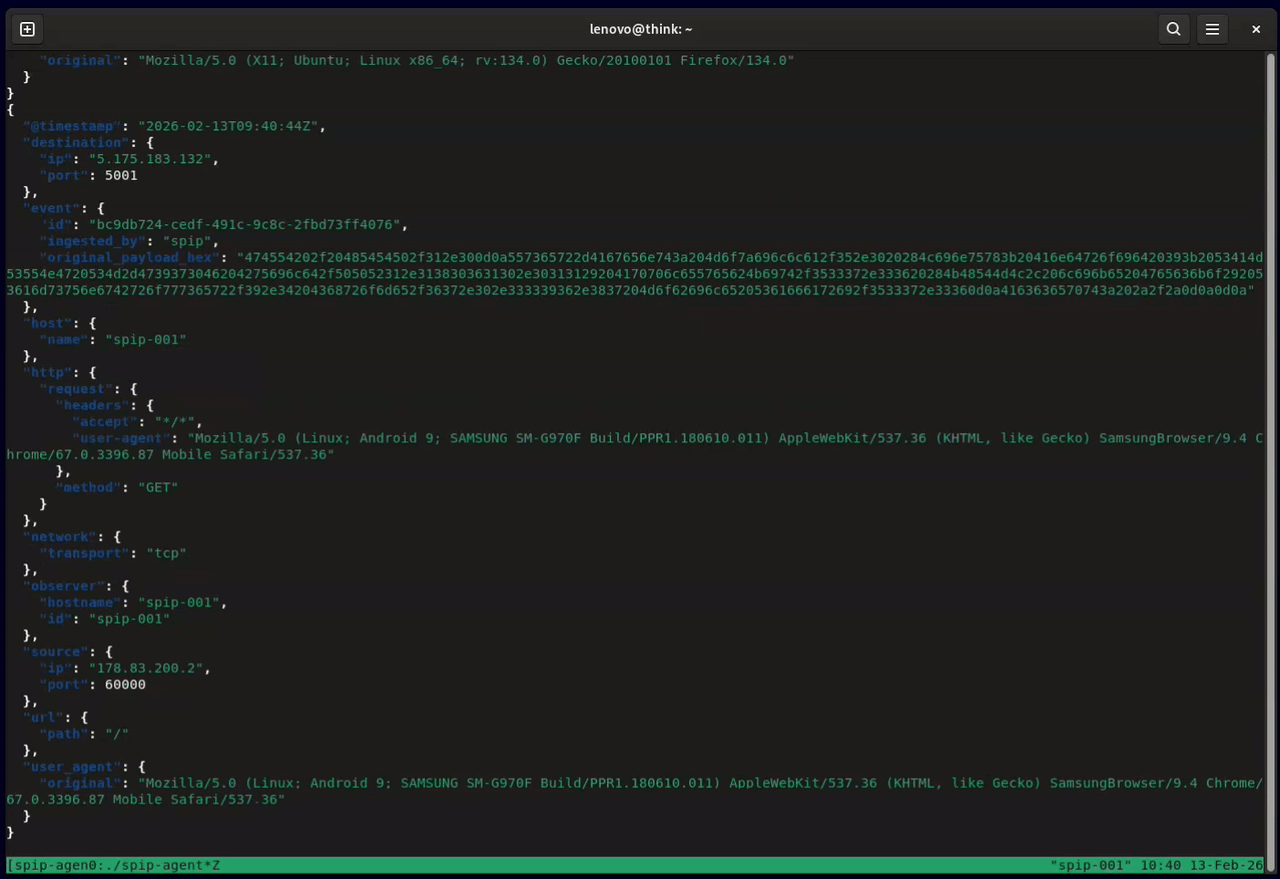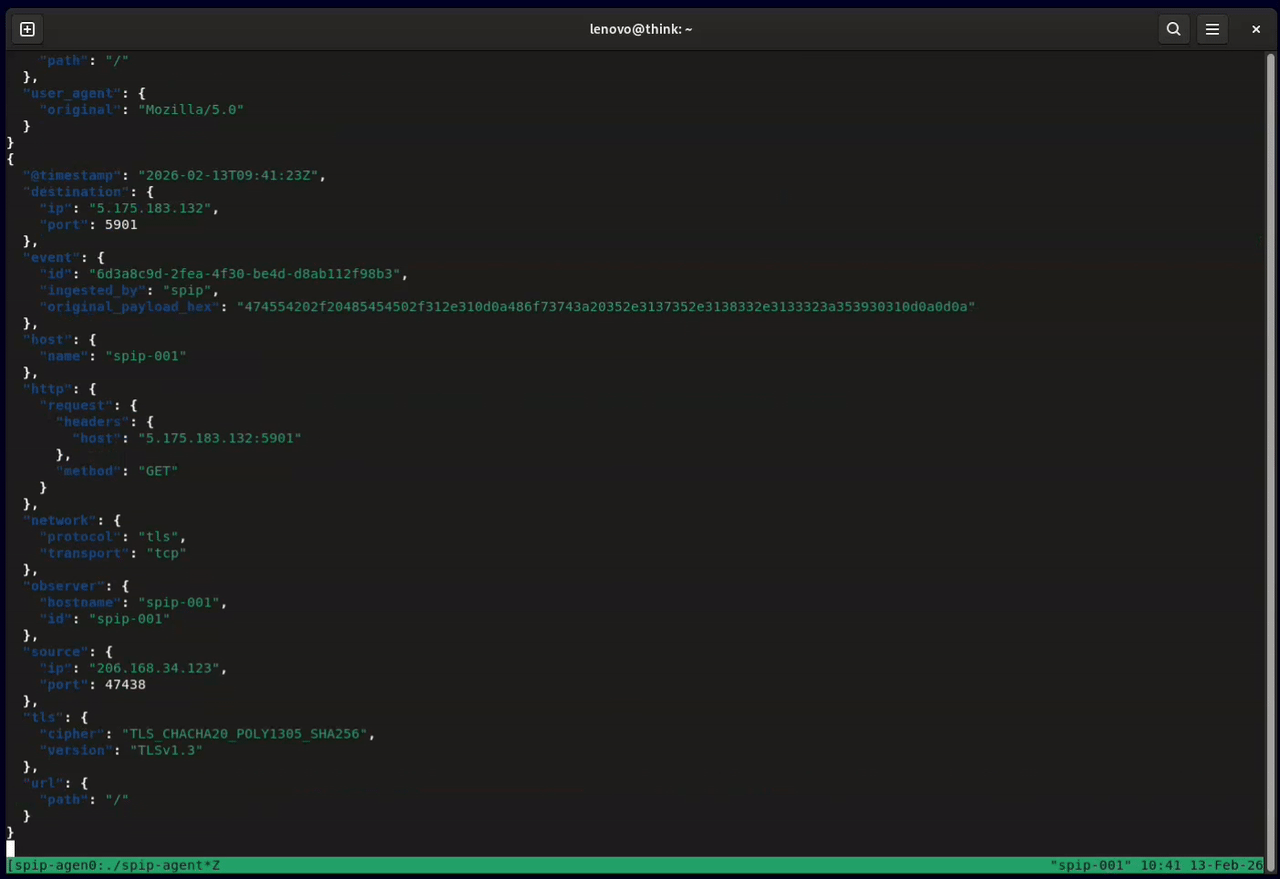 honeylabshq/spip-go
Spip network sensor written in Go
 mgreen27/detectraptor
공개적으로 사용 가능한 Velociraptor 탐지 콘텐츠를 공유하는 저장소








