
 #1
Security integration in CI/CD pipelines, shift-left, and DevOps security automation tools.
Kitploit 추천

 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.
aquasecurity/trivy컨테이너, Kubernetes, 코드 리포지토리, 클라우드 등에서 취약점, 잘못된 구성, 비밀, SBOM을 찾습니다.
 snyk/cli
Snyk CLI는 프로젝트의 보안 취약점을 스캔하고 모니터링합니다.
 microsoft/agent-governance-toolkit
자율 AI 에이전트를 위한 정책 시행, 제로 트러스트 신원, 실행 샌드박싱 및 감사 로깅. OWASP Agentic Top 10의 10/10을 결정론적이고 실패 시 폐쇄(fail-closed) 거버넌스로 포괄합니다.
 sheeki03/tirith
개발자와 AI 에이전트를 위한 터미널 보안. 호모그래프 URL, 파이프-투-셸, ANSI 인젝션, 난독화된 페이로드, 데이터 유출, 악성 AI 스킬/구성(config)이 실행되기 전에 차단합니다.
 mobsf/mobile-security-framework-mobsf
Android, iOS, Windows용 자동화된 모바일 애플리케이션 보안 테스트 프레임워크입니다. 정적 및 동적 분석, 멀웨어 탐지, CI/CD 통합을 통한 API 보안 테스트를 수행합니다.
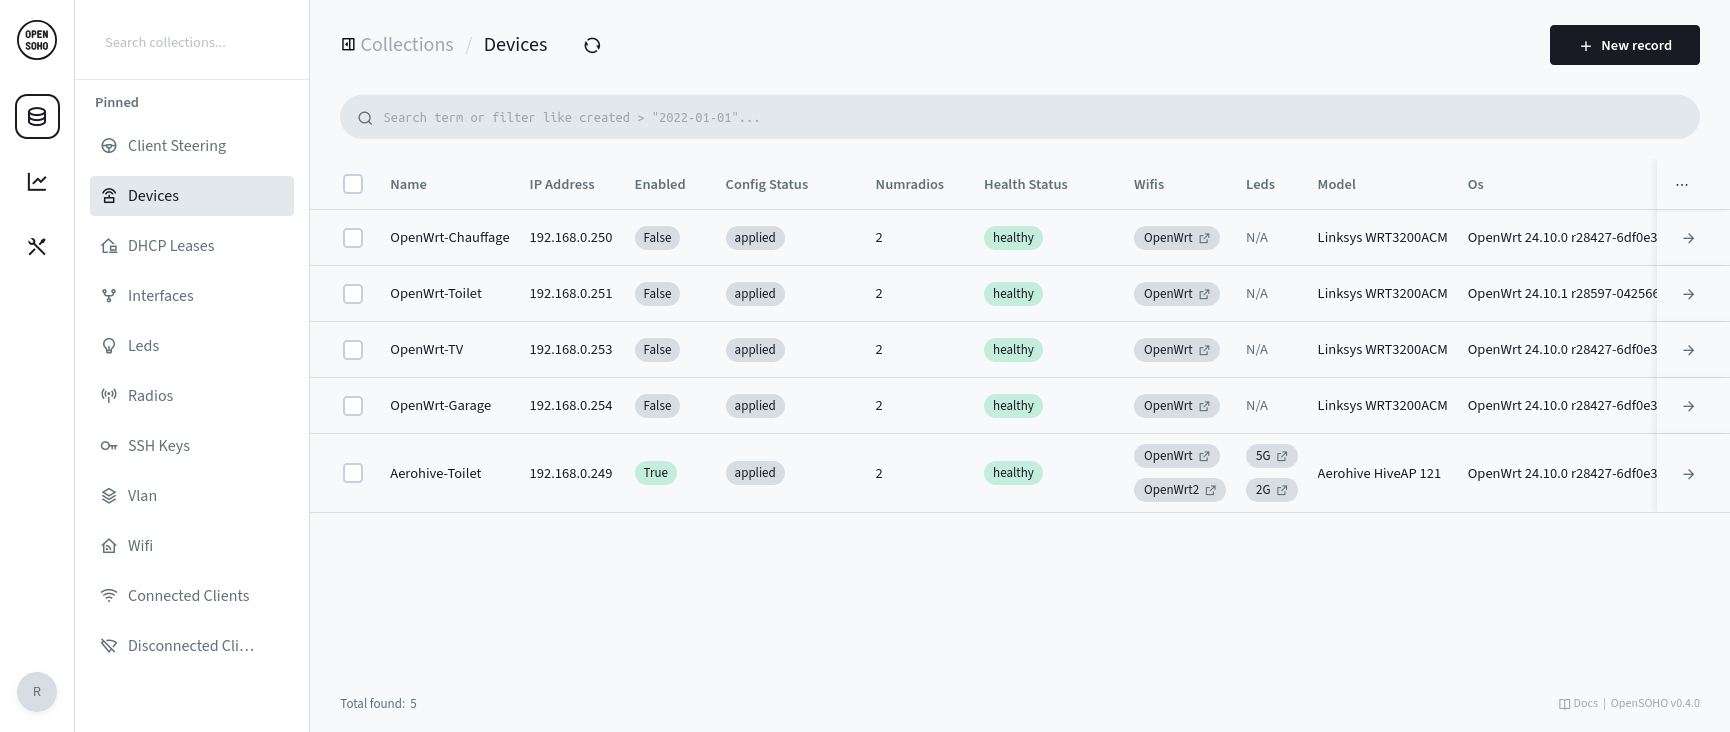 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 future-architect/vuls
에이전트 없는 취약점 스캐너: Linux, FreeBSD, 컨테이너, WordPress, 프로그래밍 언어 라이브러리, 네트워크 장치 지원
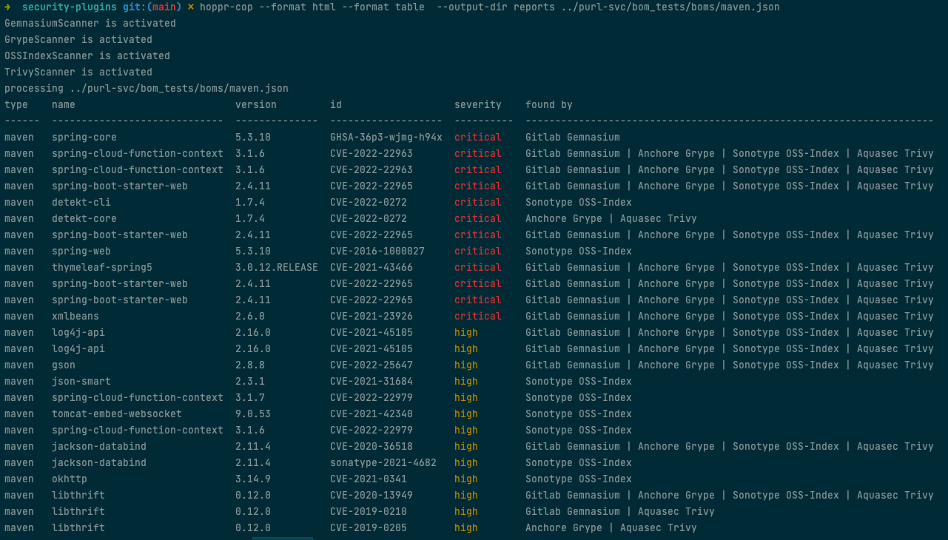
 hoppr/hoppr-cop
여러 데이터베이스의 취약점 데이터를 CycloneDX SBOM으로 집계하여, 중복이 제거된 VEX, HTML 및 GitLab 호환 보고서를 생성하여 지속적인 공급망 보안 모니터링을 제공합니다.
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 semgrep/semgrep
많은 언어를 위한 경량 정적 분석. 소스 코드처럼 보이는 패턴으로 버그 변종을 찾습니다.
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 mongodb/kingfisher
시크릿 탐지 + 실시간 검증. 영향 범위 매핑. 신속한 폐기. CLI를 사용하거나 Rust 및 Python에 임베드하세요.
 greenbone/openvas-scanner
이 저장소에는 Greenbone Community Edition용 스캐너 구성 요소가 포함되어 있습니다.







