Discover the assets you expose and map them in a Shodan-style inventory.
Assess each host with industry-standard scanners and fix what matters first.


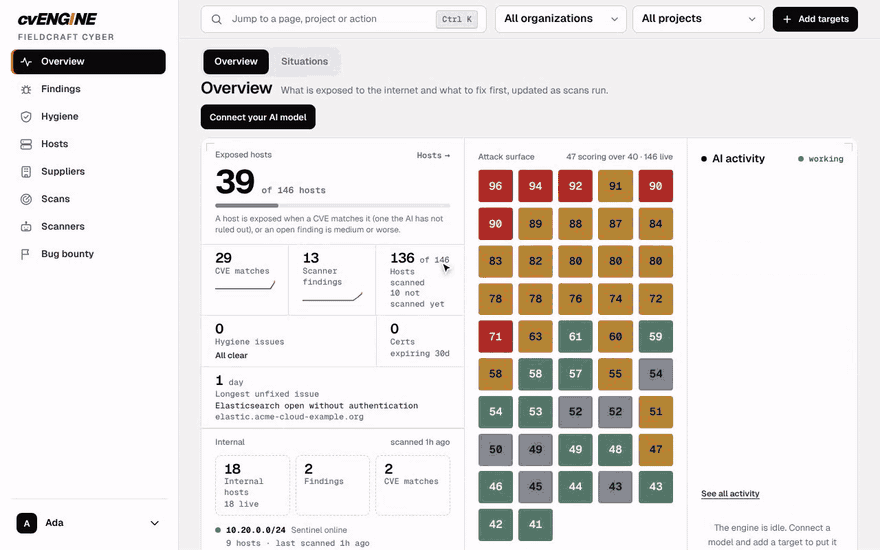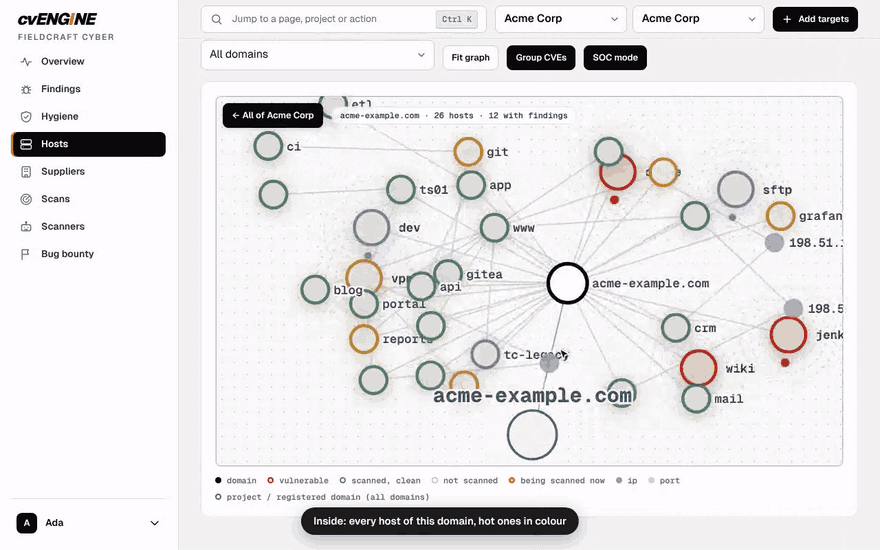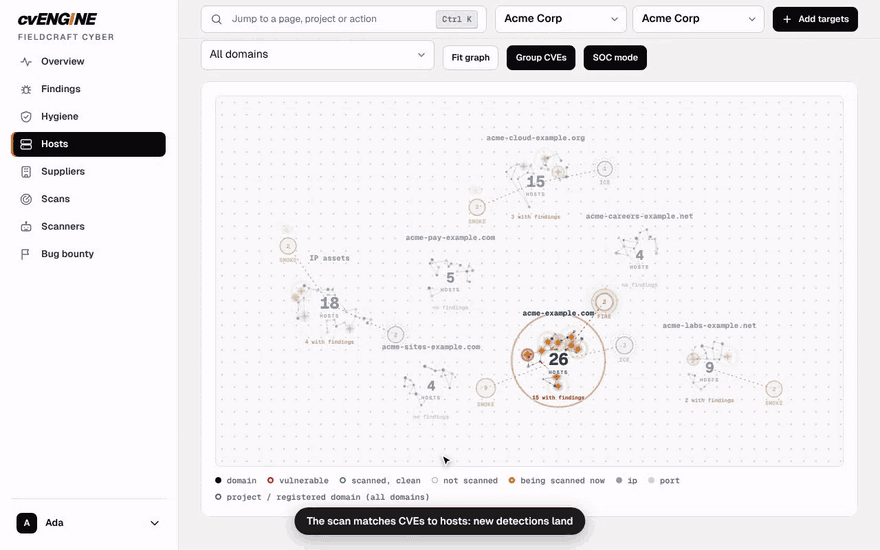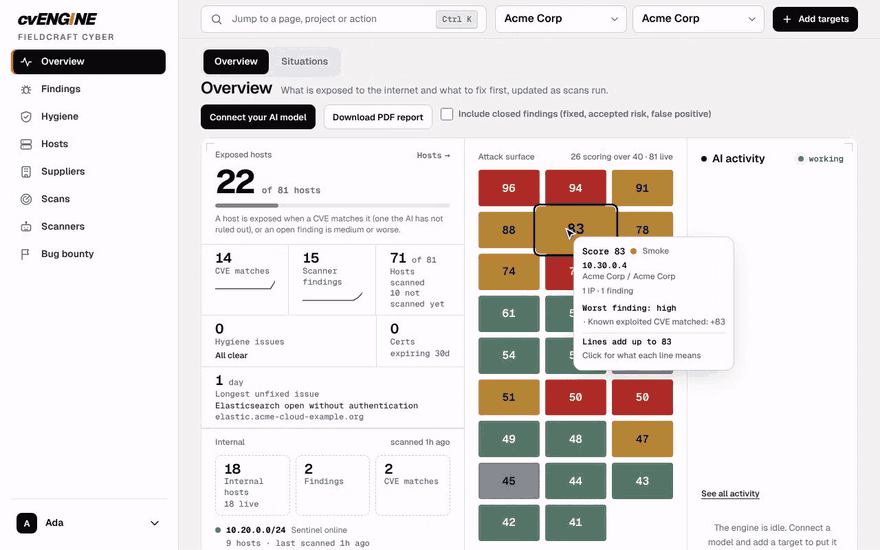
cvENGINE 1.4.1 on demo data.
cvENGINE watches the CVE feeds around the clock and shows you, with proof, which new CVEs actually reach your hosts.
Every new CVE, checked against your hosts
- Watch the feeds. New CVEs and fresh exploitation news arrive all day from the sources that matter.
- Find who is exposed. Each CVE is matched to the hosts that run the affected product and version.
- Write the check. When no vetted check exists, your AI drafts a read-only one that cvENGINE validates first.
- Prove it on your hosts. A Sentinel reproduces each match with a read-only check and keeps the evidence.
- Cut the noise. AI reviews the evidence, so what is real rises and likely false positives sink.
Bring your own AI: Anthropic, OpenAI or OpenRouter on your own key, or fully local with Ollama, LM Studio or vLLM. It is off until you switch it on, and it never closes a finding a check proved. Without a model, cvENGINE still discovers, scans, matches and validates.
How it works, exactly
- Feeds. The cve.now feed is read every 30 minutes. CISA KEV, ENISA EUVD, FIRST EPSS, Exploit-DB, Metasploit and, with a key, VulnCheck KEV are read every hour, so a CVE that becomes exploited turns hot within the hour.
- Matching. A CVE becomes a match only when a host runs the same product at a version inside a bounded affected range. A product seen with no version never makes a match.
- Checks the AI writes. For hot CVEs, within a daily budget, the AI reads the advisory and records how to detect it. When no vetted Nuclei template exists it can draft a read-only one, which runs on a host only after the system validated it: syntax and a harmless loopback control on a Sentinel, an offline test against an affected and a fixed response, and a second AI pass. This ships off: an administrator switches on Validate AI-written checks automatically.
- Proof. Every five minutes up to 20 matches, fire first, are reproduced on a Sentinel with one of six read-only checks: a vetted Nuclei template,
nmap -sV on the one port, a version banner request, the credential-less database check, a version and identity probe, or a JavaScript library read. The exact command and result are kept. A check that does not reproduce a finding never lowers it.
- Triage. CVE matches, scanner findings, open databases, open admin routes, routes exposing credentials and hygiene findings of medium severity or worse are rated confirmed, likely, needs validation, likely false positive or not applicable, within daily caps (by default 500 per project and 2,000 in all).
- AI reviewer. Reads each open finding once, up to 300 a day by default, and records whether it is real. It closes a false positive only when you allow it and only when the finding has no hard evidence and no person has worked it.
- Floors. Hard evidence sets a floor the model cannot go below: a template hit, a database that answered or a validation hit is confirmed, and a version inside the affected range is at least needs validation. The model alone can never confirm a finding.
- Your AI, your controls. For triage and review the model sees structured evidence with host names redacted, it has no tools, and the server checks every answer before it counts. The AI jobs have daily caps, and the usage page shows calls, tokens and cost estimates. The AI reviewer, AI-written checks and auto-fire (AI confirmation and tests as soon as a new hot CVE lands) each ship switched off.
More in Pipeline, CVE intelligence and AI reviewer.
Know everything you expose
cvENGINE is a self-hosted external attack surface and vulnerability assessment platform. Give it your domains and it keeps discovering the subdomains, addresses and certificates you expose, in a searchable, Shodan-style inventory of every host, port, service, technology and certificate. Forgotten and shadow assets come to light, and new hosts, opened ports and version changes land on a timeline as soon as a scan sees them. Every host is assessed with industry-standard open-source scanners, and Situations ranks what to fix first: proof before likelihood, known exploited before severity alone.
cvENGINE 1.4.0 is here









