
mobsfscan v1.0.1
mobsfscan è uno strumento di analisi statica in grado di trovare pattern di codice insicuri nel codice sorgente Android e iOS. Supporta codice Java, Kotlin, Swift e Objective C. mobsfscan utilizza le regole di analisi statica di MobSF ed è alimentato da semgrep e dal pattern matcher libsast.
mobsfscan
mobsfscan è uno strumento di analisi statica in grado di individuare pattern di codice non sicuri nel codice sorgente Android e iOS. Supporta codice Java, Kotlin, Android XML, iOS Info.plist, Swift e Objective C. mobsfscan utilizza le regole di analisi statica di MobSF ed è basato sul pattern matcher semgrep e libsast.
Made with  in India


Supporta mobsfscan
Se ti è piaciuto mobsfscan e lo trovi utile, ti invitiamo a considerare una donazione.
Corsi e Certificazioni e-Learning
 Automated Mobile Application Security Assessment with MobSF -MAS
 Android Security Tools Expert -ATX
Installazione
pip install mobsfscan
Richiede Python 3.10–3.14
Opzioni della riga di comando```bash
$ mobsfscan usage: mobsfscan [-h] [--json] [--sarif] [--sonarqube] [--gitlab-sast] [--html] [--type {android,ios,auto}] [-o OUTPUT] [-c CONFIG] [-mp {default,billiard,thread}] [-w] [--no-fail] [-v] [path ...]
positional arguments: path Path can be file(s) or directories with source code
options: -h, --help show this help message and exit --json set output format as JSON --sarif set output format as SARIF 2.1.0 --sonarqube set output format as SonarQube generic issues (10.3+) --gitlab-sast set output format as GitLab SAST report --html set output format as HTML --type {android,ios,auto} optional: force android or ios rules explicitly -o OUTPUT, --output OUTPUT output filename to save the result -c CONFIG, --config CONFIG location to .mobsf config file -mp {default,billiard,thread}, --multiprocessing {default,billiard,thread} optional: specify multiprocessing strategy -w, --exit-warning non zero exit code on warning --no-fail force zero exit code, takes precedence over --exit-warning -v, --version show mobsfscan version
## Esempio di utilizzo```bash
$ mobsfscan tests/assets/src/
- Pattern Match ████████████████████████████████████████████████████████████ 3
- Semantic Grep ██████ 37

mobsfscan: v0.3.0 | Ajin Abraham | opensecurity.in
╒══════════════╤════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID      │ android_webview_ignore_ssl                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION  │ Insecure WebView Implementation. WebView ignores SSL Certificate errors and accept any SSL Certificate. This application is vulnerable to MITM attacks │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ TYPE         │ RegexAnd                                                                                                                                               │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ PATTERN      │ ['onReceivedSslError\\(WebView', '\\.proceed\\(\\);']                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY     │ ERROR                                                                                                                                                   │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ INPUTCASE    │ exact                                                                                                                                                  │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CVSS         │ 7.4                                                                                                                                                    │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE          │ CWE-295 Improper Certificate Validation                                                                                                                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP-MOBILE │ M3: Insecure Communication                                                                                                                             │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ MASVS        │ MSTG-NETWORK-3                                                                                                                                         │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ REF          │ https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#webview-server-certificate-verification                │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES        │ ╒════════════════╤═════════════════════════════════════════════════════════════════════════════════════════════╕                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1480 - 1491                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 50                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ .proceed();                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ File           │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match Position │ 1331 - 1357                                                                                 │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Line Number(s) │ 46                                                                                          │                                       │
│              │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤                                       │
│              │ │ Match String   │ onReceivedSslError(WebView                                                                  │                                       │
│              │ ╘════════════════╧═════════════════════════════════════════════════════════════════════════════════════════════╛                                       │
╘══════════════╧════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╛
API Python```python
from mobsfscan.mobsfscan import MobSFScan src = 'tests/assets/src/java/java_vuln.java' scanner = MobSFScan([src], json=True) scanner.scan() { 'results': { 'android_logging': { 'files': [{ 'file_path': 'tests/assets/src/java/java_vuln.java', 'match_position': (13, 73), 'match_lines': (19, 19), 'match_string': ' Log.d("htbridge", "getAllRecords(): " + records.toString());' }], 'metadata': { 'cwe': 'CWE-532 Insertion of Sensitive Information into Log File', 'owasp-mobile': 'M1: Improper Platform Usage', 'masvs': 'MSTG-STORAGE-3', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#logs', 'description': 'The App logs information. Please ensure that sensitive information is never logged.', 'severity': 'INFO' } }, 'android_certificate_pinning': { 'metadata': { 'cwe': 'CWE-295 Improper Certificate Validation', 'owasp-mobile': 'M3: Insecure Communication', 'masvs': 'MSTG-NETWORK-4', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#testing-custom-certificate-stores-and-certificate-pinning-mstg-network-4', 'description': 'This App does not use TLS/SSL certificate or public key pinning to detect or prevent MITM attacks in secure communication channel.', 'severity': 'INFO' } }, 'android_root_detection': { 'metadata': { 'cwe': 'CWE-919 - Weaknesses in Mobile Applications', 'owasp-mobile': 'M8: Code Tampering', 'masvs': 'MSTG-RESILIENCE-1', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1', 'description': 'This App does not have root detection capabilities. Running a sensitive application on a rooted device questions the device integrity and affects users data.', 'severity': 'INFO' } }, 'android_prevent_screenshot': { 'metadata': { 'cwe': 'CWE-200 Information Exposure', 'owasp-mobile': 'M2: Insecure Data Storage', 'masvs': 'MSTG-STORAGE-9', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#finding-sensitive-information-in-auto-generated-screenshots-mstg-storage-9', 'description': 'This App does not have capabilities to prevent against Screenshots from Recent Task History/ Now On Tap etc.', 'severity': 'INFO' } }, 'android_safetynet_api': { 'metadata': { 'cwe': 'CWE-353 Missing Support for Integrity Check', 'owasp-mobile': 'M8: Code Tampering', 'masvs': 'MSTG-RESILIENCE-1', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1', 'description': "This App does not uses SafetyNet Attestation API that provides cryptographically-signed attestation, assessing the device's integrity. This check helps to ensure that the servers are interacting with the genuine app running on a genuine Android device. ", 'severity': 'INFO' } }, 'android_detect_tapjacking': { 'metadata': { 'cwe': 'CWE-200 Information Exposure', 'owasp-mobile': 'M1: Improper Platform Usage', 'masvs': 'MSTG-PLATFORM-9', 'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05h-Testing-Platform-Interaction.md#testing-for-overlay-attacks-mstg-platform-9', 'description': "This app does not has capabilities to prevent tapjacking attacks. An attacker can hijack the user's taps and tricks him into performing some critical operations that he did not intend to.", 'severity': 'INFO' } } }, 'errors': [] }
## Configurare mobsfscan

Un file `.mobsf` nella directory principale del codice sorgente consente di configurare mobsfscan. È inoltre possibile utilizzare un file `.mobsf` personalizzato tramite l'argomento `--config`.```yaml
---
- ignore-filenames:
  - skip.java

  ignore-paths:
  - __MACOSX
  - skip_dir

  ignore-rules:
  - android_kotlin_logging
  - android_safetynet_api
  - android_prevent_screenshot
  - android_detect_tapjacking
  - android_certificate_pinning
  - android_root_detection
  - android_certificate_transparency

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    ios_log: ERROR
    android_logging: WARNING
severity-overrides modifica la severità segnalata per specifici ID di regola (INFO, WARNING o ERROR). Le sovrascritture vengono applicate prima di severity-filter e influenzano l'output della CLI, i codici di uscita e i formati di report (SARIF, SonarQube, GitLab SAST).
Sopprimere i Risultati
Puoi sopprimere i risultati dai file sorgente aggiungendo il commento // mobsf-ignore: rule_id1, rule_id2 sulla riga che genera il risultato. Viene soppressa solo quella corrispondenza; le altre corrispondenze della stessa regola nel file vengono comunque segnalate.
Esempio:```java String password = "strong password"; // mobsf-ignore: hardcoded_password
## Integrazioni CI/CD

Puoi abilitare mobsfscan nelle tue pipeline CI/CD o DevSecOps.

#### Github Action

Aggiungi quanto segue al file `.github/workflows/mobsfscan.yml`.```yaml
name: mobsfscan

on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]

jobs:
  build:
    runs-on: ubuntu-latest
    steps:
    - uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: mobsfscan
      uses: MobSF/mobsfscan@main
      with:
        args: '. --json'
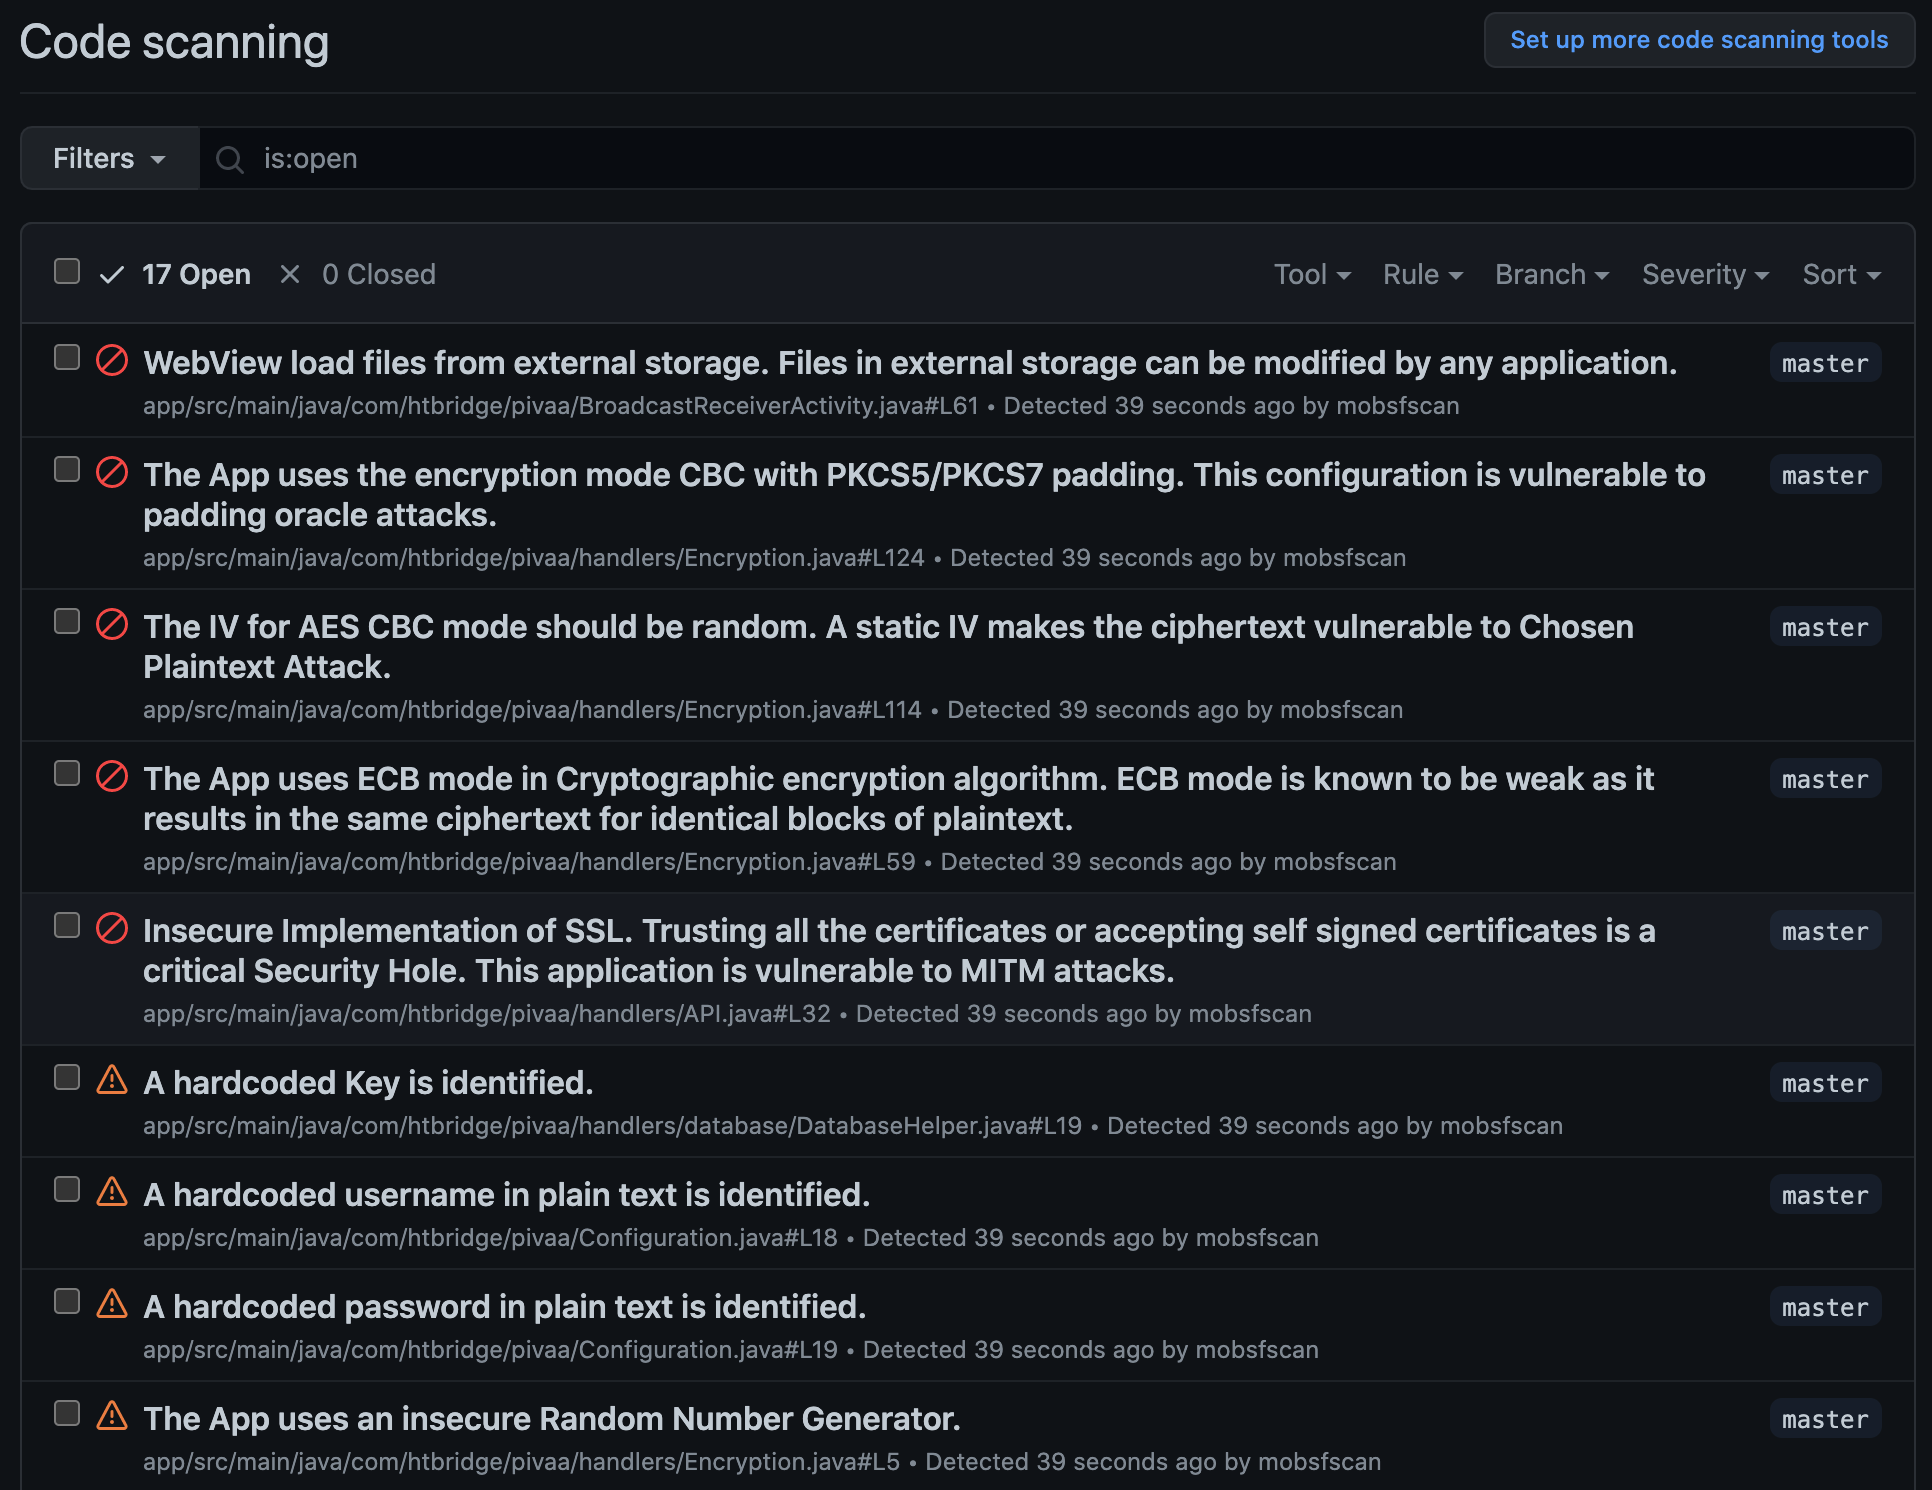
Esempio: pivaa con mobsfscan github action
Integrazione della scansione del codice di Github
Aggiungi quanto segue al file .github/workflows/mobsfscan_sarif.yml.```yaml
name: mobsfscan sarif
on:
push:
branches: [ master, main ]
pull_request:
branches: [ master, main ]
jobs: mobsfscan: runs-on: ubuntu-latest name: mobsfscan code scanning permissions: security-events: write actions: read contents: read steps: - name: Checkout the code uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1 - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0 with: python-version: '3.12' - name: mobsfscan uses: MobSF/mobsfscan@main with: args: '. --sarif --output results.sarif || true' - name: Upload mobsfscan report uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1 with: sarif_file: results.sarif
#### Gitlab CI/CD
Aggiungi quanto segue al file `.gitlab-ci.yml`.```yaml
stages:
- test
mobsfscan:
image: python:3.12
stage: test
before_script:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan . --gitlab-sast -o gl-sast-report.json
artifacts:
reports:
sast: gl-sast-report.json
Esempio di comando (locale):```bash mobsfscan . --gitlab-sast -o gl-sast-report.json
This writes a native [GitLab SAST report](https://docs.gitlab.com/user/application_security/sast/) so findings appear in the Vulnerability Report / MR security widget without a SARIF converter.

#### SonarQube / SonarCloud

`--sonarqube` writes the [generic issue format](https://docs.sonarsource.com/sonarqube-server/analyzing-source-code/importing-external-issues/generic-issue-import-format) (SonarQube 10.3+ / SonarCloud), with separate `rules` and `issues` arrays:```bash
mobsfscan . --sonarqube -o mobsfscan-sonar.json
Importa con sonar.externalIssuesReportPaths=mobsfscan-sonar.json.
Travis CI
Aggiungi quanto segue al file .travis.yml.```yaml
language: python
install:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan .
#### Circle CI

Aggiungi quanto segue al file `.circleci/config.yaml````yaml
version: 2.1
jobs:
  mobsfscan:
    docker:
      - image: cimg/python:3.12
    steps:
      - checkout
      - run:
          name: Install mobsfscan
          command: pip install --upgrade mobsfscan
      - run:
           name: mobsfscan check
           command: mobsfscan .
Bitrise
Aggiungi quanto segue al file `bitrise.yml````yaml security_audit: steps:
- activate-ssh-key@4: run_if: '{{getenv "SSH_RSA_PRIVATE_KEY" | ne ""}}'
- [email protected]: {}
- mobsfscan@1: {}
- deploy-to-bitrise-io@2: {}
## Docker

### Immagine precompilata da [DockerHub](https://hub.docker.com/r/opensecurity/mobsfscan)```bash
docker pull opensecurity/mobsfscan
docker run -v /path-to-source-dir:/src opensecurity/mobsfscan /src
Compilazione locale```
docker build -t mobsfscan . docker run -v /path-to-source-dir:/src mobsfscan /src