
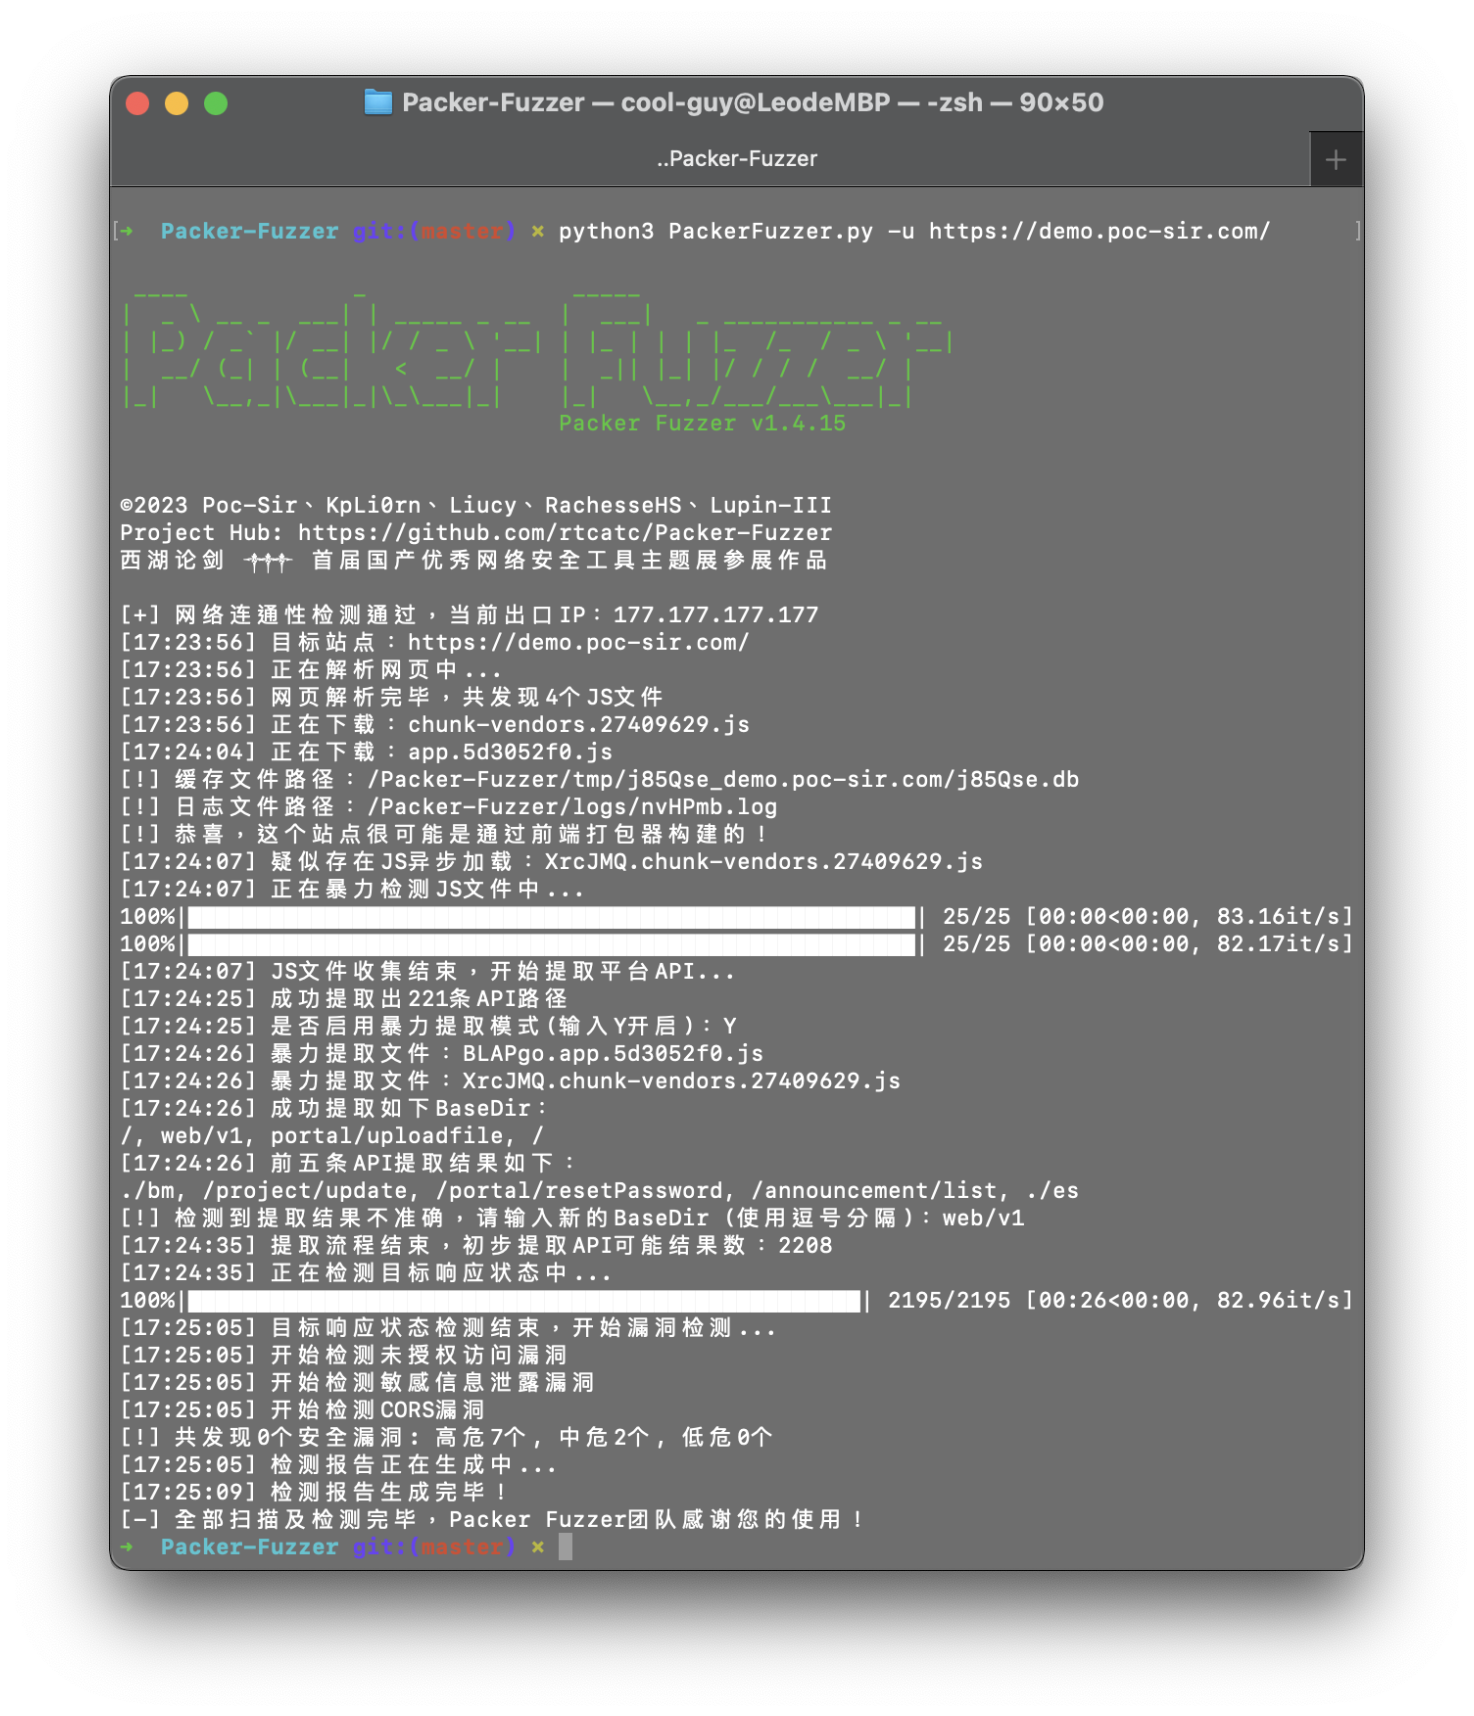
Packer-Fuzzer
 rtcatc/packer-fuzzer
Packer Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
api-security-testingfuzzingvulnerability-scanners+1
3.3k
rtcatc/packer-fuzzerPacker Fuzzer is a fast and efficient scanner for security detection of websites constructed by javascript module bundler such as Webpack.
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 nemesida-waf/waf-bypass
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…
 owasp/securityshepherd
Web and mobile application security training platform
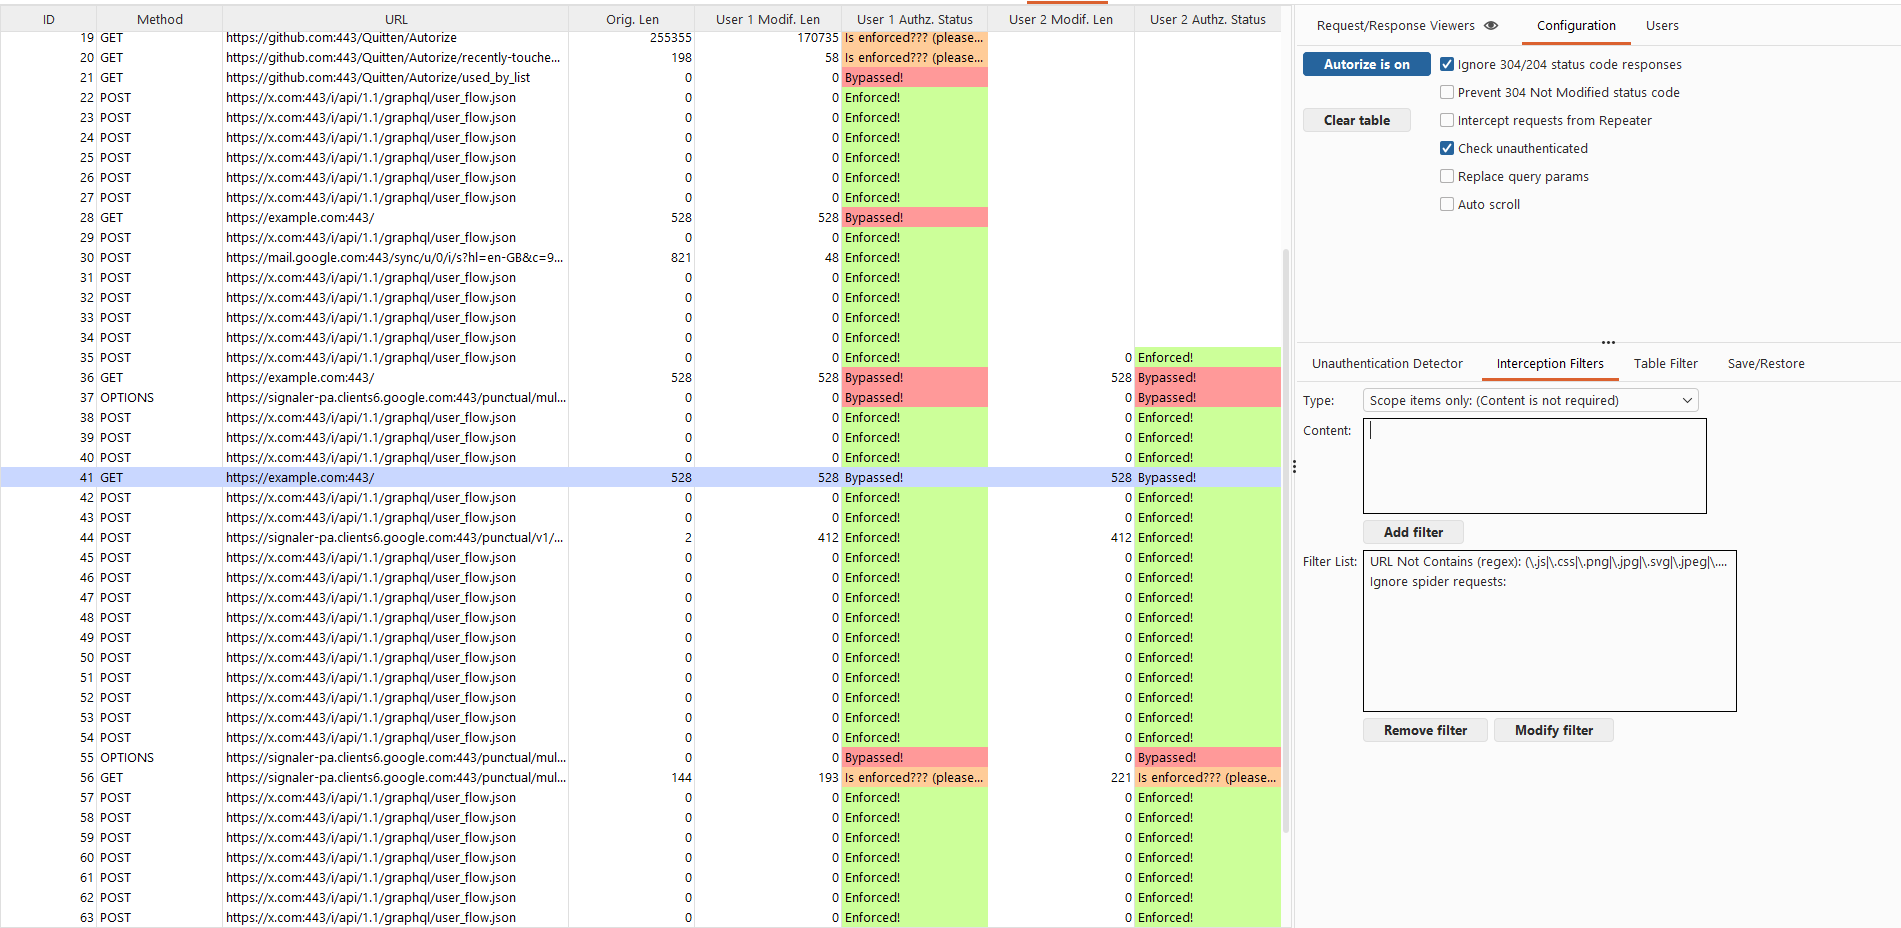 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
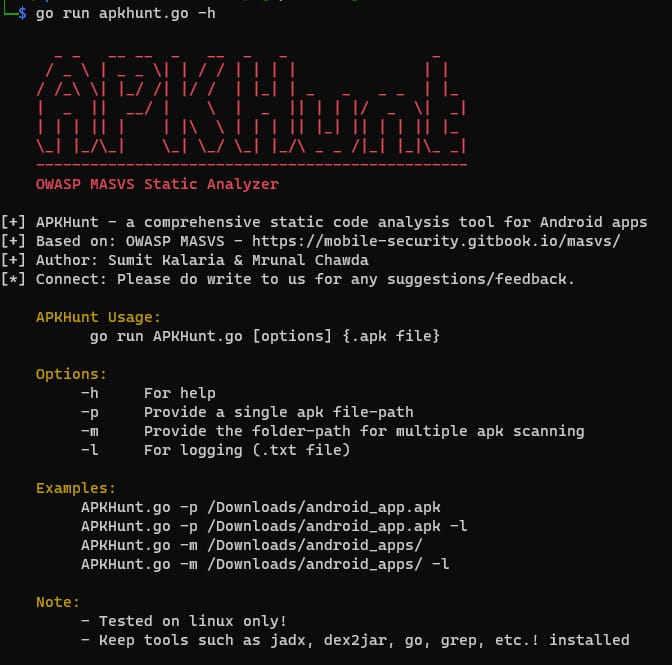 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
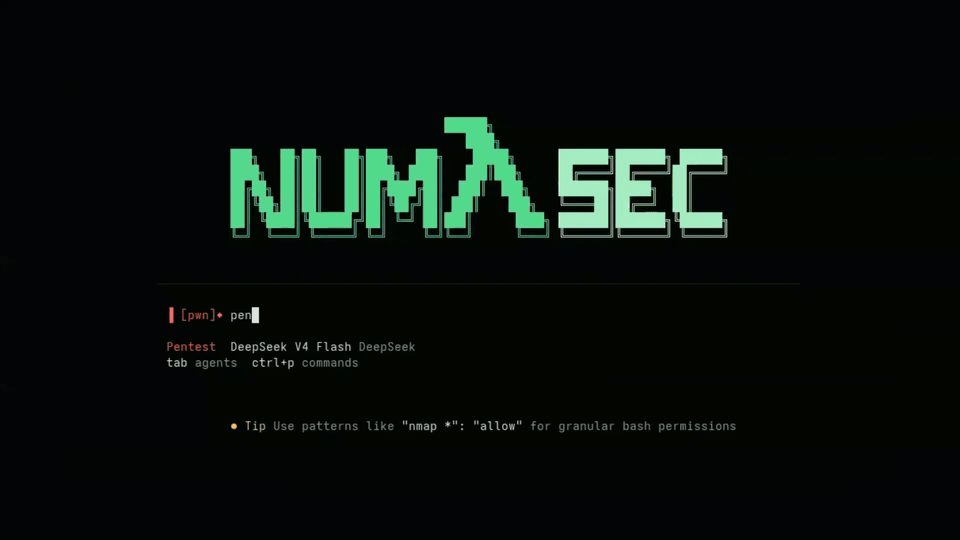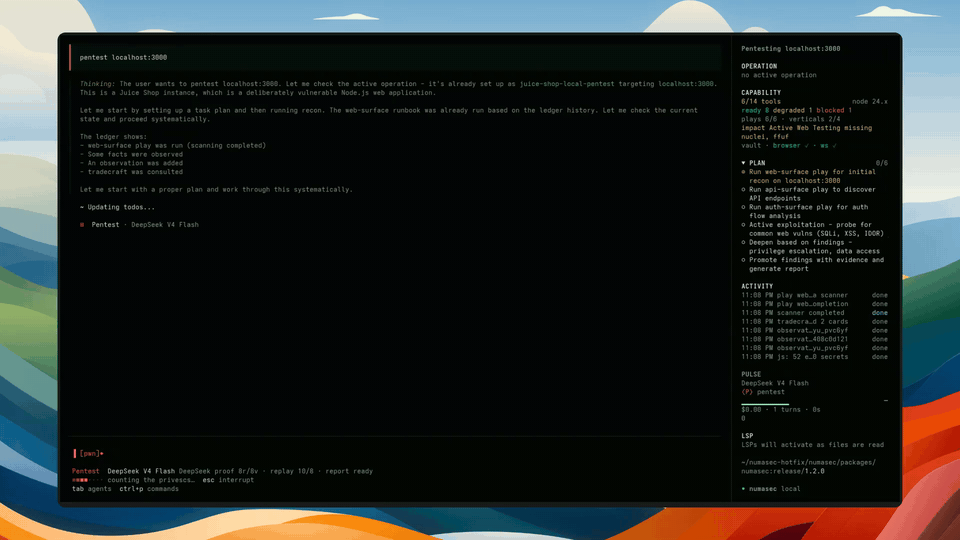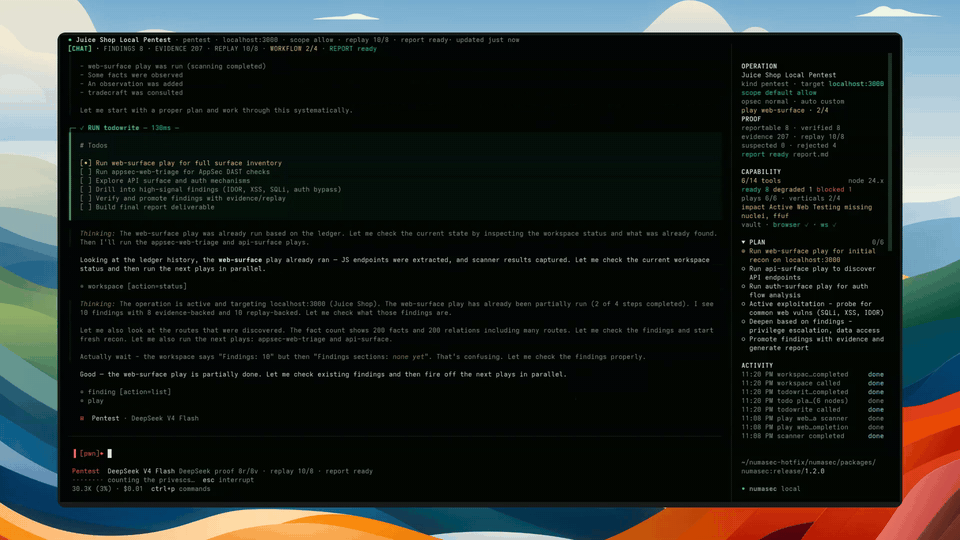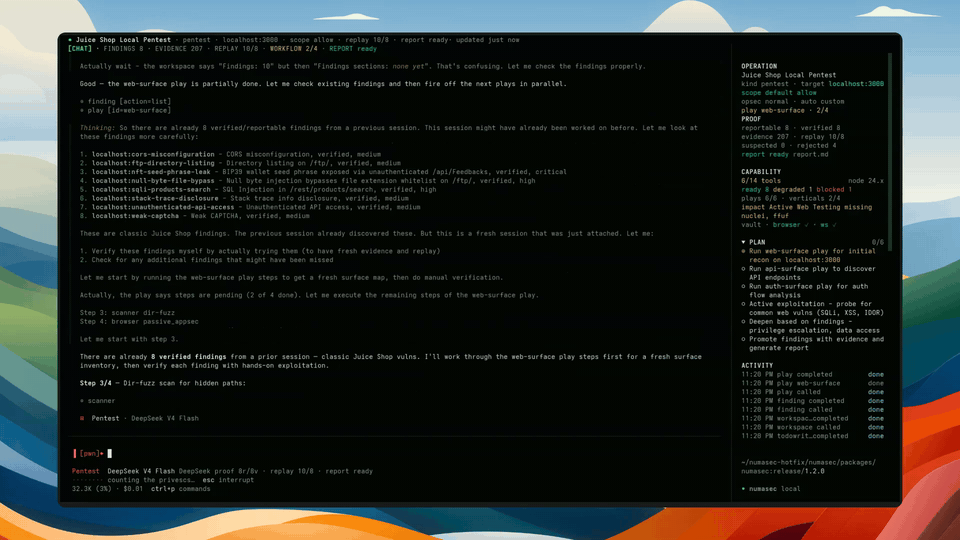 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 ethicalhackingplayground/ssrf-king
SSRF plugin for burp Automates SSRF Detection in all of the Request
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
 owasp/dvsa
a Damn Vulnerable Serverless Application
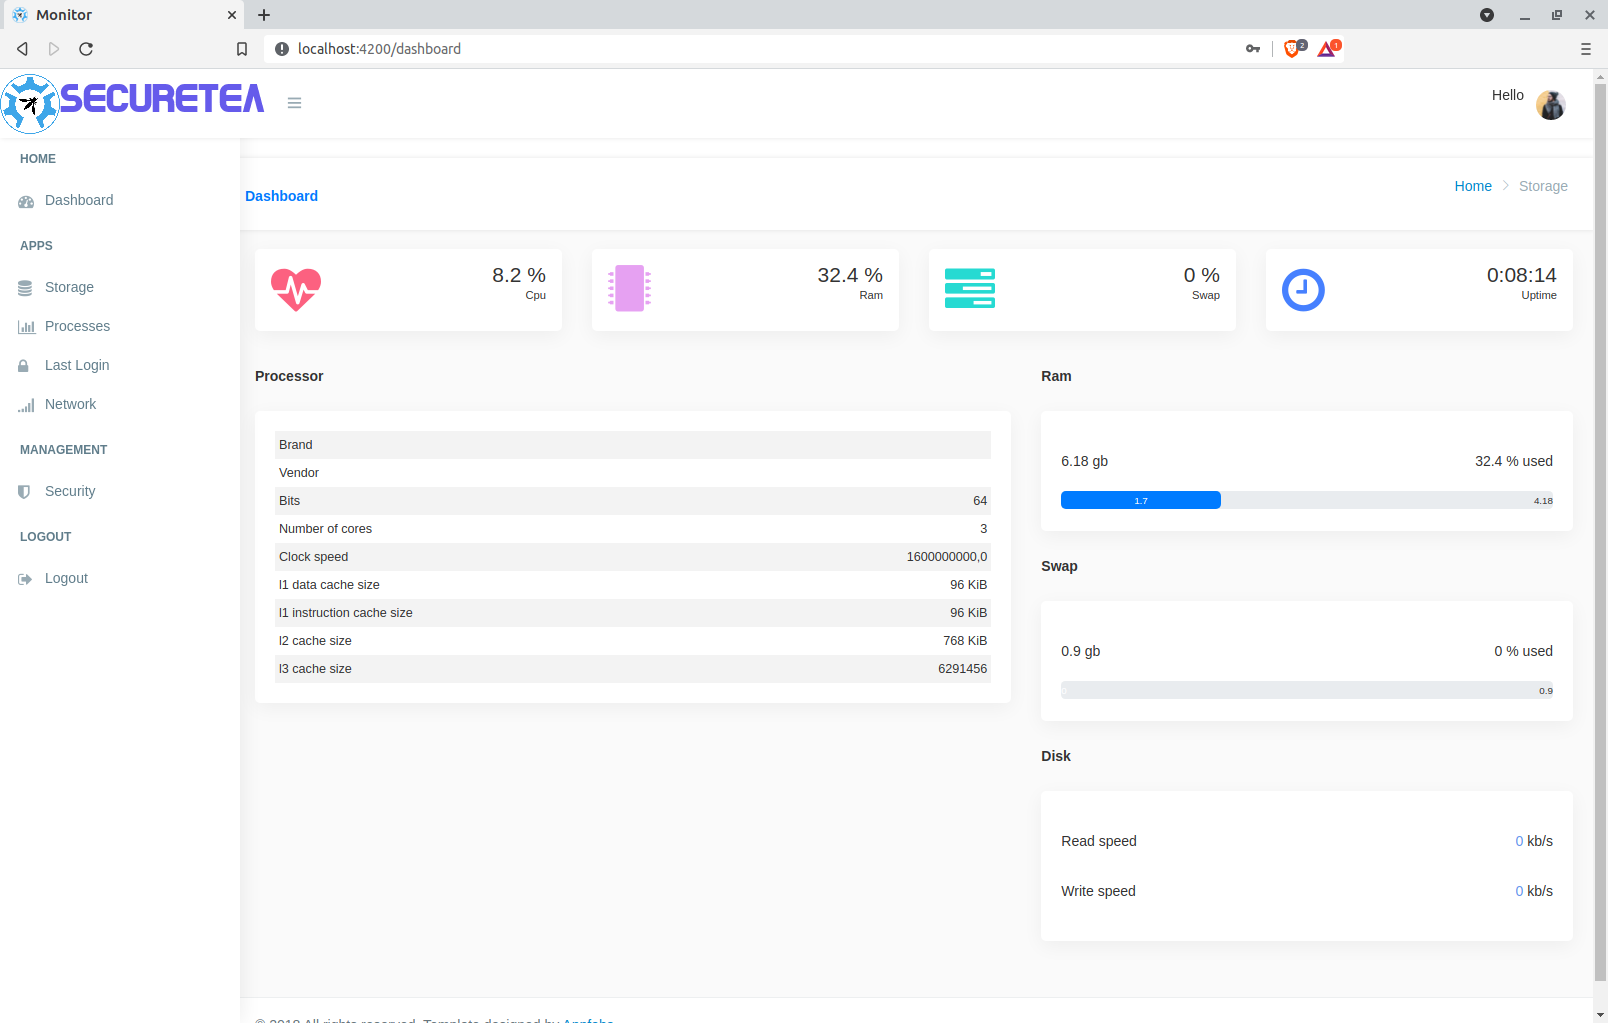 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
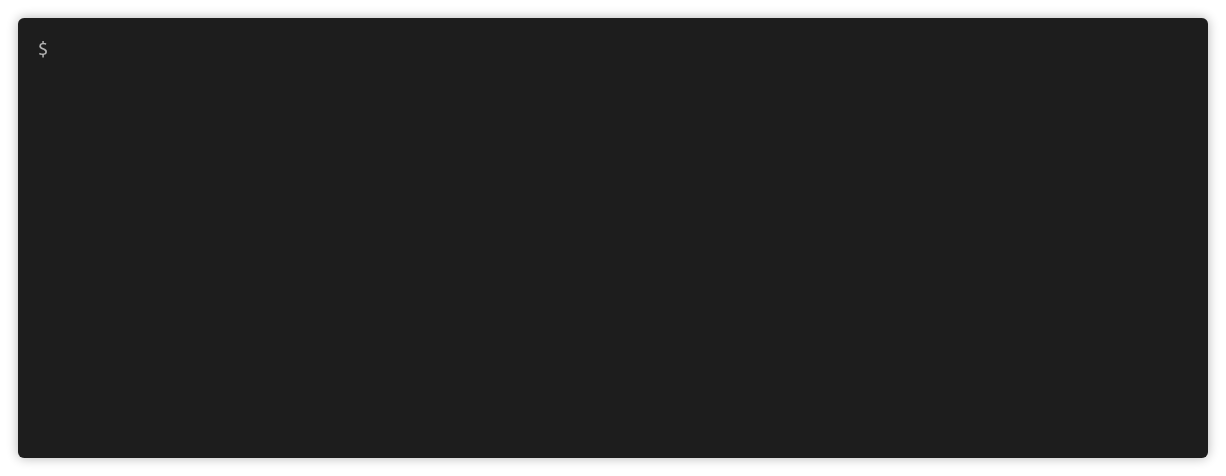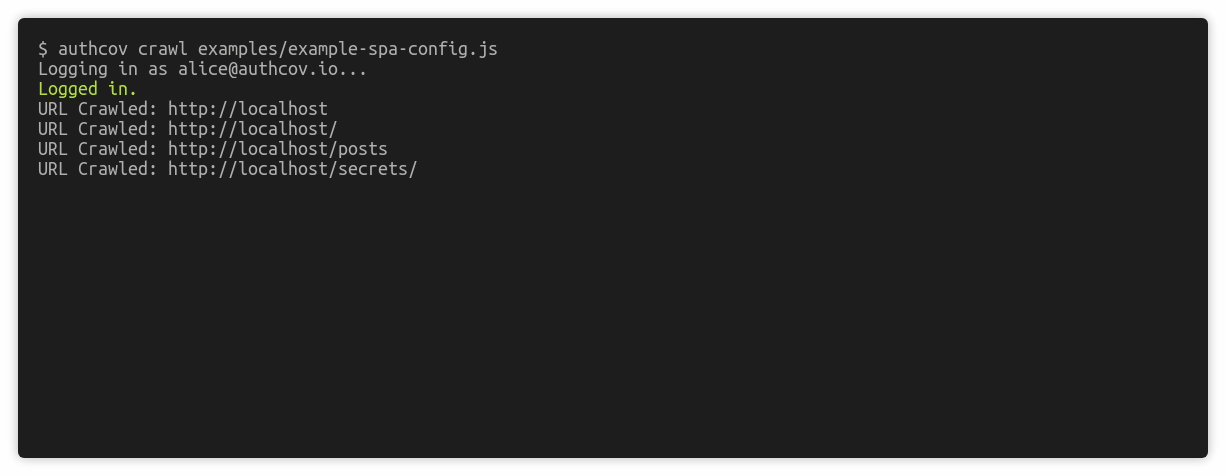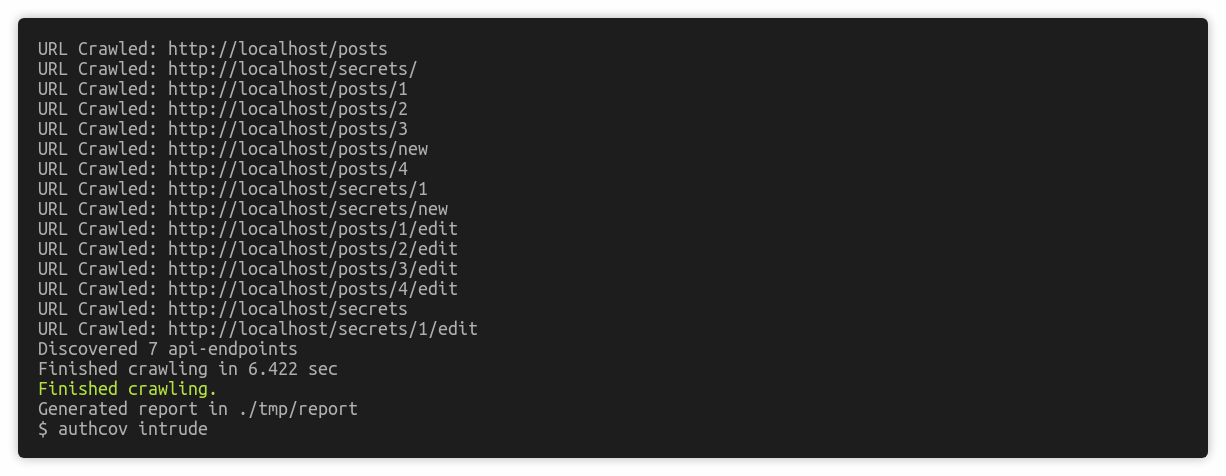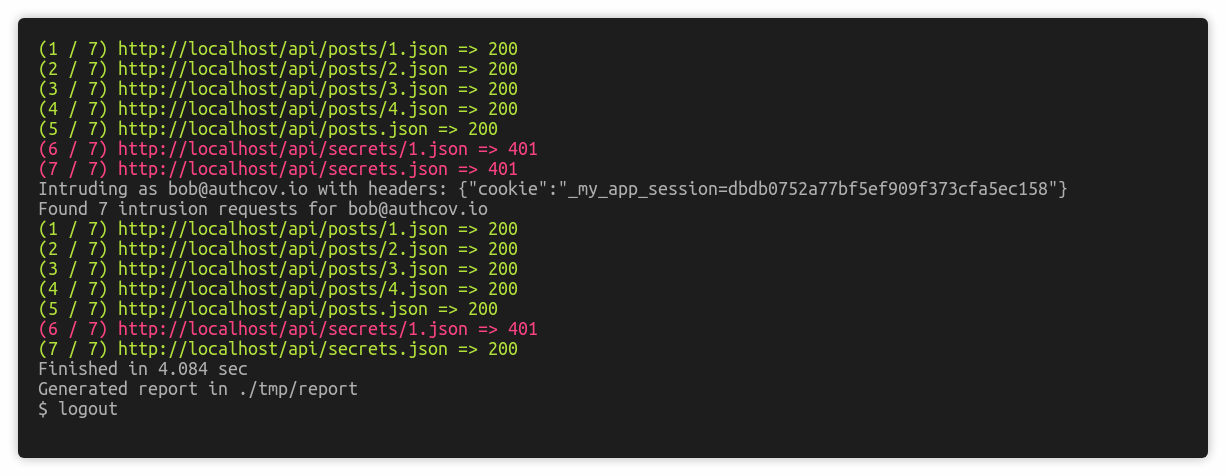 authcov/authcov
Web app authorisation coverage scanning
 bwasp/bwasp
BoB Web Application Security Project
 deepseasred/autonessus
This script communicates with the Nessus API in an attempt to help with automating scans. Depending on the flag issued with the script, you can list…
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 ngalongc/openapi_security_scanner
Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…