

angr
 angr/angr
A powerful and user-friendly binary analysis platform!
ai-assisted-reversingbinary-analysisbinary-exploitation+12
angr/angrA powerful and user-friendly binary analysis platform!
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
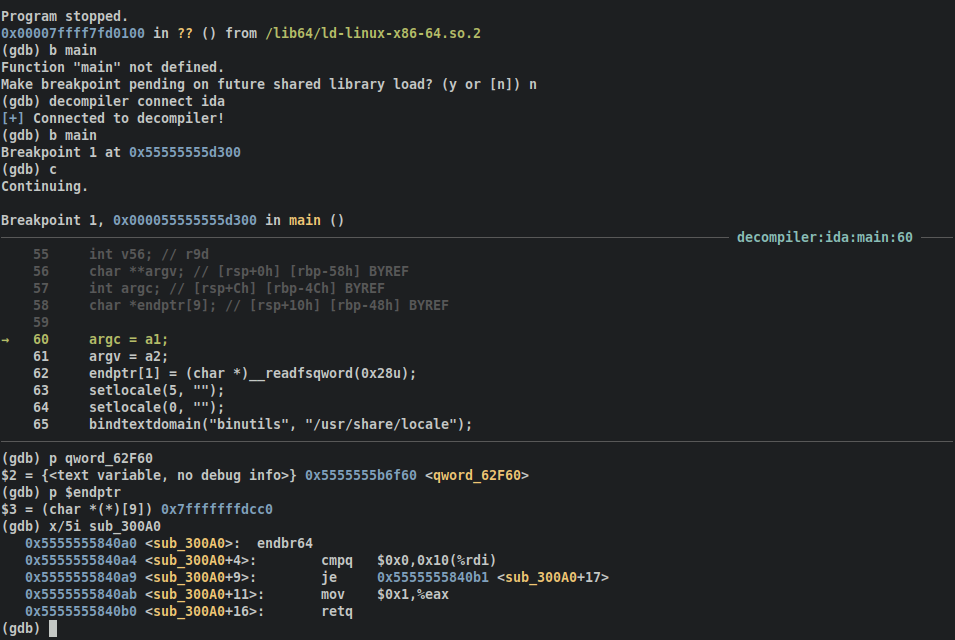 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 neurosaki987/tvm-recover
Devirtualizes Tencent VM .tvm0 sections: lifts VM handlers to guest-level listings and LLVM IR, recovers CFG and dispatch, and patches recovered code…
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 gallopsled/pwntools
CTF framework and exploit development library

 abraxas/vbox-lsilogic-sas-config
VirtualBox 7.2.20 - Critical - Local - Type confusion / arb R/W - SAS1068 CONFIG SCSI-SPI overlay
 jaime64net/debuggerj-
Debugger de aplicaciones x86 y x64 con intgracion de AI