Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Brovan — User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing, network dumping, and interactive debugging in a sandboxed environment. | Kitploit
Tools/GitHubGitHub/advdebug/brovan
Dynamic Analysis (Sandboxing)Dynamic Code Analysis (DAST)Reverse EngineeringDebuggersMalware AnalysisBinary Analysis
GitHubadvdebug/brovan

Brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing, network dumping, and interactive debugging in a sandboxed environment.

View Repository
155115018h 59m agoReviewed by Kitploit
Share
Brovan banner


.NET Language License

A user-mode x86_64 binary emulator for inspecting programs, tracing syscalls, and safely running untrusted software.

What is Brovan?

Brovan is an interactive x86_64 emulator that gives you full control over how programs execute. It can be used to reverse engineer binaries, trace API and system calls, capture network traffic, or run software in an isolated environment without executing it directly on your host CPU.

It is designed to support as much software as possible while remaining a safe, efficient, and high-performance option for running Windows and Linux software across Windows, Linux and Android. Brovan is still in early development, so it is not yet fully mature or reliable.

Supported backends:

  • Unicorn Engine for cross-platform emulation
  • WHP (Windows Hypervisor Platform) for hardware acceleration on Windows
  • KVM (Kernel-based Virtual Machine) for hardware acceleration on Linux

Core Features

MULTI-FORMAT LOADING

Load and execute binaries directly inside the emulator without host installation.

PE   ELF   Memory Dumps   Raw Shellcode

BROVVULK GRAPHICS LAYER

Custom Vulkan translation subsystem handling DXVK calls and game rendering.

DXVK   DirectX   Vulkan Surface

SYSCALL & API TRACING

Inspect execution live to see what functions, DLLs, and kernel calls the program accesses.

Kernel Syscalls   Symbol Resolving   Loaded DLLs

NETWORK DUMPING

Intercept guest socket traffic and export network activity for payload analysis.

Socket Intercept   PCAP Capture   Traffic Analysis

Previews & Demos

Gaming & Graphics (Brovvulk)

Brovan can render guest graphical applications through its Brovvulk (Brovan<->Vulkan) translation subsystem. Here is a sample game i had (Deltarune), but it can work on many other games:
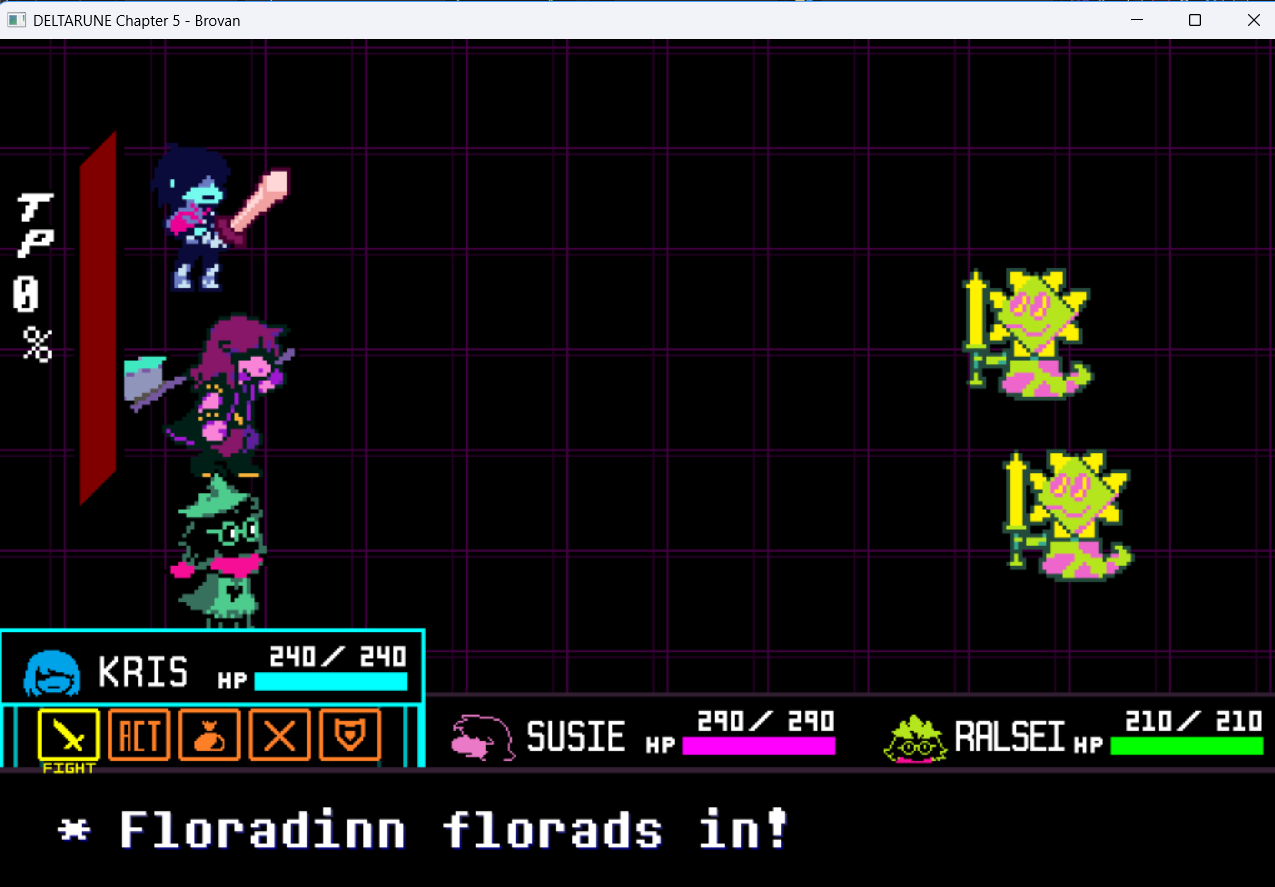
Deltarune running in Brovan

Deltarune Bring-up

  • Vulkan surface rendering via Brovvulk
  • DPI-aware host window integration
  • WHP acceleration for a smoother gaming experience

Binary Execution & Tracing

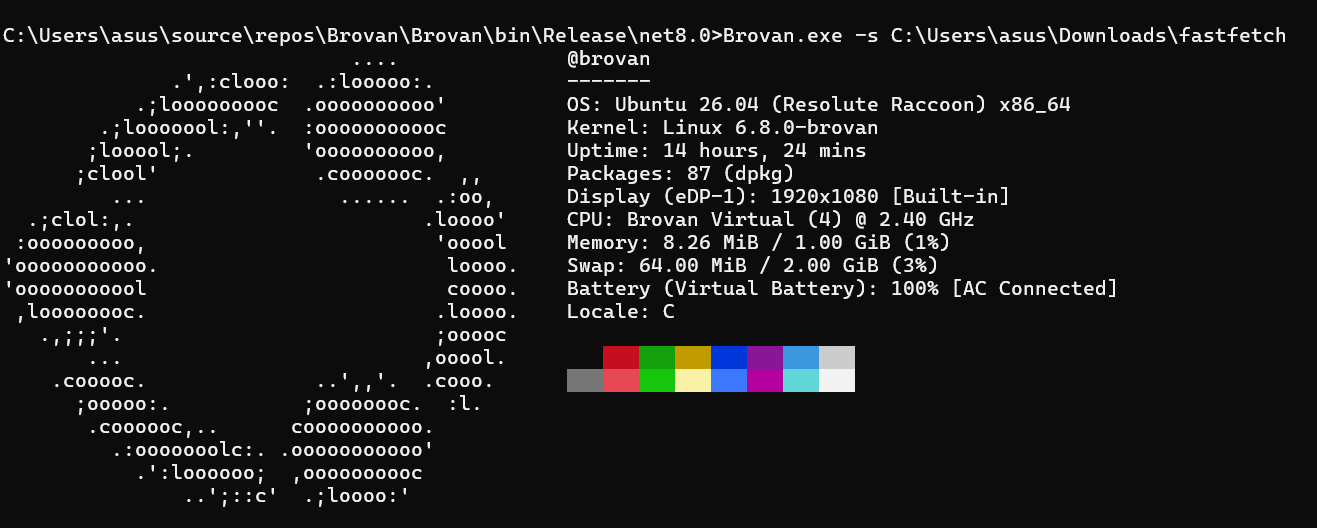
Cross-platform Linux execution
Linux ELF on Windows
Running fastfetch cross-platform
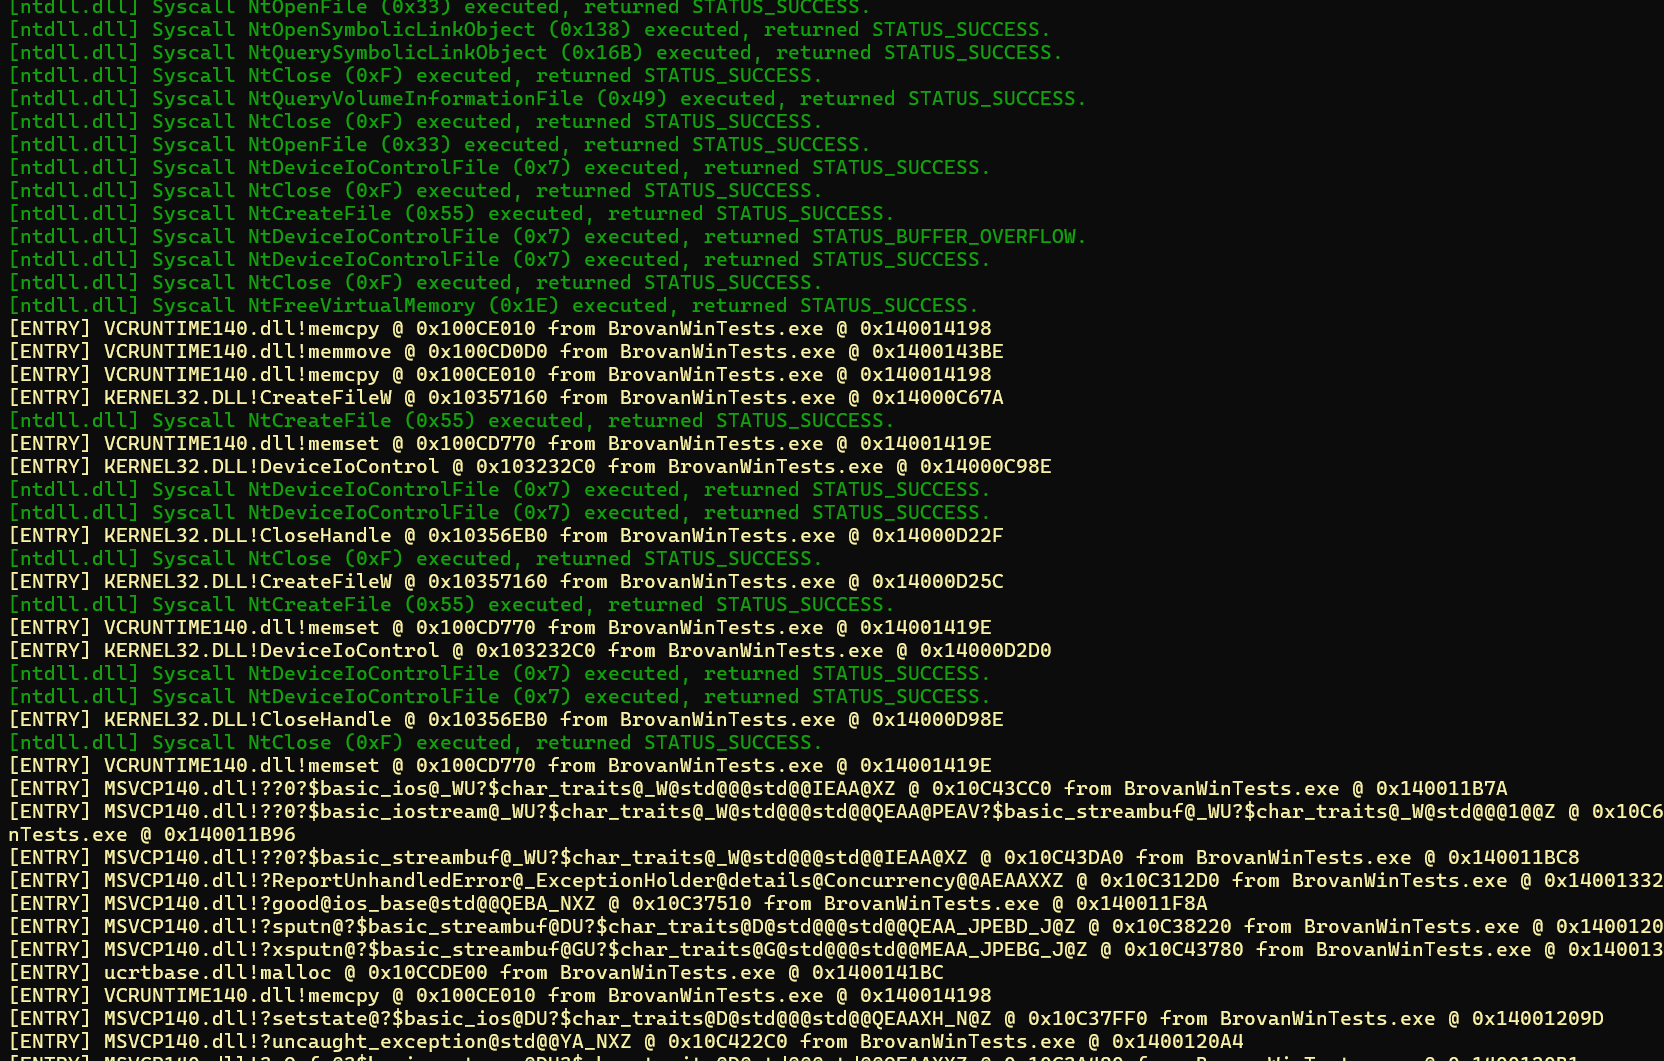
Syscall tracing log
Syscall Tracing
Live logs of API calls and dynamic symbols
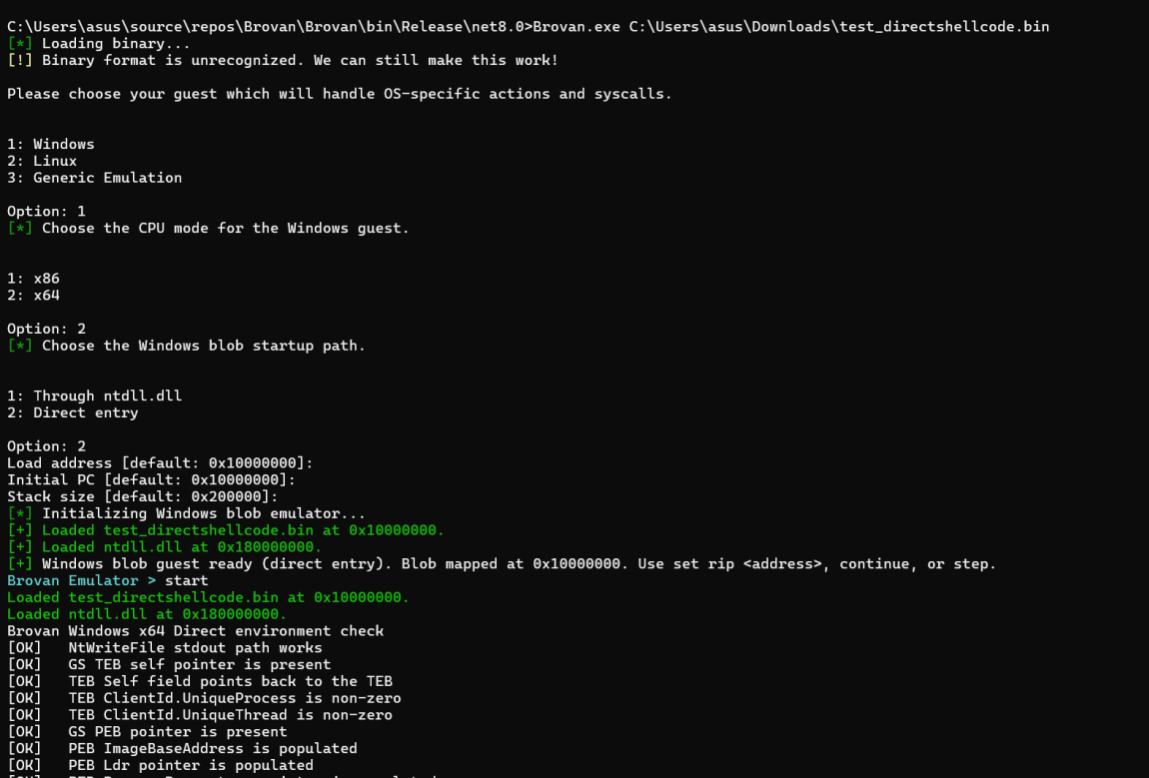
Raw binary execution
Raw Binaries
Executing shellcode and memory dumps

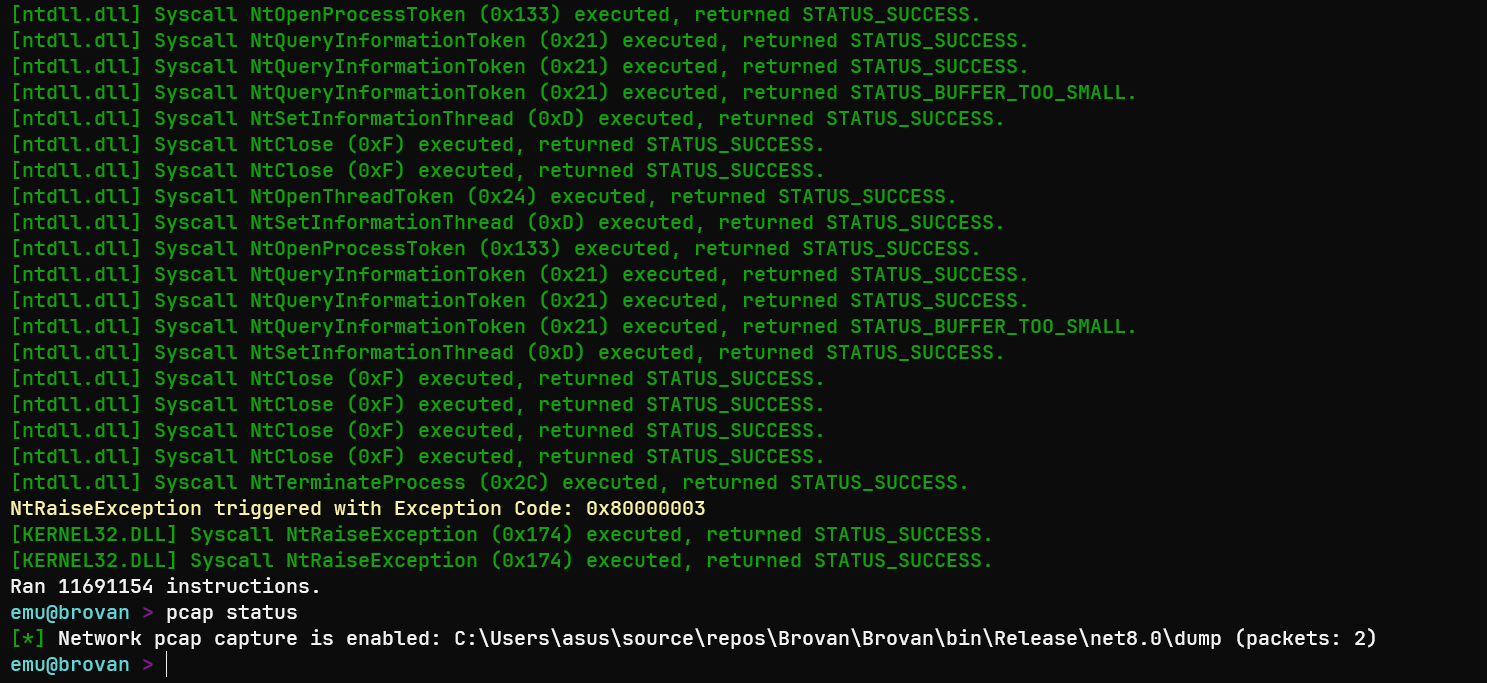
Network Inspection

Network dumping
Network Capture
Intercepting guest socket reads and writes
Traffic viewer
Traffic Analyzer
Viewing dumped PCAPs and payloads

Documentation & Wiki

Check out the GitHub Wiki for:

  • Building from source
  • Architecture details
  • Command reference and usage guides
  • FAQ

[!WARNING] The Releases page may not always have the latest changes.
For the most up-to-date version, build from source instead or use the latest build from GitHub Actions

Credits

Thanks to Iced library for x86_64 disassembly and assembly.

Thanks to Unicorn Engine for the core emulator.

Thanks to Mesa for zink, which gives Windows programs OpenGL on top of Brovvulk.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    614
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    476
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    389
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    334
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    257
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    247

Explore all tools

Browse our collection of tools

View all tools →