Al-Khaser v0.81
Content
Introduction
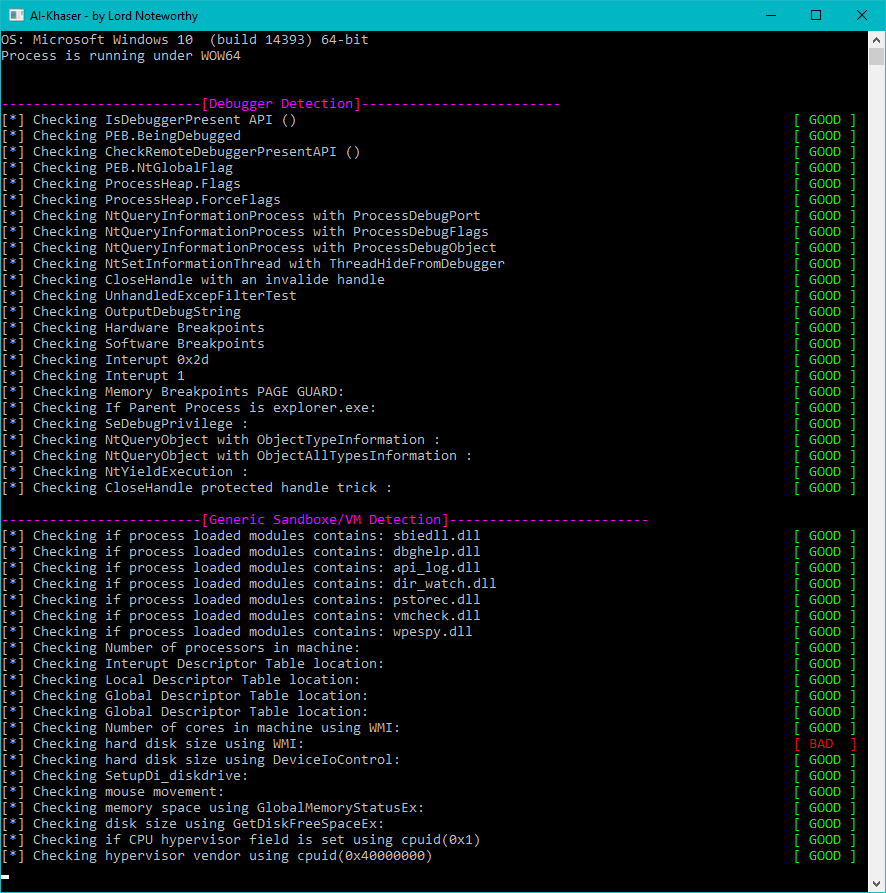
al-khaser is a PoC "malware" application with good intentions that aims to stress your anti-malware system.
It performs a bunch of common malware tricks with the goal of seeing if you stay under the radar.
Usage
$ ./al-khaser.exe -h
Usage: al-khaser.exe [OPTIONS]
Options:
  --check <type>      Enable specific check(s). Can be used multiple times. Valid types are:
                        TLS              (Thread Local Storage callback checks)
                        DEBUG            (Anti-debugging checks)
                        INJECTION        (Code injection checks)
                        GEN_SANDBOX      (Generic sandbox checks)
                        VBOX             (VirtualBox detection)
                        VMWARE           (VMware detection)
                        VPC              (Virtual PC detection)
                        QEMU             (QEMU detection)
                        KVM              (KVM detection)
                        XEN              (Xen detection)
                        WINE             (Wine detection)
                        PARALLELS        (Parallels detection)
                        HYPERV           (Hyper-V detection)
                        CODE_INJECTIONS  (Additional code injection techniques)
                        TIMING_ATTACKS   (Timing/sleep-based sandbox evasion)
                        DUMPING_CHECK    (Dumping memory/process checks)
                        ANALYSIS_TOOLS   (Analysis tools detection)
                        ANTI_DISASSM     (Anti-disassembly checks)
  --sleep <seconds>   Set sleep/delay duration in seconds (default: 600).
  --delay <seconds>   Alias for --sleep.
  -h, --help          Show this help message and exit.

Examples:
  al-khaser.exe --check DEBUG --check TIMING_ATTACKS --sleep 30
  al-khaser.exe --check VMWARE --check QEMU
  al-khaser.exe --sleep 30
Download
You can download built binaries (x86, x64) from this project's releases page. The password for the 7zs can be found here.
Possible uses
- You are making an anti-debug plugin and you want to check its effectiveness.
- You want to ensure that your sandbox solution is hidden enough.
- Or you want to ensure that your malware analysis environment is well hidden.
Please, if you encounter any of the anti-analysis tricks which you have seen in a malware, don't hesitate to contribute.
Features
Anti-debugging attacks
- IsDebuggerPresent
- CheckRemoteDebuggerPresent
- Process Environment Block (BeingDebugged)
- Process Environment Block (NtGlobalFlag)
- ProcessHeap (Flags)
- ProcessHeap (ForceFlags)
- Low Fragmentation Heap (LFH)
- NtQueryInformationProcess (ProcessDebugPort)
- NtQueryInformationProcess (ProcessDebugFlags)
- NtQueryInformationProcess (ProcessDebugObject)
- WudfIsAnyDebuggerPresent
- WudfIsKernelDebuggerPresent
- WudfIsUserDebuggerPresent
- NtSetInformationThread (HideThreadFromDebugger)
- NtQueryObject (ObjectTypeInformation)
- NtQueryObject (ObjectAllTypesInformation)
- CloseHanlde (NtClose) Invalide Handle
- SetHandleInformation (Protected Handle)
- UnhandledExceptionFilter
- OutputDebugString (GetLastError())
- Hardware Breakpoints (SEH / GetThreadContext)
- Software Breakpoints (INT3 / 0xCC)
- Memory Breakpoints (PAGE_GUARD)
- Interrupt 0x2d
- Interrupt 1
- Trap Flag
- Parent Process (Explorer.exe)
- SeDebugPrivilege (Csrss.exe)
- NtYieldExecution / SwitchToThread
- TLS callbacks
- Process jobs
- Memory write watching
- Page exception breakpoint detection
- API hook detection (module bounds based)
Anti-injection
- Enumerate modules with EnumProcessModulesEx (32-bit, 64-bit, and all options)
- Enumerate modules with ToolHelp32
- Enumerate the process LDR structures with LdrEnumerateLoadedModules
- Enumerate the process LDR structures directly
- Walk memory with GetModuleInformation
- Walk memory for hidden modules
Anti-Dumping
- Erase PE header from memory
- SizeOfImage
Timing Attacks [Anti-Sandbox]
- RDTSC (with CPUID to force a VM Exit)
- RDTSC (Locky version with GetProcessHeap & CloseHandle)
- Sleep -> SleepEx -> NtDelayExecution
- Sleep (in a loop a small delay)
- Sleep and check if time was accelerated (GetTickCount)
- SetTimer (Standard Windows Timers)
- timeSetEvent (Multimedia Timers)
- WaitForSingleObject -> WaitForSingleObjectEx -> NtWaitForSingleObject
- WaitForMultipleObjects -> WaitForMultipleObjectsEx -> NtWaitForMultipleObjects
- IcmpSendEcho (CCleaner Malware)
- CreateWaitableTimer
- CreateTimerQueueTimer
- Big crypto loops (todo)
Human Interaction / Generic [Anti-Sandbox]
- Mouse movement
- File names like
sample.exe or sandbox.exe.
- Total Physical memory (GlobalMemoryStatusEx)
- Disk size using DeviceIoControl (IOCTL_DISK_GET_LENGTH_INFO)
- Disk size using GetDiskFreeSpaceEx (TotalNumberOfBytes)
- Mouse (Single click / Double click) (todo)
- DialogBox (todo)
- Scrolling (todo)
- Execution after reboot (todo)
- Count of processors (Win32/Tinba - Win32/Dyre)
- Sandbox known product IDs (todo)
- Color of background pixel (todo)
- Keyboard layout (Win32/Banload) (todo)
- Genuine Windows installation.
- Known Sandbox hostnames and usernames
Anti-Virtualization / Full-System Emulation
- Registry key value artifacts
- HARDWARE\DEVICEMAP\Scsi\Scsi Port 0\Scsi Bus 0\Target Id 0\Logical Unit Id 0 (Identifier) (VBOX)
- HARDWARE\DEVICEMAP\Scsi\Scsi Port 0\Scsi Bus 0\Target Id 0\Logical Unit Id 0 (Identifier) (QEMU)
- HARDWARE\Description\System (SystemBiosVersion) (VBOX)
- HARDWARE\Description\System (SystemBiosVersion) (QEMU)
- HARDWARE\Description\System (VideoBiosVersion) (VIRTUALBOX)
- HARDWARE\Description\System (SystemBiosDate) (06/23/99)
- HARDWARE\DEVICEMAP\Scsi\Scsi Port 0\Scsi Bus 0\Target Id 0\Logical Unit Id 0 (Identifier) (VMWARE)
- HARDWARE\DEVICEMAP\Scsi\Scsi Port 1\Scsi Bus 0\Target Id 0\Logical Unit Id 0 (Identifier) (VMWARE)
- HARDWARE\DEVICEMAP\Scsi\Scsi Port 2\Scsi Bus 0\Target Id 0\Logical Unit Id 0 (Identifier) (VMWARE)
- SYSTEM\ControlSet001\Control\SystemInformation (SystemManufacturer) (VMWARE)
- SYSTEM\ControlSet001\Control\SystemInformation (SystemProductName) (VMWARE)
- Registry Keys artifacts
- HARDWARE\ACPI\DSDT\VBOX__ (VBOX)
- HARDWARE\ACPI\FADT\VBOX__ (VBOX)
- HARDWARE\ACPI\RSDT\VBOX__ (VBOX)
- SOFTWARE\Oracle\VirtualBox Guest Additions (VBOX)
- SYSTEM\ControlSet001\Services\VBoxGuest (VBOX)
- SYSTEM\ControlSet001\Services\VBoxMouse (VBOX)
- SYSTEM\ControlSet001\Services\VBoxService (VBOX)
- SYSTEM\ControlSet001\Services\VBoxSF (VBOX)
- SYSTEM\ControlSet001\Services\VBoxVideo (VBOX)
- SOFTWARE\VMware, Inc.\VMware Tools (VMWARE)
- SOFTWARE\Wine (WINE)
- SOFTWARE\Microsoft\Virtual Machine\Guest\Parameters (HYPER-V)
- SYSTEM\CurrentControlSet\Services\Disk\Enum
- SYSTEM\CurrentControlSet\Enum\IDE
- SYSTEM\CurrentControlSet\Enum\SCSI
- File system artifacts
 ayoubfaouzi/al-khaser

