
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
OSweep — Don't Just Search OSINT. Sweep It. | Kitploit
Tools/GitHubGitHub/ecstatic-nobel/osweep
OSINT (Open Source Intelligence)Phishing ToolsThreat Feeds & AggregatorsDNS & Subdomain EnumerationInformation GatheringMalware AnalysisThreat Intelligence
GitHubecstatic-nobel/osweep

OSweep

Don't Just Search OSINT. Sweep It.

View Repository
31865887 years agoReviewed by Kitploit
Share
Website

[OSweep™]

Don't Just Search OSINT. Sweep It.

Description

If you work in IT security, then you most likely use OSINT to help you understand what it is that your SIEM alerted you on and what everyone else in the world understands about it. More than likely you are using more than one OSINT service because most of the time OSINT will only provide you with reports based on the last analysis of the IOC. For some, that's good enough. They create network and email blocks, create new rules for their IDS/IPS, update the content in the SIEM, create new alerts for monitors in Google Alerts and DomainTools, etc etc. For others, they deploy these same countermeasures based on provided reports from their third-party tools that the company is paying THOUSANDS of dollars for.

The problem with both of these is that the analyst needs to dig a little deeper (ex. FULLY deobfuscate a PowerShell command found in a malicious macro) to gather all of the IOCs. And what if the additional IOC(s) you are basing your analysis on has nothing to do with what is true about that site today? And then you get pwned? And then other questions from management arise...

See where this is headed? You're about to get a pink slip and walked out of the building so you can start looking for another job in a different line of work.

So why did you get pwned? You know that if you wasted time gathering all the IOCs for that one alert manually, it would have taken you half of your shift to complete and you would've got pwned regardless.

The fix? OSweep™.

Prerequisites

Before getting started, ensure you have the following:
Ubuntu 18.04+

  • Python 2.7.14 ($SPLUNK_HOME/bin/python)
  • Splunk 7.1.3+
  • Deb Packages
    • gcc
    • python-pip

CentOS 7+

  • Python 2.7.14 ($SPLUNK_HOME/bin/python)
  • Splunk 7.1.3+
  • Yum Packages
    • epel-release
    • gcc
    • python-pip

Optional Packages

  • Git

Click HERE to get started.

Gallery

OSINT Sweep - Dashboard

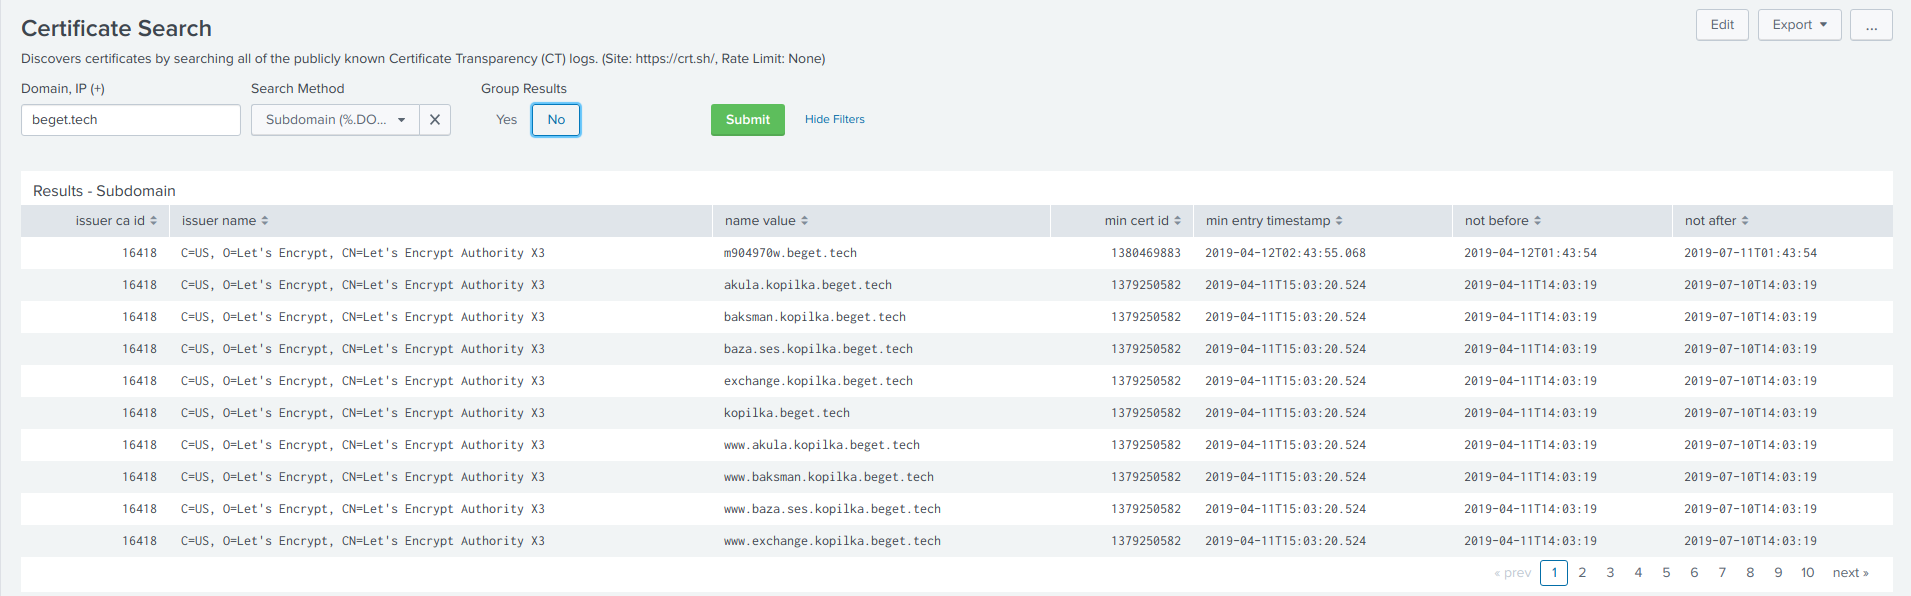
Certificate Search - Dashboard crtsh - Dashboard
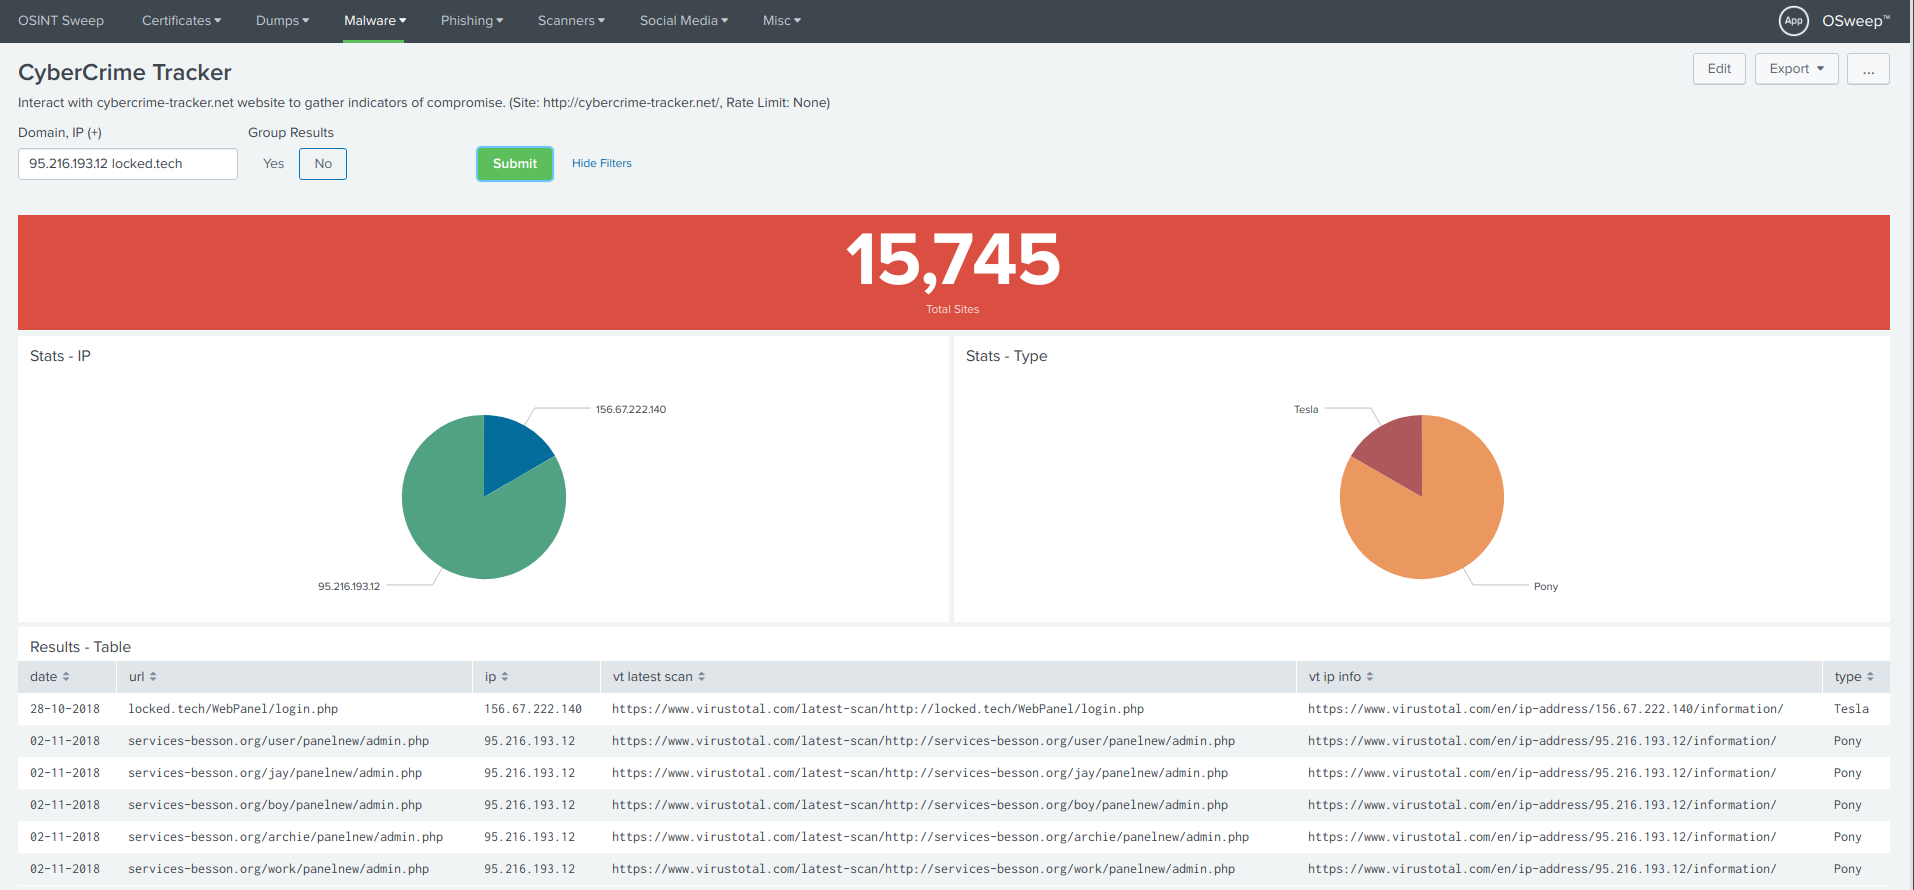
CyberCrime Tracker - Dashboard CyberCrime Tracker - Dashboard
GreyNoise - Dashboard

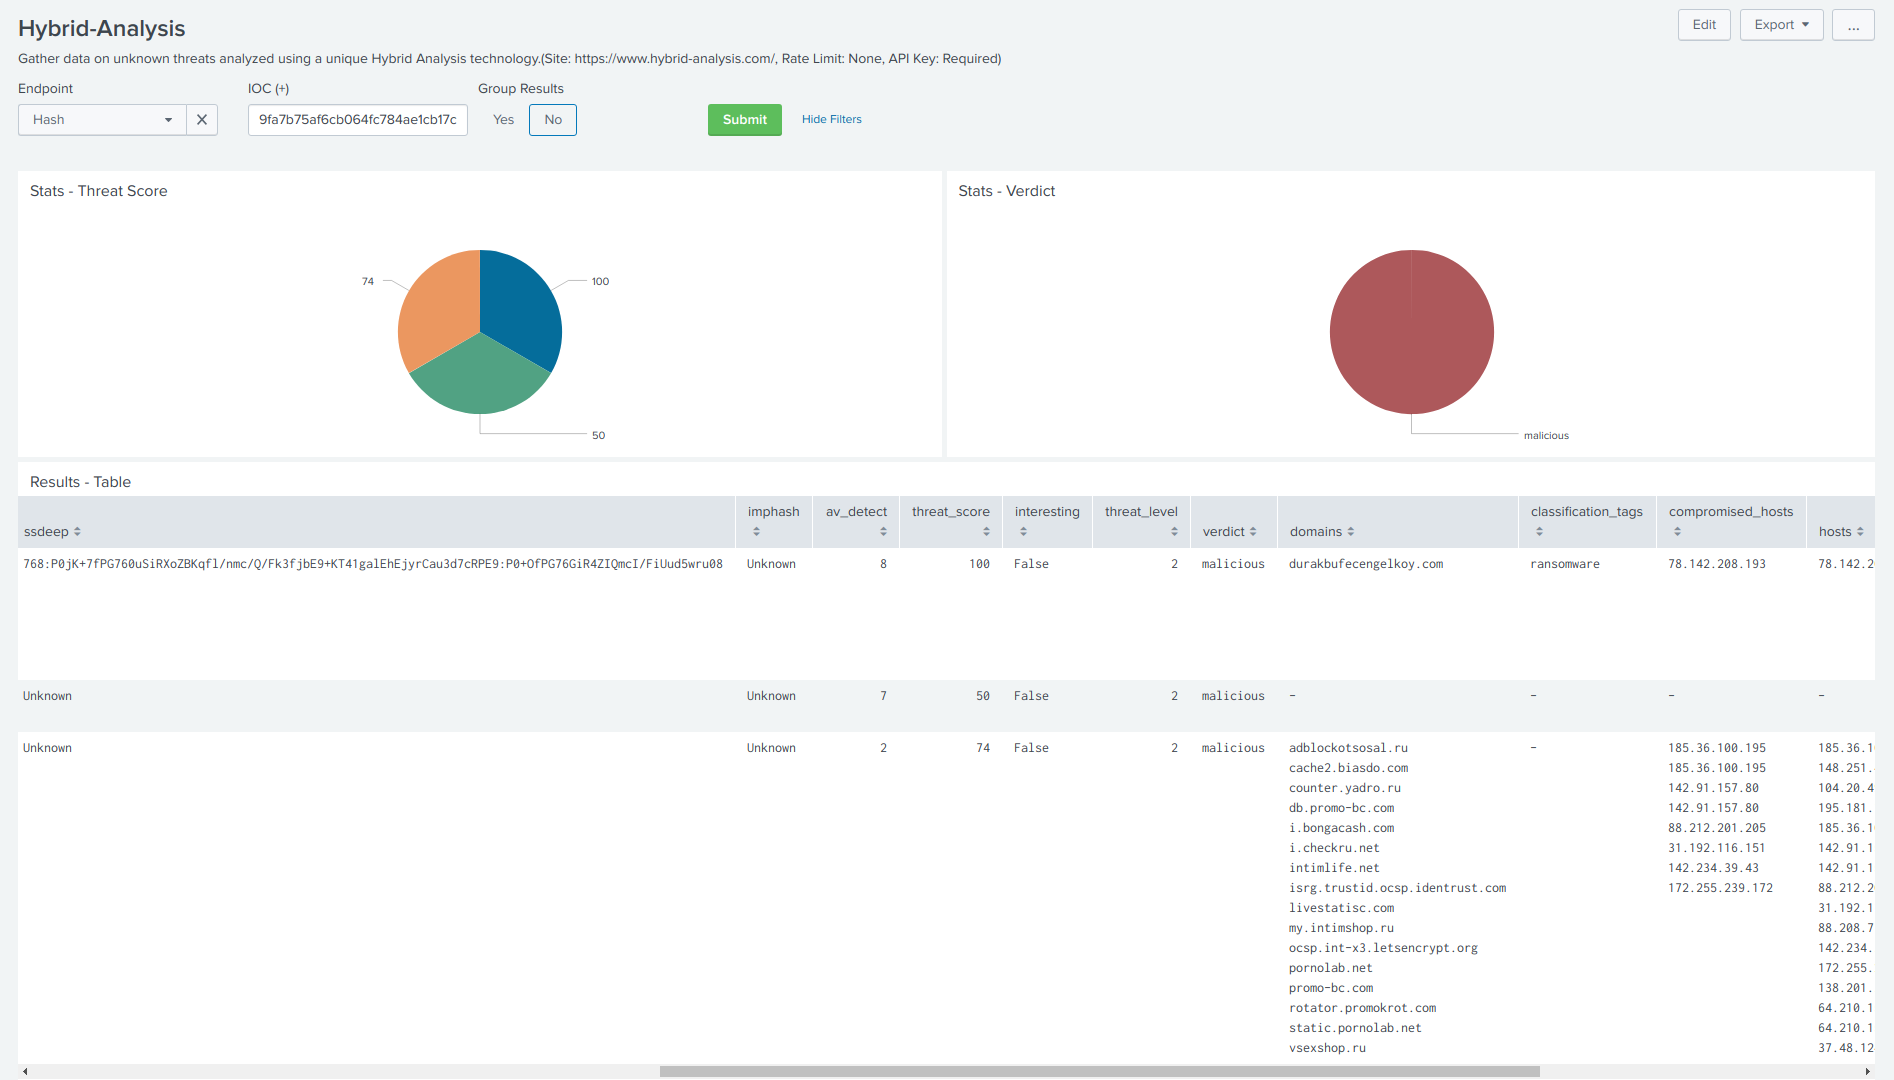
Hybrid-Analysis - Dashboard

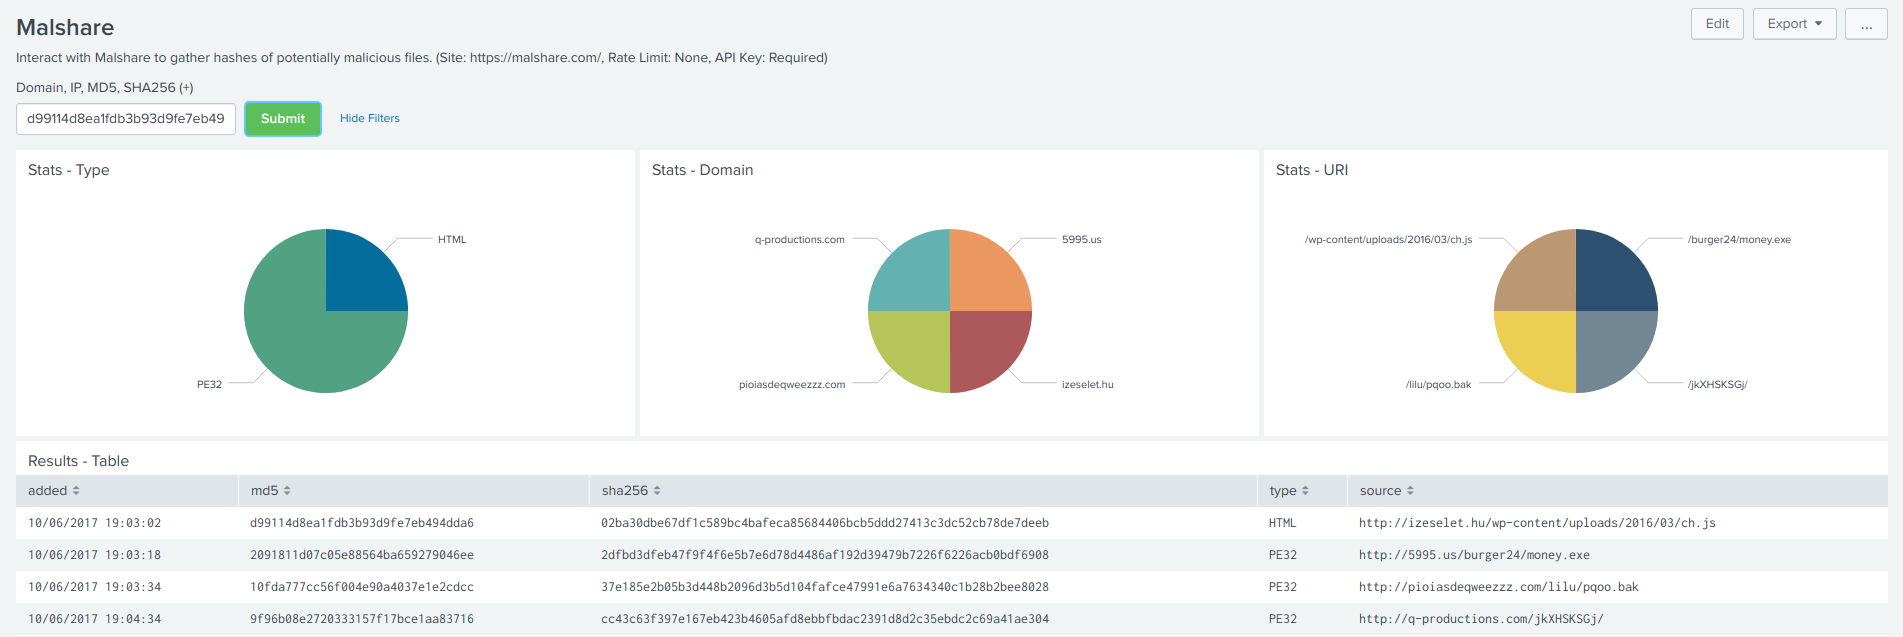
MalShare - Dashboard

Phishing Catcher - Dashboard
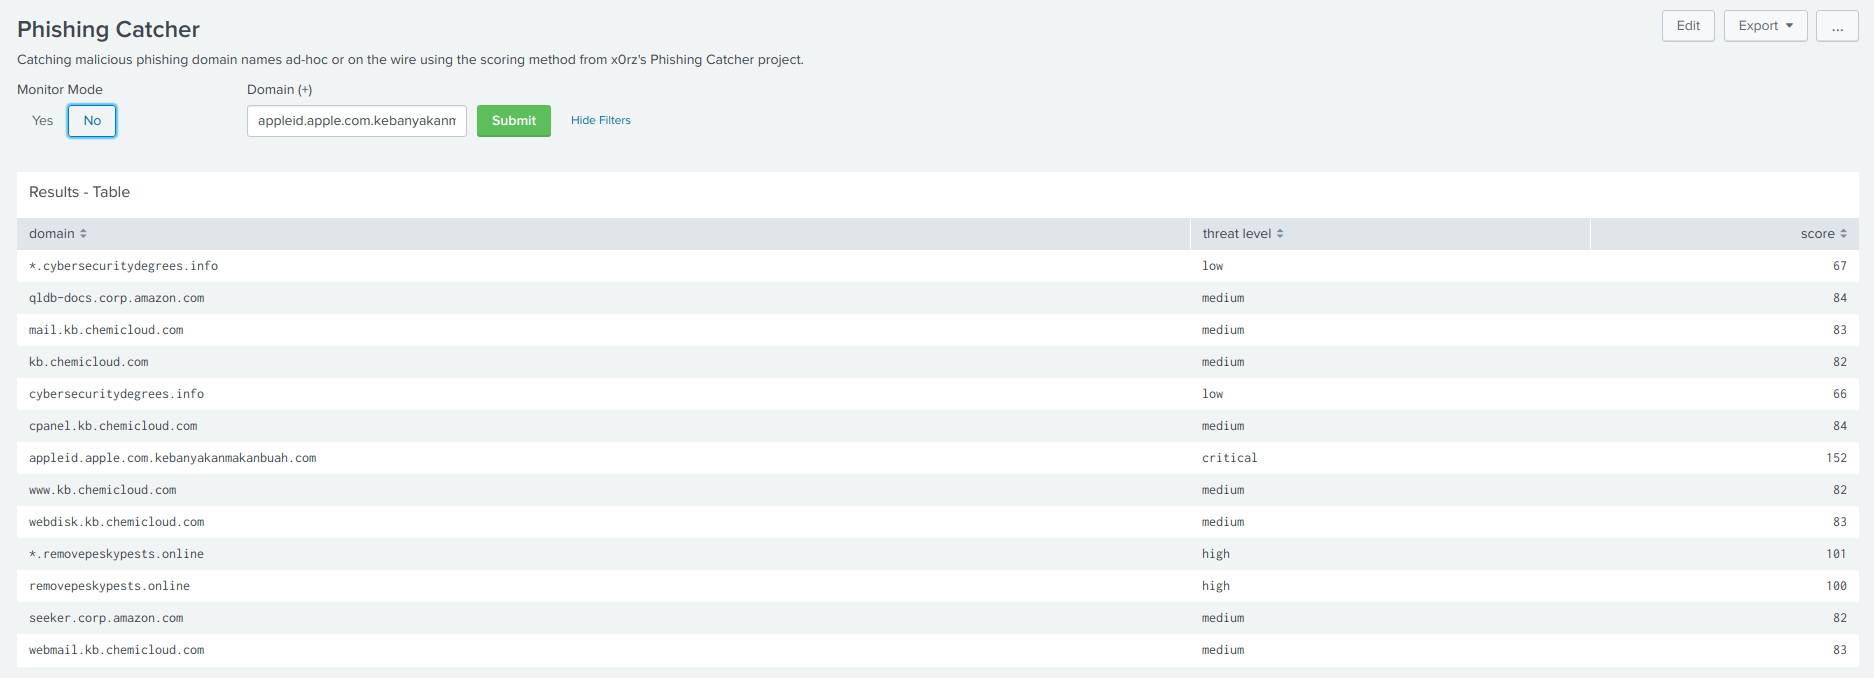

Phishing Kit Tracker - Dashboard

Pastebin Dump - Dashboard

ThreatCrowd - Dashboard ThreatCrowd - Dashboard
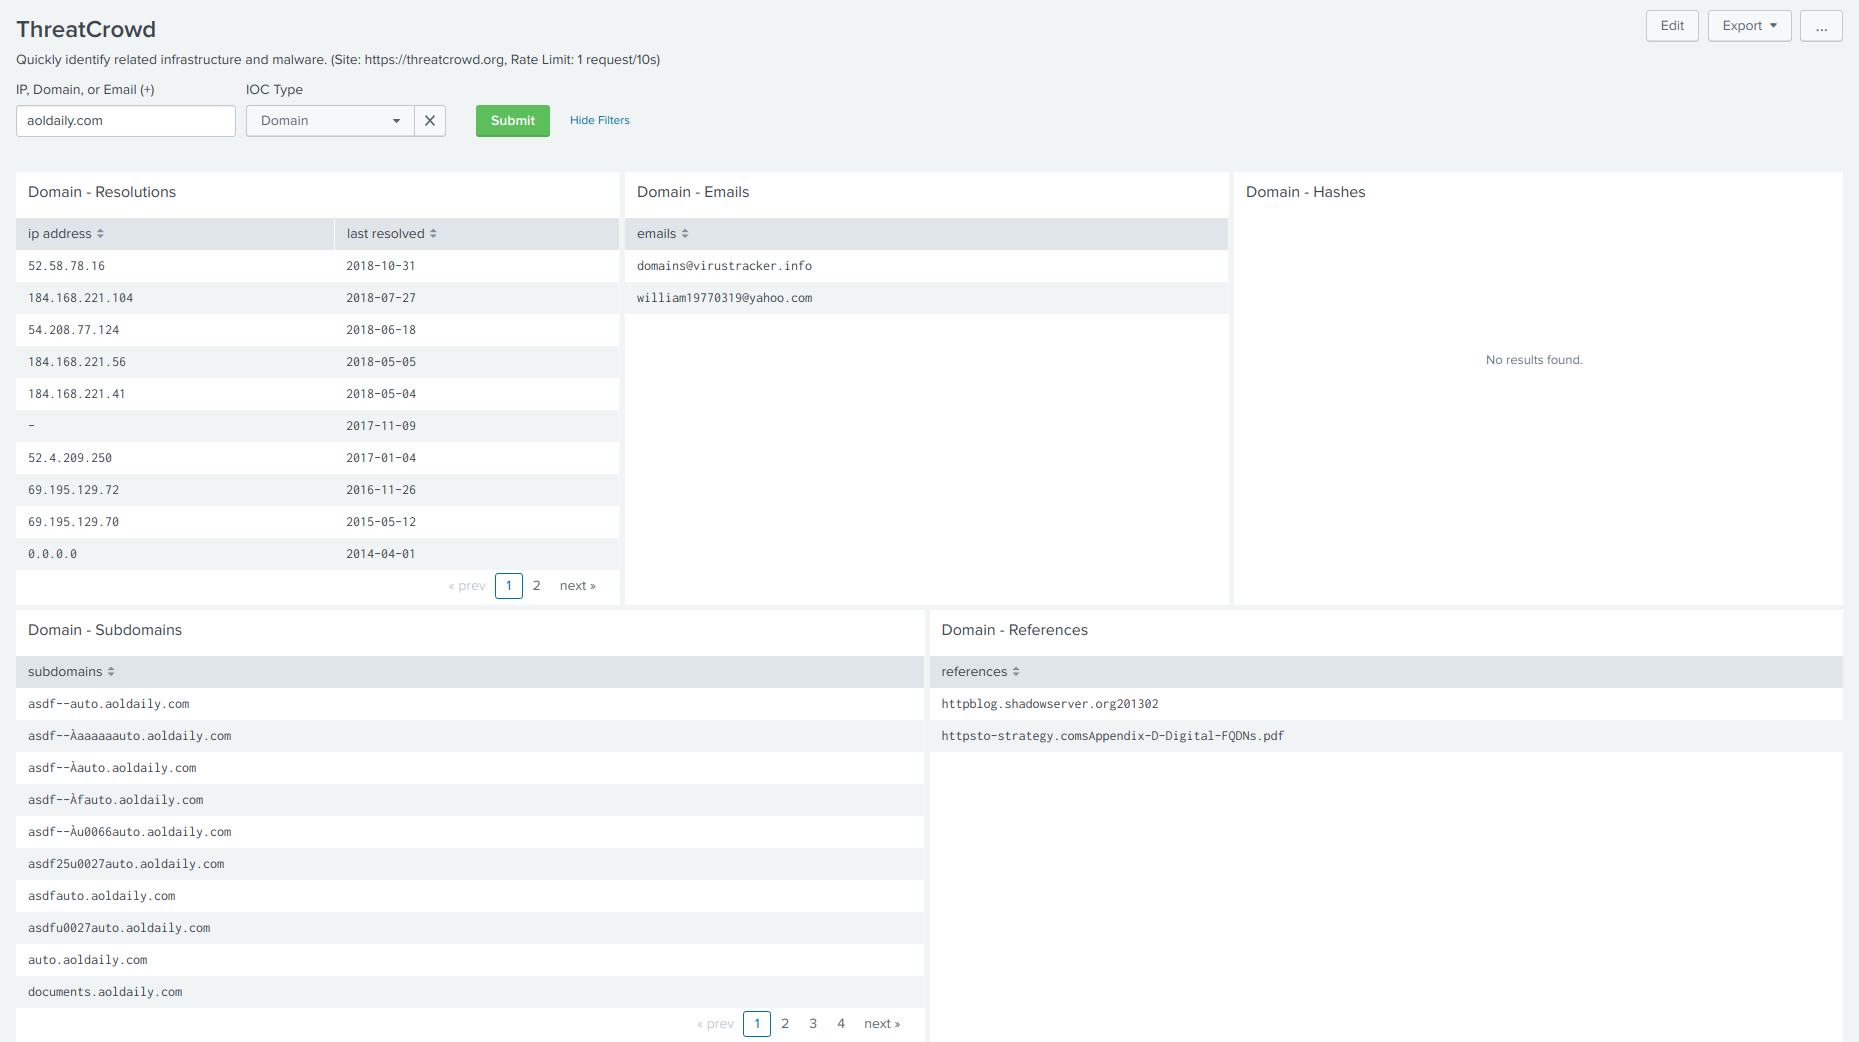
Twitter - Dashboard Twitter - Dashboard

URLhaus - Dashboard URLhaus - Dashboard
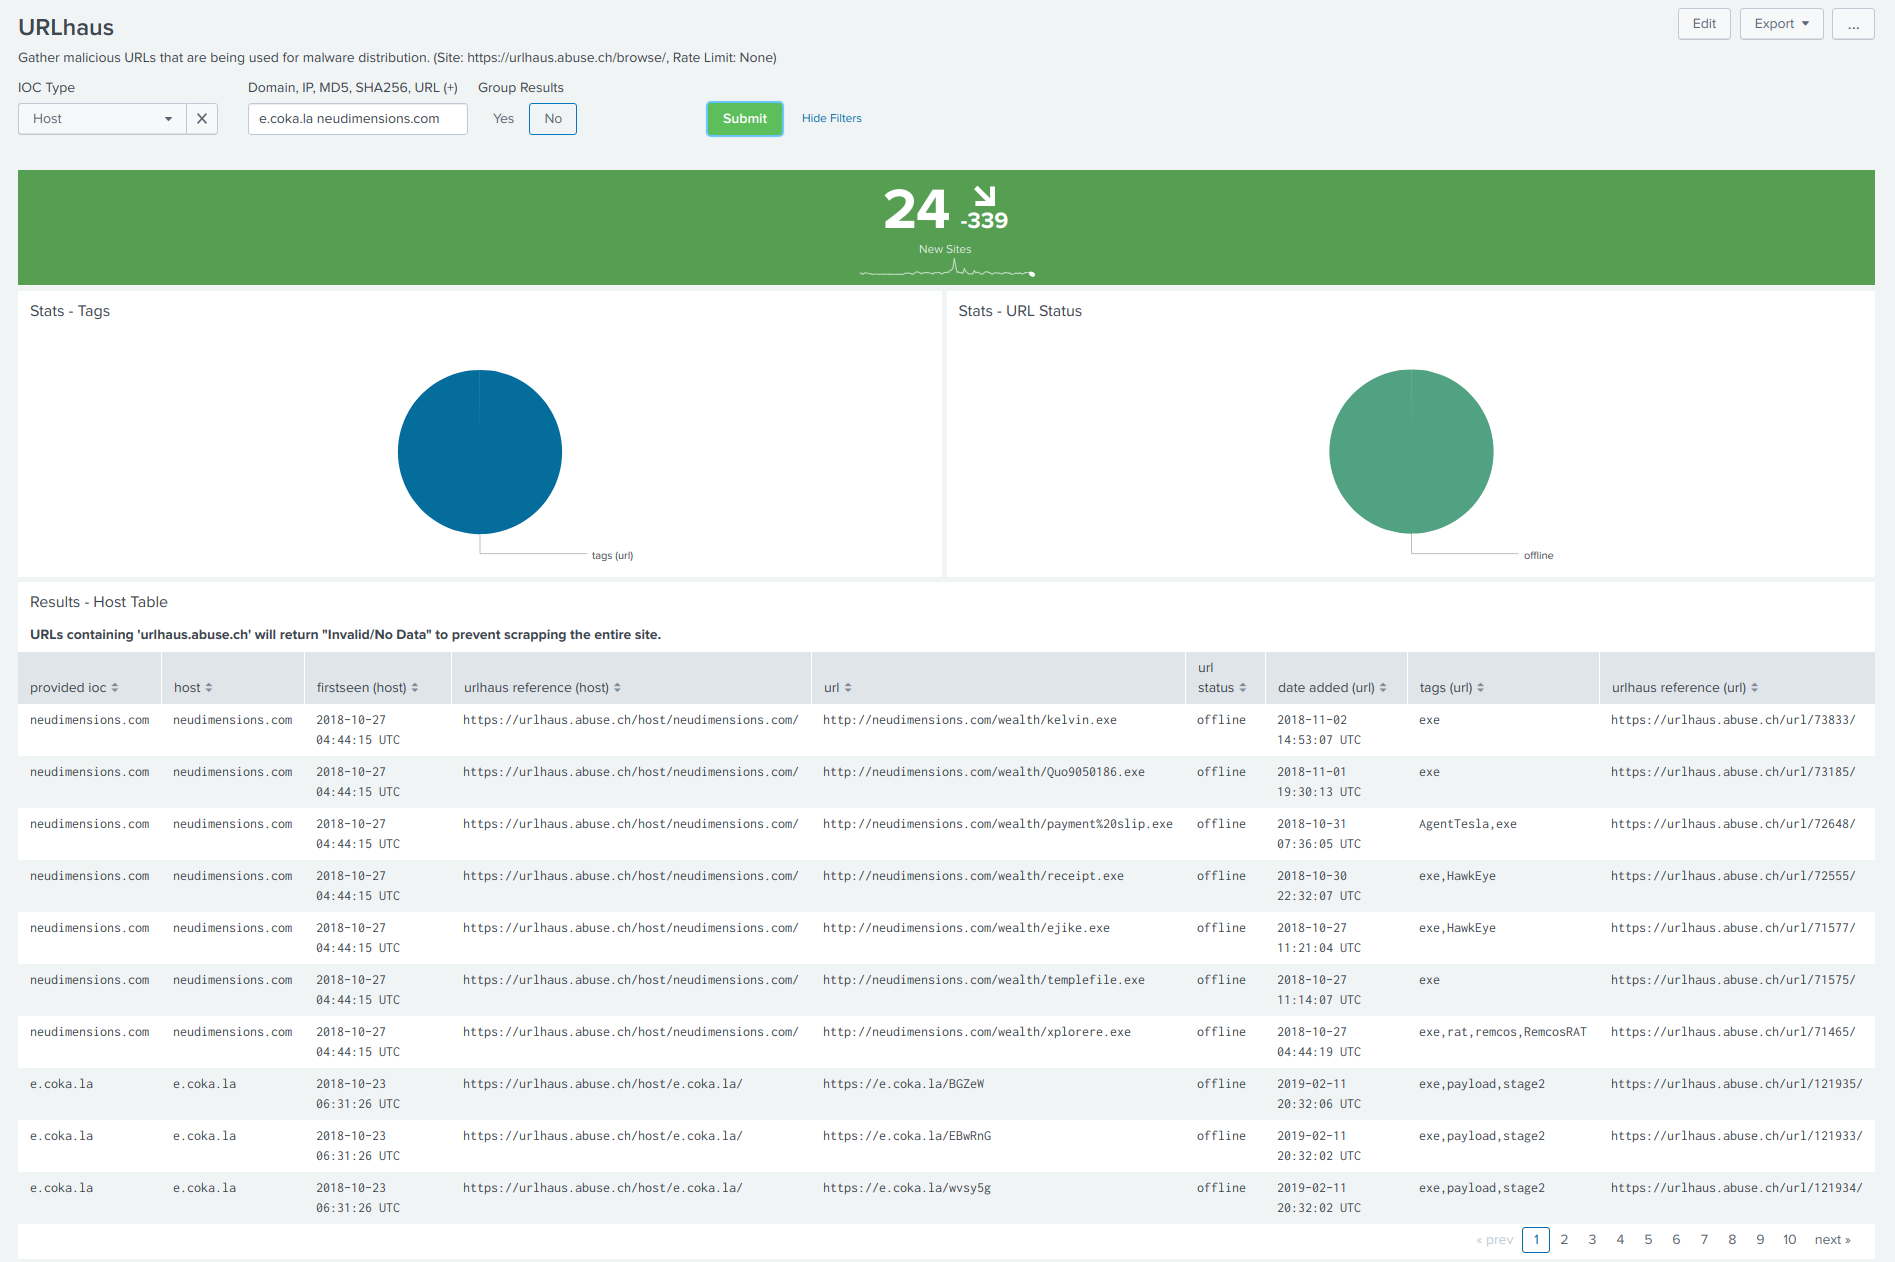
urlscan.io - Dashboard urlscanio - Dashboard
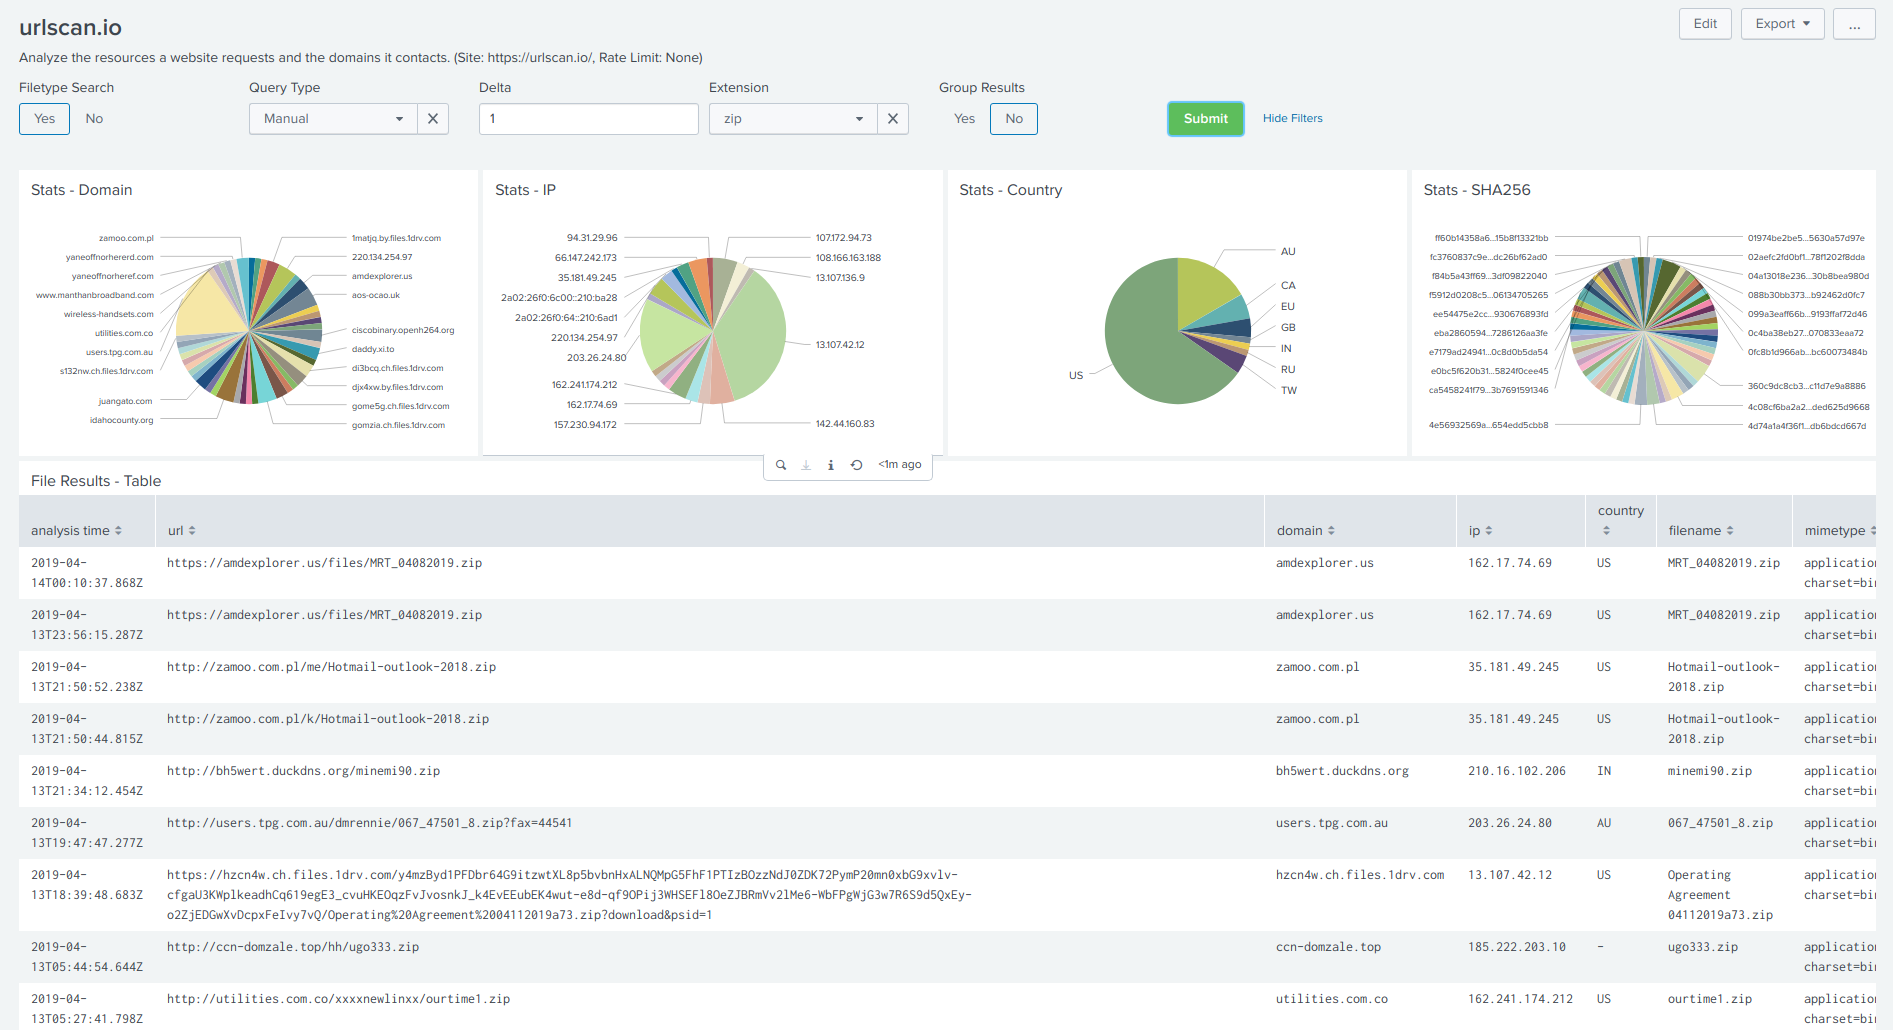
Dashboards Coming Soon

  • Alienvault
  • Censys
  • PulseDive

Please fork, create merge requests, and help make this better.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    831
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    534
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    284
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    275

Explore all tools

Browse our collection of tools

View all tools →





