
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.



Aikido Device Protection builds on Safe Chain, extending package and extension security across more ecosystems: npm, PyPI, VS Code, Open VSX - (Cursor, Windsurf, Kiro, Vs Codium, ...), Maven, NuGet, Chrome extensions, Go, Skills.sh AI skills, Ruby, Rust, and more.
Get centralized policy management, request-and-approval workflows, and visibility across every developer workstation in your org. Powered by the same Aikido Intel feed. Deploy it manually or manage it through your MDM tool (Jamf, Fleet, or Iru).
Aikido Safe Chain supports the following package managers:
Installing the Aikido Safe Chain is easy with the installation script.
curl -fsSL https://github.com/AikidoSec/safe-chain/releases/download/1.5.27/install-safe-chain.sh -o /tmp/install-safe-chain.sh \
  && echo "600ebddcb3aaf1fd53653a8d7985df44528722c0f5ee7eb9fff86f26a1a4e5a8  /tmp/install-safe-chain.sh" | sha256sum -c - \
  && sh /tmp/install-safe-chain.sh \
  && rm /tmp/install-safe-chain.sh
$installer = Join-Path $env:TEMP "install-safe-chain.ps1"
Invoke-WebRequest "https://github.com/AikidoSec/safe-chain/releases/download/1.5.27/install-safe-chain.ps1" -OutFile $installer -UseBasicParsing
$expectedHash = "9B9F329CB3E6EFC3B1BFB8B0B791F546FA52AC6CA791C8E9961C5830936D64F3"
if ((Get-FileHash $installer -Algorithm SHA256).Hash -ne $expectedHash) {
    Remove-Item $installer -ErrorAction SilentlyContinue
    throw "Checksum verification failed for install-safe-chain.ps1"
}
& $installer
Remove-Item $installer
The install commands above always reference a specific release. To install a different version, replace the version with your desired version number. All available versions are on the releases page.
The install scripts are served from a versioned release URL (releases/download/1.5.27/...). GitHub releases are immutable — once an artifact is published at a versioned URL it cannot be modified or replaced, so the file you download is guaranteed to be exactly what was released.
❗Restart your terminal to start using the Aikido Safe Chain.
Verify the installation by running the verification command:
npm safe-chain-verify
pnpm safe-chain-verify
pip safe-chain-verify
uv safe-chain-verify

# Any other supported package manager: {packagemanager} safe-chain-verify
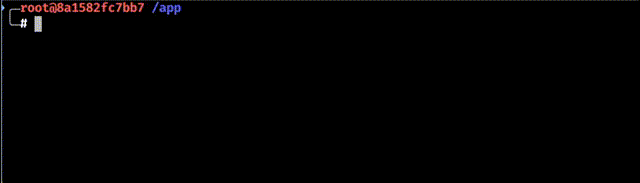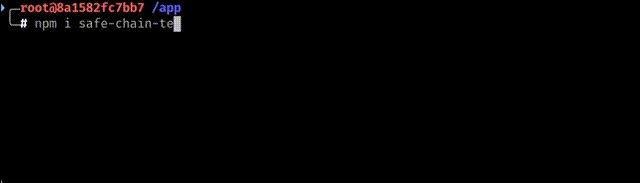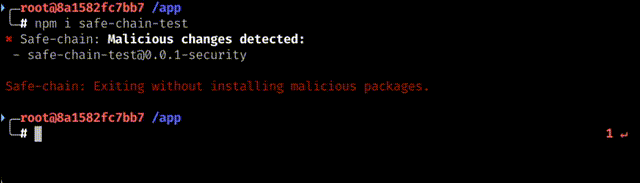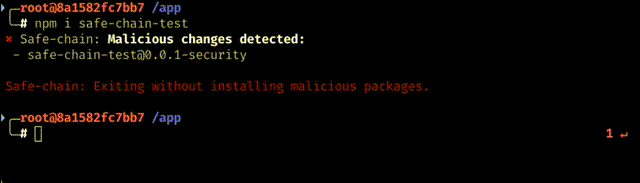
(Optional) Test malware blocking by attempting to install a test package:
For JavaScript/Node.js:
npm install safe-chain-test
For Python:
pip3 install safe-chain-pi-test
When running npm, npx, yarn, pnpm, pnpx, rush, rushx, bun, bunx, pip, pip3, uv, uvx, poetry, pipx and pdm commands, the Aikido Safe Chain will automatically check for malware in the packages you are trying to install. It also intercepts Python module invocations for pip when available (e.g., python -m pip install ..., python3 -m pip download ...). If any malware is detected, it will prompt you to exit the command.
You can check the installed version by running:
safe-chain --version
The Aikido Safe Chain works by running a lightweight proxy server that intercepts package downloads from the npm registry and PyPI. When you run npm, npx, yarn, pnpm, pnpx, rush, rushx, bun, bunx, pip, pip3, uv, uvx, poetry, pipx or pdm commands, all package downloads are routed through this local proxy, which verifies packages in real-time against Aikido Intel - Open Sources Threat Intelligence. If malware is detected in any package (including deep dependencies), the proxy blocks the download before the malicious code reaches your machine.
Safe Chain applies minimum package age checks to supported ecosystems.
Current enforcement differs by ecosystem:
By default, the minimum package age is 48 hours. This provides an additional security layer during the critical period when newly published packages are most vulnerable to containing undetected threats. You can configure this threshold or bypass this protection entirely - see the Minimum Package Age Configuration section below.
For urgent CVE fixes, Aikido confirms the patch release is free of malware and Safe Chain exempts it from the minimum age check, so you're not left exposed to the vulnerability it fixes while waiting out the window.
The Aikido Safe Chain integrates with your shell to provide a seamless experience when using npm, npx, yarn, pnpm, pnpx, rush, rushx, bun, bunx, and Python package managers (pip, uv, uvx, poetry, pipx, pdm). It sets up aliases for these commands so that they are wrapped by the Aikido Safe Chain commands, which manage the proxy server before executing the original commands. We currently support:
More information about the shell integration can be found in the shell integration documentation.
To uninstall the Aikido Safe Chain, use our one-line uninstaller:
curl -fsSL https://github.com/AikidoSec/safe-chain/releases/download/1.5.27/uninstall-safe-chain.sh | sh







