
oxo
 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
devsecopsmobile-securitynetwork-security+3
5802h 15m ago
ostorlab/oxoModular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
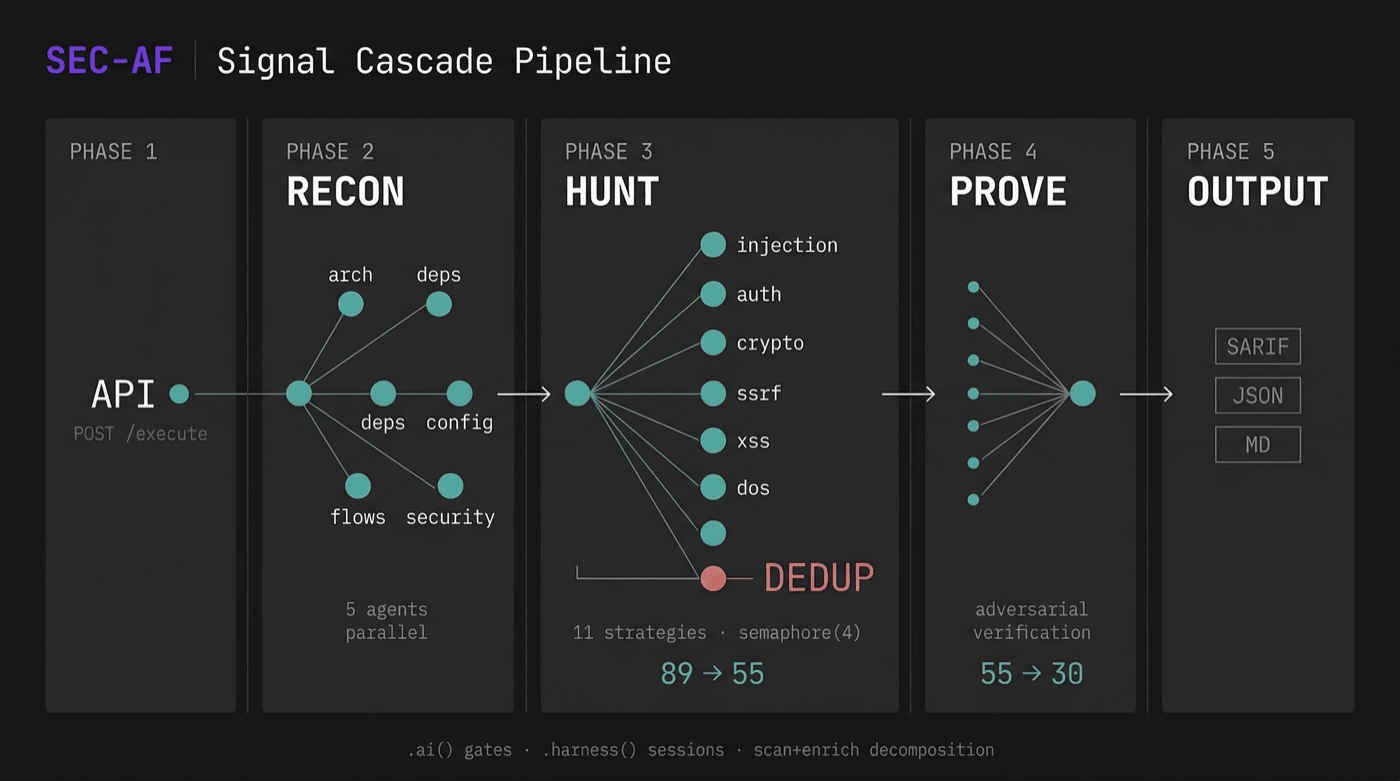 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 0sec-labs/0
Open-source AI security harness. Includes a web UI for code analysis, pentesting, vulnerability research, reverse engineering, verification, and…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
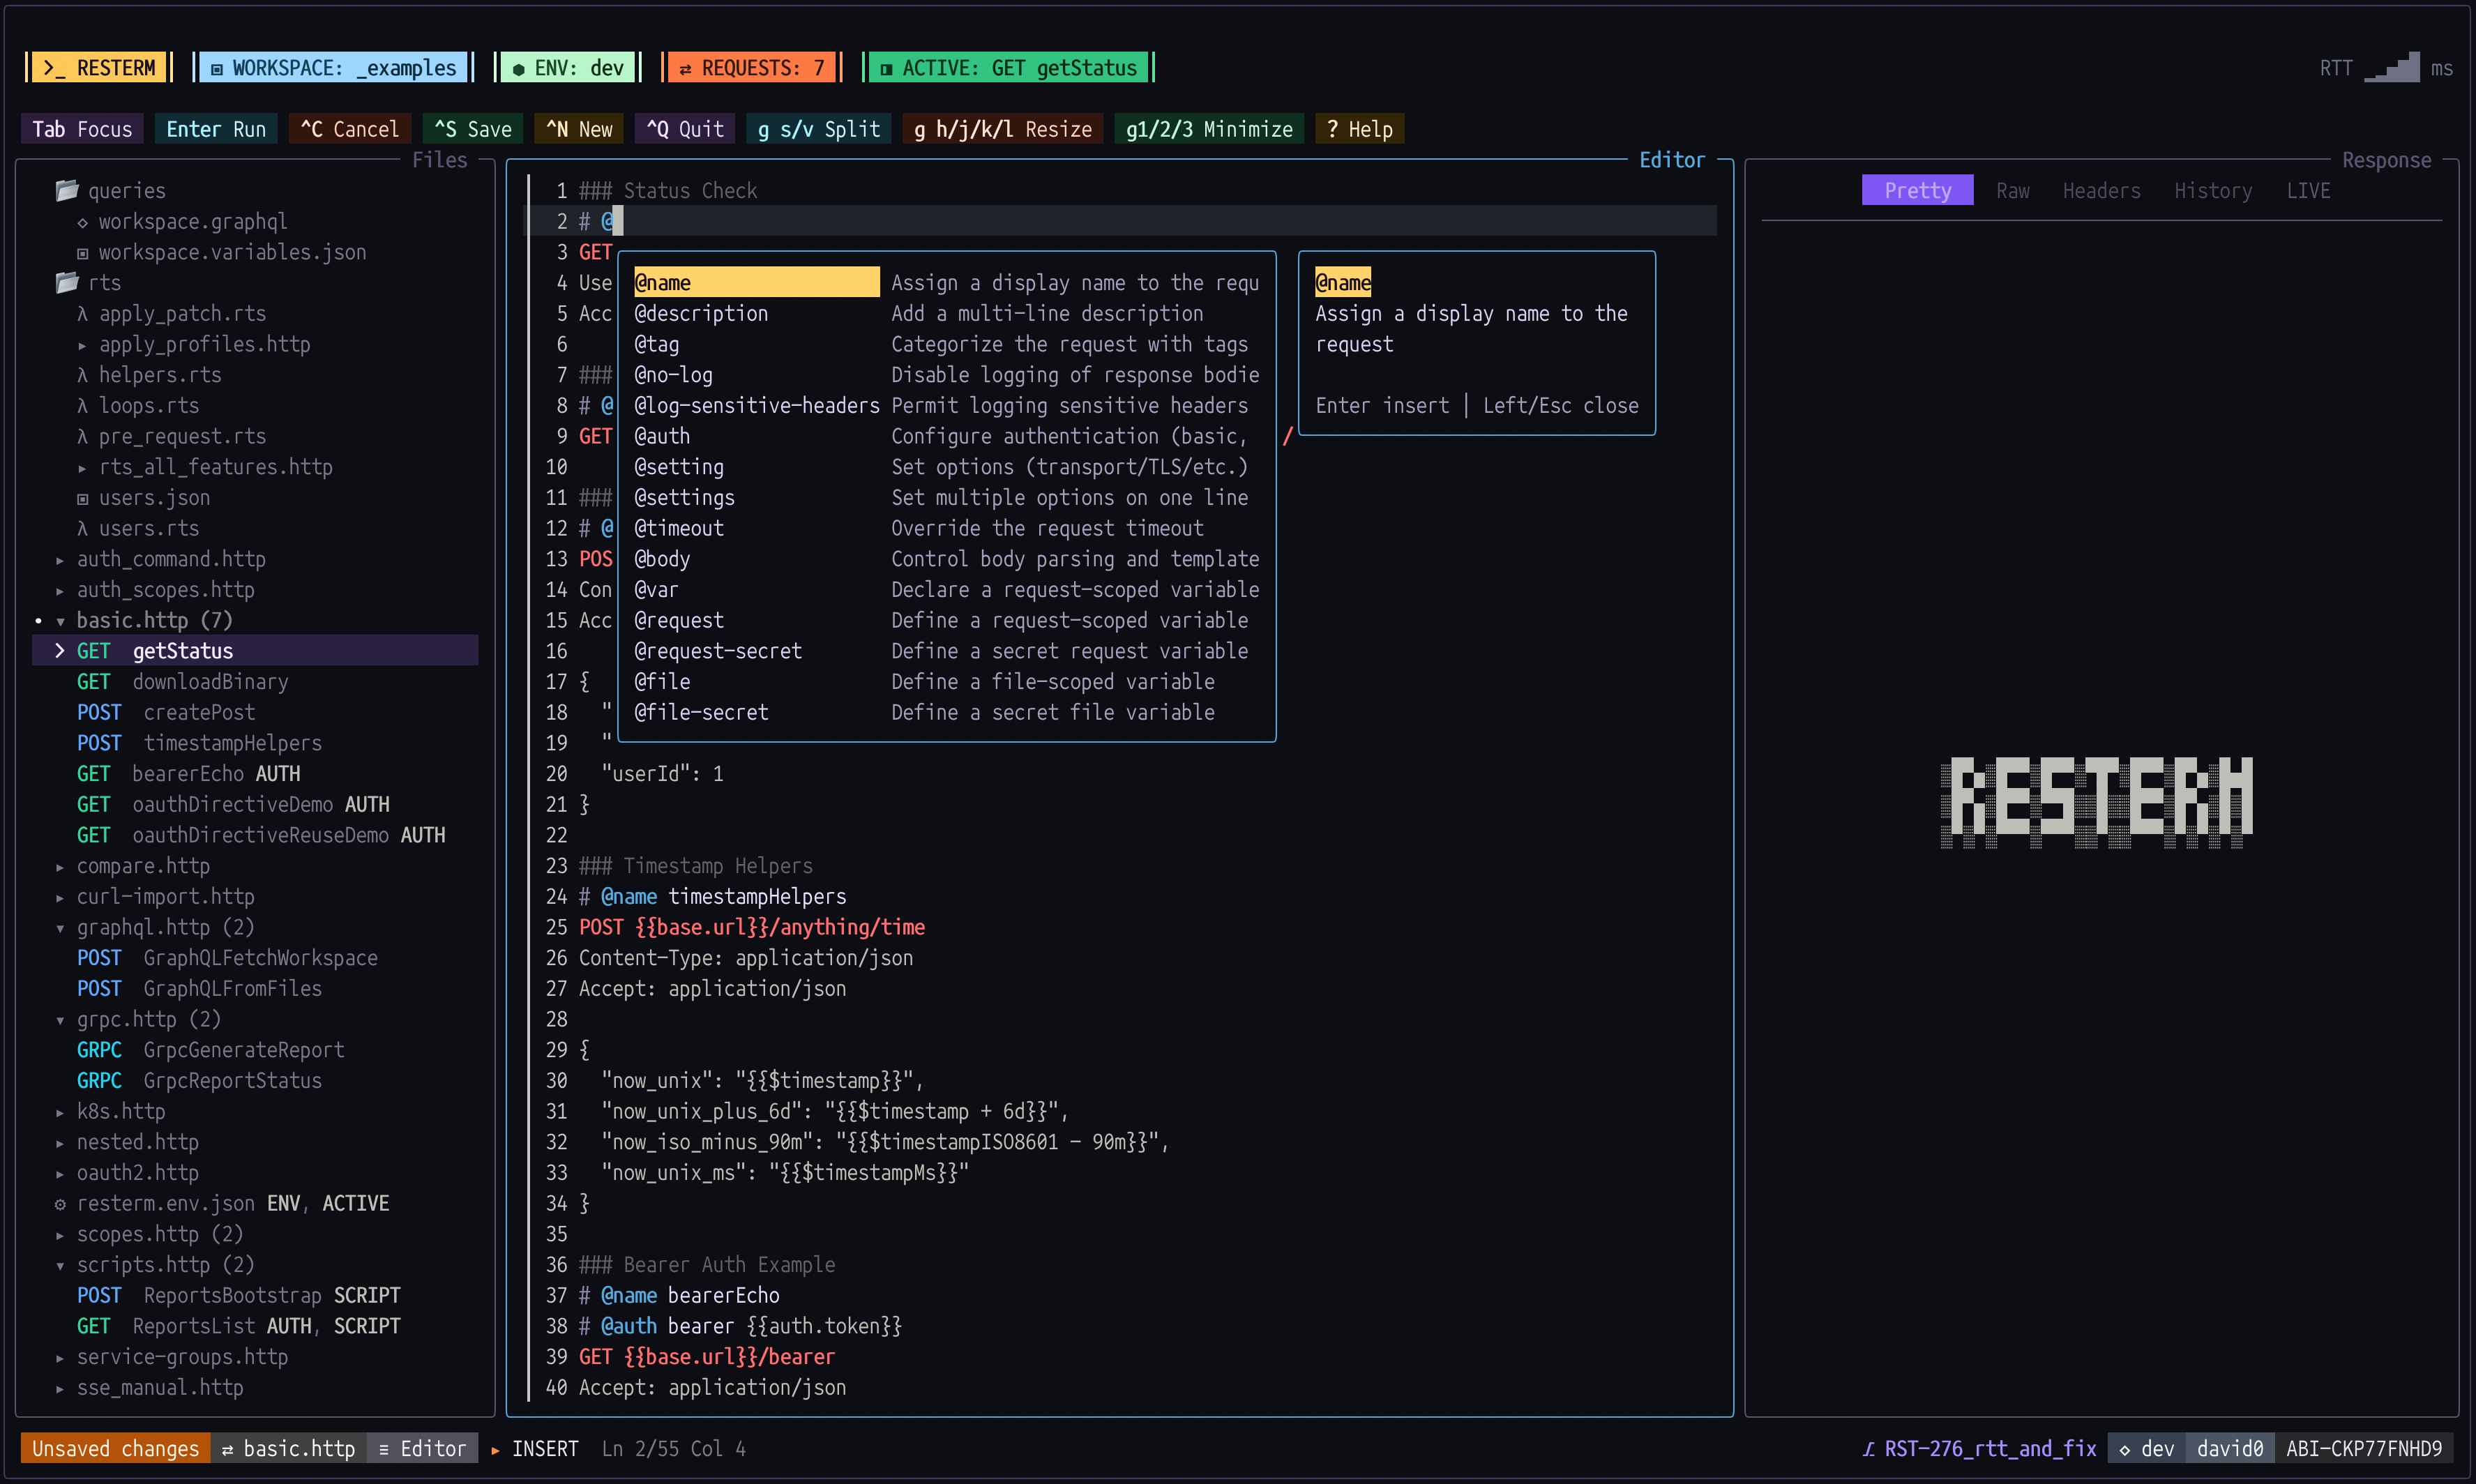 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 infobyte/faraday
Open-source and AI-powered cybersecurity tools for offensive security, vulnerability management, and autonomous pentesting. Built by hackers in Latin…
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
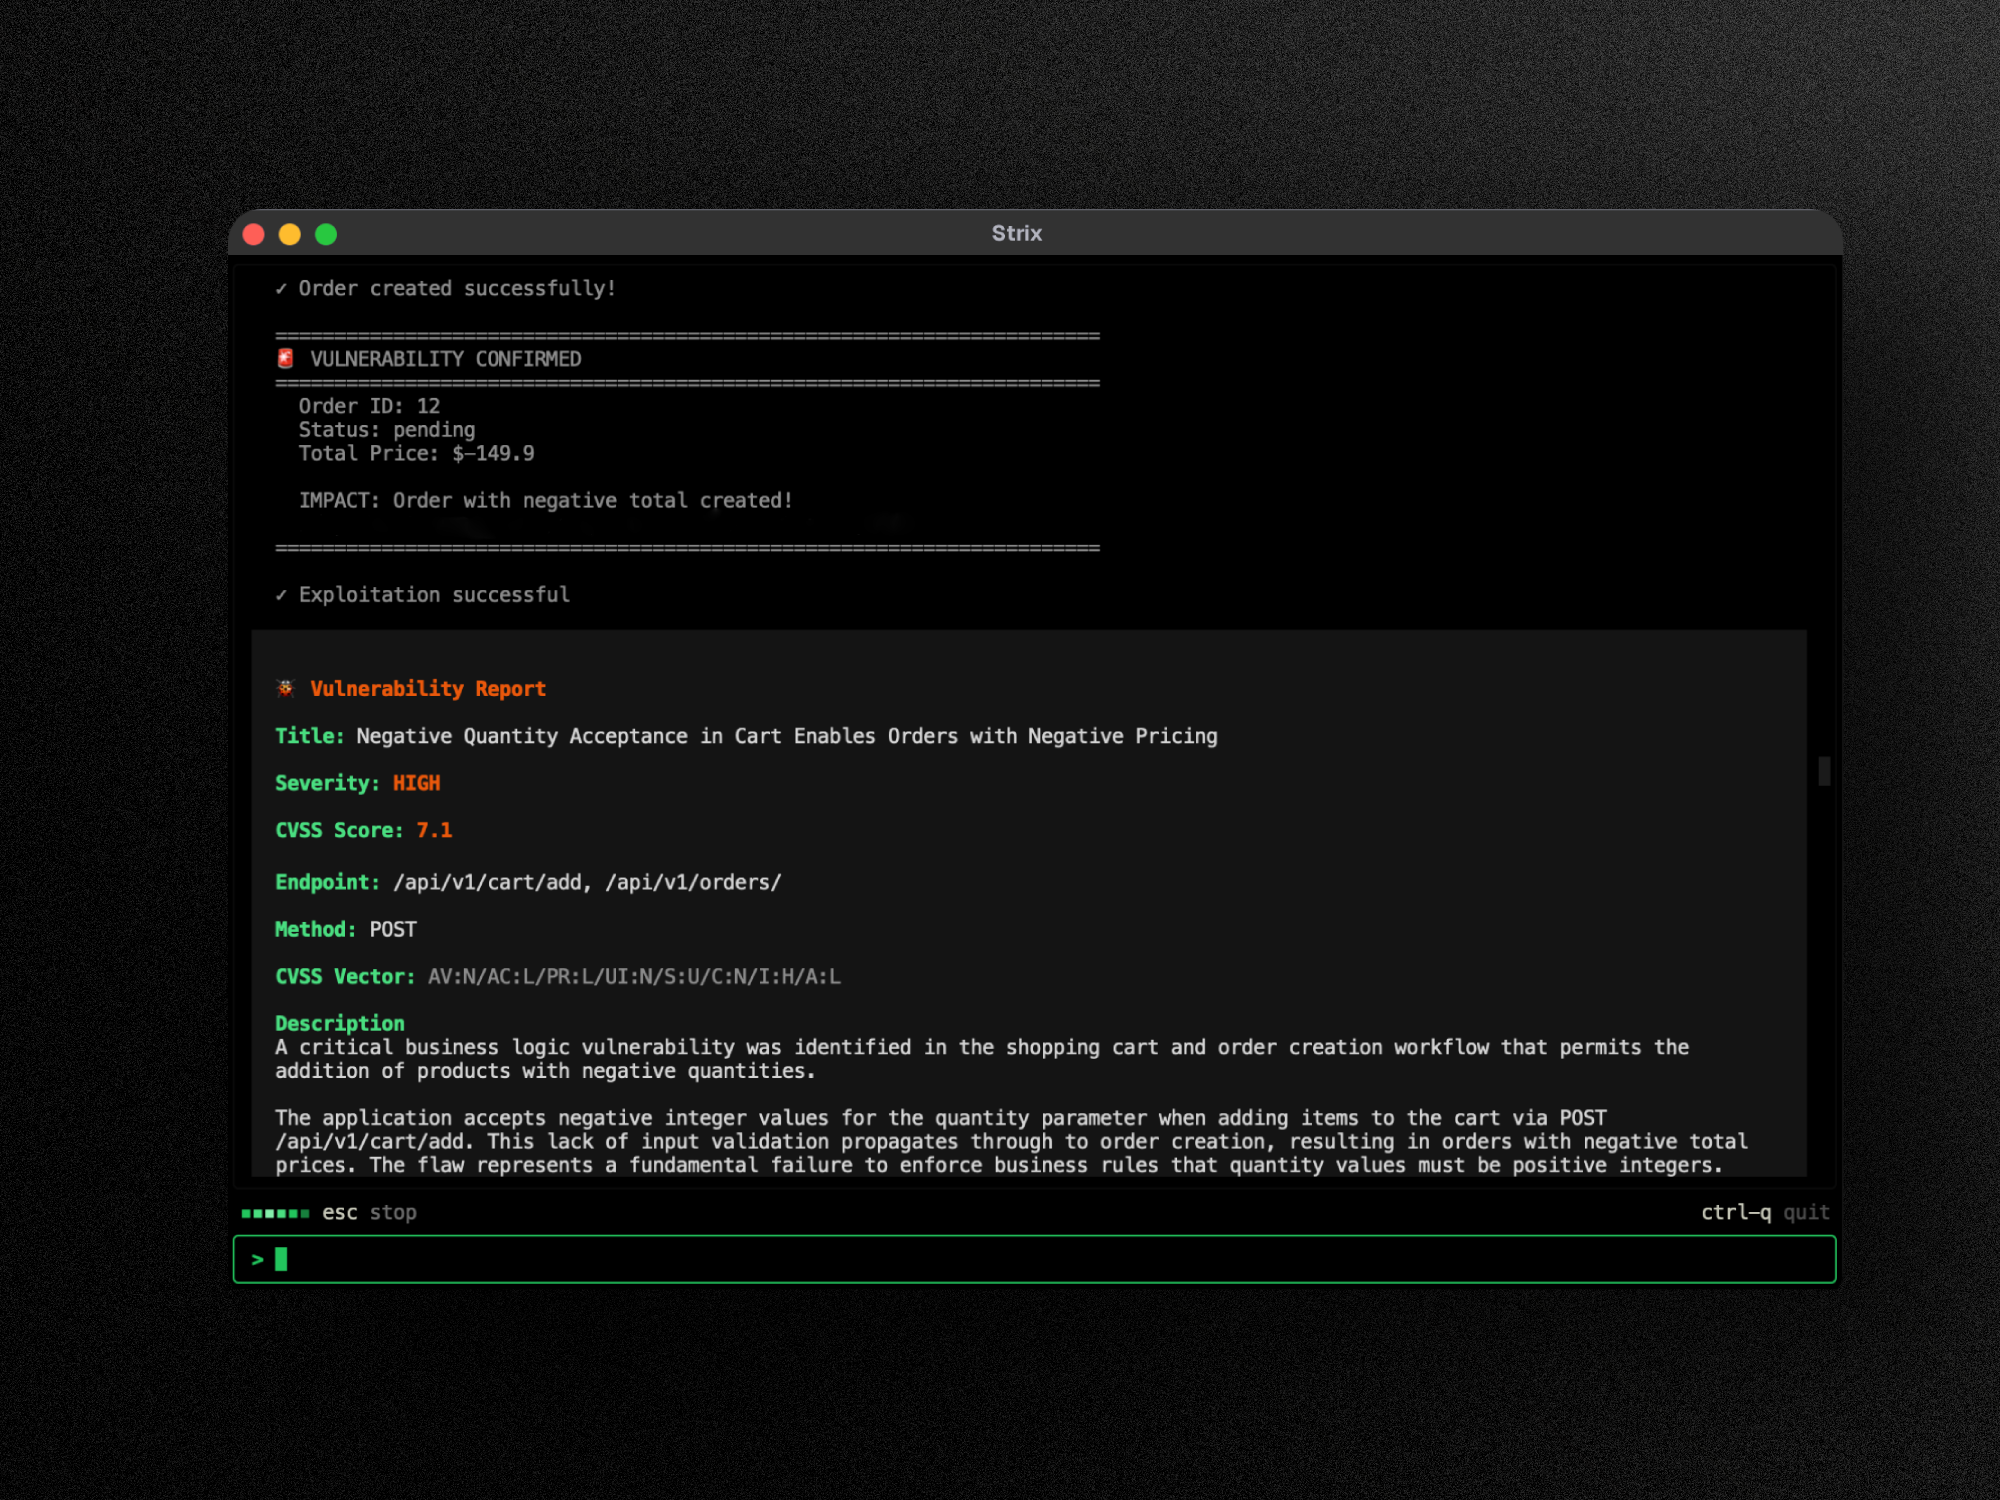 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.