Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
0 — Software infrastructure to build and deploy sovereign, persistent AI security agents that continuously find, prove and fix security risks. Open source. Web UI, CLI, CI and MCP. | Kitploit
Tools/GitHubGitHub/0sec-labs/0
Static AnalysisVulnerability ScannersVulnerability AnalysisFuzzingPenetration TestingDevSecOpsBinary AnalysisRed TeamingAI Security
GitHub0sec-labs/0

0

Software infrastructure to build and deploy sovereign, persistent AI security agents that continuously find, prove and fix security risks. Open source. Web UI, CLI, CI and MCP.

1.4k1931948h 42m agoReviewed by Kitploit
View RepositoryWebsite
Share

0security

Sovereign AI security agents

By the Swiss Applied AI & Cybersecurity Research Lab

Backed by Y Combinator
Latest release MIT or Apache-2.0 license GitHub stars

0security is software infrastructure to deploy sovereign, persistent AI security agents that find and fix security risks across any tech stack, work with any model, and run anywhere.

Documentation Security research Install locally Enterprise

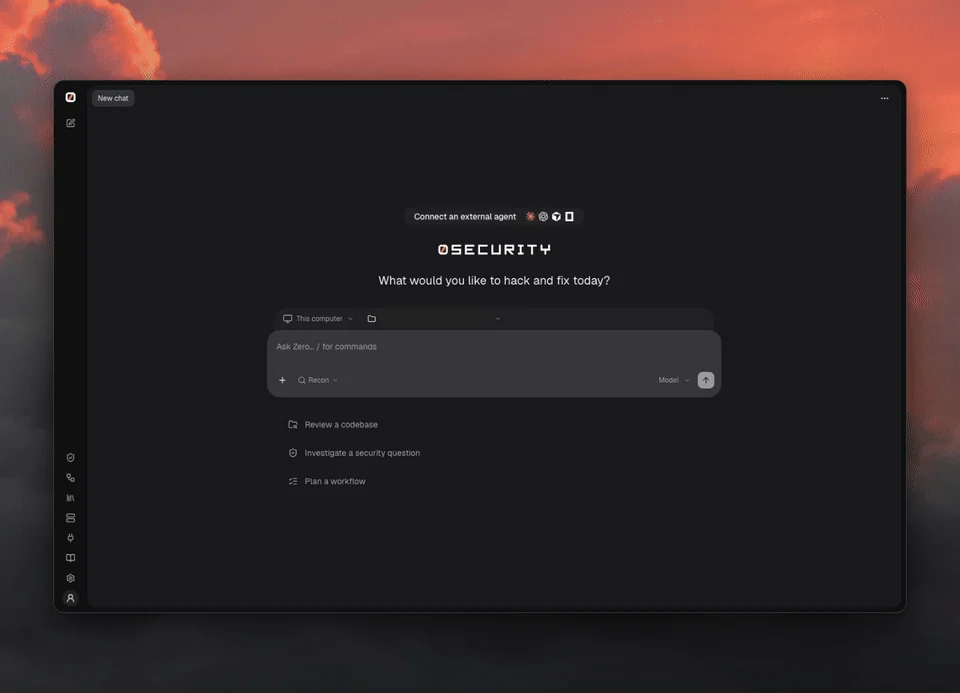
0 web UI: review a demo API, watch the investigation, then open findings with suggested fixes and verification

Quick start

curl -fsSL https://raw.githubusercontent.com/0sec-labs/0security/main/install.sh | bash
0

Prefer the terminal?

export OPENAI_API_KEY="your-api-key"
0 threads send new "Review ./your-repo for security problems"
0 findings list

Any supported provider works: set its key instead (Anthropic, OpenRouter, DeepSeek and more, see Models), or connect one in the browser with 0.

Windows, Docker and source installs
  • Windows (experimental): download 0-windows-x64.exe from Releases.
  • Docker: docker run --rm ghcr.io/0sec-labs/0security:latest --help. See the Docker guide.
  • Source: Node.js 24+ and pnpm, then pnpm install --frozen-lockfile && pnpm build.
  • install.sh supports Apple Silicon macOS and x64/ARM64 Linux. Set INSTALL_DIR to change the location.

Only point 0 at systems you own or are authorized to test. See Scope.
What can you do with 0?

  • Talk to a security agent about a folder on your computer or a remote Computer, in a Thread
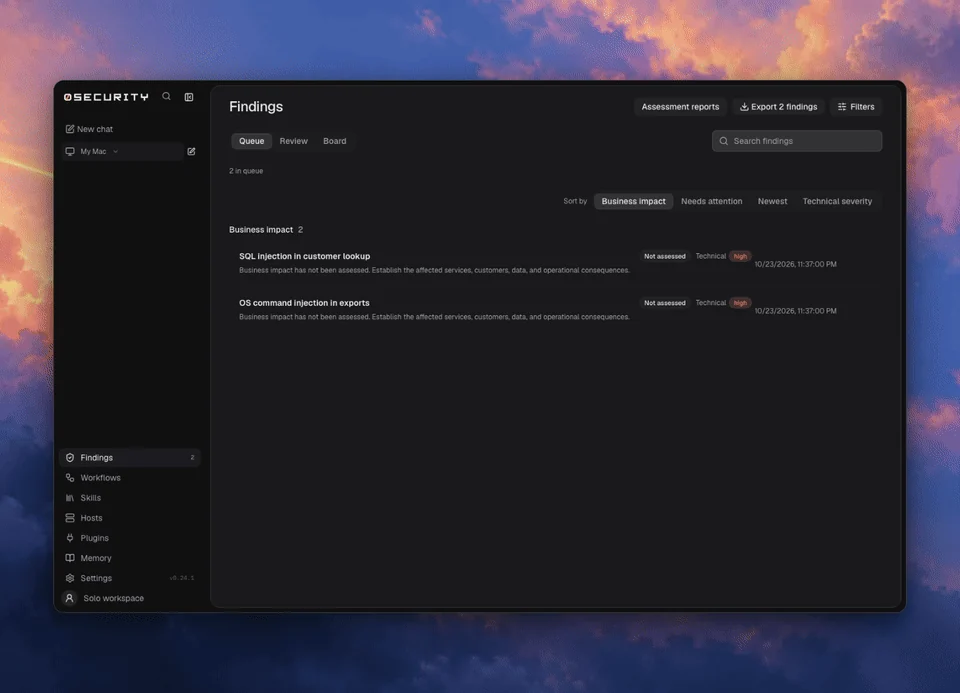
  • Review findings on a board, with source evidence, and export them
  • Verify fixes: a finding is marked Verified by or Not verified
  • Build persistent security agents: Agents are standing threads that wake on a schedule or on every pull request, with skills, memory and automations written as prompts
  • Keep memory as plain notes that every thread can read
  • Extend it with extensions and skills, or drive it from coding agents over MCP

0 findings: review the queue, organize the board, and inspect source evidence

Why 0?

  • Open source: MIT or Apache-2.0, built in the open
  • Private: runs on your computer, in your CI or in a container, and only the context you send to your chosen model leaves it
  • Flexible: any provider key or local OpenAI-compatible server, from the CLI, CI or a coding agent over MCP
  • Evidence first: every finding links to its source evidence
  • Verified: a finding says whether it was verified, and by what
  • Proven in public: disclosed vulnerabilities and upstream fixes, including in the Linux kernel

Coding agents

0 agents run <id> --task "Review this pull request" --yes
0 lab mcp-server --automations --workspace /absolute/path/to/repo

See extensions and MCP and the command reference.

Learn more

  • Documentation
  • Models and providers
  • Extensions and MCP
  • Command reference
  • Security research
  • Enterprise

Contributing

0 is built in the open. Huge thanks to everyone who has filed a bug, fixed a doc or sent a patch.

  • Report bugs in issues
  • Improve the docs
  • Write an extension or a skill
  • Found a vulnerability in 0? See SECURITY.md

Start with the contributing guide. Run pnpm install and pnpm dev to work on the engine. Open an issue before large changes.

Contributors to 0sec-labs/0security

License

MIT OR Apache-2.0. Public disclosures and upstream fixes.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

No popularity data yet.

Explore all tools

Browse our collection of tools

View all tools →