
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
django-DefectDojo — Open-Source Unified Vulnerability Management, DevSecOps & ASPM | Kitploit

Tools/GitHubGitHub/defectdojo/django-defectdojo
Vulnerability ScannersPenetration TestingDevSecOpsTop in DevSecOps #17
GitHubdefectdojo/django-defectdojo

django-DefectDojo

Open-Source Unified Vulnerability Management, DevSecOps & ASPM
View Repository
4.9k1.9k13412h 51m agoReviewed by Kitploit
Website
Share

DefectDojo

Open-source vulnerability management, DevSecOps and ASPM

Pro demo · Community demo · Docs · Slack · Community · Website

OWASP Flagship GitHub release Unit Tests Integration Tests CII Best Practices YouTube Subscribe Twitter Follow

Open Source Security Index - Fastest Growing Open Source Security Projects

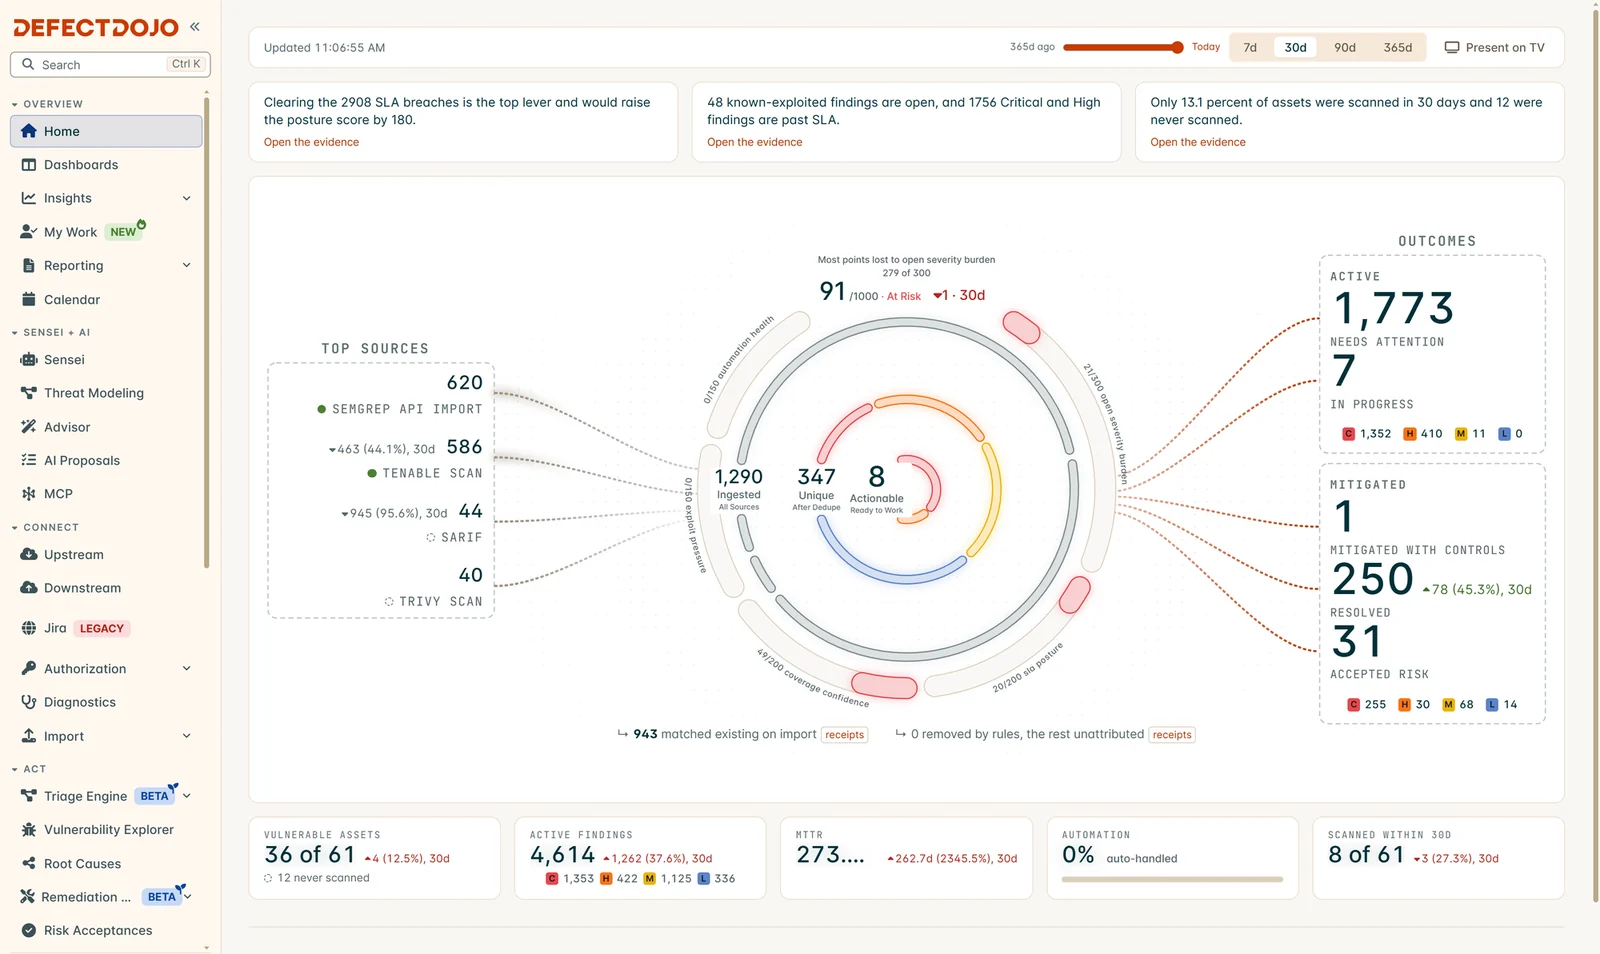
The DefectDojo Pro home page: findings from each scan source, the overall risk score, and outcomes
DefectDojo Pro home page. Try it on the live Pro demo. The Community Edition demo is at demo.defectdojo.org. Sign-in details for both are under Demo.

DefectDojo is a DevSecOps, ASPM (application security posture management), and vulnerability management tool. DefectDojo orchestrates end-to-end security testing, vulnerability tracking, deduplication, remediation, and reporting.

Demo

Pro Edition: pro.demo.defectdojo.com

OWASP Community Edition: demo.defectdojo.org

Either demo environment can be logged into with username admin and password 1Defectdojo@demo#appsec. Please note that the demos are publicly accessible and reset every day. Do not put sensitive data in the demo. An easy way to test DefectDojo is to upload some sample scan reports.

Quick Start for Docker Compose

git clone https://github.com/DefectDojo/django-DefectDojo && cd django-DefectDojo && docker compose up

This quick start guide will do the following

  • Clone the repository and change directories
  • Start the application
  • Obtain admin credentials in the initializer logs. The first initialization can take up to 3 minutes to run.

if running DefectDojo in detached mode via docker compose up -d, obtain admin credentials from the initializer logs with the command below. Please note, the initializer can take up to 3 minutes to run.

docker compose logs initializer | grep "Admin password:"
Documentation

  • Official Docs
  • REST APIs
  • Client APIs and Wrappers
  • Authentication: local accounts in Open Source. SSO (SAML, OIDC, OAuth), LDAP, and MFA are DefectDojo Pro features.
  • Supported tools
  • How to Write Documentation Locally
  • Development

Supported Installation Options

  • Pro - SaaS or self-hosted (via K8s or docker compose). Book a demo, speak to our team or get Pro from $100/mo
  • OS - docker compose

Community, Getting Involved, and Updates

DefectDojo Slack LinkedIn Twitter Youtube

Checkout our new Community Portal and join the DefectDojo community on Slack!

Follow DefectDojo on LinkedIn, YouTube, and X for platform updates!

Contributing

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →