
PPLBlade
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
604
tastypepperoni/pplbladeBypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 nccgroup/solitude
Solitude is a privacy analysis tool that enables anyone to conduct their own privacy investigations. Whether a curious novice or a more advanced…
 shoucheng3/asf__nifi_cve-2023-36542_1-22-0
Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…
 shoucheng3/apache__nifi_cve-2022-33140_1-16-22
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
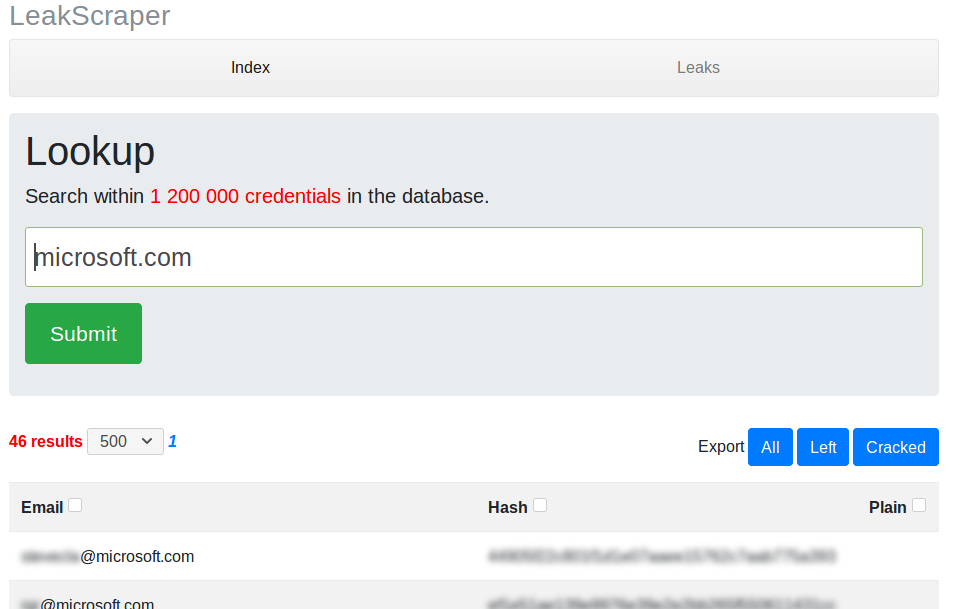 acceis/leakscraper
LeakScraper is an efficient set of tools to process and visualize huge text files containing credentials. Theses tools are designed to help…
 shoucheng3/asf__nifi_cve-2023-34468_1-21-00
Exploit for Apache NiFi CVE-2023-34468, targeting a vulnerability in versions 1.21.0 and earlier to demonstrate data access and system compromise.
 jfriedli/cve-2025-12137
Proof-of-concept exploit for CVE-2025-12137 demonstrating local file disclosure via a WordPress plugin's REST API importer endpoint. Includes…
 pwardle/not-a-mused
Proof-of-concept exploiting an undocumented Muse dictation endpoint setting, letting a local unprivileged process redirect dictation traffic to…
 c6fc/warcannon
High speed/Low cost CommonCrawl RegExp in Node.js
 reverseclabs/physmem2profit
Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely
 xaitax/chrome-app-bound-encryption-decryption
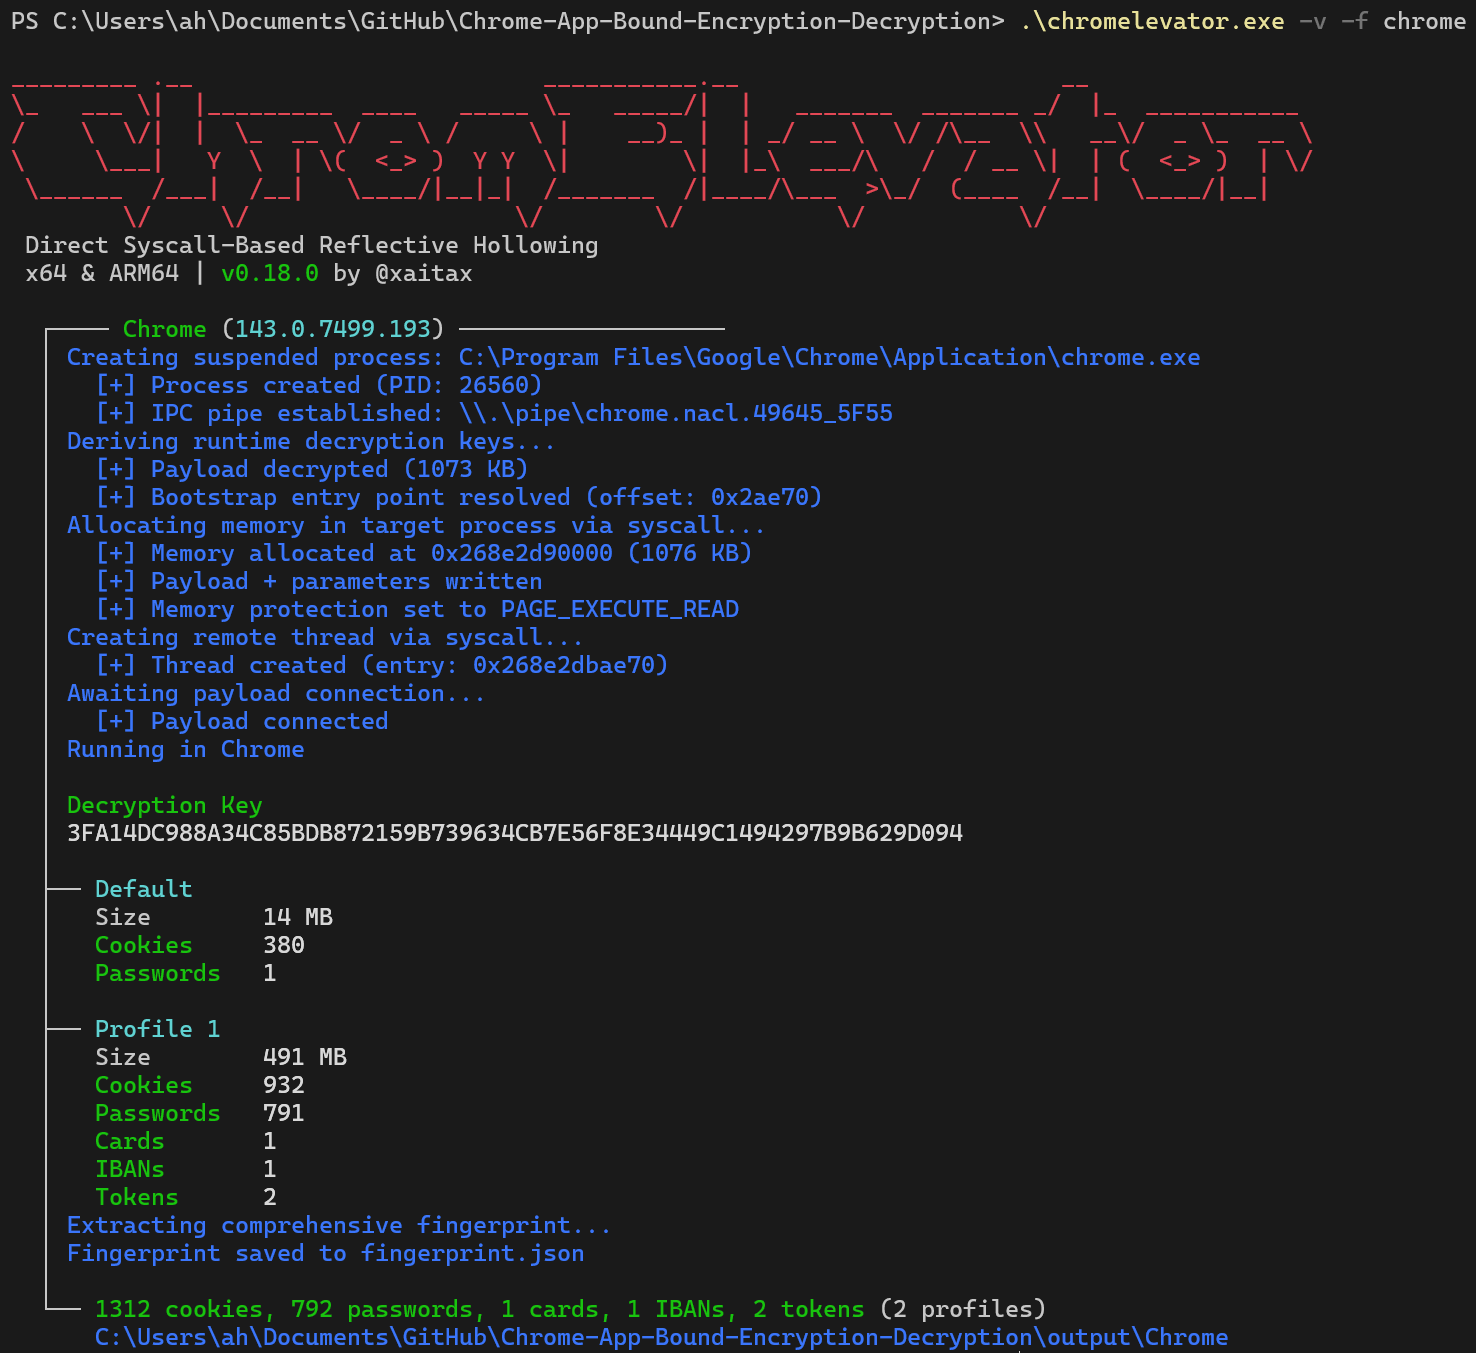
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 jssngc/ontheedge
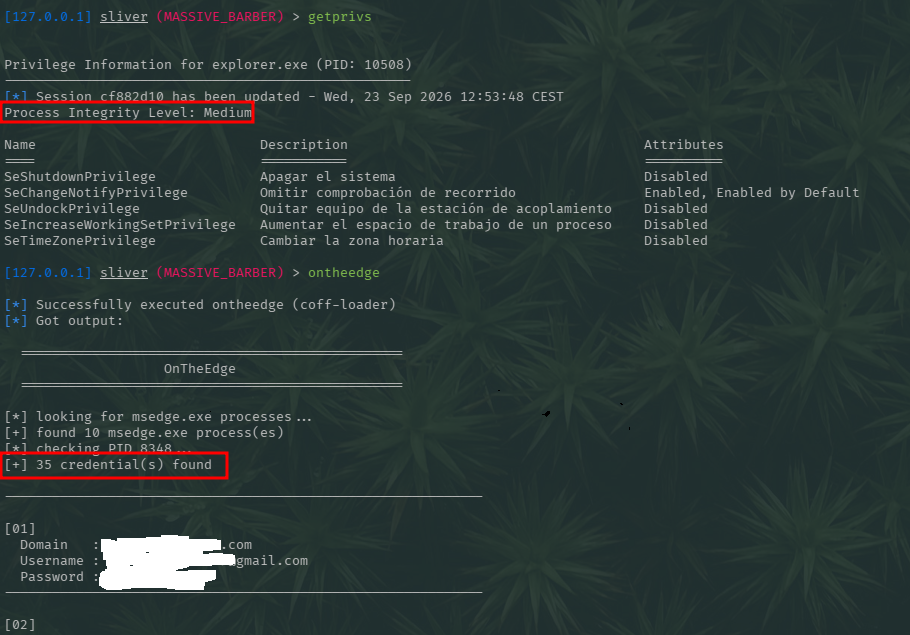
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
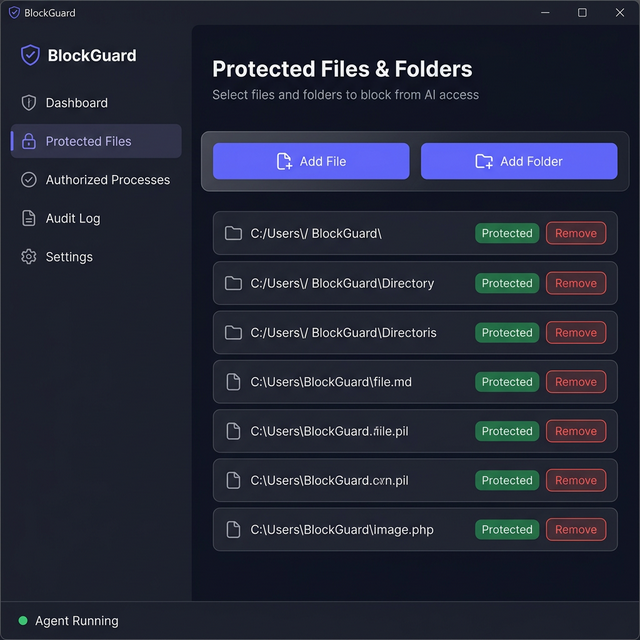 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)