

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
OnTheEdge — Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2 lab environments. | Kitploit
Tools/GitHubGitHub/jssngc/ontheedge
Memory ForensicsData ExfiltrationPost-ExploitationMalware AnalysisPenetration TestingCommand and ControlRed Teaming
GitHubjssngc/ontheedge

OnTheEdge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2 lab environments.

View Repository
1111021 month agoNot yet reviewed
Share

OnTheEdge

OnTheEdge is a small Windows research PoC written in C for studying credential-related data that may be present in the memory of Microsoft Edge processes while the browser is running. The project provides two variants:

  • Standalone executable — intended for local testing and research.
  • BOF — intended for controlled C2 laboratory environments.

Disclaimer: This project is intended for authorized security research, malware analysis, testing environments, and educational use only. Do not use it against systems or accounts without explicit authorization.

Output

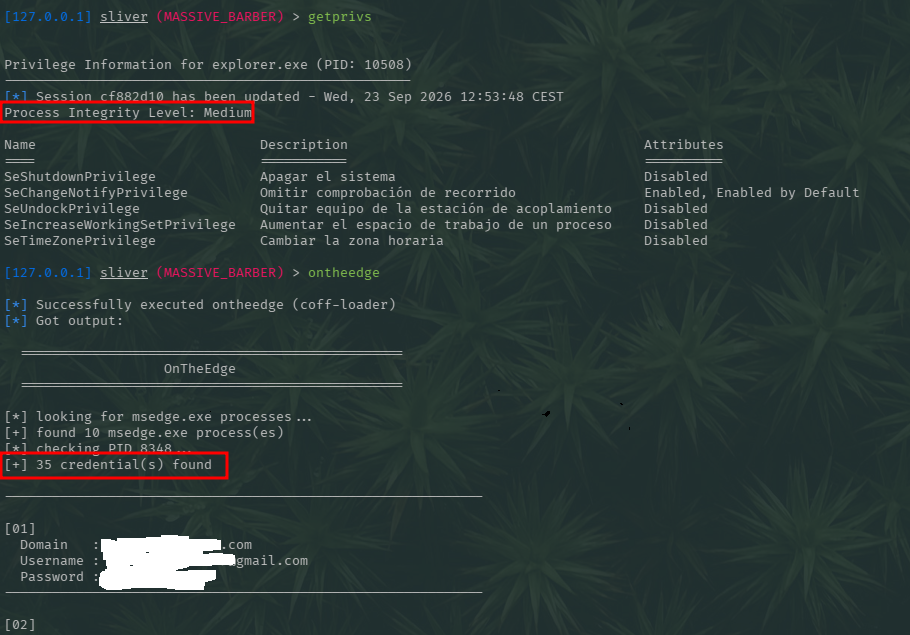
The tool displays information discovered during the memory scan using a simple console format. Example:

================================================
                  OnTheEdge
================================================

[*] looking for msedge.exe processes...
[+] found 9 msedge.exe process(es)
[*] checking PID 9164...
[+] 1 credential(s) found

Results depend on the Edge version, process layout, browser state, and the contents currently present in memory. ![[test.png]] Tested on Windows 11 Pro
Limitations

Memory-based pattern matching is inherently dependent on the runtime representation of data. Results may therefore vary depending on:


  • Microsoft Edge version
  • Browser state
  • Process layout
  • User session
  • Profile configuration
  • Runtime changes to Edge
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →




