
HTB-TwoMillion-machine
 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
api-security-testingctfeducation+4
abedallarawashdeh/htb-twomillion-machineHack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
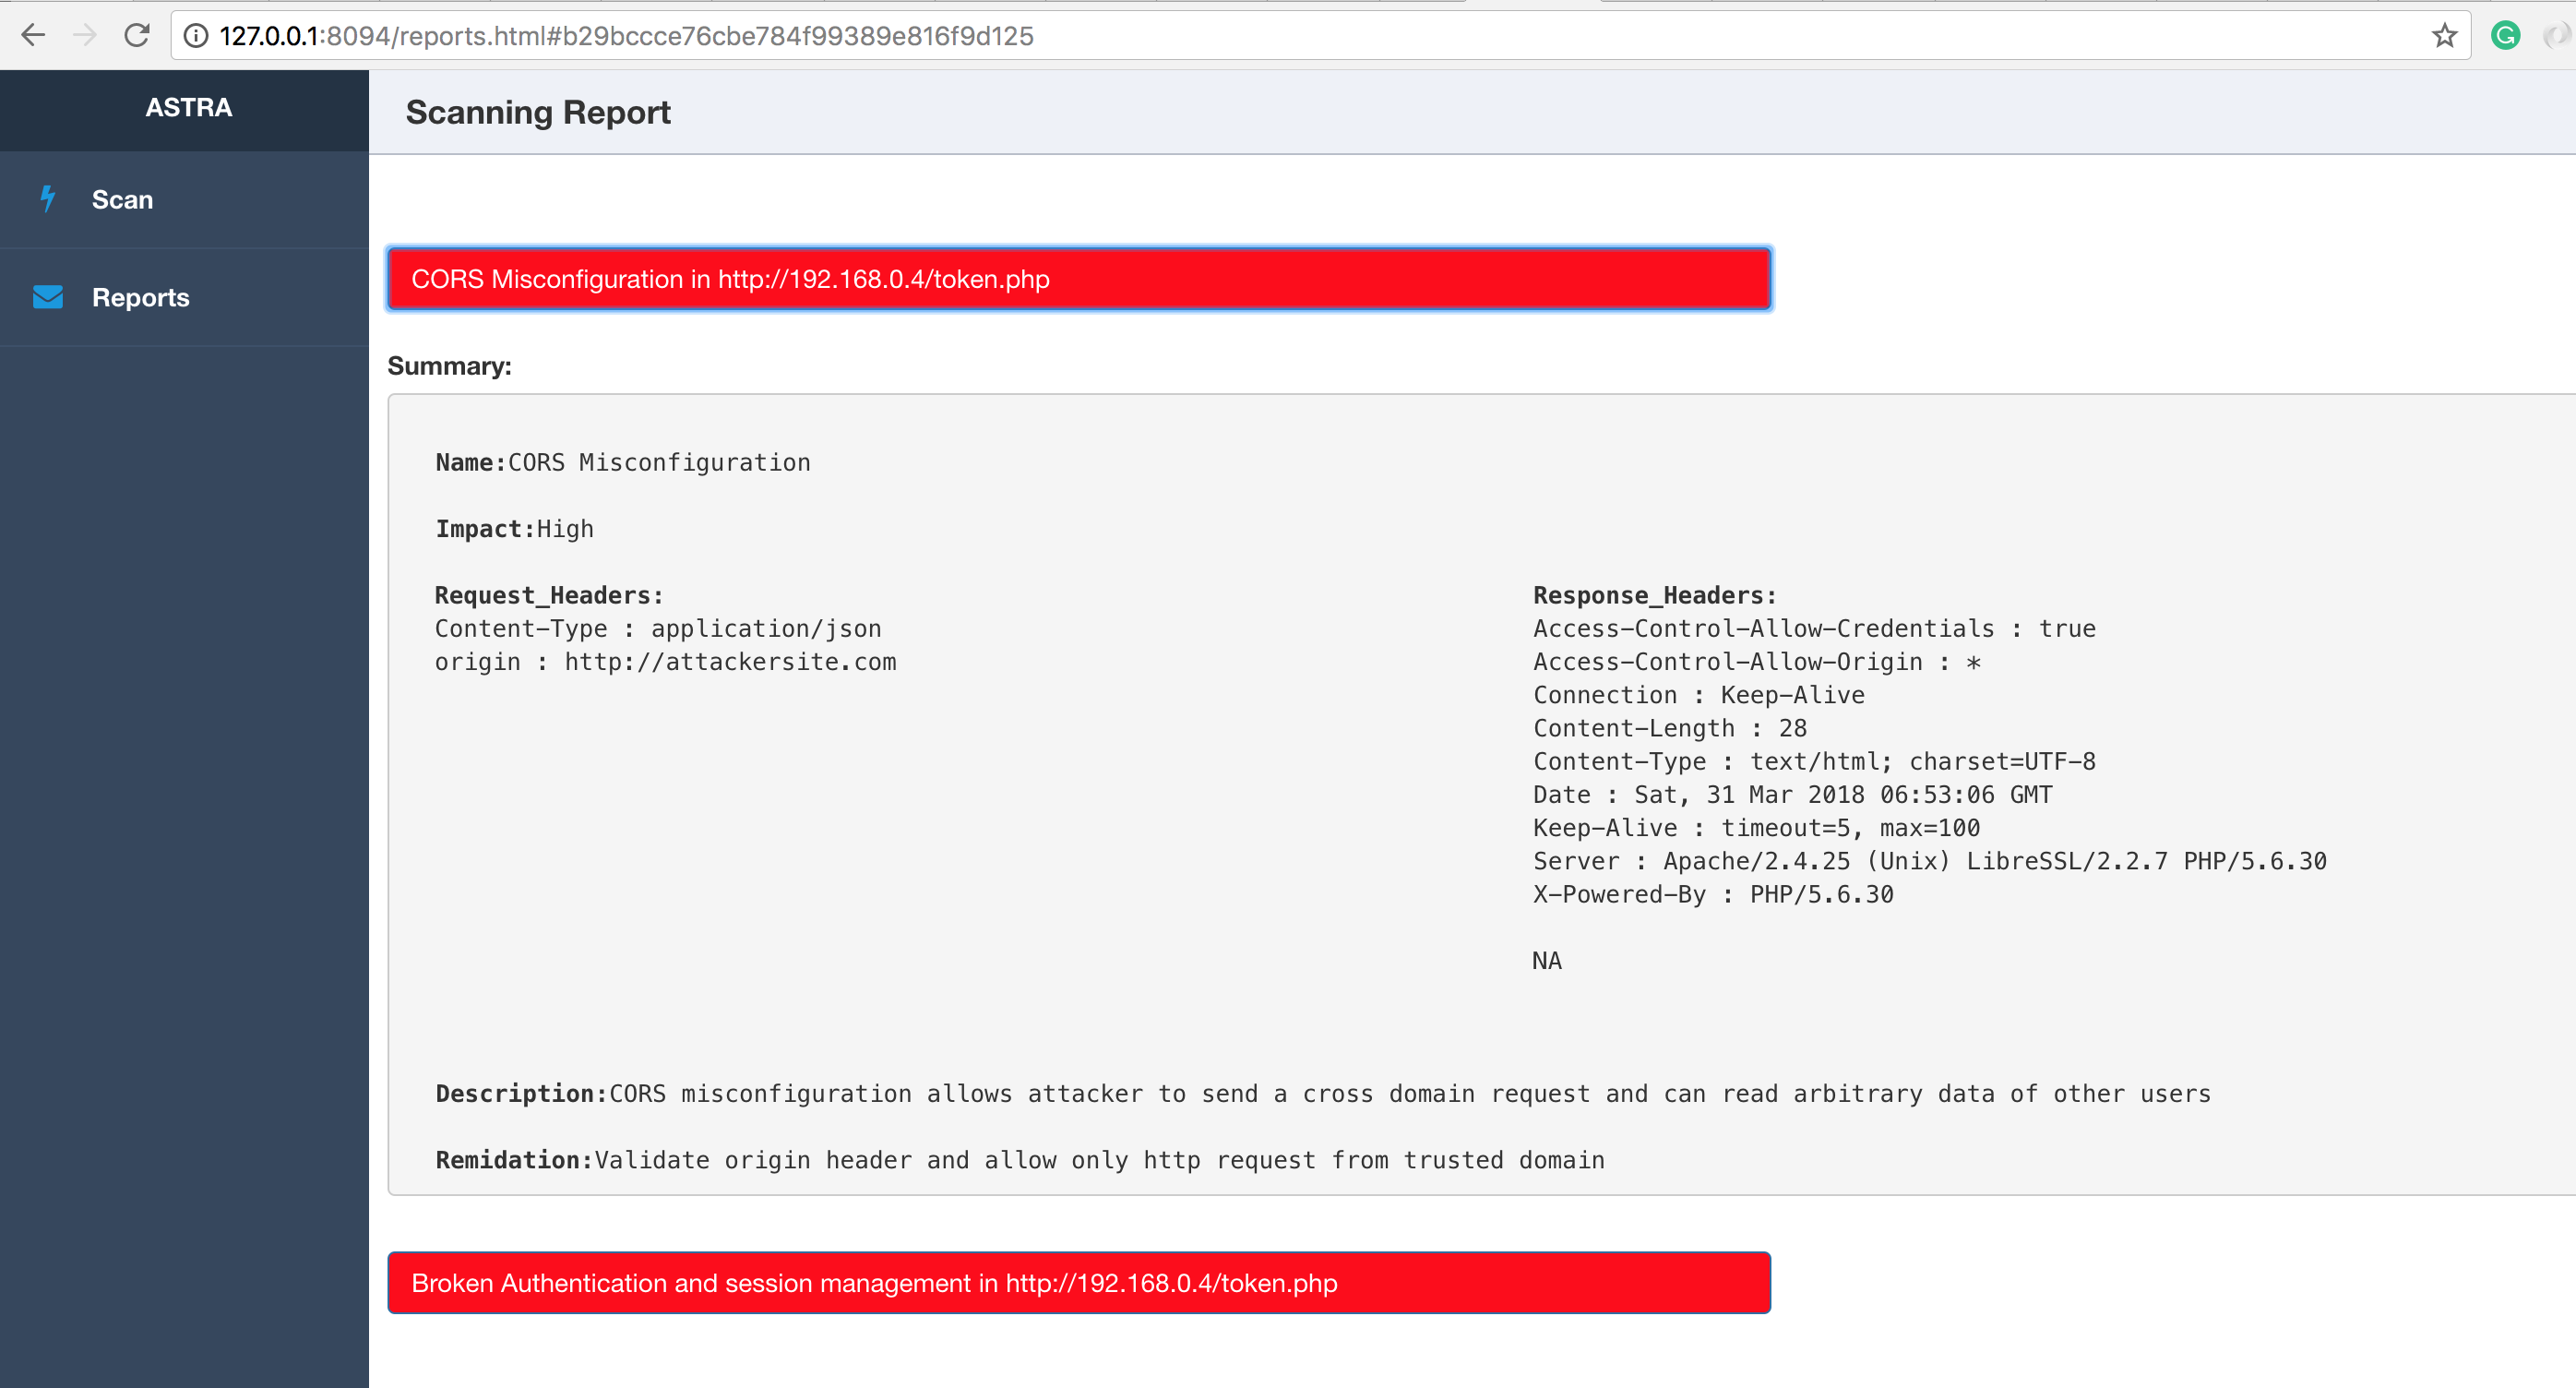 flipkart-incubator/astra
Automated Security Testing For REST API's
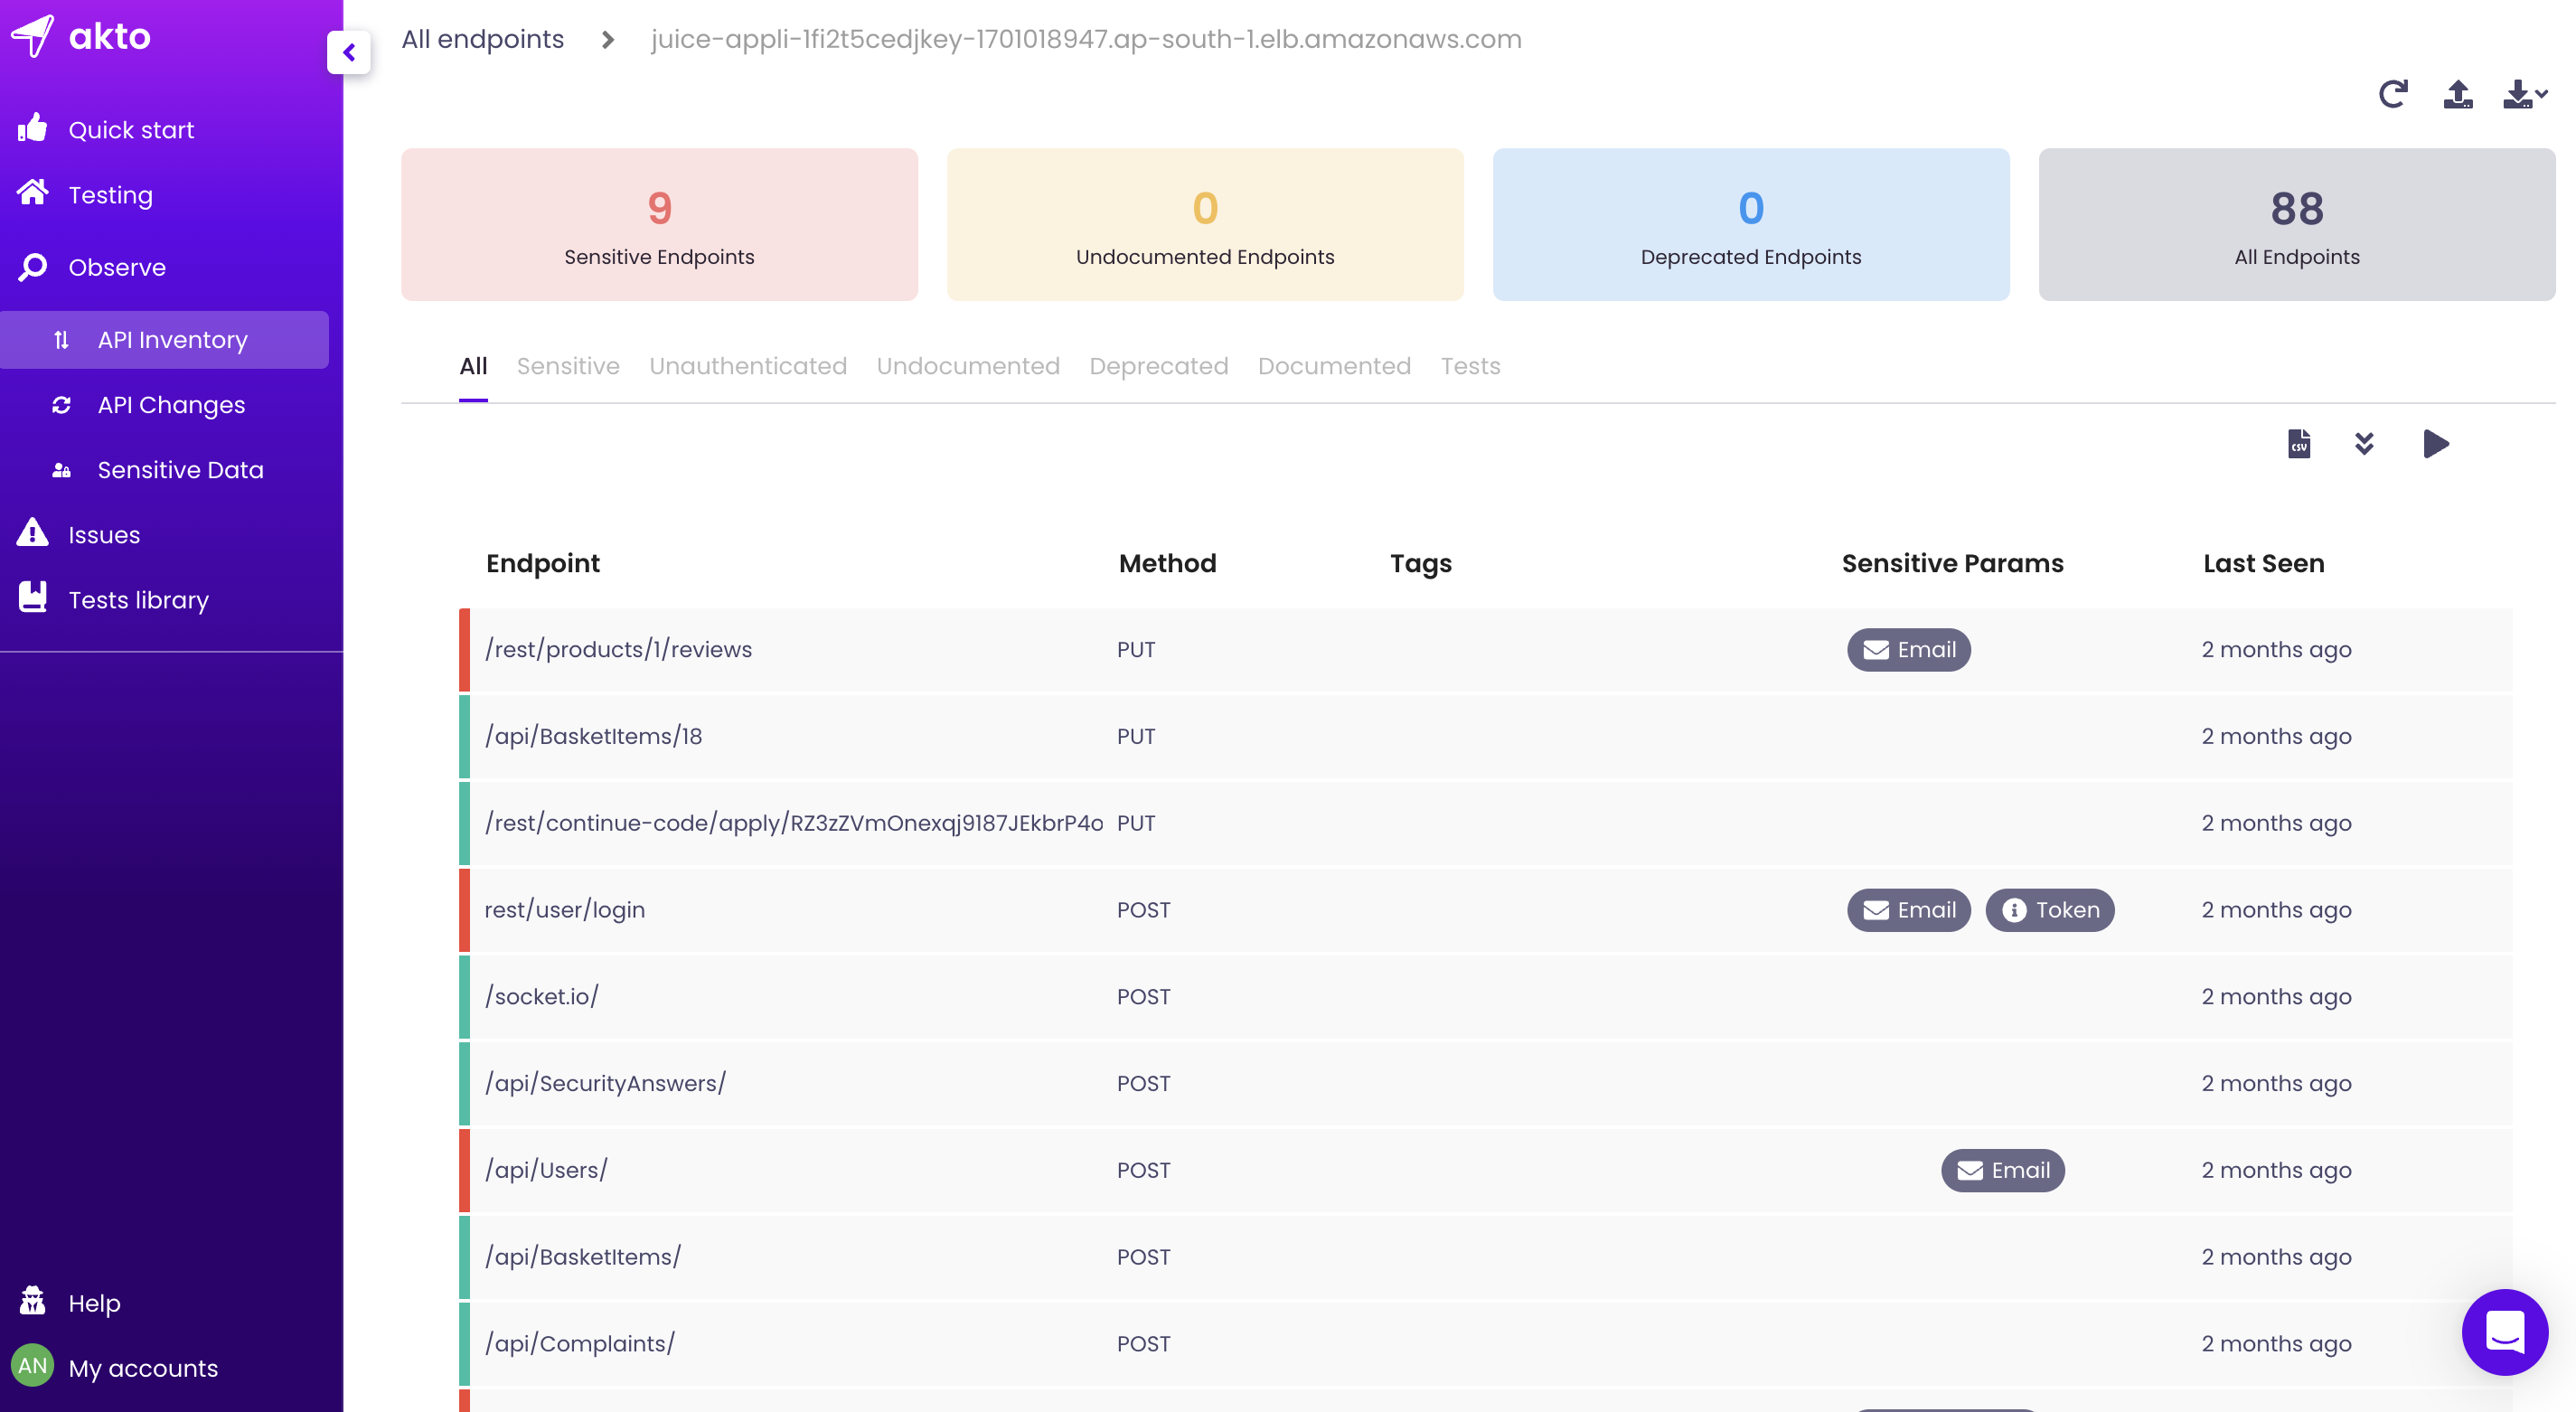 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
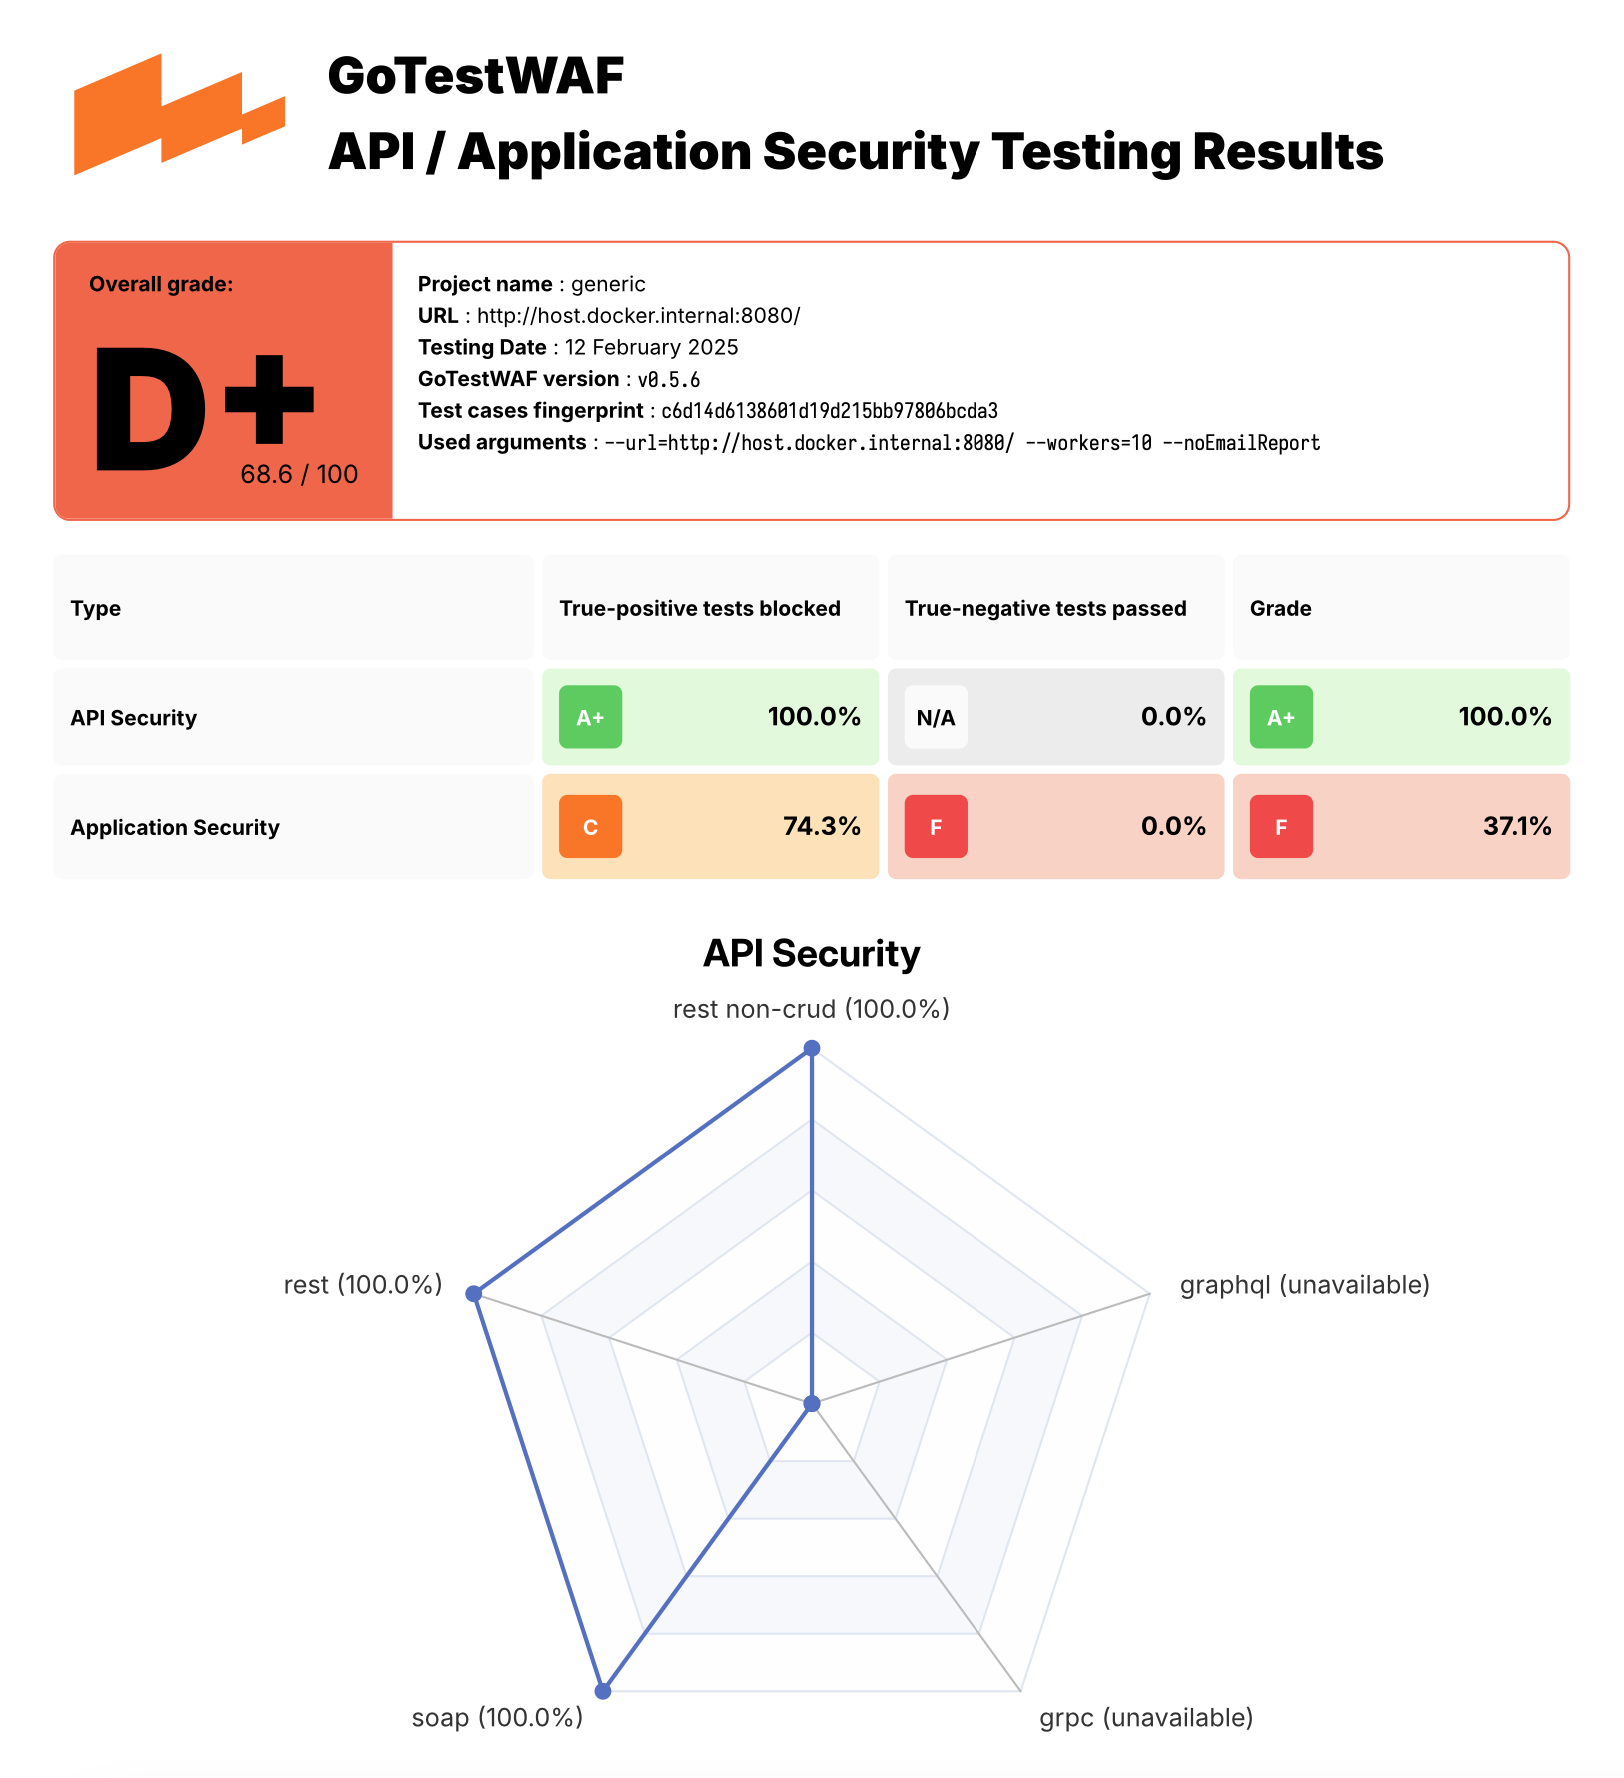 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
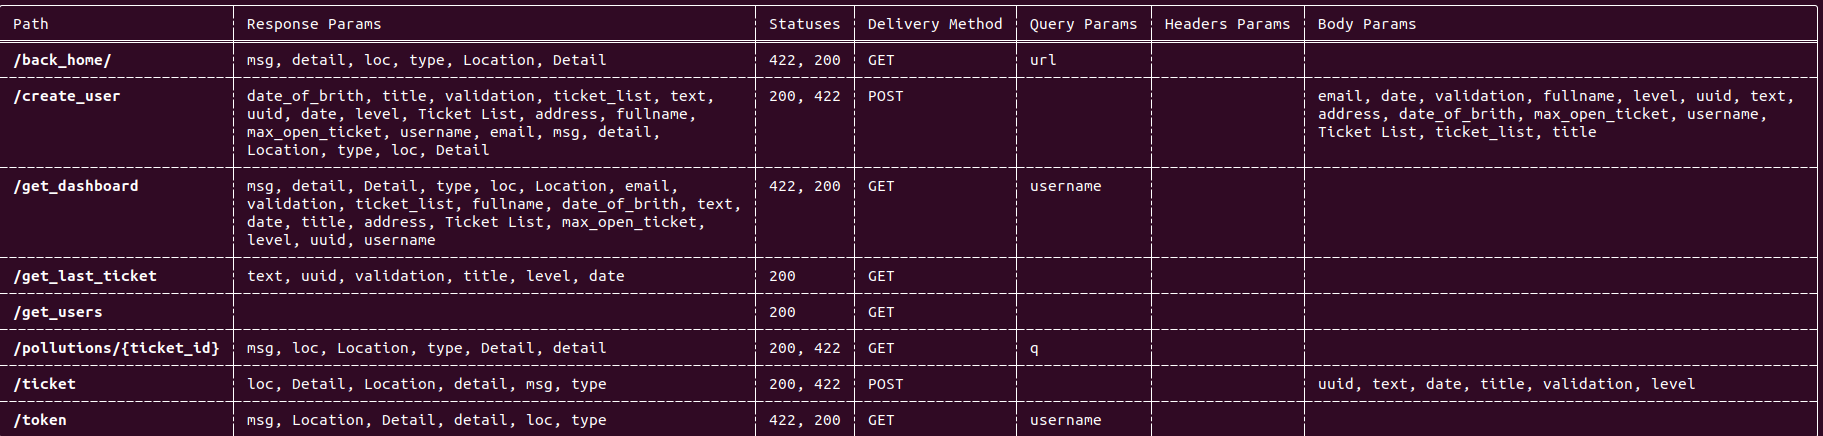 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
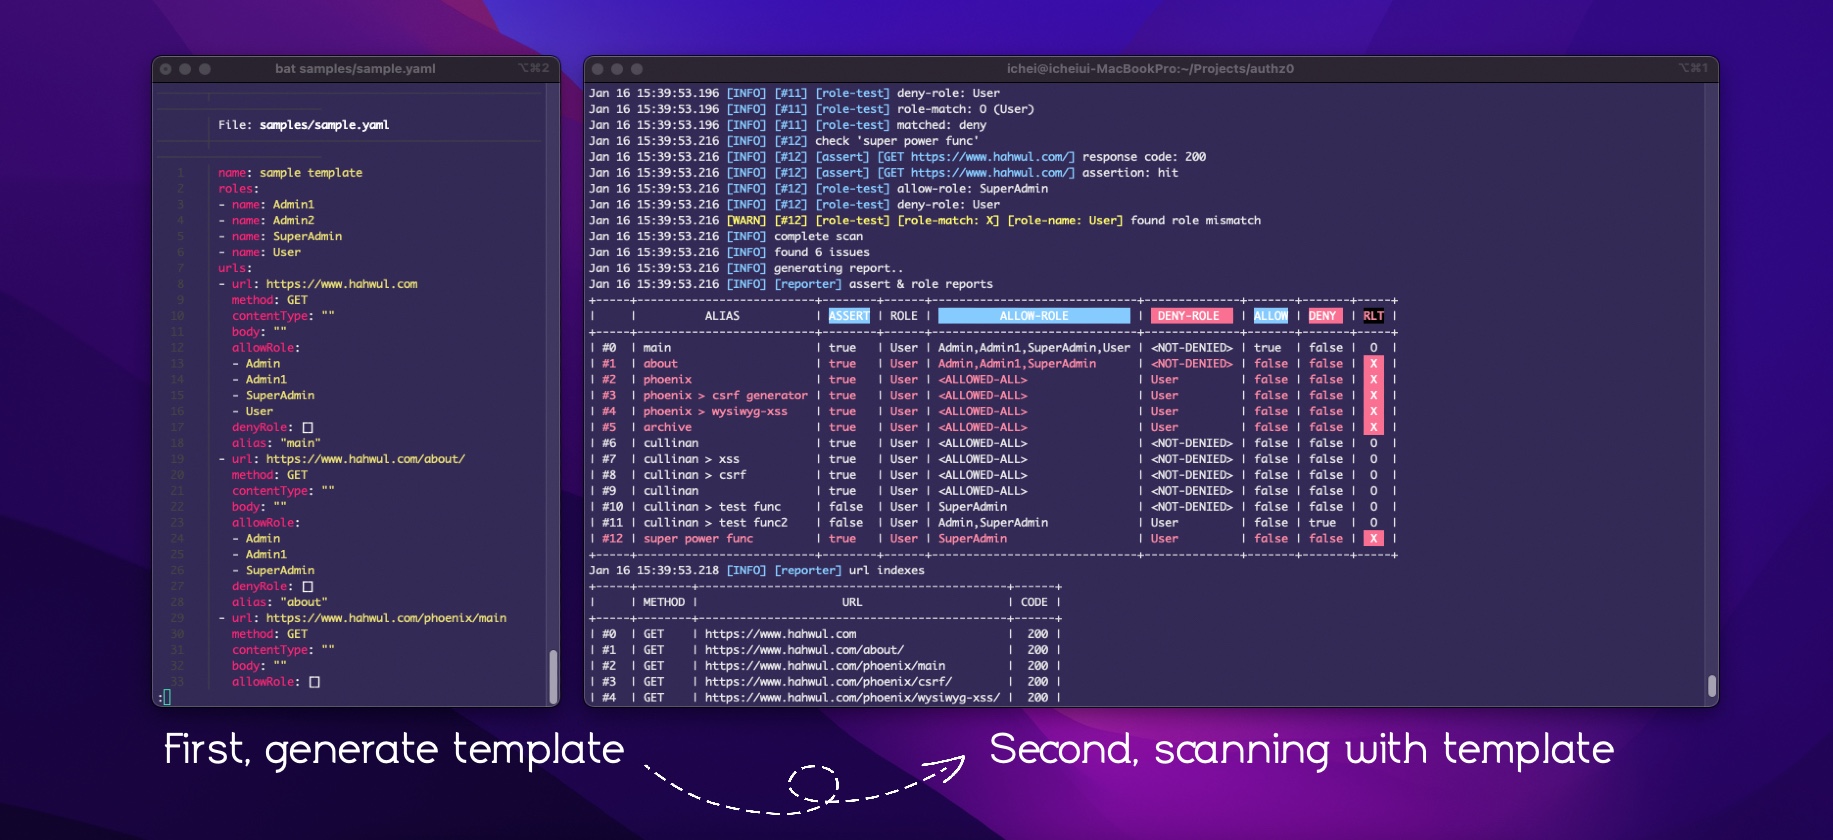 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
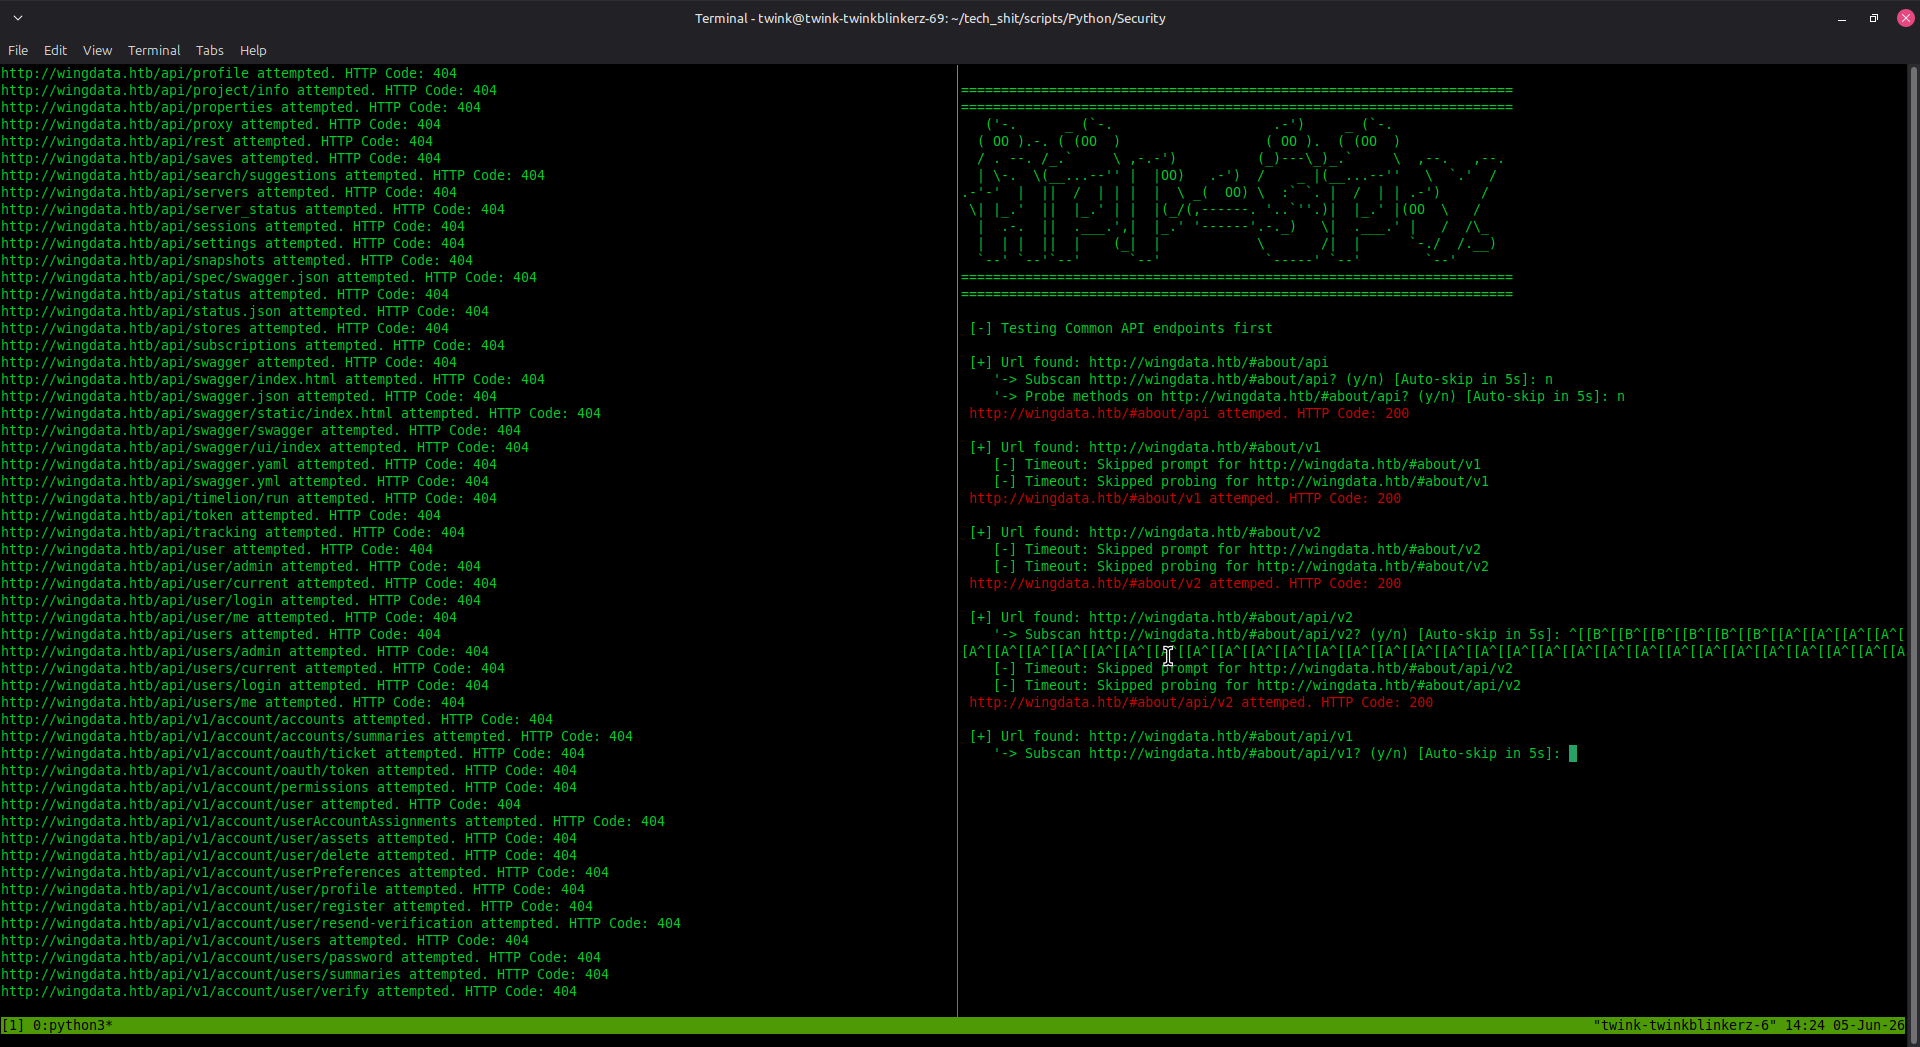 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
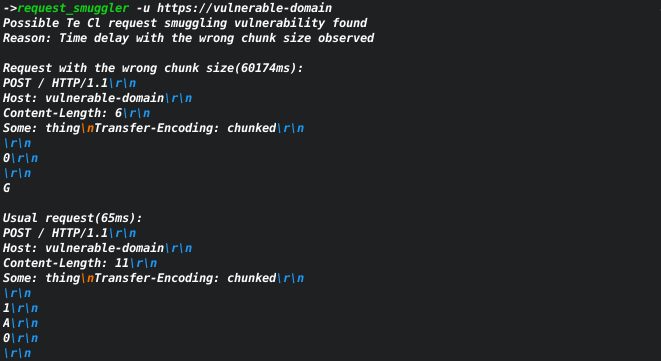 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
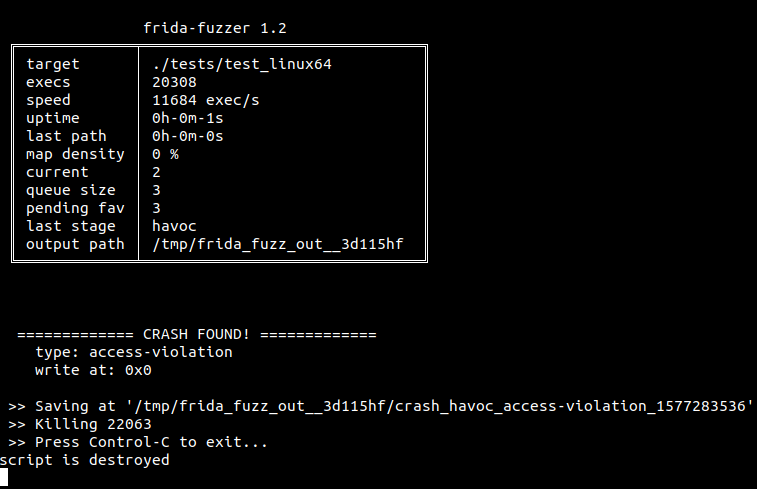 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 google/nogotofail
An on-path blackbox network traffic security testing tool