
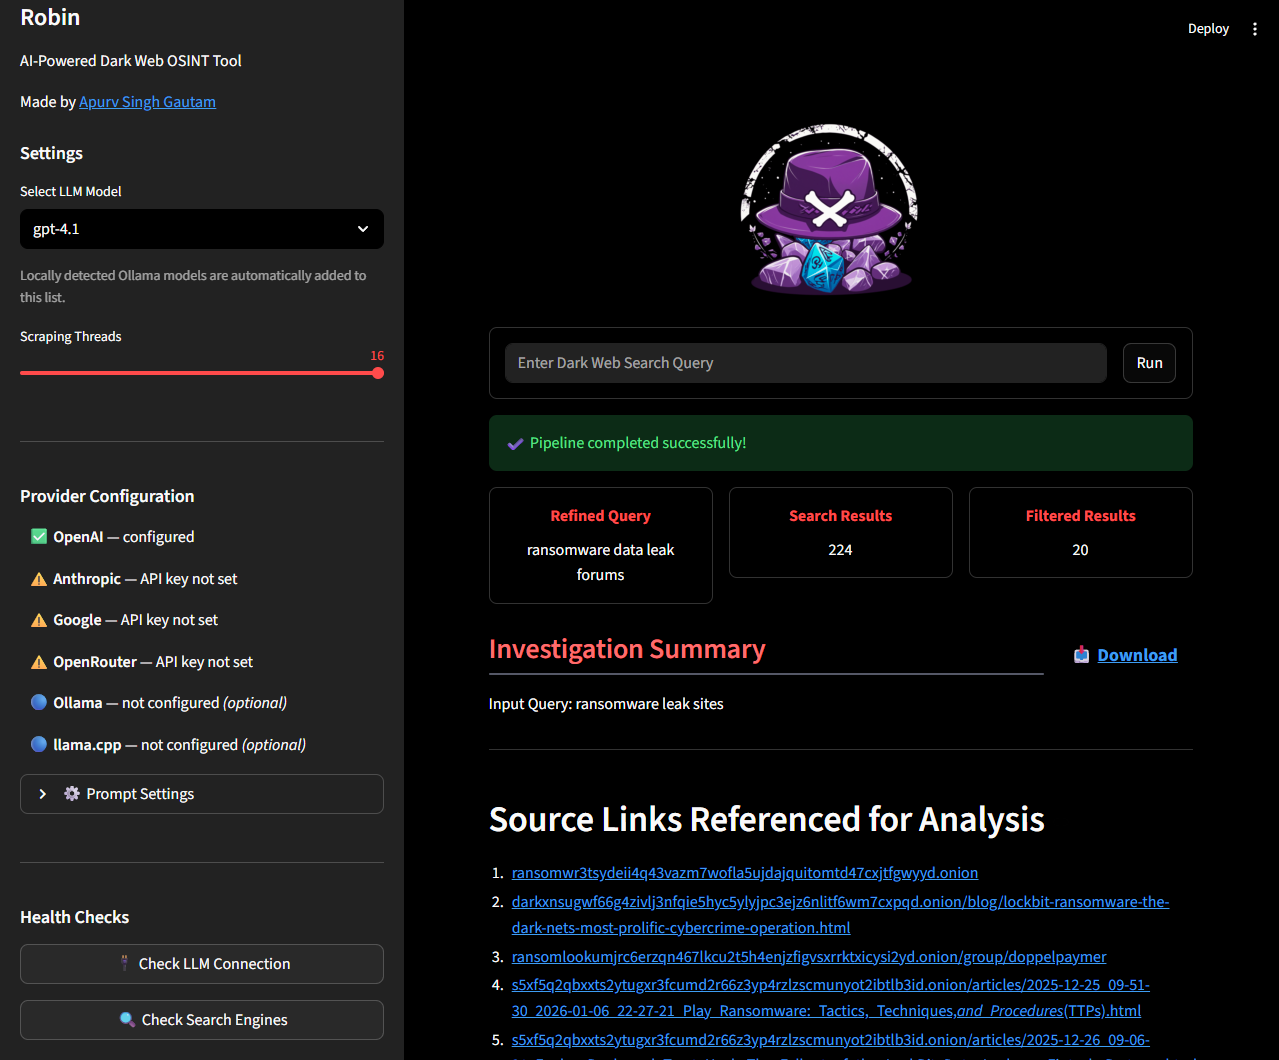
robin
 apurvsinghgautam/robin
AI-powered dark web OSINT tool that uses LLMs to refine queries, filter search results, and generate investigation summaries with a web UI and Docker…
ai-securitycrawlerinformation-gathering+3
7.6k
apurvsinghgautam/robinAI-powered dark web OSINT tool that uses LLMs to refine queries, filter search results, and generate investigation summaries with a web UI and Docker…
 0xblarky/nextpass
A tool which can be used to generate password list or dictionary from the details of the target
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
 panniantong/agent-reach
Give your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
 meta-llama/purplellama
Set of tools to assess and improve LLM security.
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
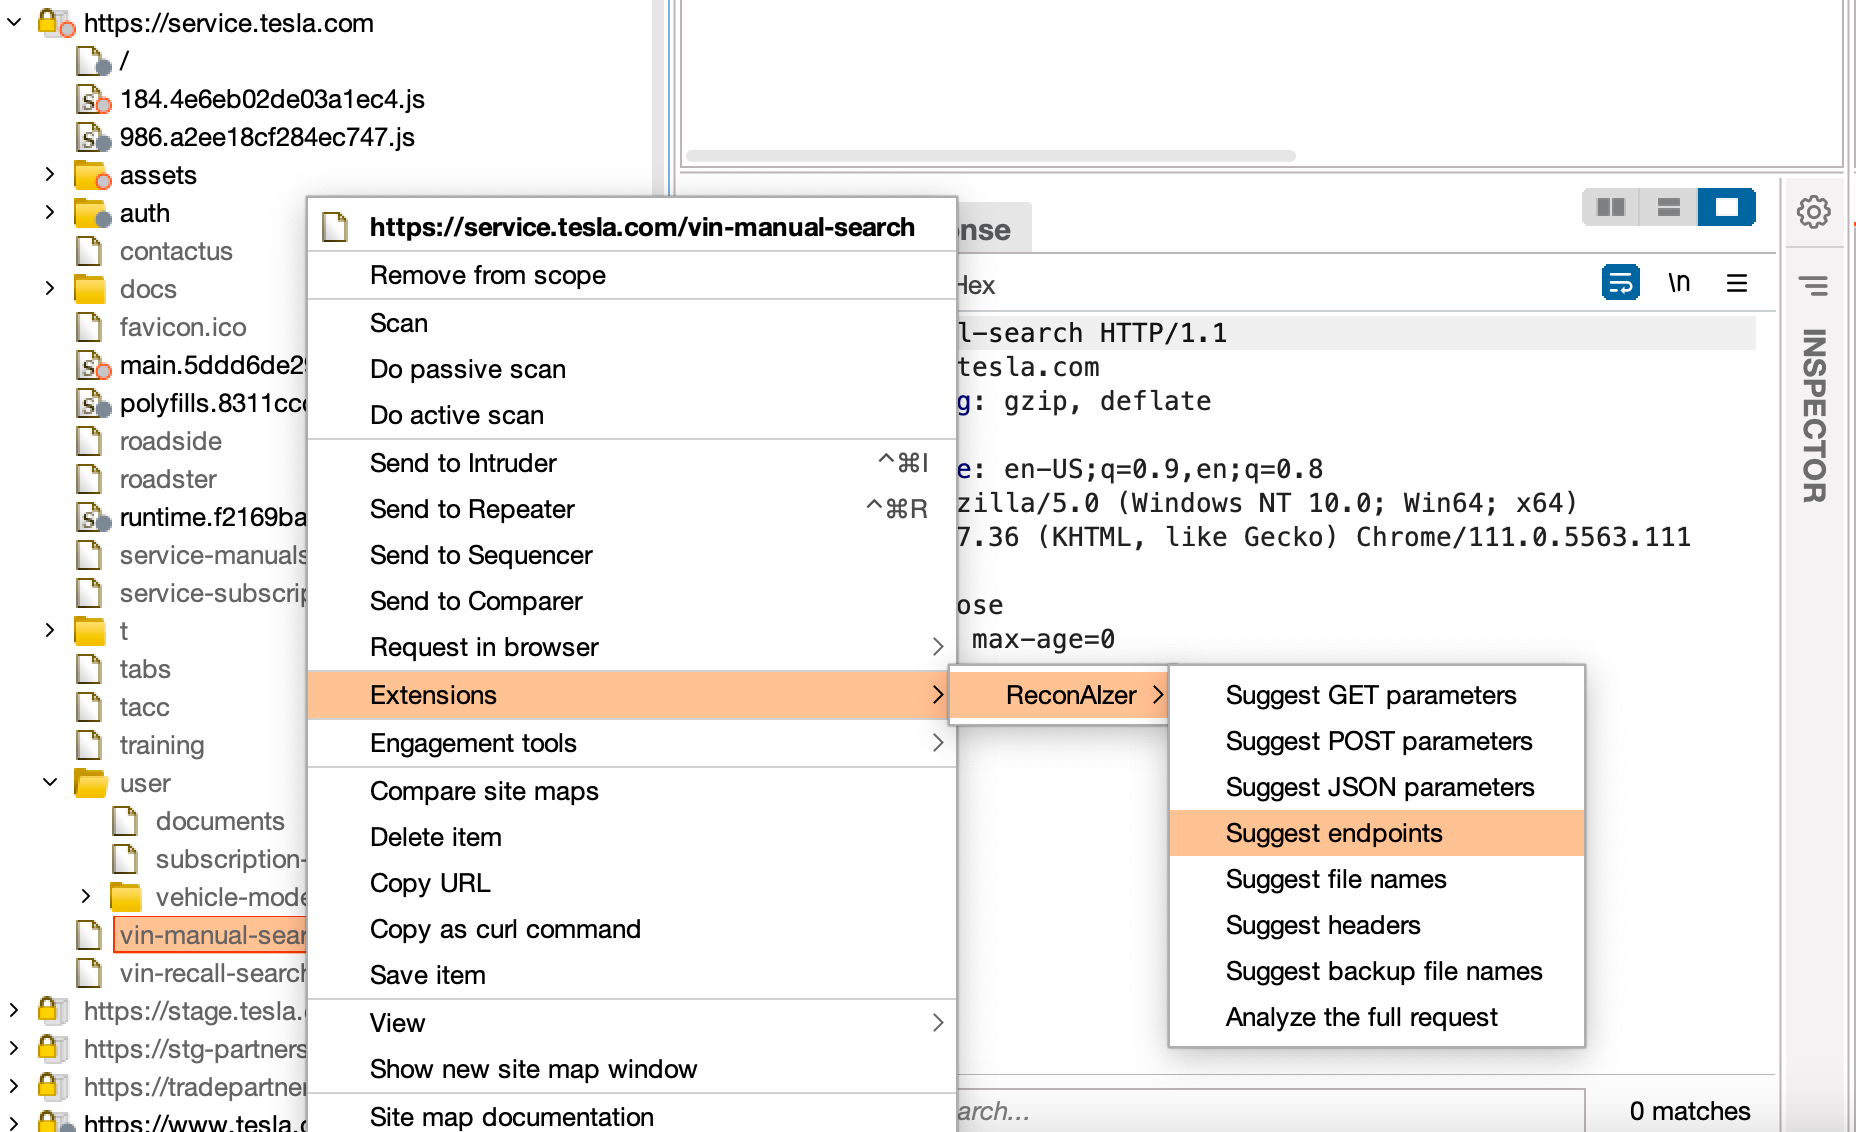 hisxo/reconaizer
A Burp Suite extension to add OpenAI (GPT) on Burp and help you with your Bug Bounty recon to discover endpoints, params, URLs, subdomains and more!
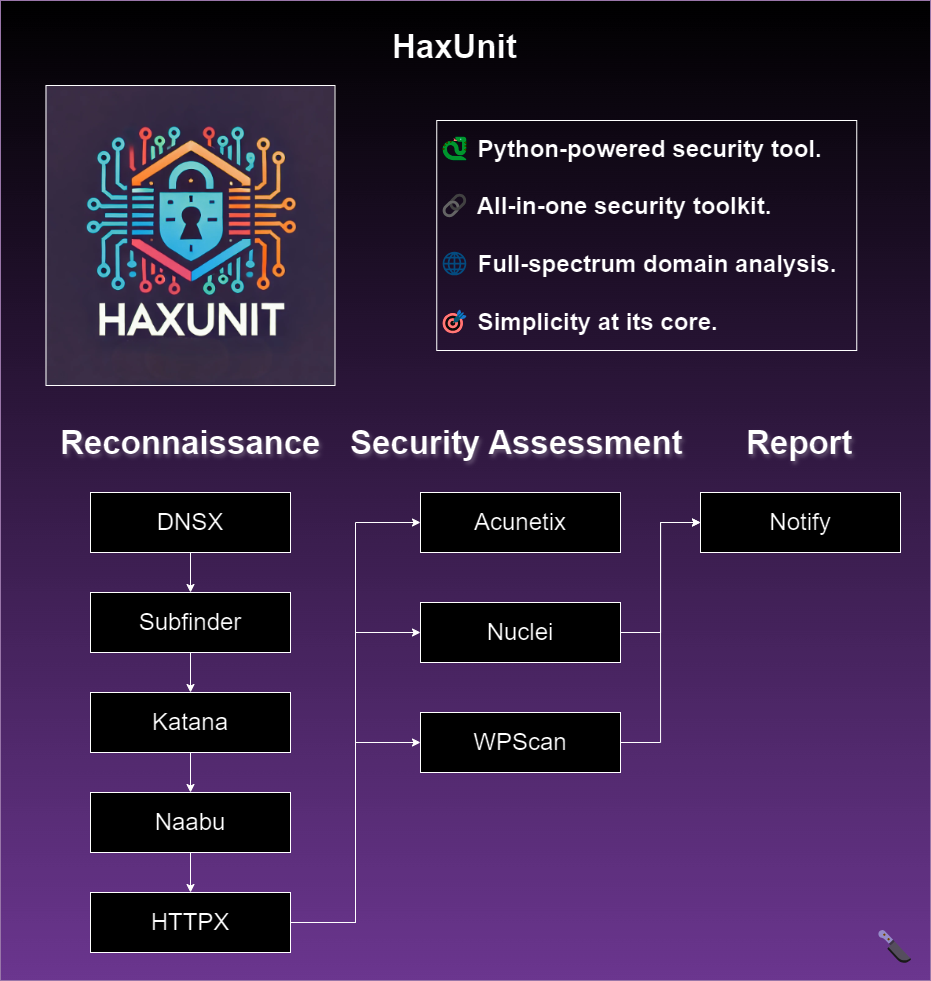 bandit-haxunit/haxunit
Automated web domain reconnaissance and security assessment tool integrating subdomain enumeration, port scanning, vulnerability scanning, and…
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
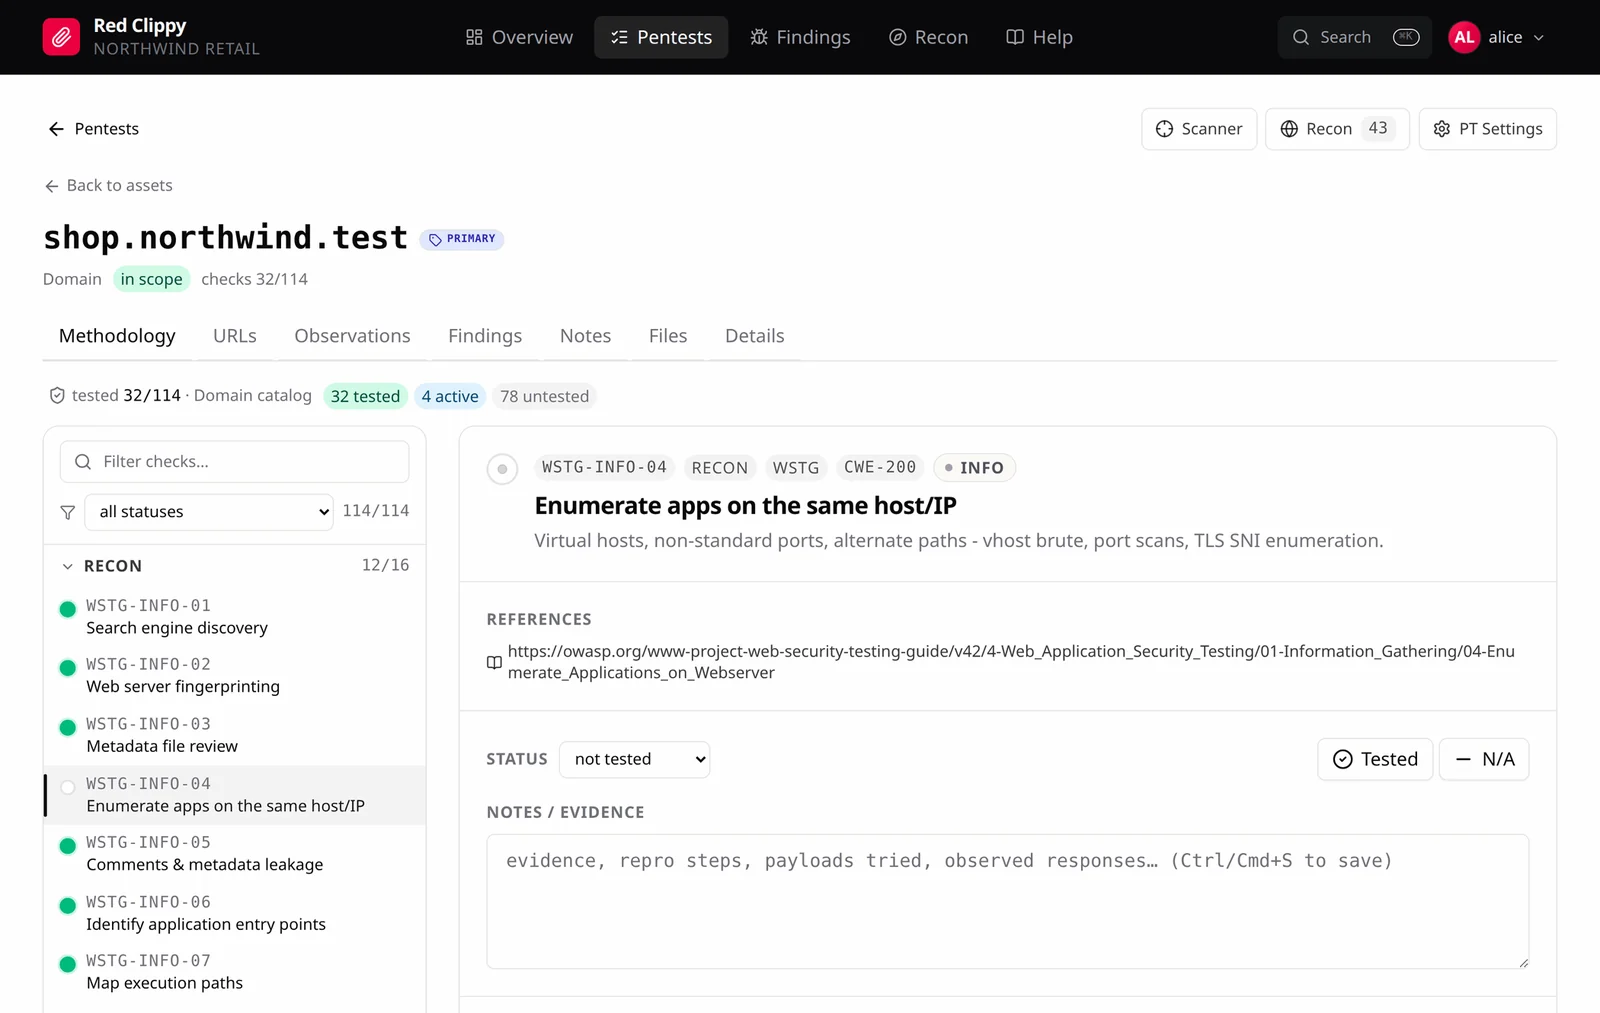 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
 hannahbellesheart/blackbox.ai.security.analysis
Security analysis tool identifying risks in Blackbox.ai extensions, including credential harvesting, unpatched CVEs, and privacy threats from hidden…
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 sydsec/syd
Offline AI Security Assistant for Air-Gapped Pentesting
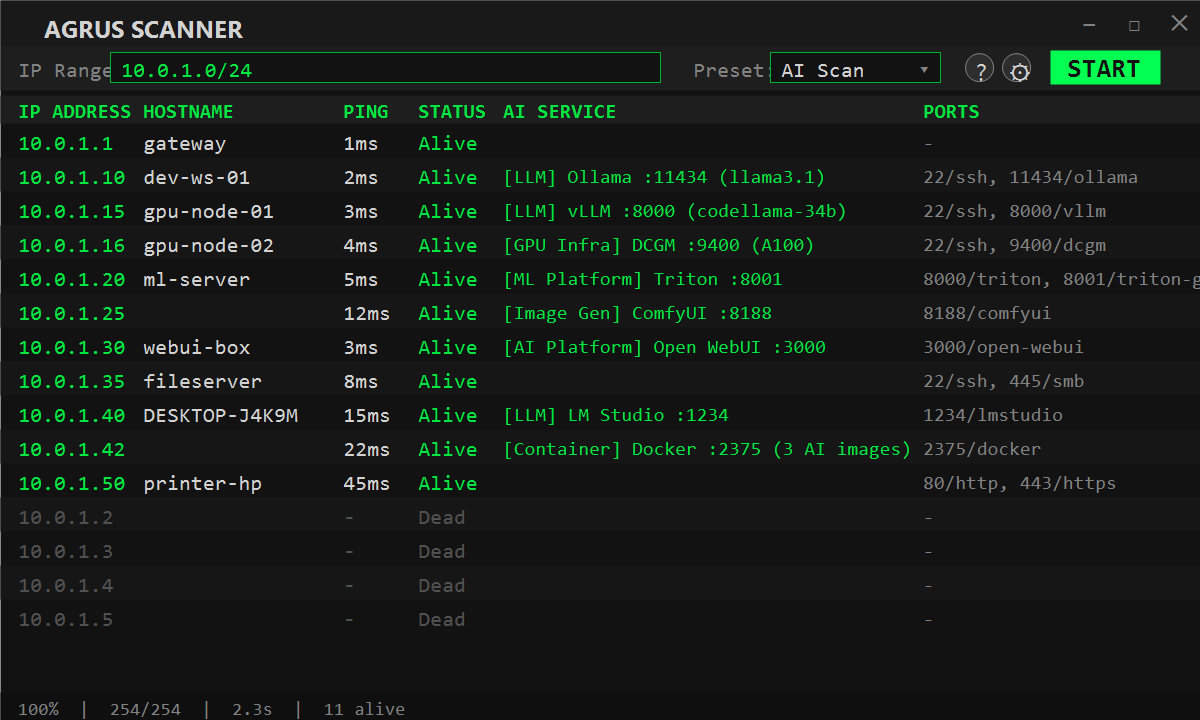 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
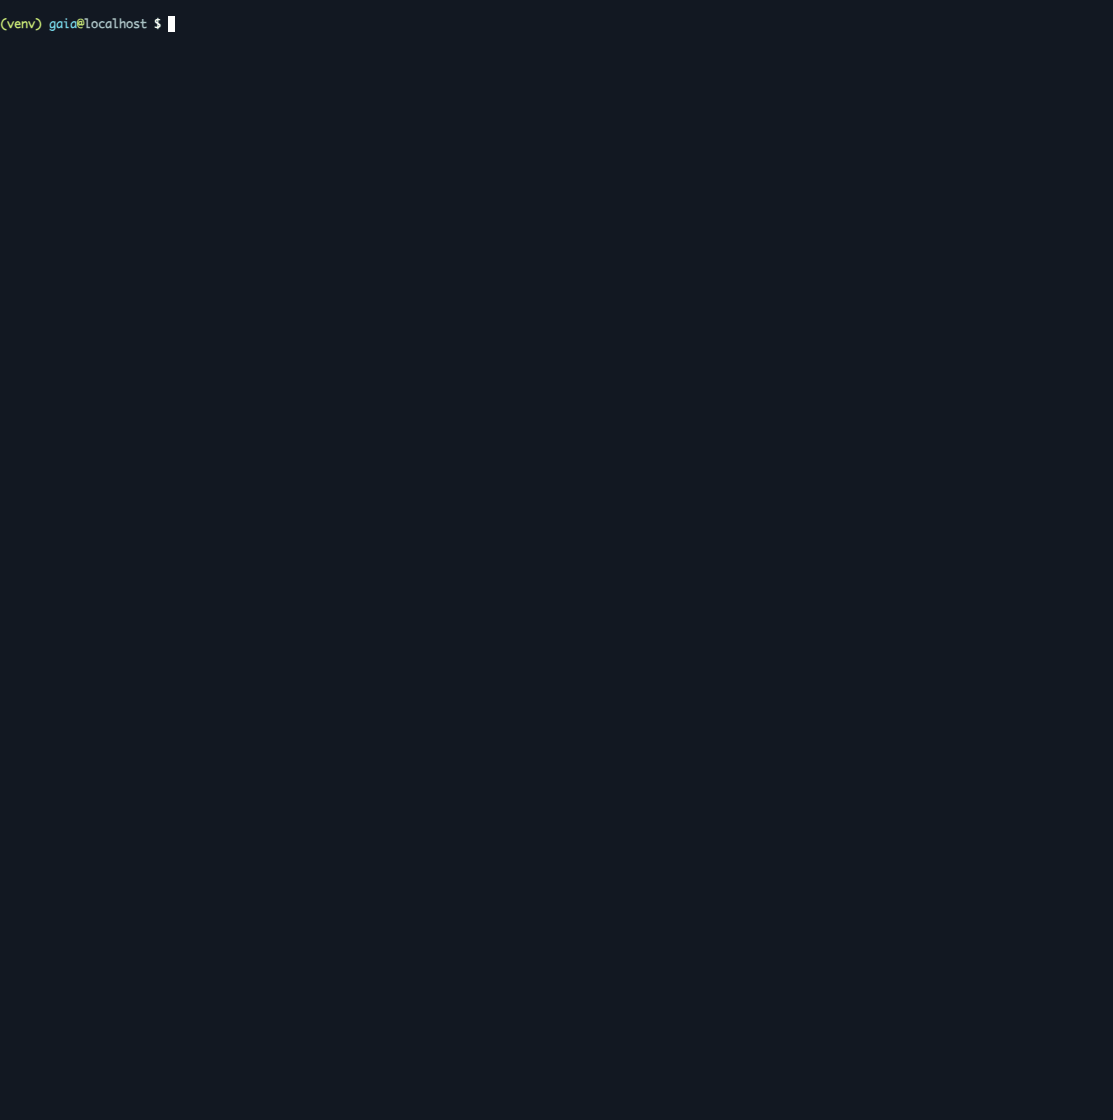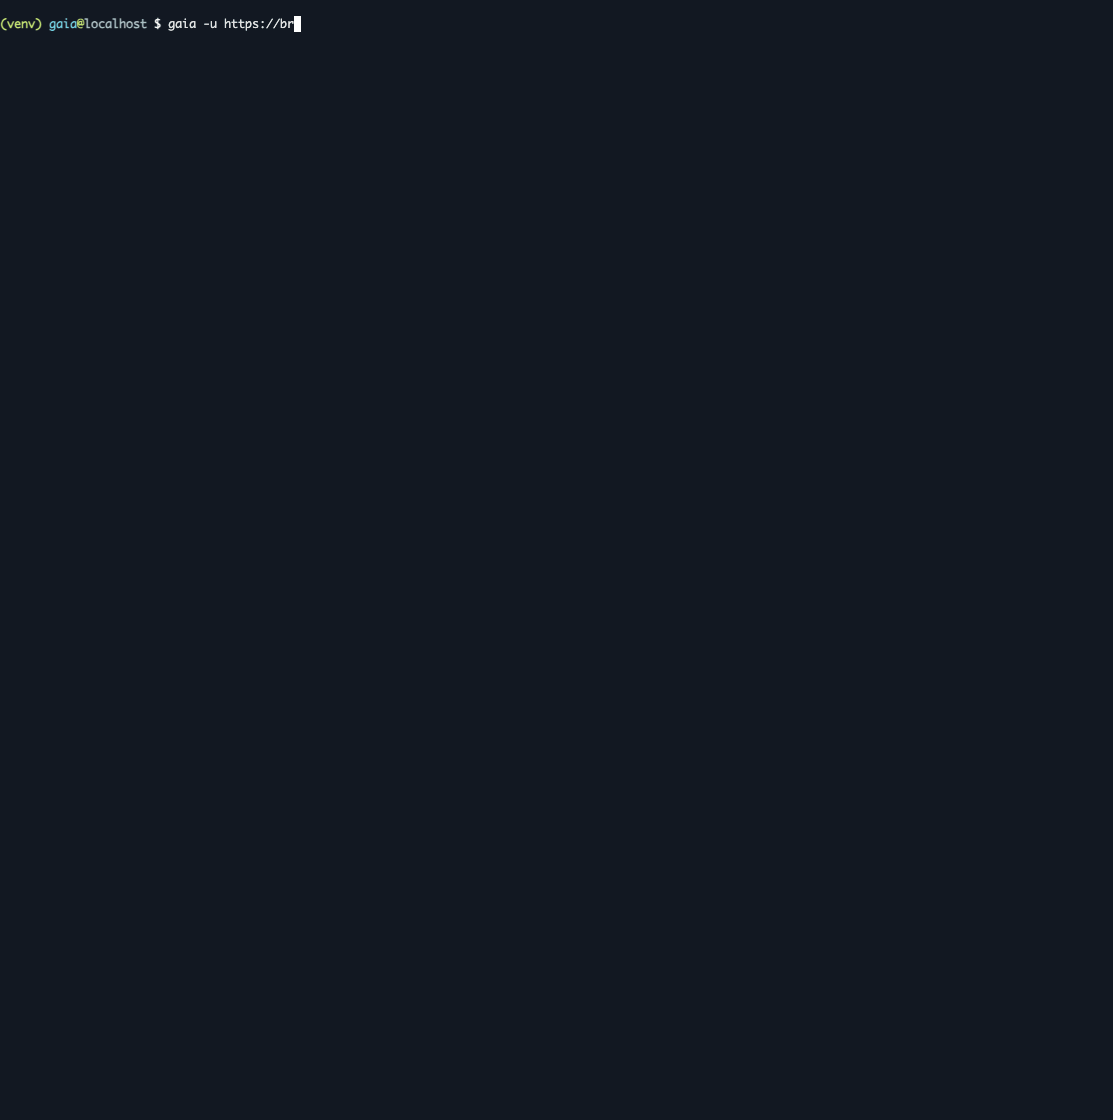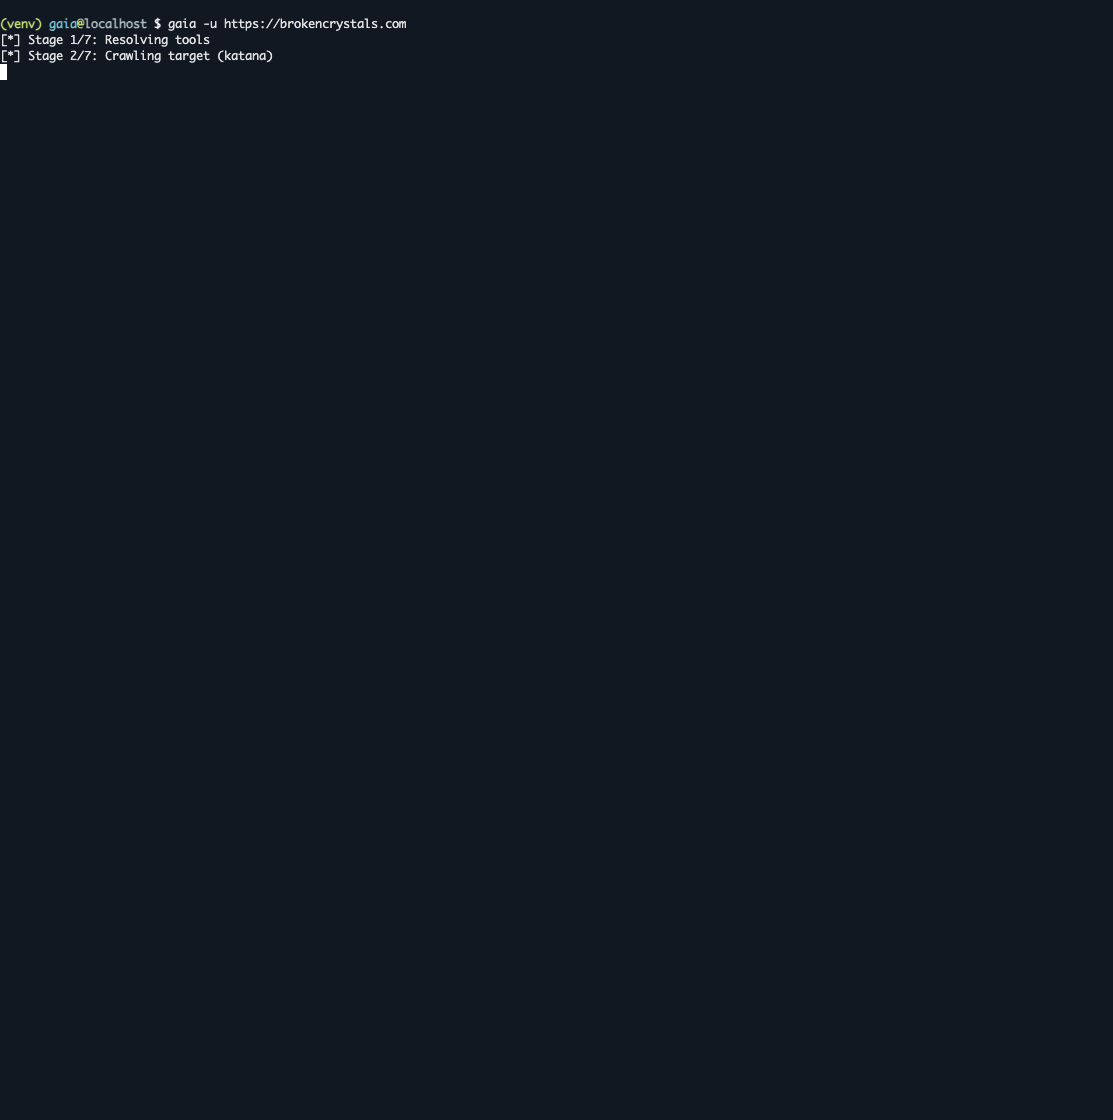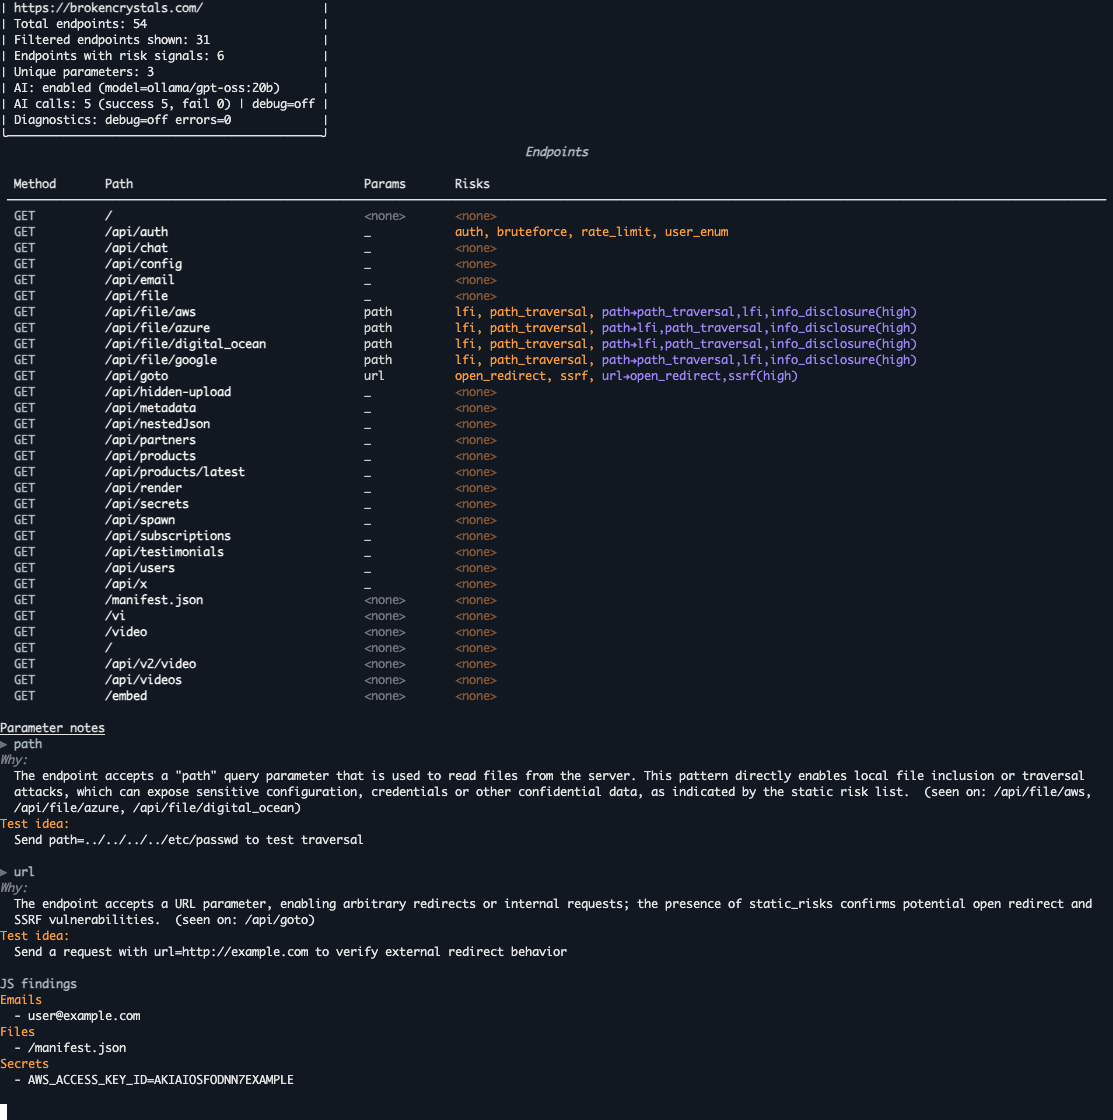 oksuzkayra/gaia
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.