 apurvsinghgautam/robin
AI-powered dark web OSINT tool that uses LLMs to refine queries, filter search results, and generate investigation summaries with a web UI and Docker support.



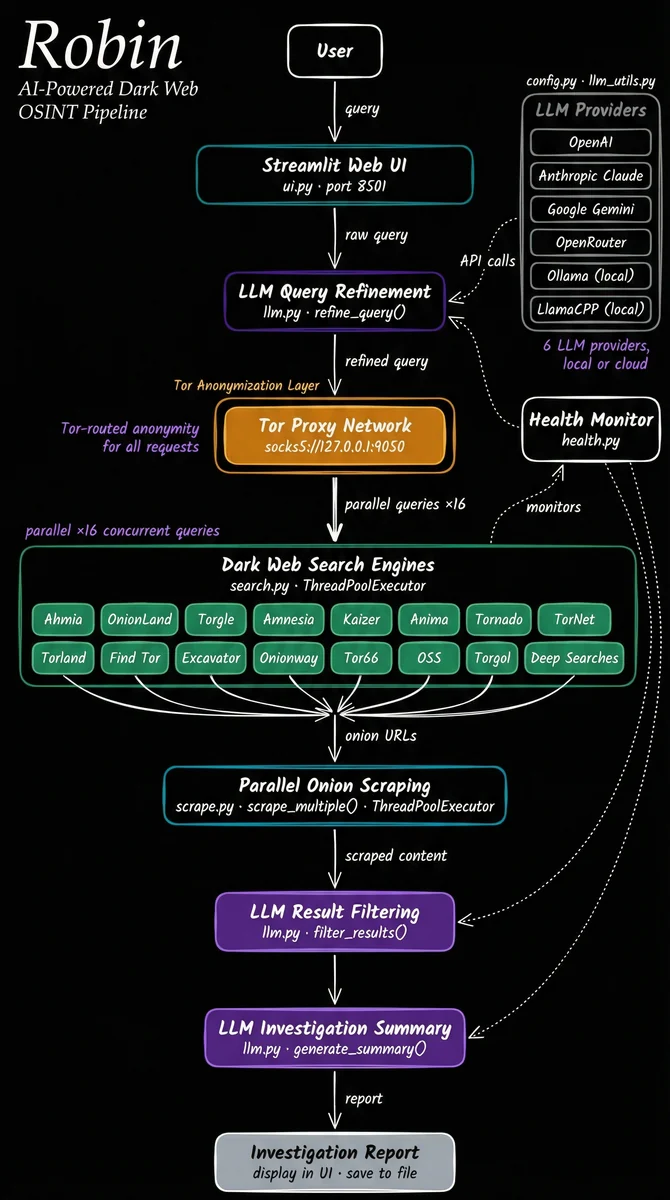
Robin is an AI-powered tool for conducting dark web OSINT investigations. It leverages LLMs to refine queries, filter search results from dark web search engines, and provide an investigation summary.
Installation • Robin as MCP • Troubleshooting • Contributing • Acknowledgements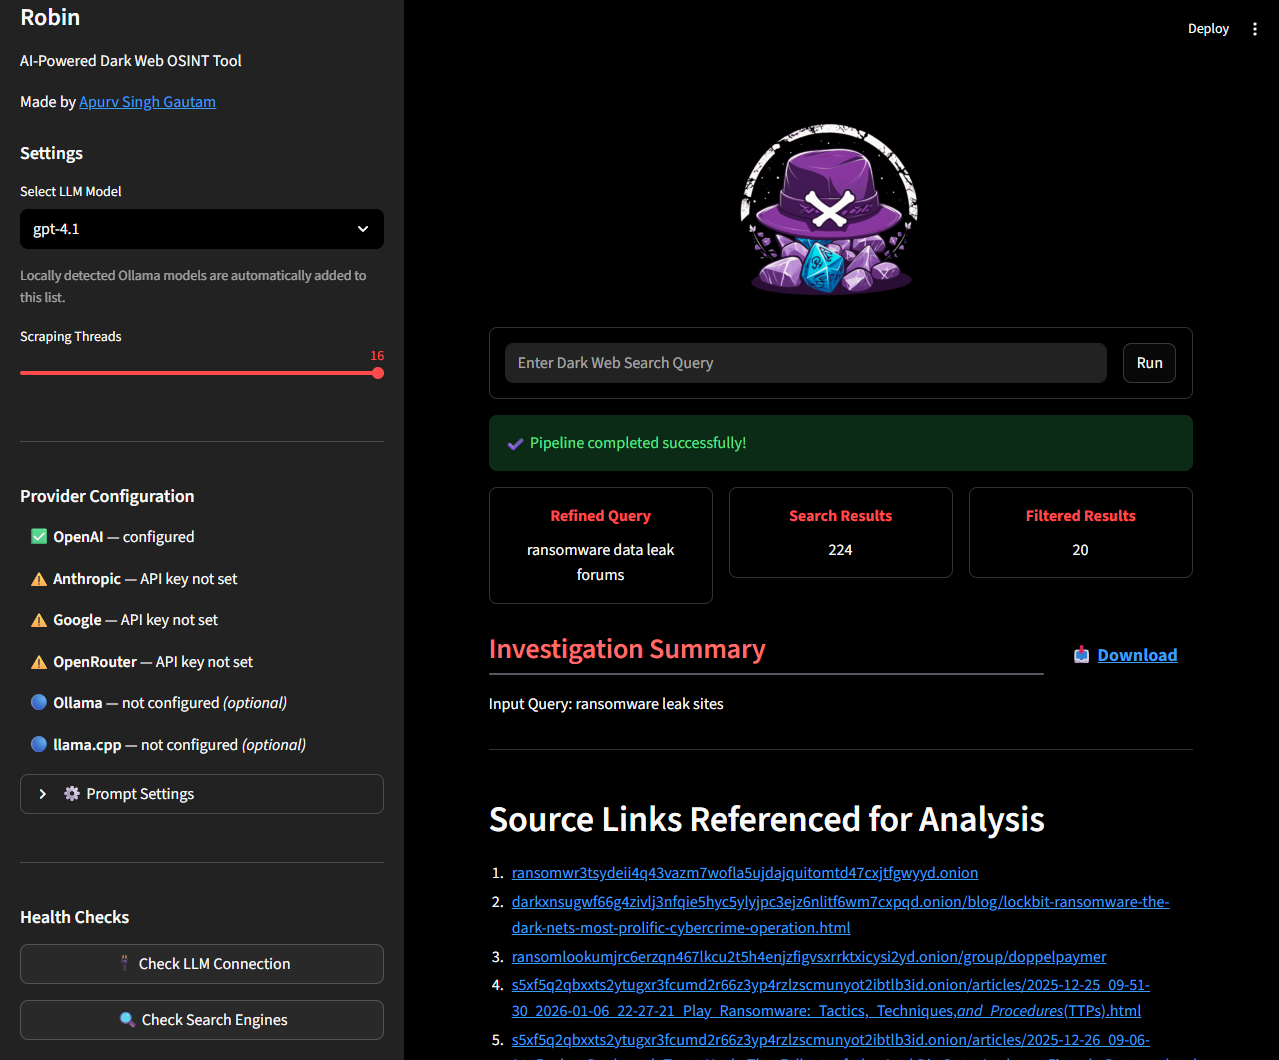
This tool is intended for educational and lawful investigative purposes only. Accessing or interacting with certain dark web content may be illegal depending on your jurisdiction. The author is not responsible for any misuse of this tool or the data gathered using it.
Use responsibly and at your own risk. Ensure you comply with all relevant laws and institutional policies before conducting OSINT investigations.
Additionally, Robin leverages third-party APIs (including LLMs). Be cautious when sending potentially sensitive queries, and review the terms of service for any API or model provider you use.
[!NOTE] The tool needs Tor to do the searches. You can install Tor using
apt install toron Linux/Windows(WSL) orbrew install toron Mac. Once installed, confirm if Tor is running in the background.
[!TIP] Provide your API key either in a
.envfile (copy.env.example) or as environment variables. One key is enough: Robin lists models for whichever providers it finds. Supported keys areOPENAI_API_KEY,ANTHROPIC_API_KEY,GOOGLE_API_KEY,MISTRAL_API_KEYandOPENROUTER_API_KEY.For Ollama, nothing goes in your
.env. Robin defaults tohttp://host.docker.internal:11434, which is what the recommended Docker install needs. Two things are still on you:
- Run the container with
--add-host=host.docker.internal:host-gateway(the README command already does).- Make Ollama listen on all interfaces, since it binds to
127.0.0.1by default and a container cannot reach that. If you start it yourself,OLLAMA_HOST=0.0.0.0 ollama serve &. If it runs under systemd,sudo systemctl edit ollama.service, add[Service]andEnvironment="OLLAMA_HOST=0.0.0.0", thensudo systemctl daemon-reload && sudo systemctl restart ollama.See TROUBLESHOOTING.md if it still doesn't appear.
For any other OpenAI-compatible provider (LM Studio, llama.cpp, Groq, etc.), use the 🔌 Custom API Provider expander in the sidebar — no
.envchanges required. Enter the base URL, an optional API key, and optionally a model name if the provider doesn't expose/v1/modelsfor auto-discovery.
docker pull apurvsg/robin:latest
.env file in the folder you run from, with your API key in it (see .env.example). Create it before the first run: if it does not exist, Docker mounts an empty folder in its place and Robin starts with no keys.touch .env # then add your API key to it
docker run --rm \
   -v "$(pwd)/.env:/app/.env" \
   --add-host=host.docker.internal:host-gateway \
   -p 8501:8501 \
   apurvsg/robin:latest
[!TIP] To persist saved investigations across Docker restarts, mount a named volume or a local directory at
/app/investigations.A named volume works the same on every OS and needs no host path. It is also the volume the agent commands in Robin as MCP mount, so the UI shows the same reports your agent saved:
docker run --rm \
   -v "$(pwd)/.env:/app/.env" \
   -v robin-investigations:/app/investigations \
   --add-host=host.docker.internal:host-gateway \
   -p 8501:8501 \
   apurvsg/robin:latest
Or mount a local directory, if you want the JSON files on your own disk:
docker run --rm \
   -v "$(pwd)/.env:/app/.env" \
   -v "$(pwd)/investigations:/app/investigations" \
   --add-host=host.docker.internal:host-gateway \
   -p 8501:8501 \
   apurvsg/robin:latest
Investigations are saved to the
investigations/folder in your working directory and can be loaded from the Past Investigations panel in the sidebar.Create the folder yourself first (
mkdir -p investigations) so Docker does not create it as root. The container runs as UID 1000, and on Linux a folder owned by anyone else is read-only to it — Robin prints one warning and the save fails, though the investigation still runs. If you hit that, or your own UID isn't 1000, use the named volume above, or see Saved investigations fail with permission denied on Linux.
http://localhost:8501To run your own build instead of the published image, clone the repository and build it:
docker build -t robin .
Then use the same run commands with robin in place of apurvsg/robin:latest:
docker run --rm \
   -v "$(pwd)/.env:/app/.env" \
   --add-host=host.docker.internal:host-gateway \
   -p 8501:8501 \
   robin
