
Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.
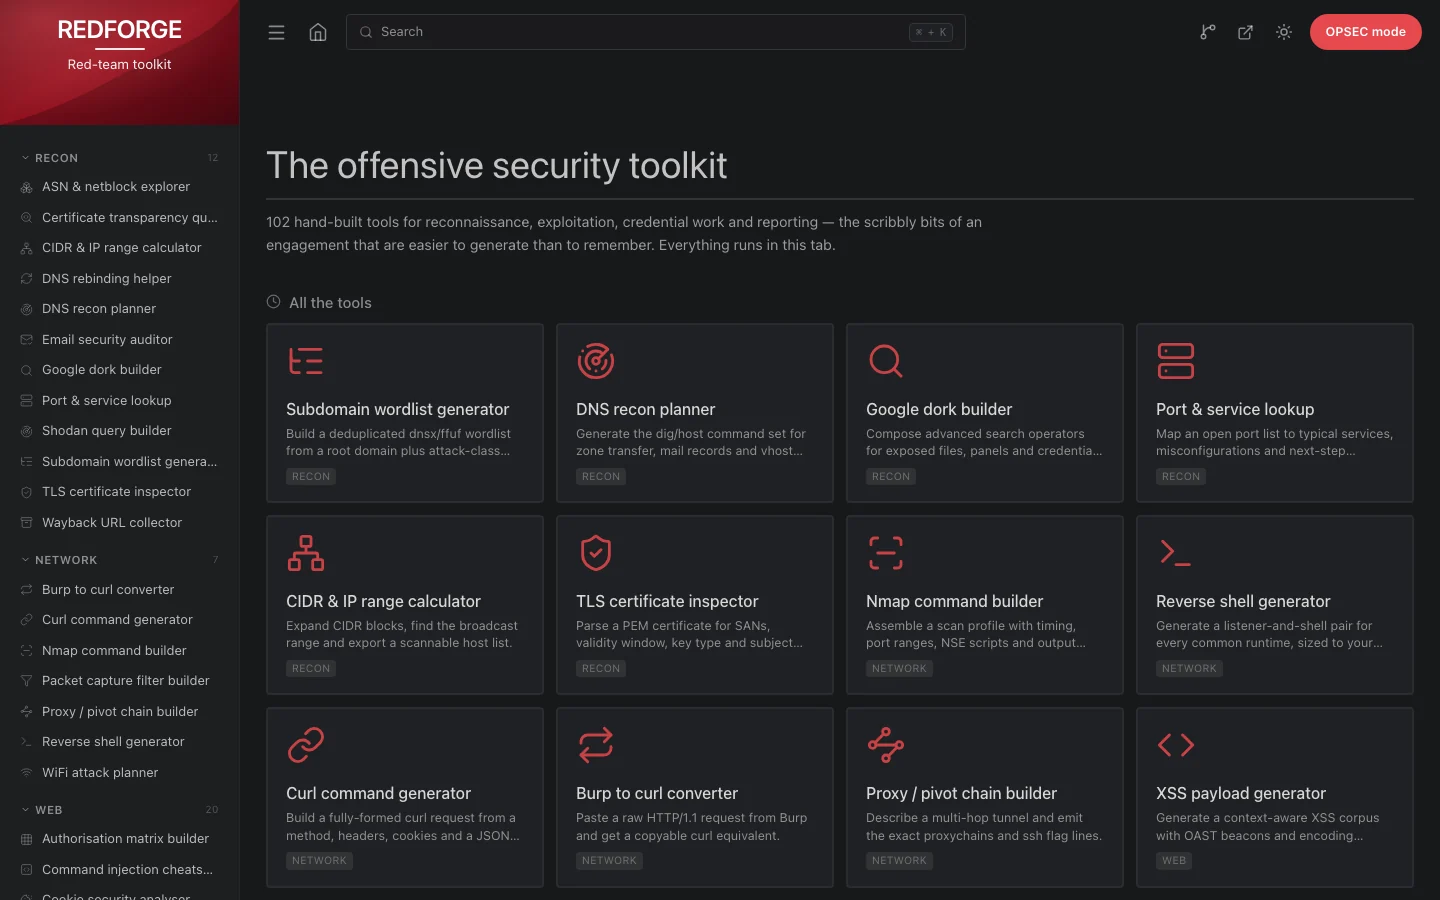
it-tools, reimagined for red teams. 102 browser-side tools for reconnaissance, exploitation, credential work and reporting — the scribbly bits of an engagement that are easier to generate than to remember.
Every tool runs entirely in the tab. No backend, no telemetry, no network calls: paste a request, a certificate, a hash or a wordlist and the answer appears locally.
 |
 |
it-tools solved the "I need a UUID, a base64 decode and a JWT parser right now" problem for developers. A red team needs the same ergonomics for a different set of chores: an nmap line with the right NSE scripts, a Kerberoasting command that names the hashcat mode, an authz matrix that proves BOLA, a CVSS vector you can defend in the report. Those are the tools here.
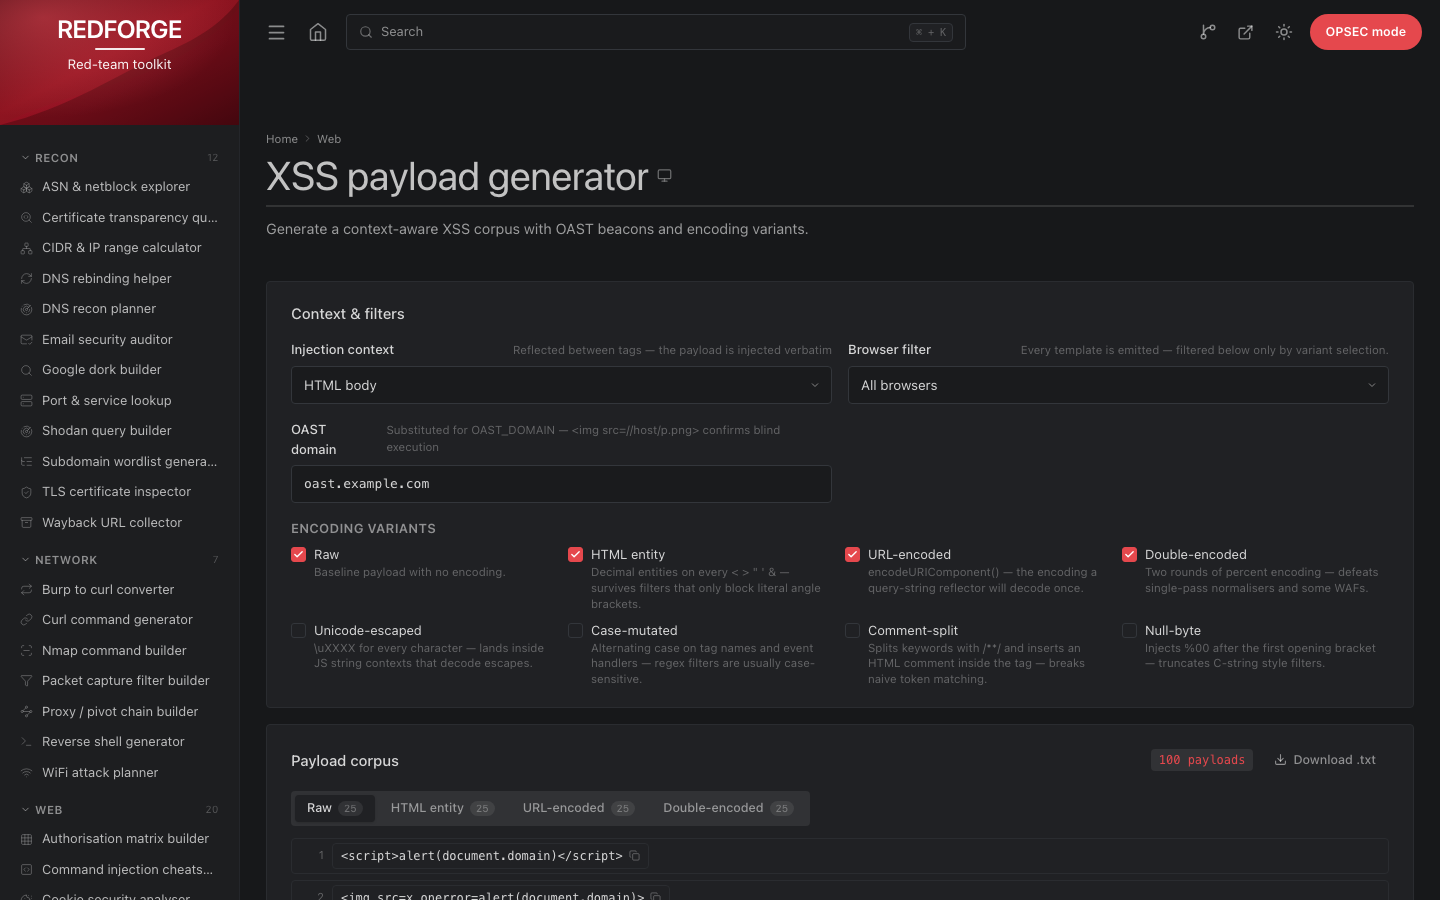
The interface is deliberately familiar — the same 240px hero sidebar, collapsible categories, ⌘K palette, card grid and centred tool column — because muscle memory is the whole point of a toolkit. The content is rebuilt from scratch around offensive work, and every tool computes rather than narrates: the RSA planner really runs Wiener's attack over continued-fraction convergents, the TOTP generator really signs with WebCrypto, the SPF auditor really counts RFC 7208 lookups.
localStorage./kerberos-attack-planner is a real URL you can paste into a ticket.git clone https://github.com/YOUR-USERNAME/redforge.git
cd redforge
docker compose up -d --build
# → http://localhost:8080
docker compose down stops it. The container runs as uid 101 with a read-only root
filesystem, all capabilities dropped, a 128 MB / 1 CPU cap and a /healthz healthcheck.
Without Compose:
docker build -t redforge:latest .
docker run -d --name redforge -p 8080:8080 --read-only \
  --tmpfs /var/cache/nginx --tmpfs /var/run redforge:latest
Change the port with REDFORGE_PORT=9090 docker compose up -d. Replace
YOUR-USERNAME in the clone URLs with the account you push to.
Requires Node 22 or newer.
git clone https://github.com/YOUR-USERNAME/redforge.git
cd redforge
npm ci
npm run dev        # http://127.0.0.1:5178
Production build:
npm run build      # typechecks, then writes dist/
npm run preview    # serve dist/ on :5178
dist/ is plain static files — copy it to any web server. Because routing is
client-side, the host must fall back to index.html for unknown paths (the bundled
nginx.conf already does).
A hot-reloading container is available too:
docker compose --profile dev up
# → http://localhost:5178
| Category | Tools | Focus |
|---|---|---|
| Recon | 12 | Passive mapping, wordlists and target triage. |
| Network | 7 | Scanning, pivoting and transport-layer tooling. |
| Web | 20 | Injection payloads, header abuse and request crafting. |
| Web tokens | 6 | JWT and SAML inspection, forging and signature recovery. |
| Exploit | 11 | Payload scaffolding, privesc and AD tradecraft. |
| Credentials | 8 | Hash identification, cracking plans and credential generation. |
| Crypto | 10 | Digests, key derivation, XOR and classical ciphers. |
| Encoding | 10 | Encode, escape and obfuscate payloads for transport. |
| Social engineering | 7 | Pretext design, lure copy and phishing-assessment planning. |
| OSINT | 3 | Entity pivots, breach and identity correlation planning. |
| Reporting | 8 | Scoring, findings, evidence and rules-of-engagement. |
| Total | 102 |
Passive mapping, wordlists and target triage.
| Tool | Route | What it does |
|---|---|---|
| Subdomain wordlist generator | /subdomain-wordlist-generator | Build a deduplicated dnsx/ffuf wordlist from a root domain plus attack-class prefixes. |
| DNS recon planner | /dns-recon-planner | Generate the dig/host command set for zone transfer, mail records and vhost discovery. |
| Google dork builder | /google-dork-builder | Compose advanced search operators for exposed files, panels and credential leaks. |
| Port & service lookup | /port-service-lookup | Map an open port list to typical services, misconfigurations and next-step checks. |
| CIDR & IP range calculator | /cidr-ip-calculator | Expand CIDR blocks, find the broadcast range and export a scannable host list. |
| TLS certificate inspector | /certificate-inspector | Parse a PEM certificate for SANs, validity window, key type and subject details. |
| DNS rebinding helper | /dns-rebinding-helper | Plan a rebinding payload: zone stanza, browser harness and TTL timing model. |
| ASN & netblock explorer | /asn-netblock-explorer | Parse ASN/prefix data, split it into /24 chunks and emit scannable target lists. |
| Wayback URL collector | /wayback-url-collector | Build CDX API queries for archived URLs, then filter them for parameters and backups. |
| Email security auditor | /email-security-auditor | Score SPF, DKIM and DMARC answers and decide whether the domain can be spoofed. |
| Shodan query builder | /shodan-query-builder | Compose Shodan, Censys and FOFA queries from facets, product filters and netblocks. |
| Certificate transparency query | /certificate-transparency-query | Build crt.sh queries and reduce certificate output to unique hostnames. |
Scanning, pivoting and transport-layer tooling.
| Tool | Route | What it does |
|---|---|---|
| Nmap command builder | /nmap-command-builder | Assemble a scan profile with timing, port ranges, NSE scripts and output flags. |
| Reverse shell generator | /reverse-shell-generator | Generate a listener-and-shell pair for every common runtime, sized to your callback host. |
| Curl command generator | /curl-generator | Build a fully-formed curl request from a method, headers, cookies and a JSON body. |
| Burp to curl converter | /burp-to-curl | Paste a raw HTTP/1.1 request from Burp and get a copyable curl equivalent. |
| Proxy / pivot chain builder | /pivot-chain-builder | Describe a multi-hop tunnel and emit the exact proxychains and ssh flag lines. |
| WiFi attack planner | /wifi-attack-planner | Plan a WPA capture and crack run with aircrack-ng, hcxdumptool and hashcat. |
| Packet capture filter builder | /packet-capture-filter-builder | Build and validate tcpdump BPF and tshark display filters for an engagement. |
Injection payloads, header abuse and request crafting.

