#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
 torvalds/linux
Linux kernel source tree
 mukul975/anthropic-cybersecurity-skills
817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3…
 grafana/loki
Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rshipp/awesome-malware-analysis
Defund the Police.

 ccfos/nightingale
Open-source alerting engine for time-series monitoring data. Connects to Prometheus, VictoriaMetrics, ElasticSearch, and other data sources. Supports…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
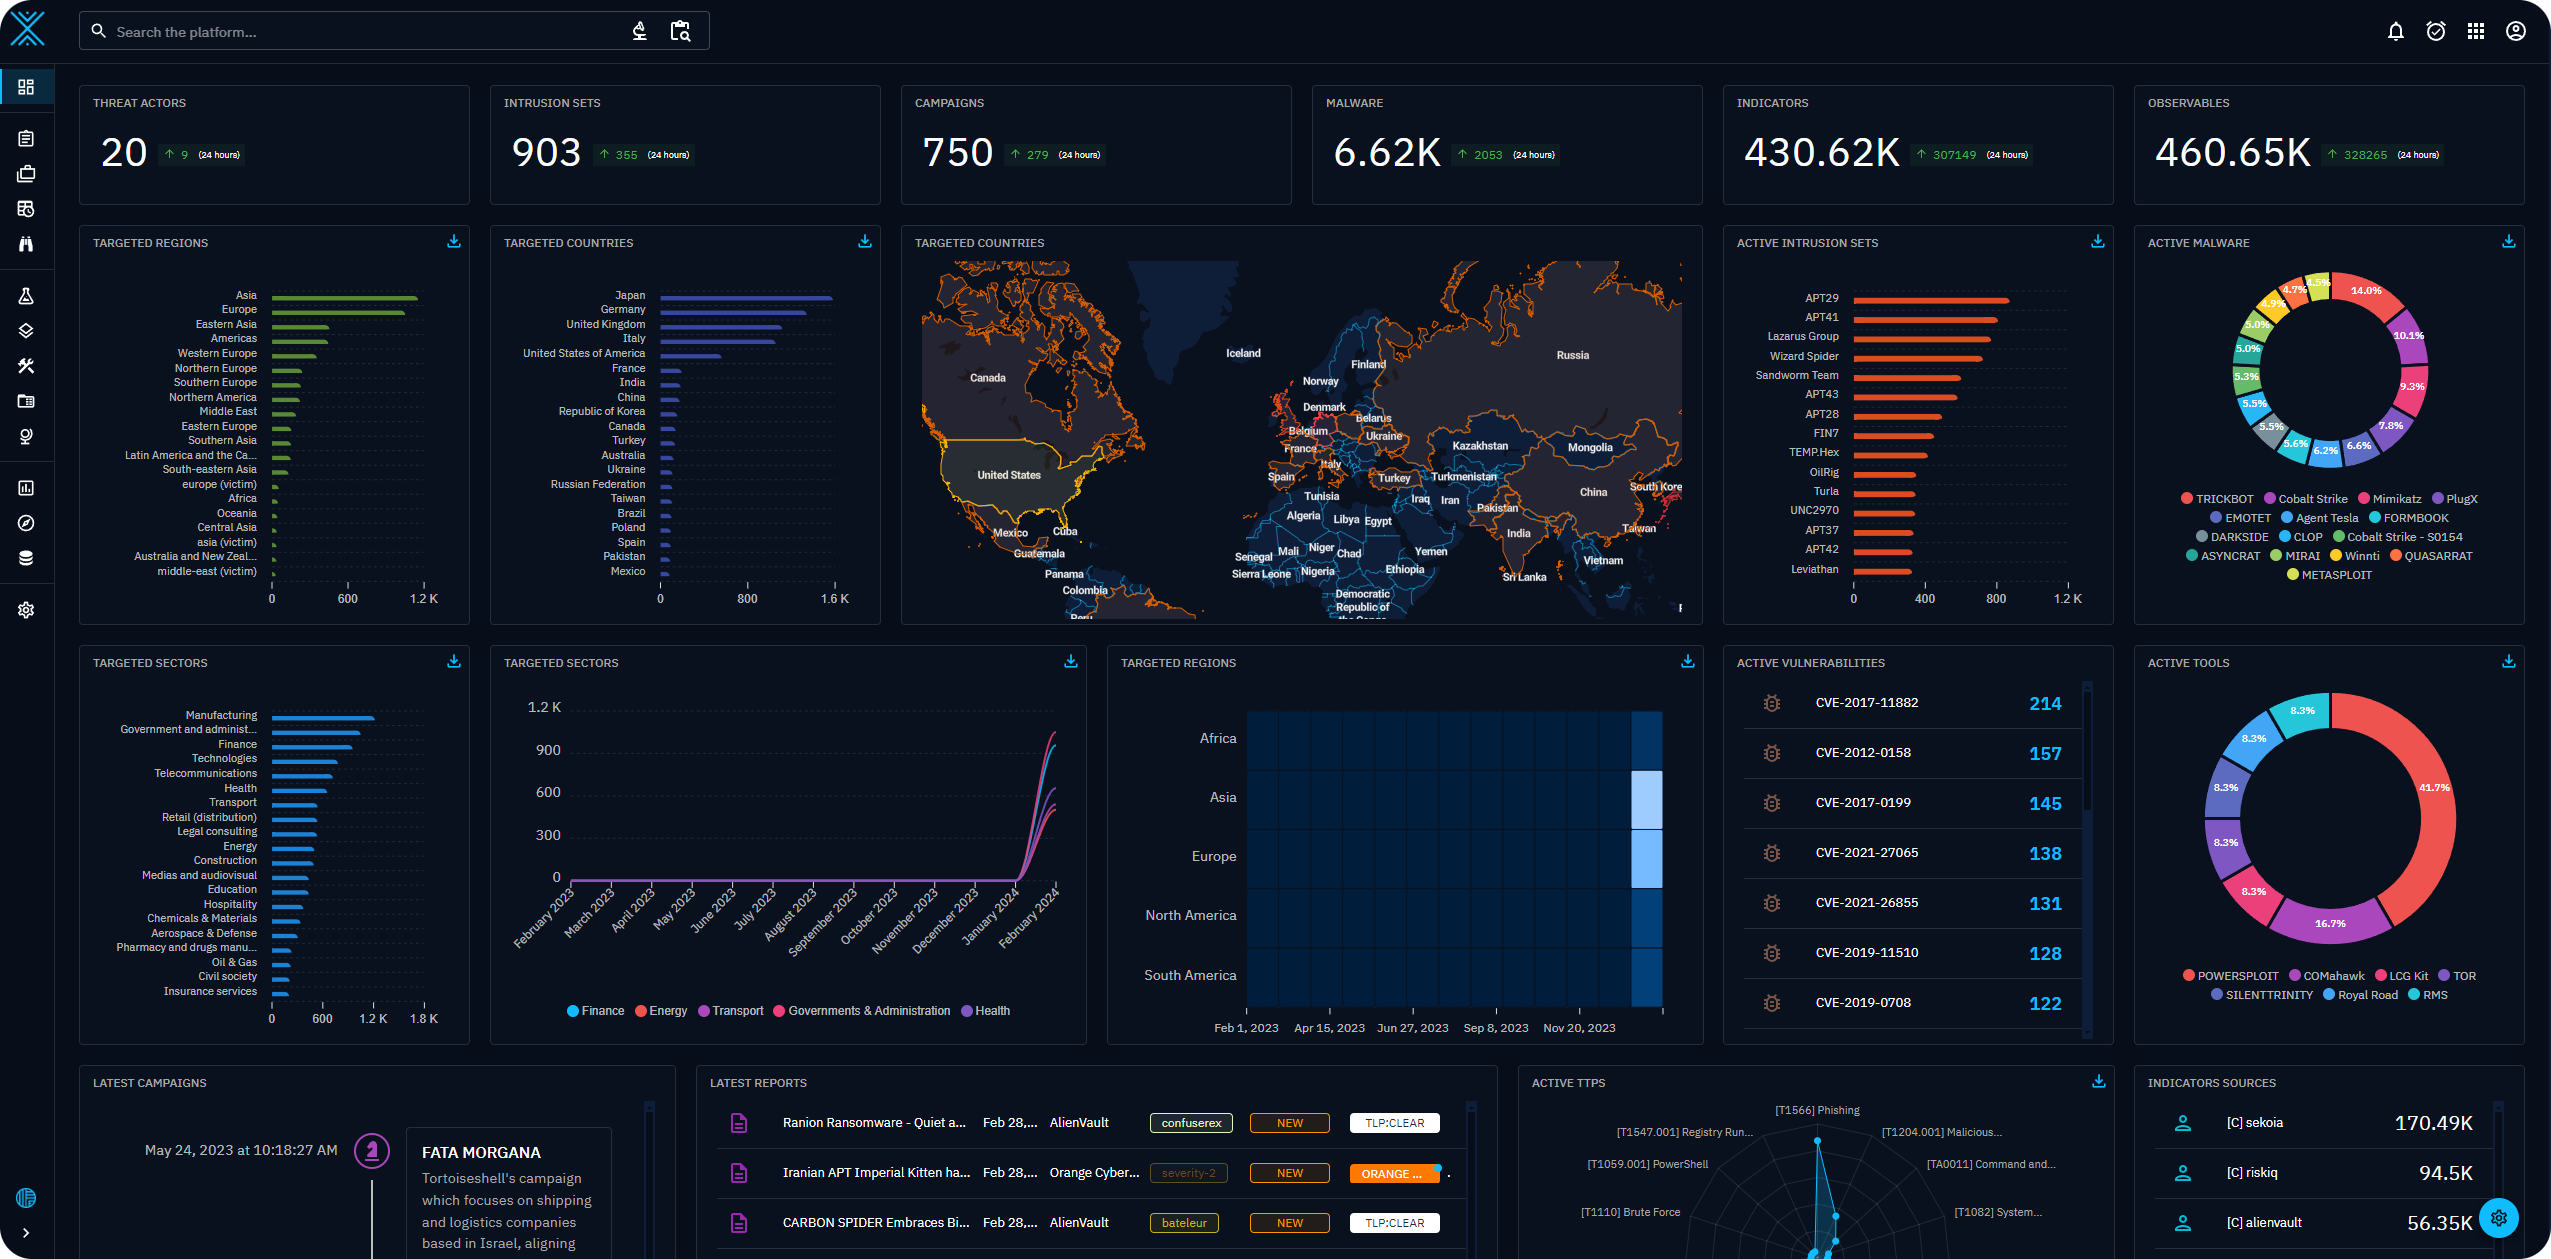 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 cachethq/cachet
🚦 Cachet, the open source, self-hosted status page system.
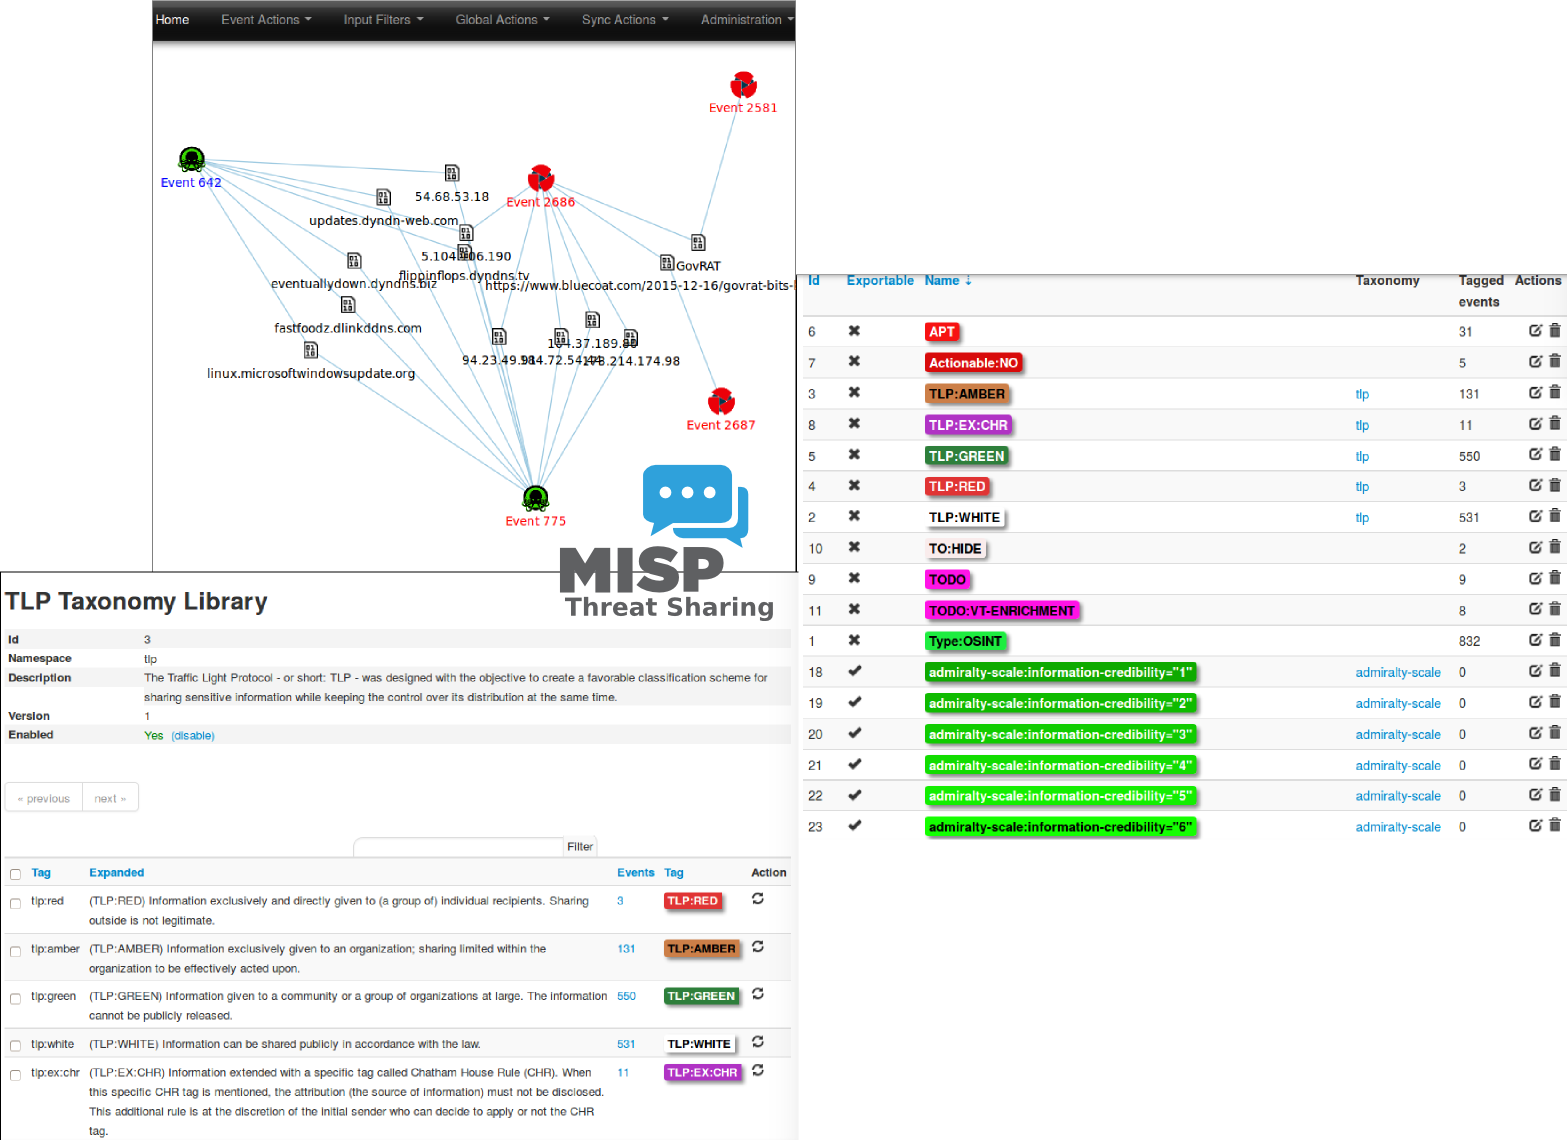 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…