 #1
Tools for analyzing network traffic and communication logs to investigate security incidents.
Kitploit recommended
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
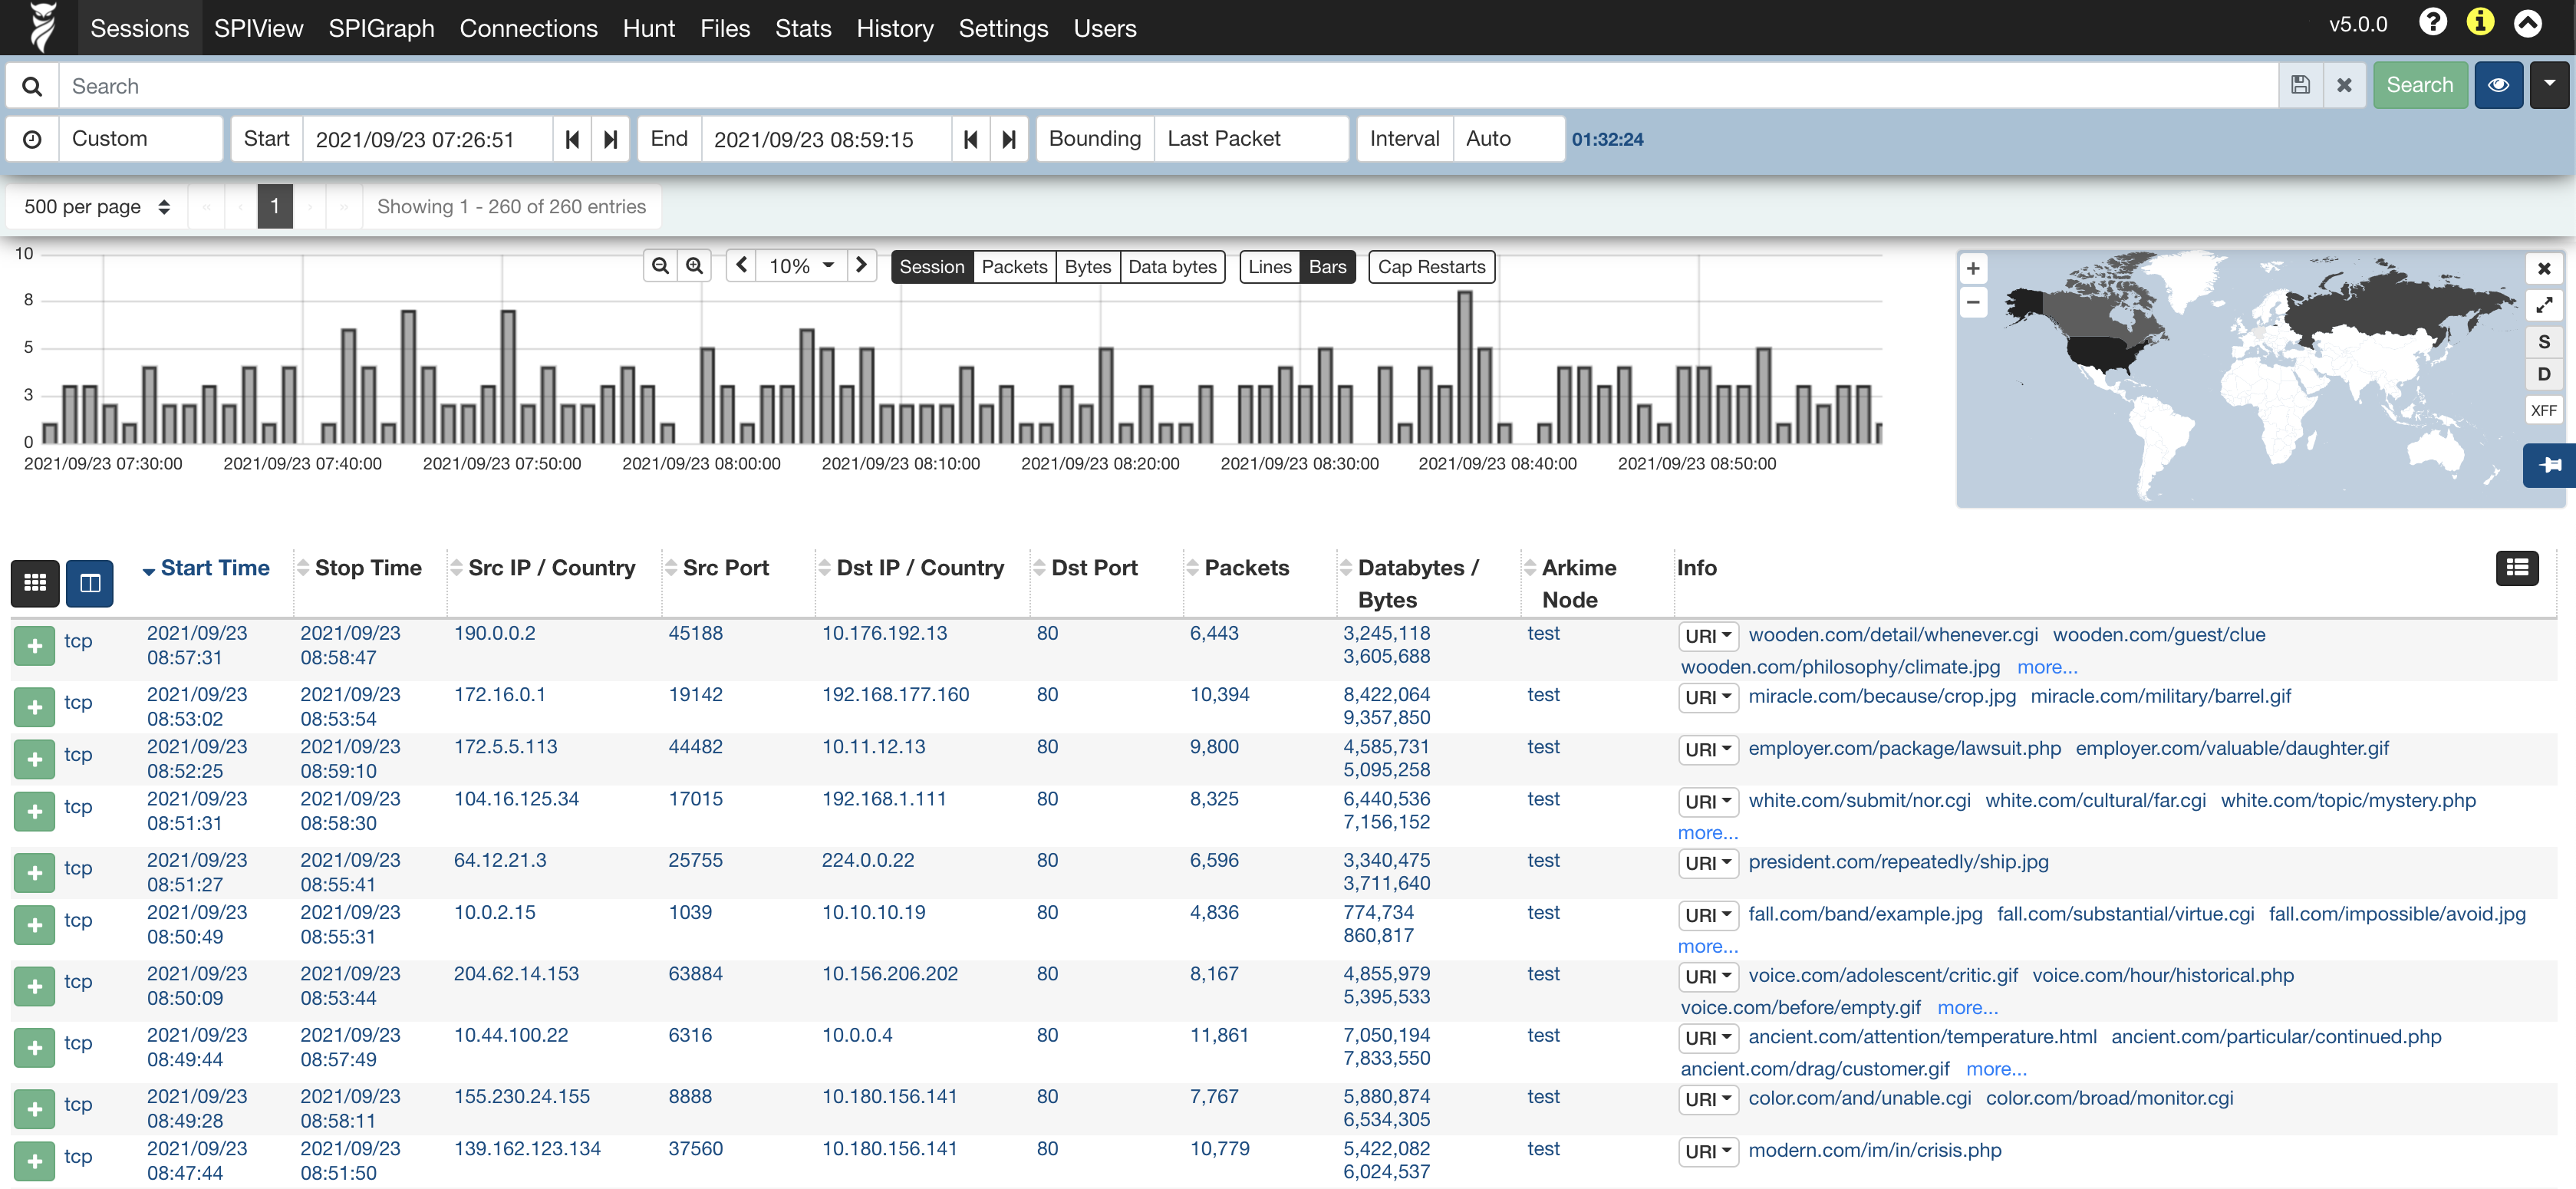 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
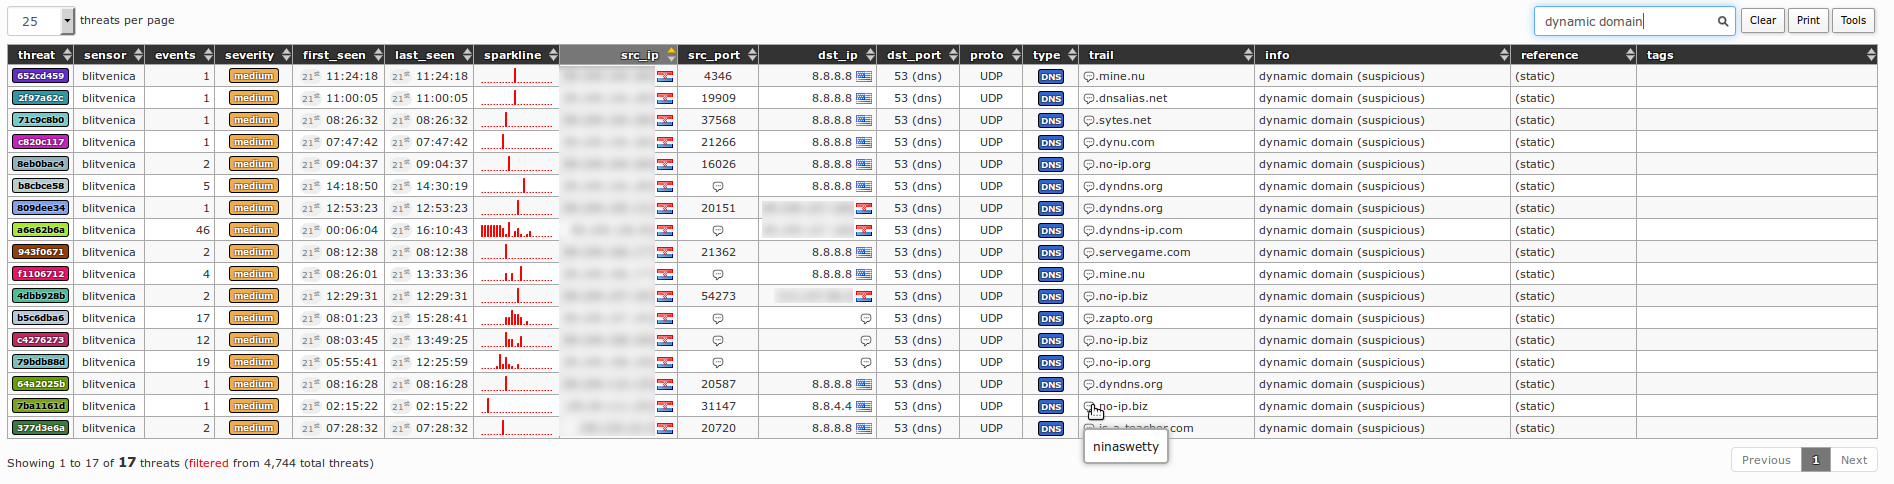 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
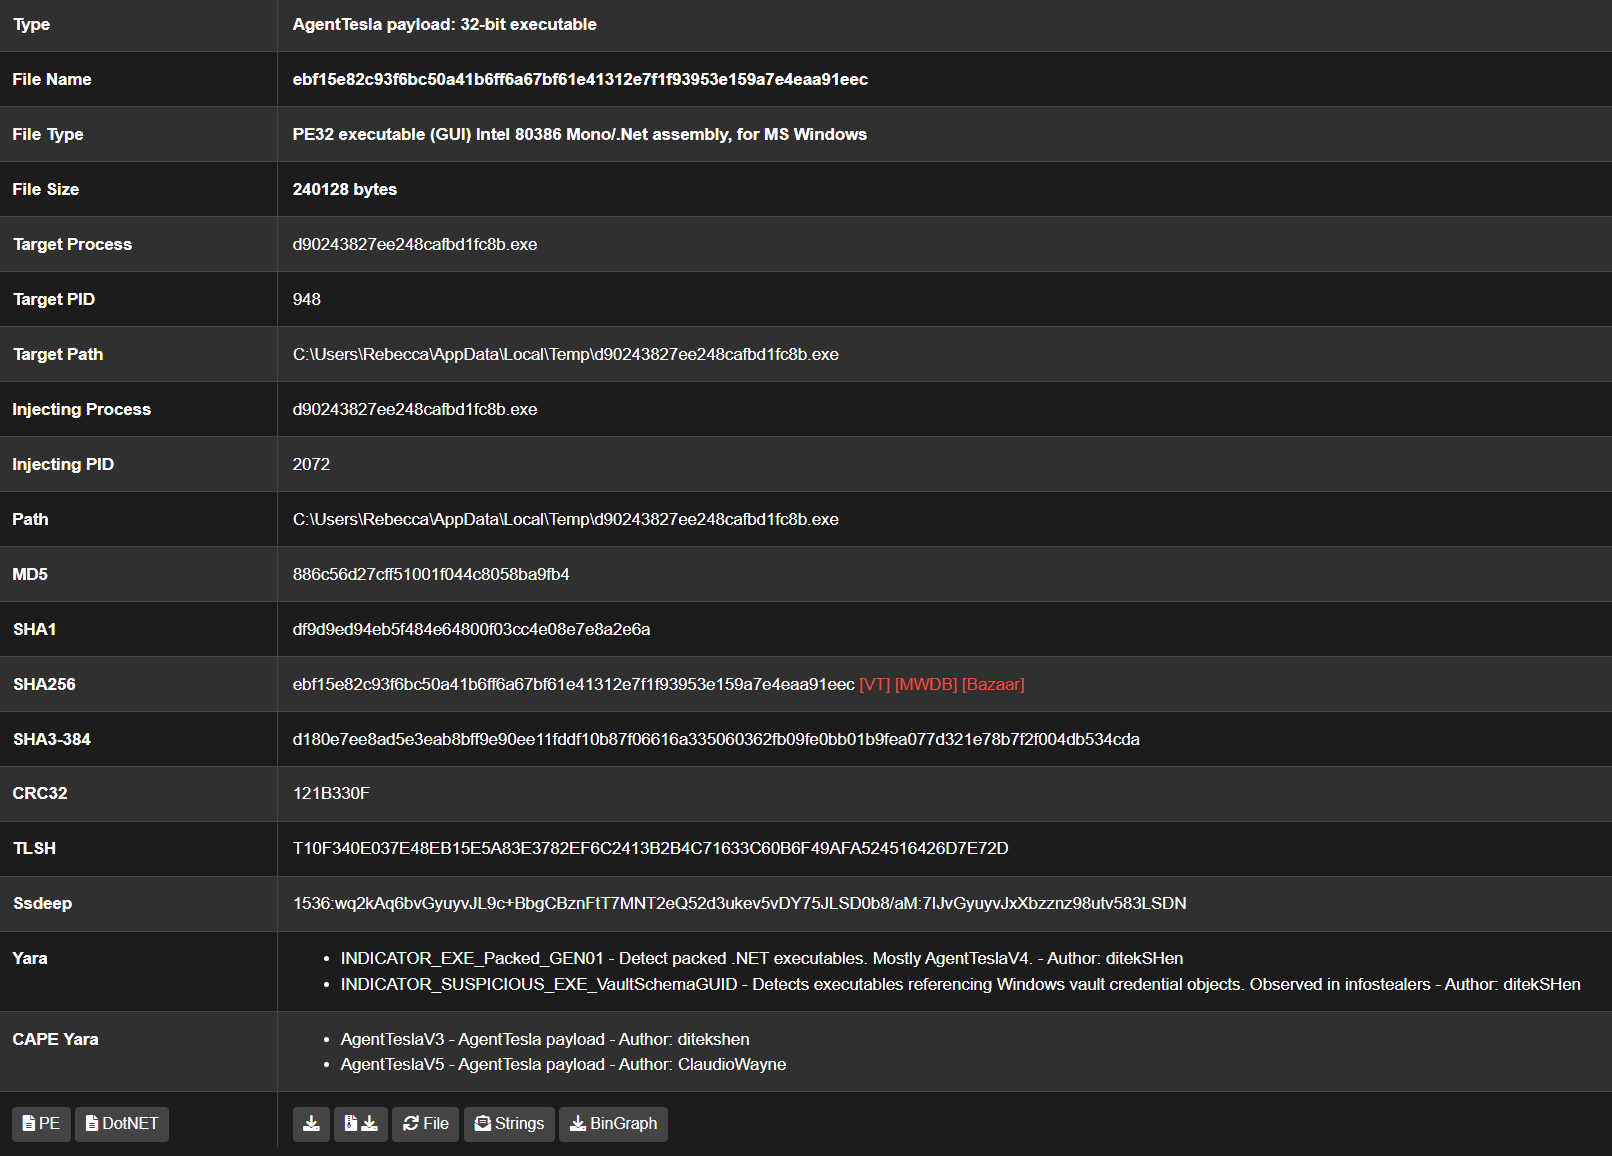 kevoreilly/capev2
Malware Configuration And Payload Extraction
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
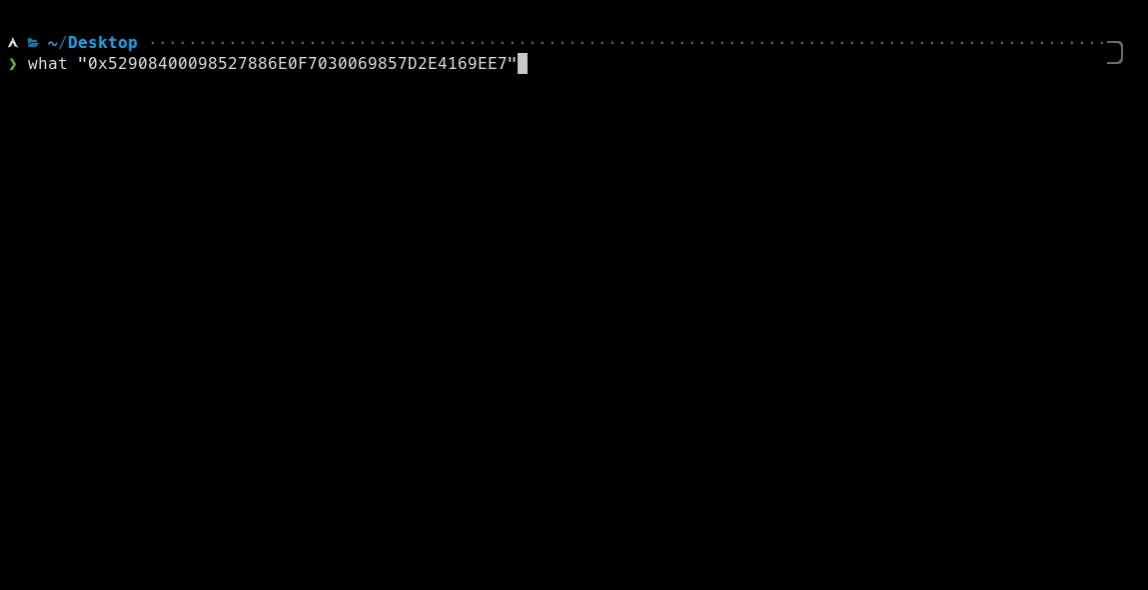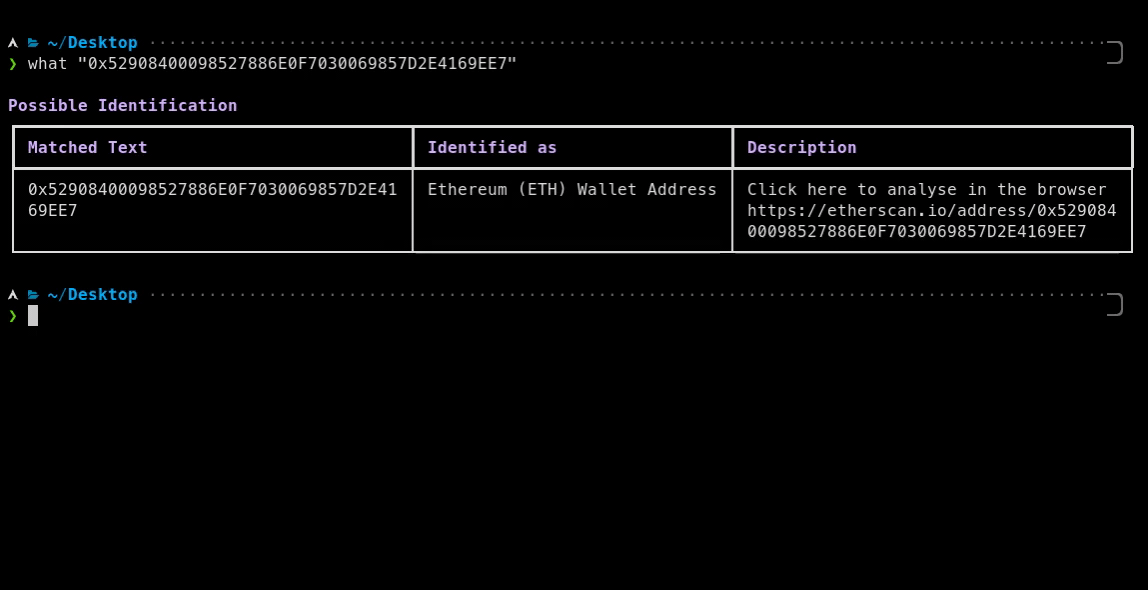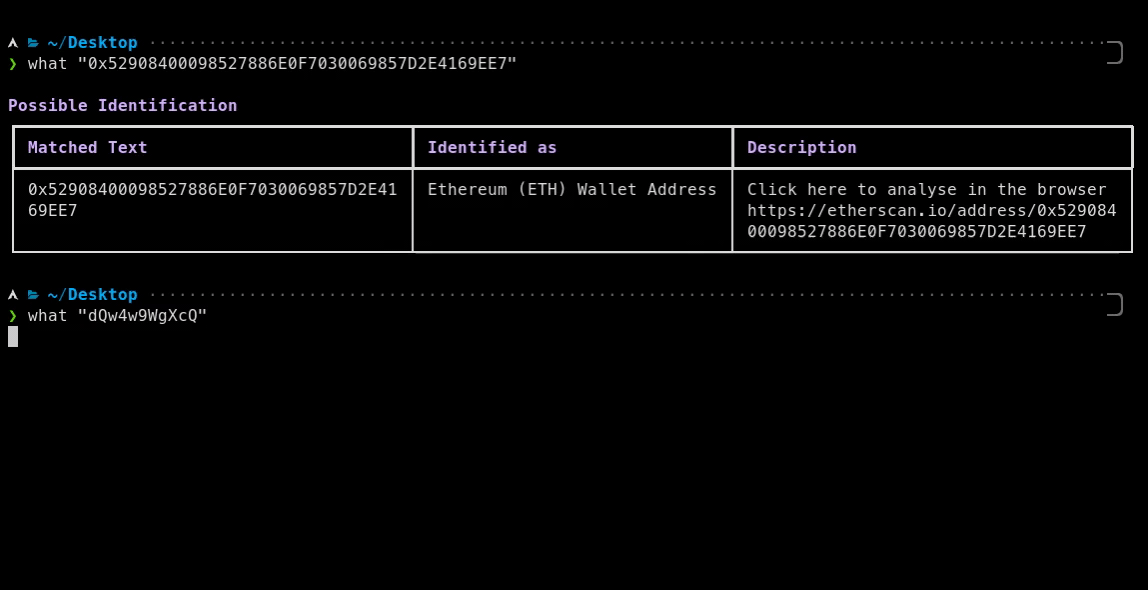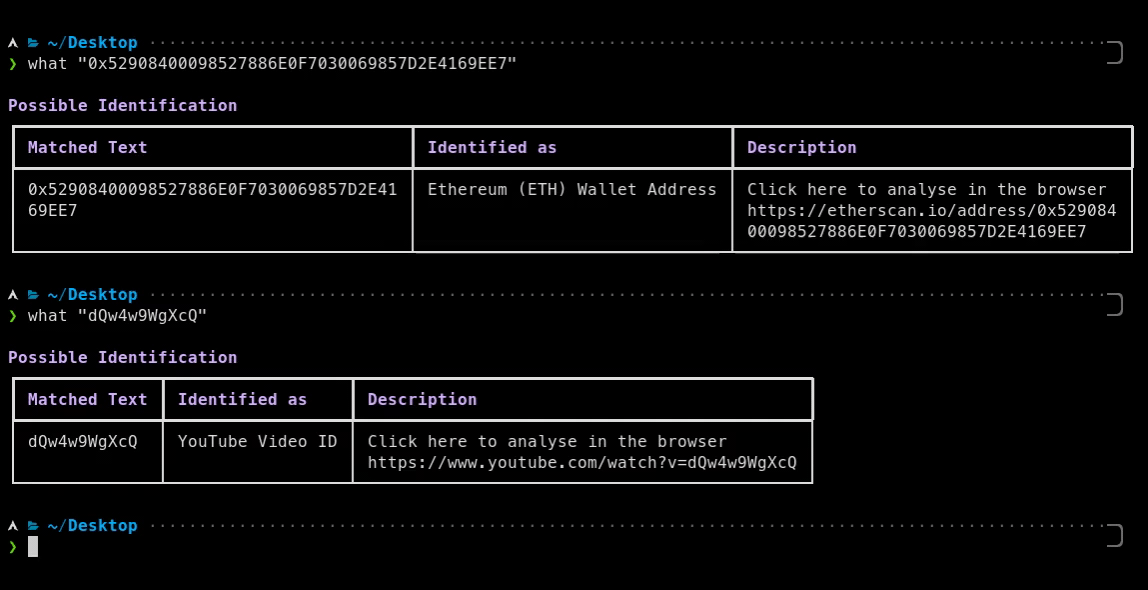 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
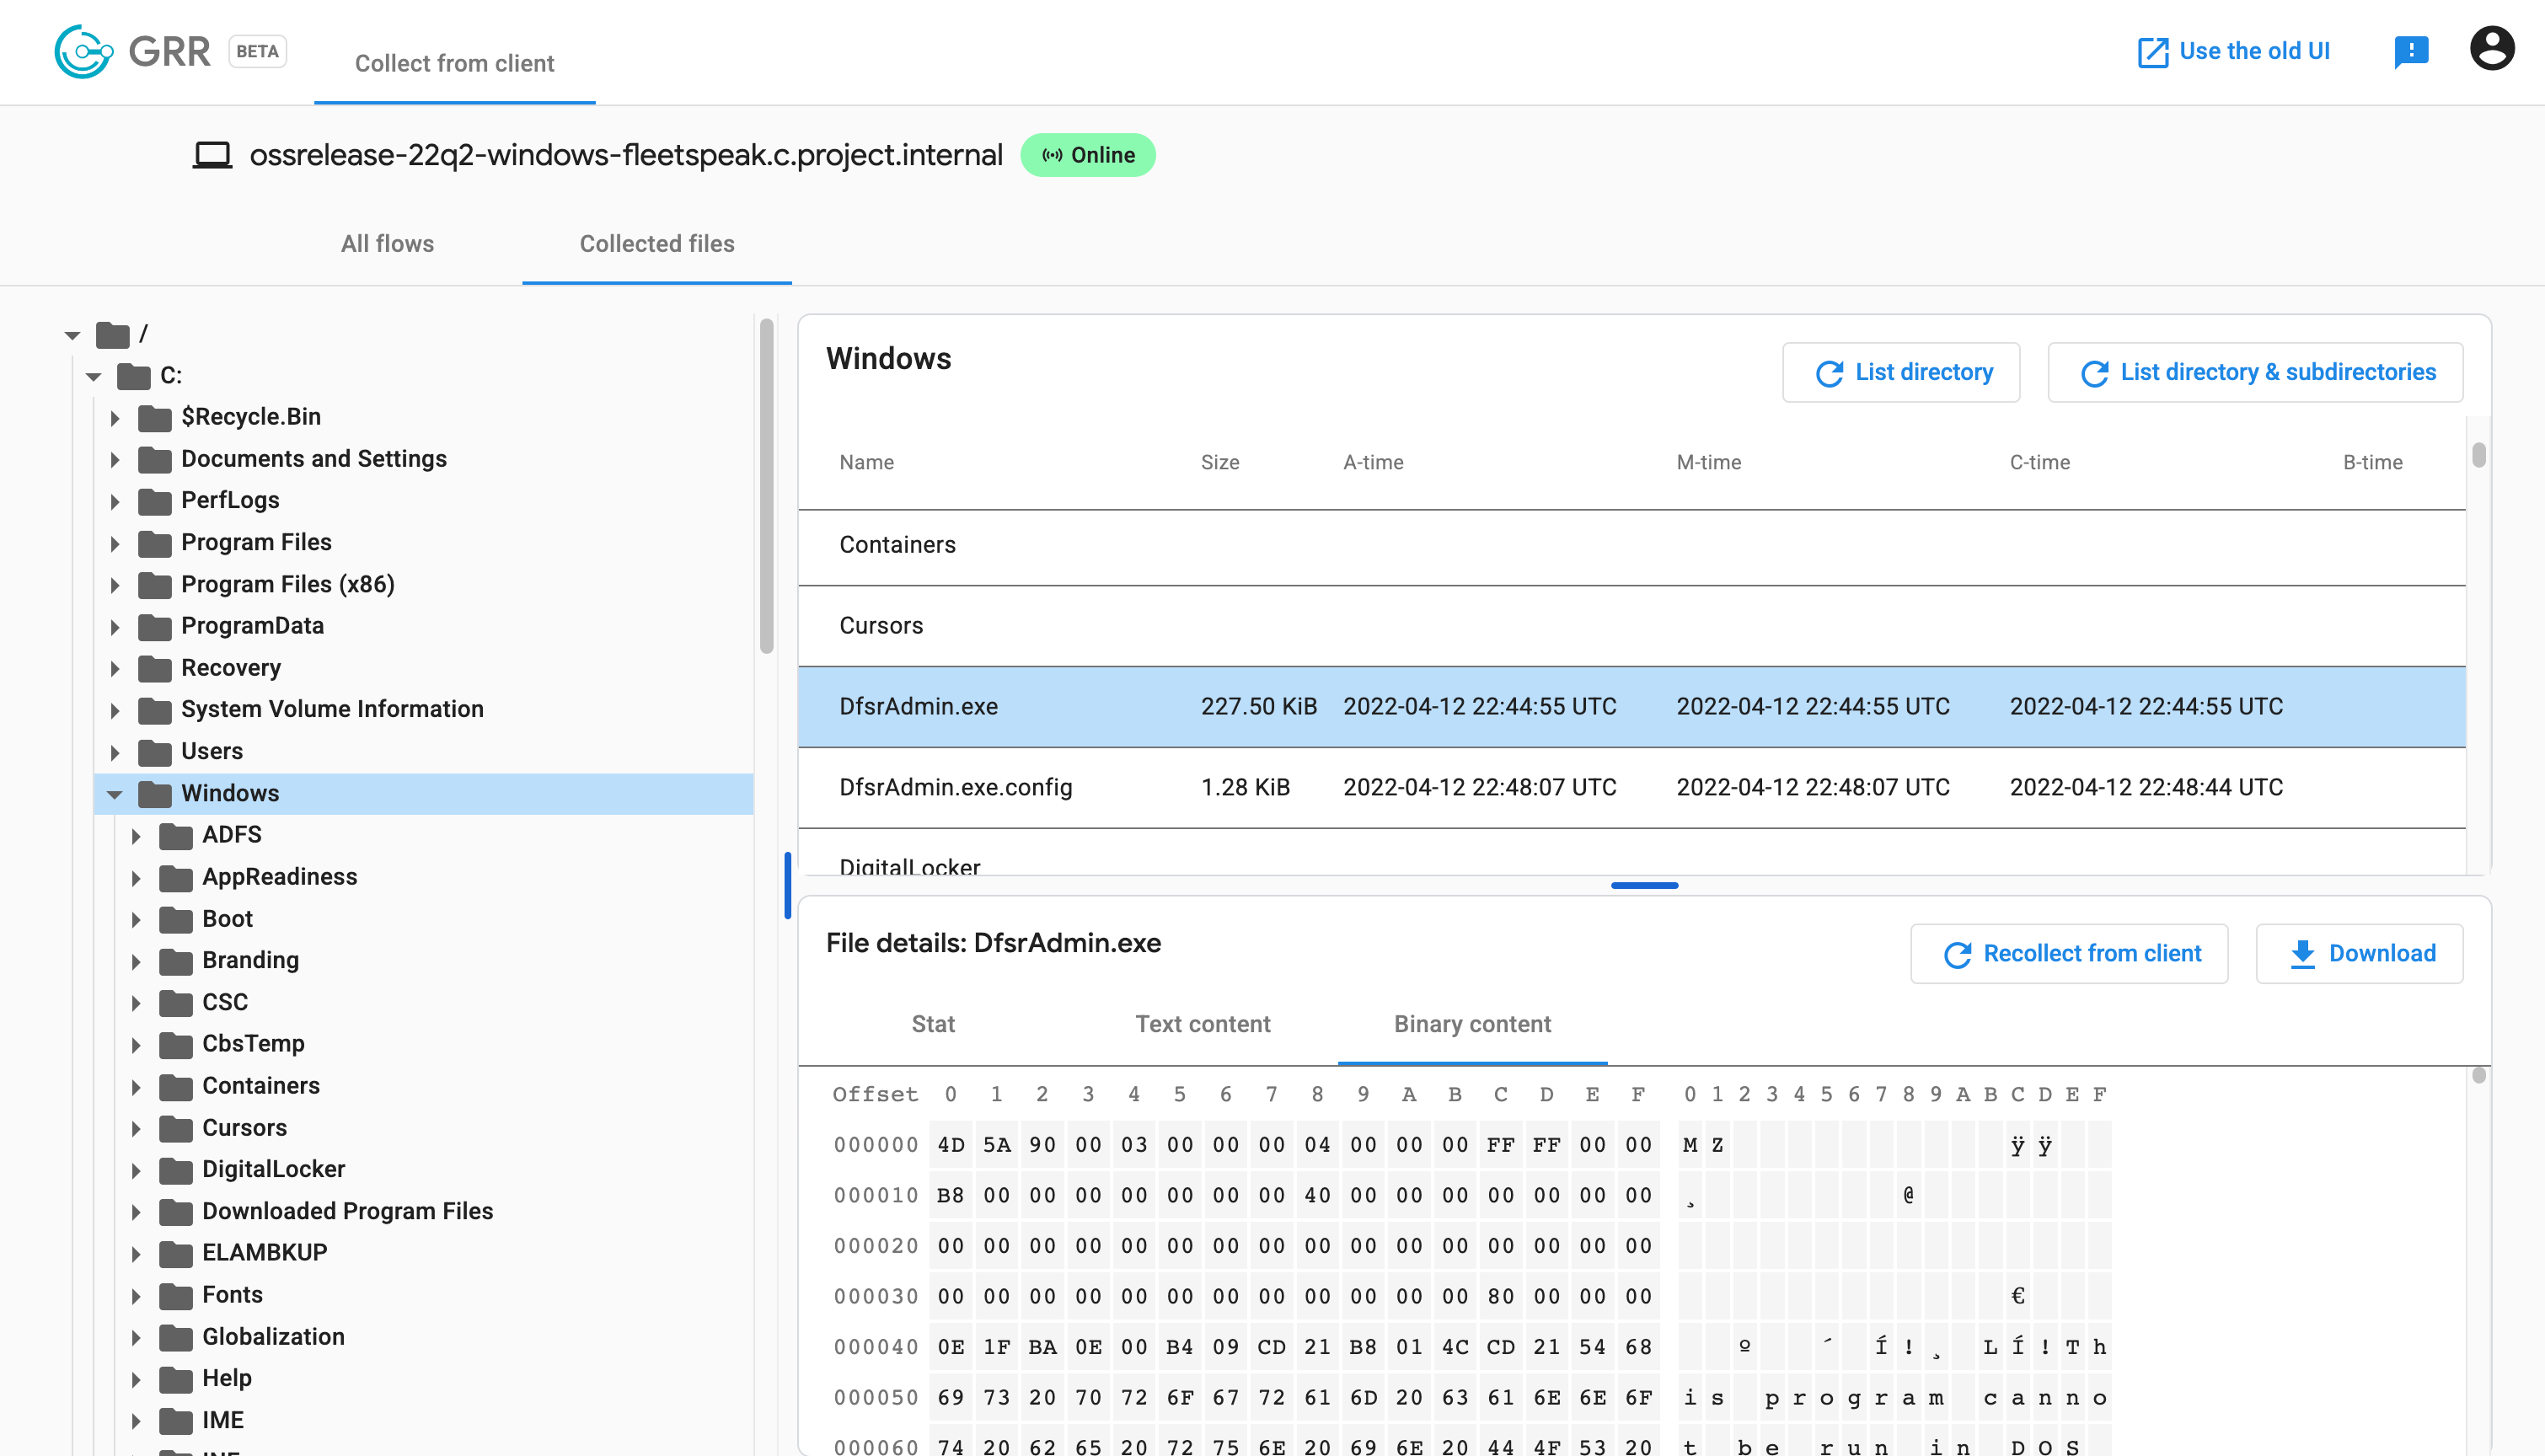 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
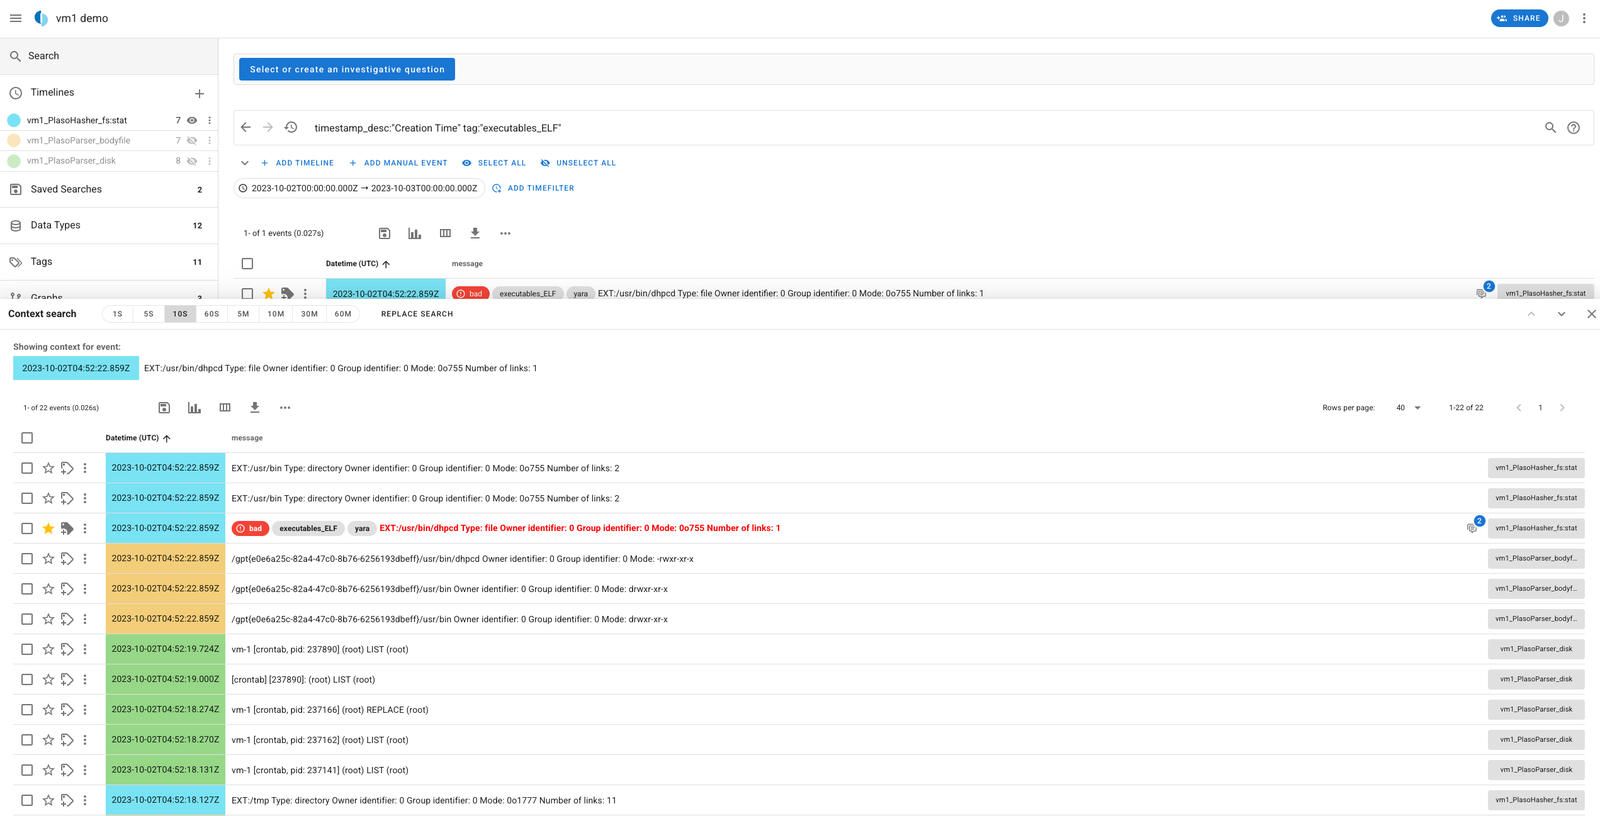 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 the-tcpdump-group/tcpdump
the TCPdump network dissector
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…