

Krawl v2.4.0
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging vulnerabilities using realistic, randomly generated decoy data and AI-generated HTML templates.
Krawl
A modern, customizable web honeypot server designed to detect and track malicious activity from attackers and web crawlers through deceptive web pages, fake credentials, and canary tokens.




Table of Contents
- Demo
- What is Krawl?
- Krawl Dashboard
- Deployment Modes
- Krawl Banlist
- Quickstart
- Configuration
- Ban Malicious IPs
- Attack Detection
- IP Reputation
- Deception using AI
- Running Behind a Reverse Proxy or CDN
- Metrics & Monitoring
- Documentation
- Contributing
Demo
Tip: crawl the robots.txt paths for additional fun
Krawl URL: http://demo.krawlme.com
View the dashboard http://demo.krawlme.com/das_dashboard
What is Krawl?
Krawl is a cloud‑native deception server designed to detect, delay, and analyze malicious attackers, web crawlers and automated scanners.
It creates realistic fake web applications filled with low‑hanging fruit such as admin panels, configuration files, and exposed fake credentials to attract and identify suspicious activity.
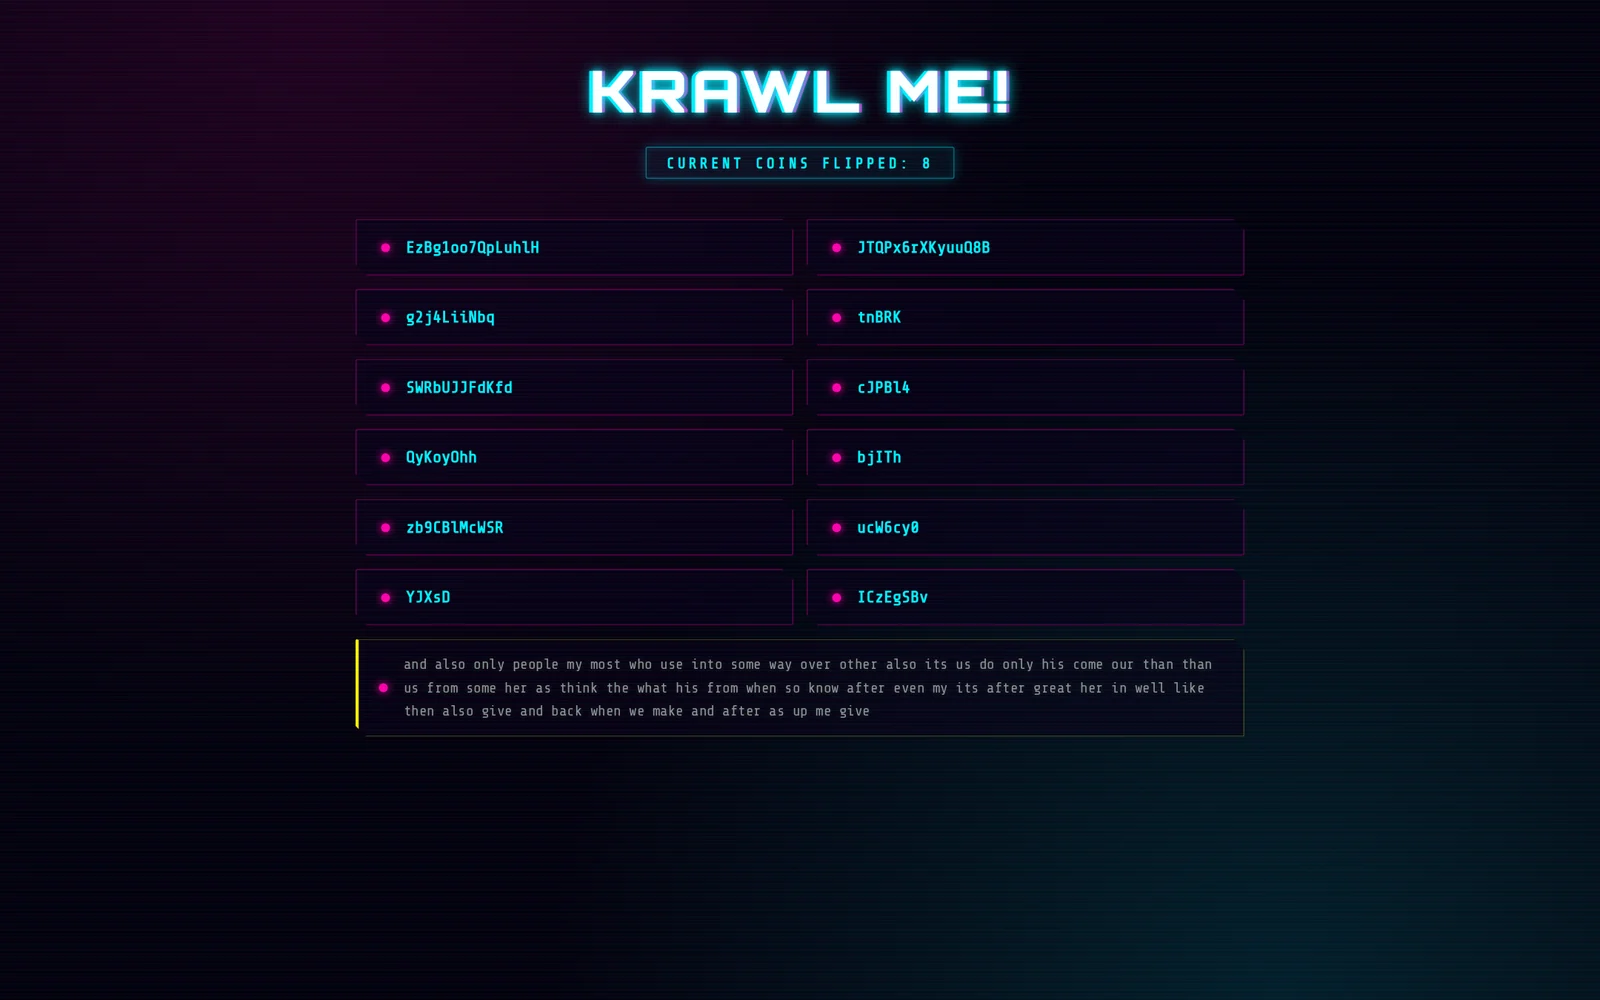
By wasting attacker resources, Krawl helps clearly distinguish malicious behavior from legitimate crawlers.
It features:
- AI Generated Deception Pages: Let attackers help generate your fake vulnerable attack surface
- Spider Trap Pages: Infinite random links to waste crawler resources based on the spidertrap project
- Fake Login Pages: WordPress, phpMyAdmin, admin panels
- Honeypot Paths: Advertised in robots.txt to catch scanners
- Fake Credentials: Realistic-looking usernames, passwords, API keys
- Canary Token Integration: External alert triggering
- Random server headers: Confuse attacks based on server header and version
- Real-time Dashboard: Monitor suspicious activity
- YARA Attack Detection: over 3,100 bundled rules for web attacks, exploit payloads, over 2,500 CVEs, IoT botnets and exposure probes, answered with matching fake replies
- Customizable fake content: every fake page and attack reply is a file listed in
responses/manifest.yaml - Random Error Injection: Mimic real server behavior
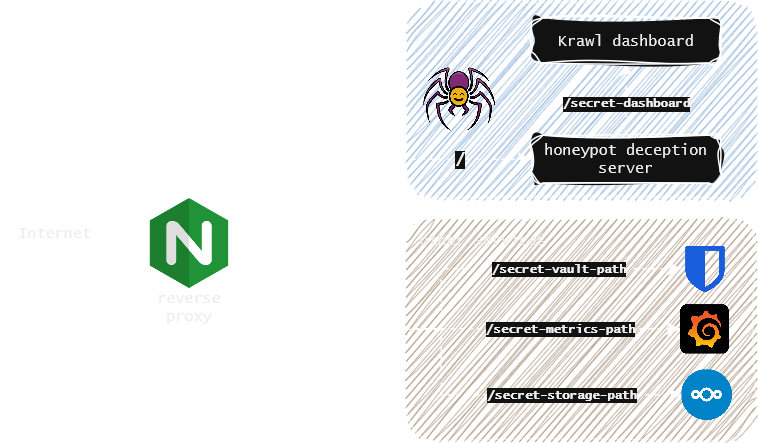
You can easily expose Krawl alongside your other services to shield them from web crawlers and malicious users using a reverse proxy. For more details, see the Reverse Proxy documentation.
Krawl Dashboard
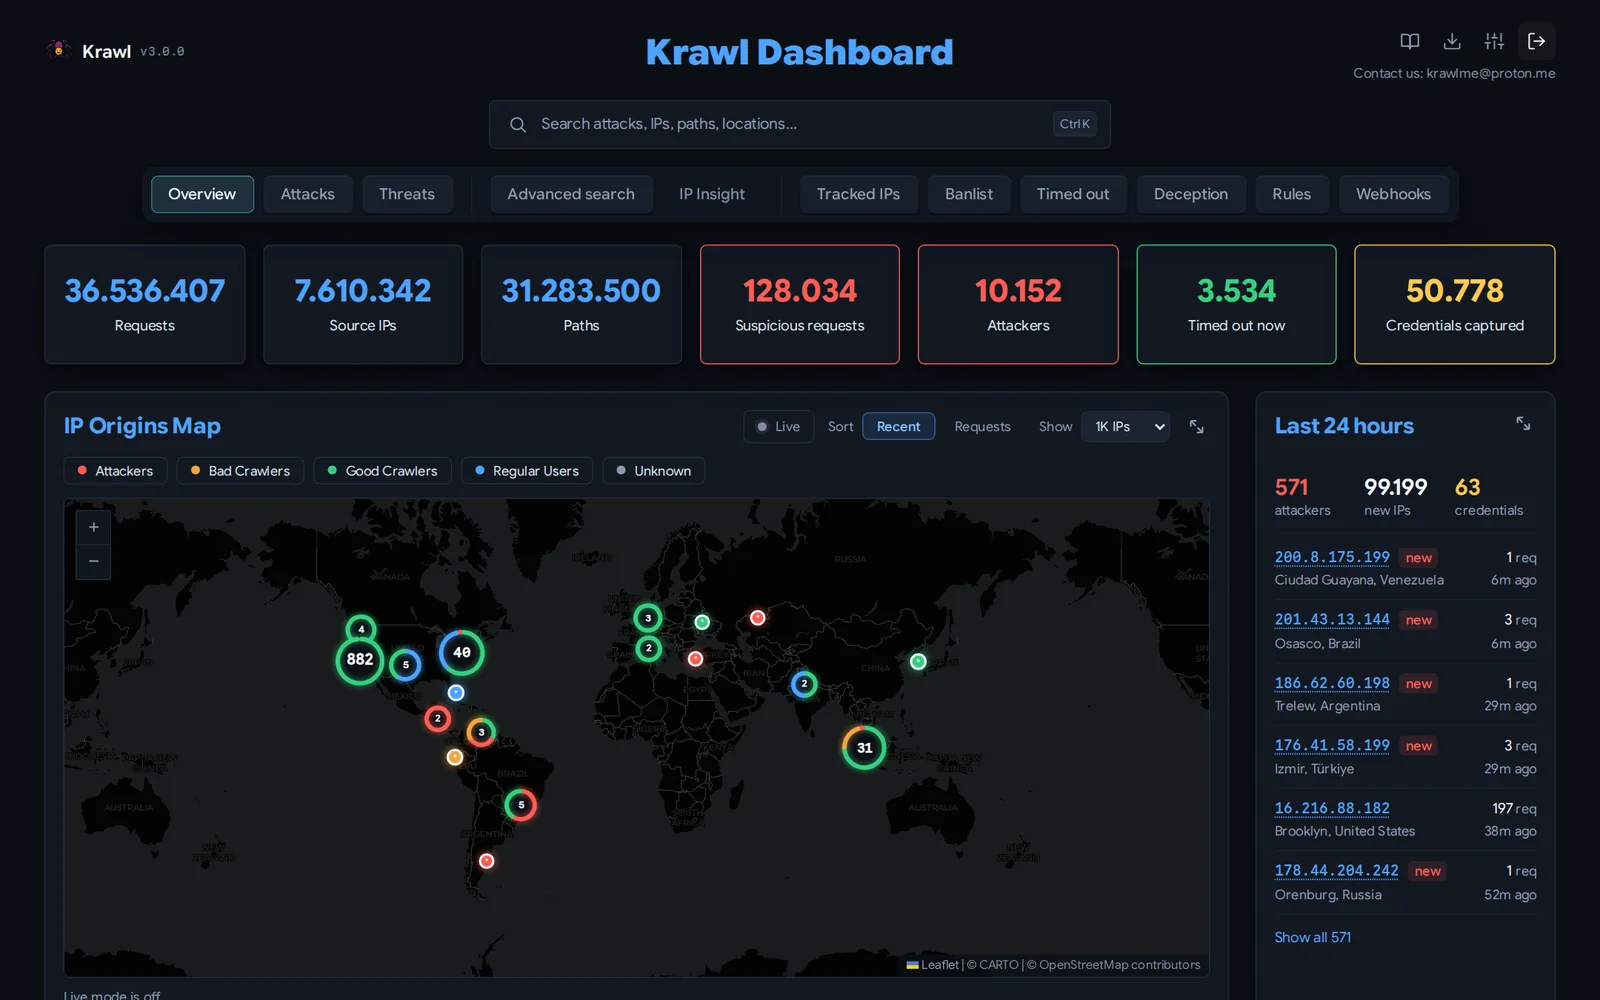
Krawl provides a comprehensive dashboard, accessible at a random secret path generated at startup or at a custom path configured via KRAWL_DASHBOARD_SECRET_PATH. This keeps the dashboard hidden from attackers scanning your honeypot.
Five tabs are open to anyone with the dashboard path:
- Overview: high-level view of attack activity: an interactive map of IP origins, recent suspicious requests, and top IPs, User-Agents, and paths.
- Attacks: detailed breakdown of captured credentials, honeypot triggers, and detected attack types (SQLi, XSS, path traversal, etc.) with charts and tables.
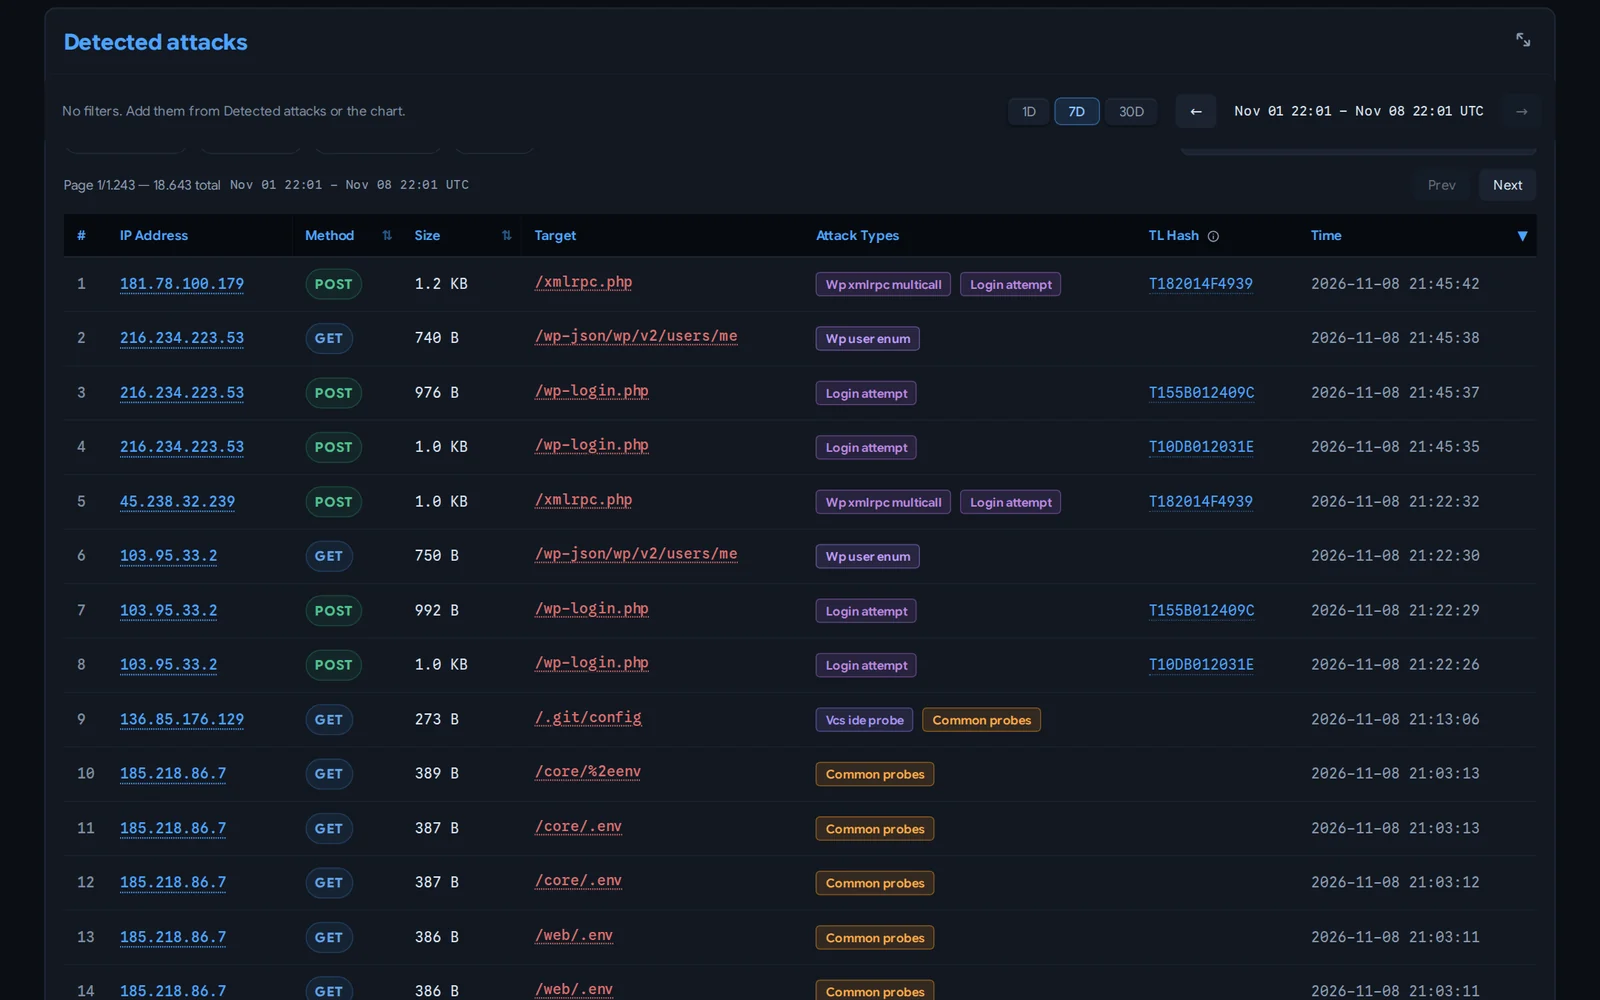
-
Threats: payloads grouped into campaigns by TLSH fuzzy hash, so a webshell and its edited variants read as one campaign rather than unrelated hits, with an index of every captured file.
-
Advanced search: find stored requests by path, host, IP, referer, user agent, method, raw request text and HTTP headers.
-
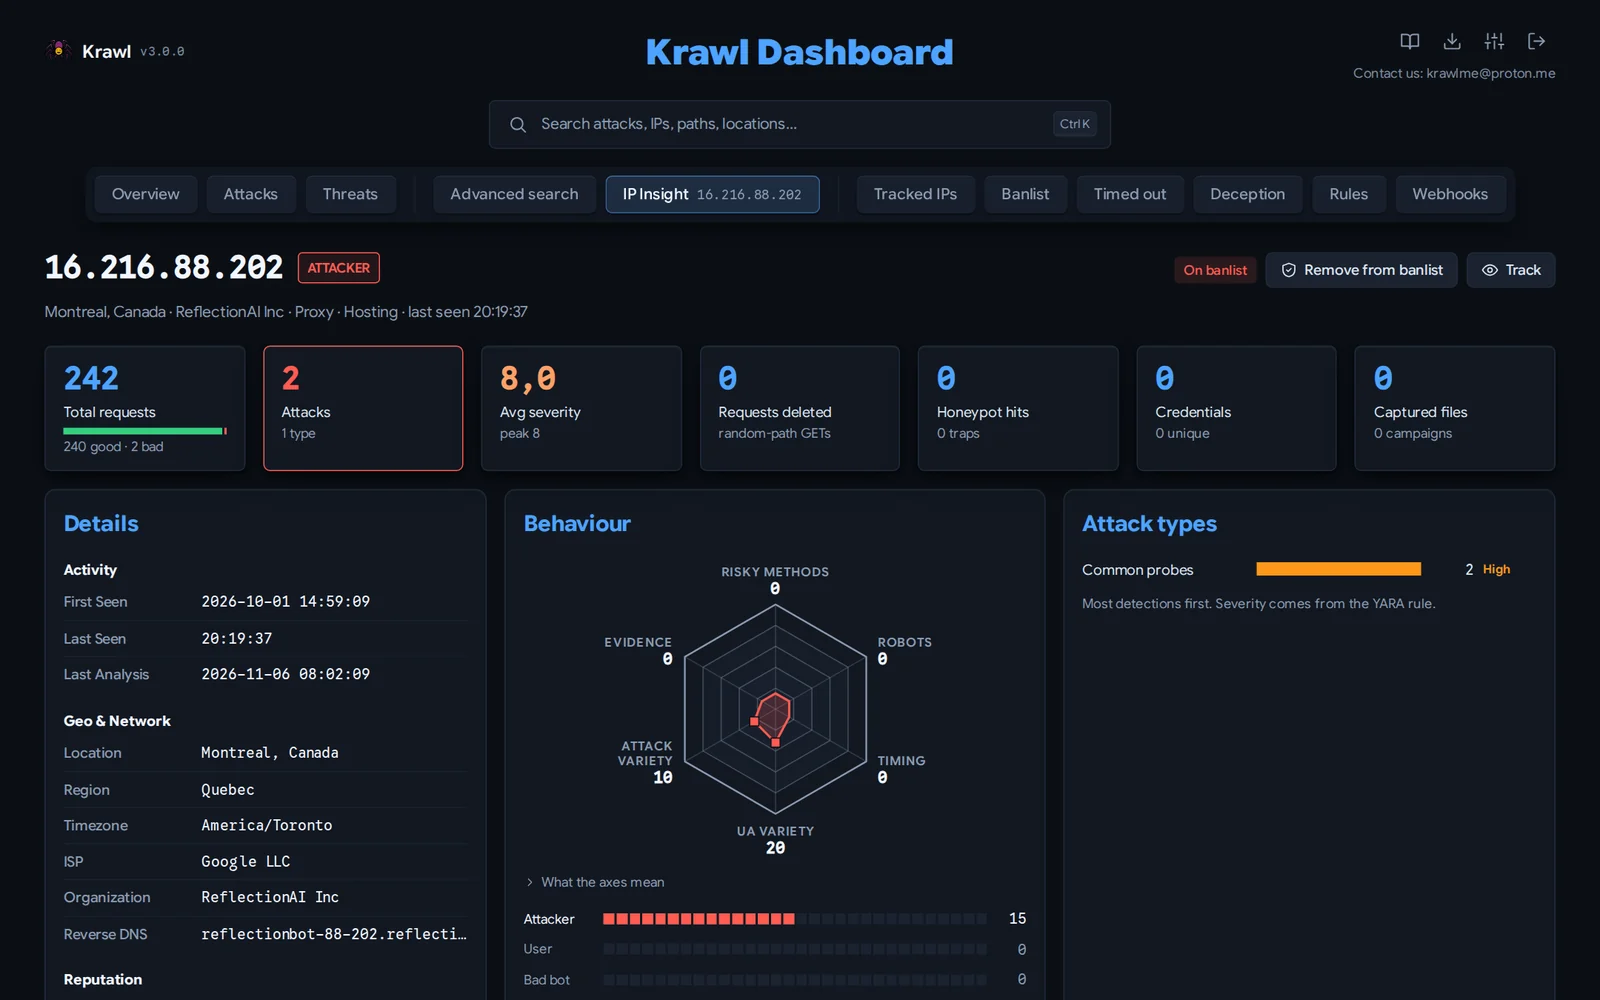
IP Insight: in-depth forensic view of a selected IP: geolocation, ISP/ASN info, reputation flags, a behaviour hexagon, ranked attack types, good and bad request counts, average severity, referer history, captured files and credentials, category timeline, and full access history.
Additionally, after authenticating with the dashboard password, protected tabs become available: