
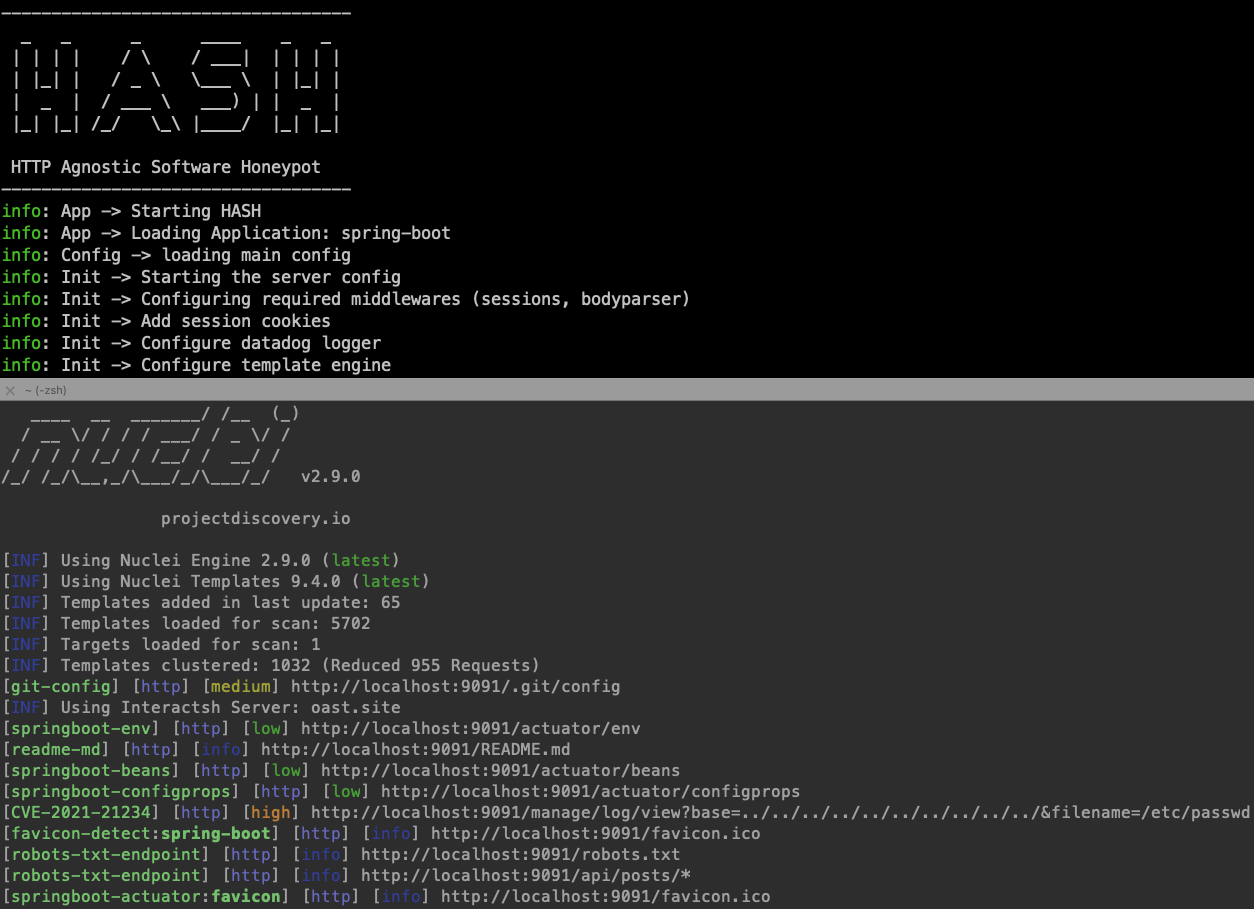
HASH
 datadog/hash
YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
defensive-toolsweb-securitynetwork-security+1
1422 days ago
Tools for testing, exploiting, and securing web applications and APIs.
datadog/hashYAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
 random-robbie/jira-scan
CVE-2017-9506 - SSRF
 exodusintel/chromium-941743
Chrome v8 1Day Exploit by István Kurucsai
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 euphrat1ca/cve-2020-0618
SQL Server Reporting Services(CVE-2020-0618)中的RCE
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 code-zm/plex2shell
CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656
 s0md3v/shiva
Improved DOS exploit for wordpress websites (CVE-2018-6389)
 wavestone-cdt/wavecrack
Wavestone's web interface for password cracking with hashcat
 0xjohnnydev/webkit-uaf-angle-oob-analysis
Analysis of CVE-2025-43529 (WebKit UAF) + CVE-2025-14174 (ANGLE OOB) exploit chain - iOS Safari
 liveoverflow/ctf-screenshotter
CTF web challenge simulating a real-world screenshotting vulnerability, with Docker setup and video writeup for hands-on security education.
 serain/bbrecon
Python library and CLI for the Bug Bounty Recon API
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
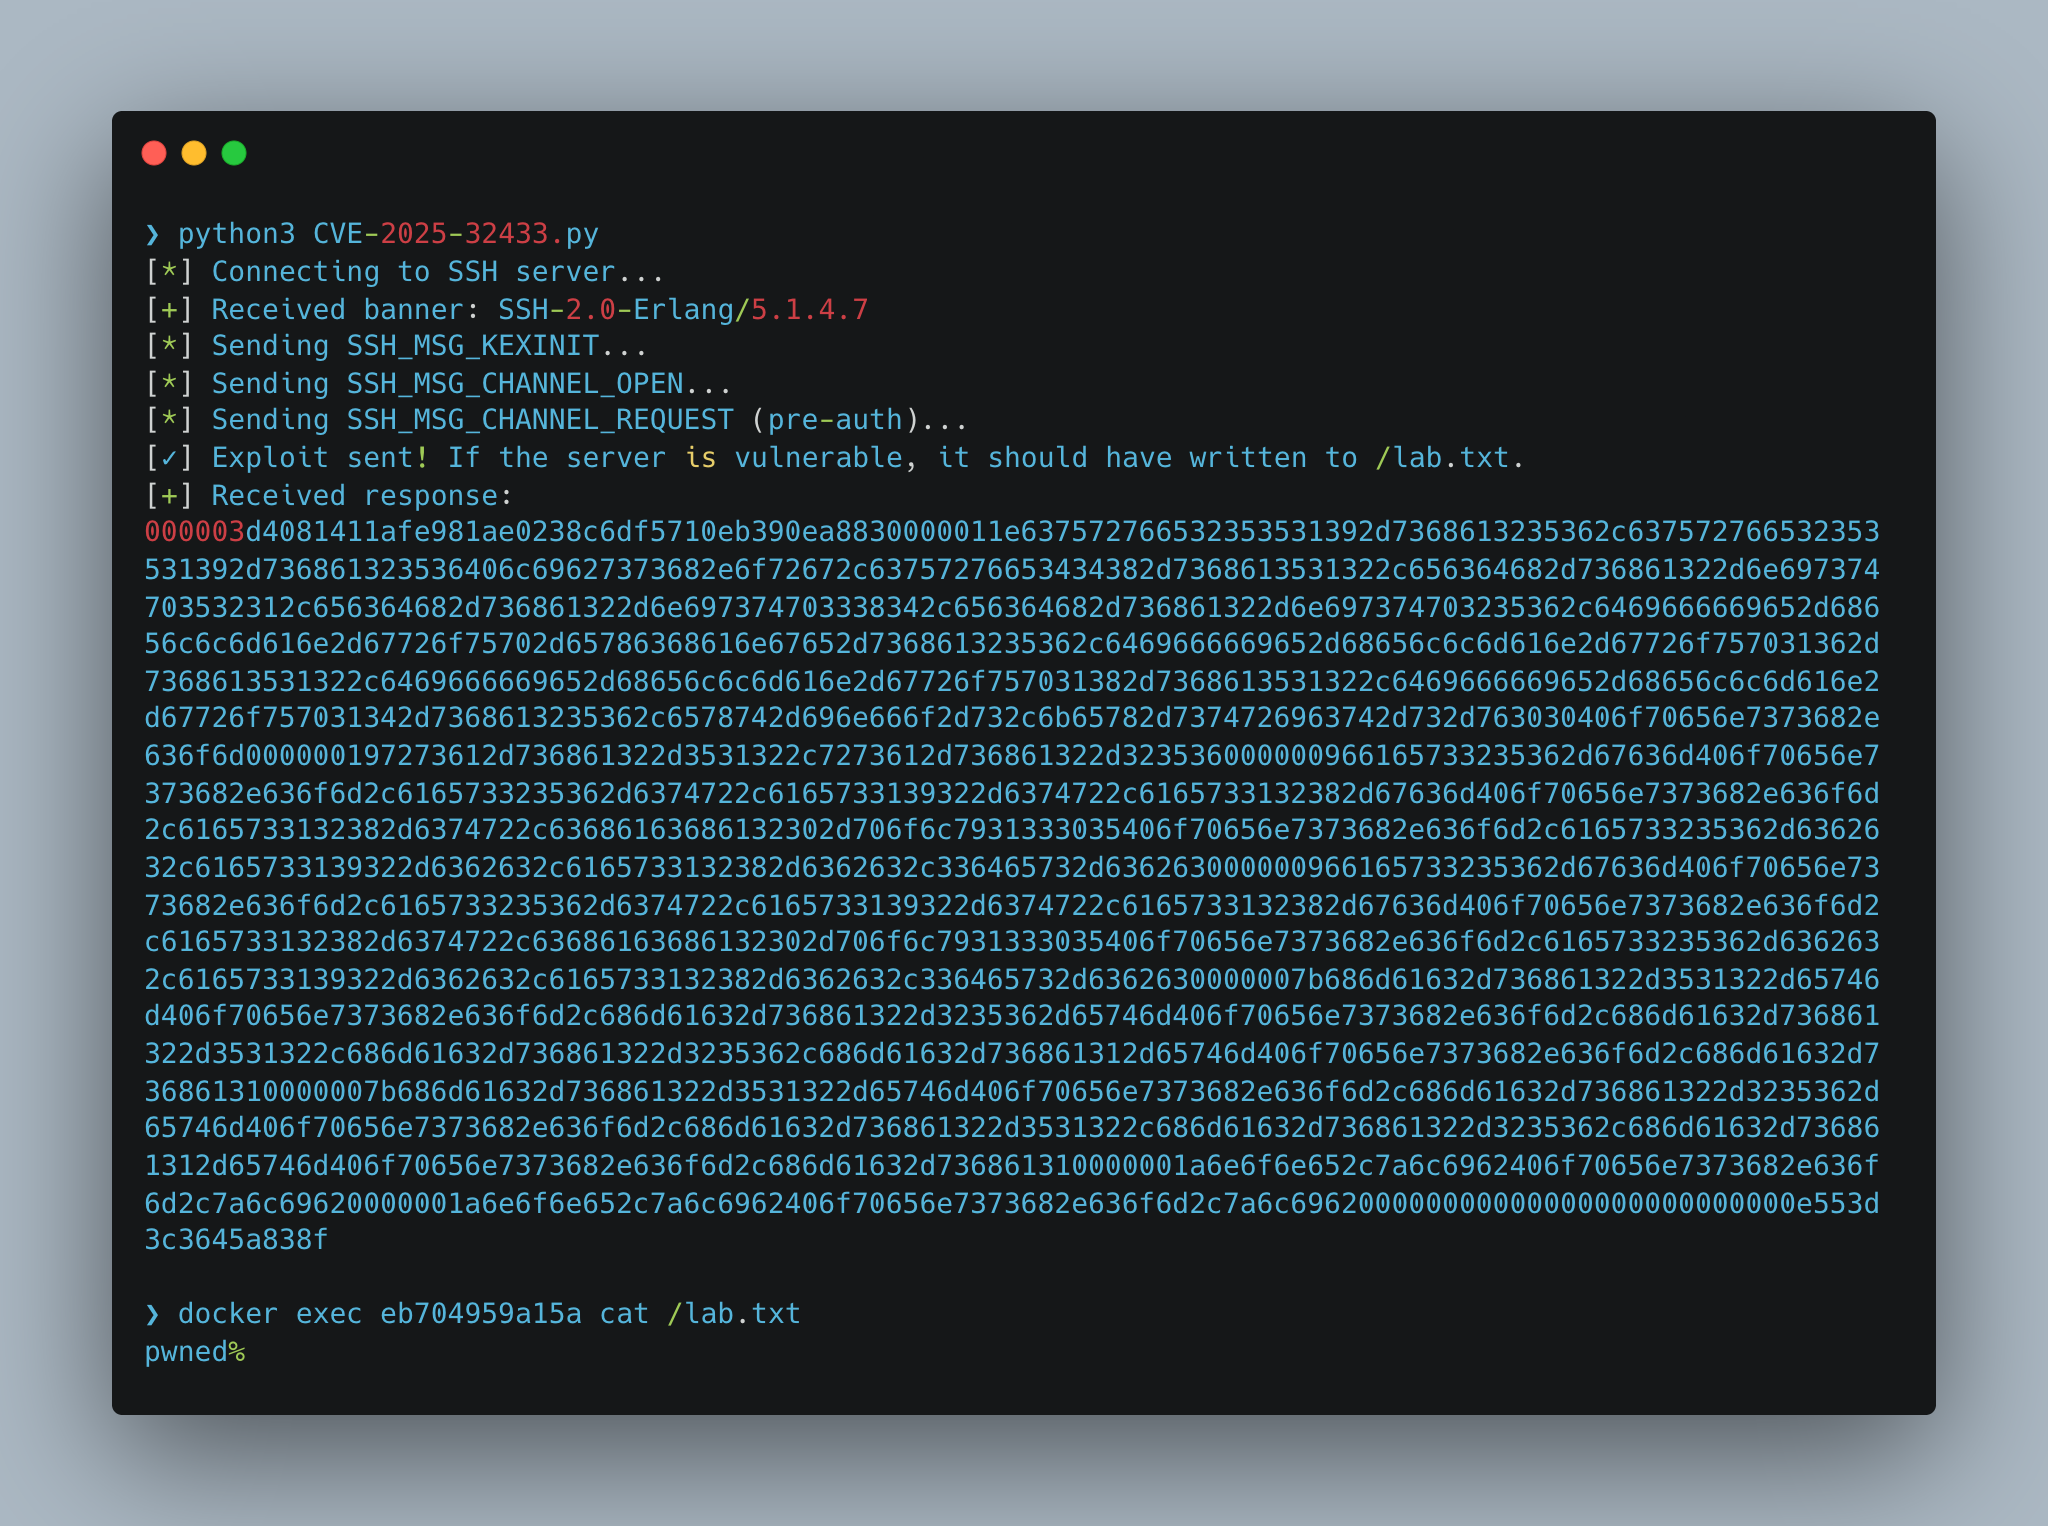 prodefense/cve-2025-32433
CVE-2025-32433 https://github.com/erlang/otp/security/advisories/GHSA-37cp-fgq5-7wc2
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
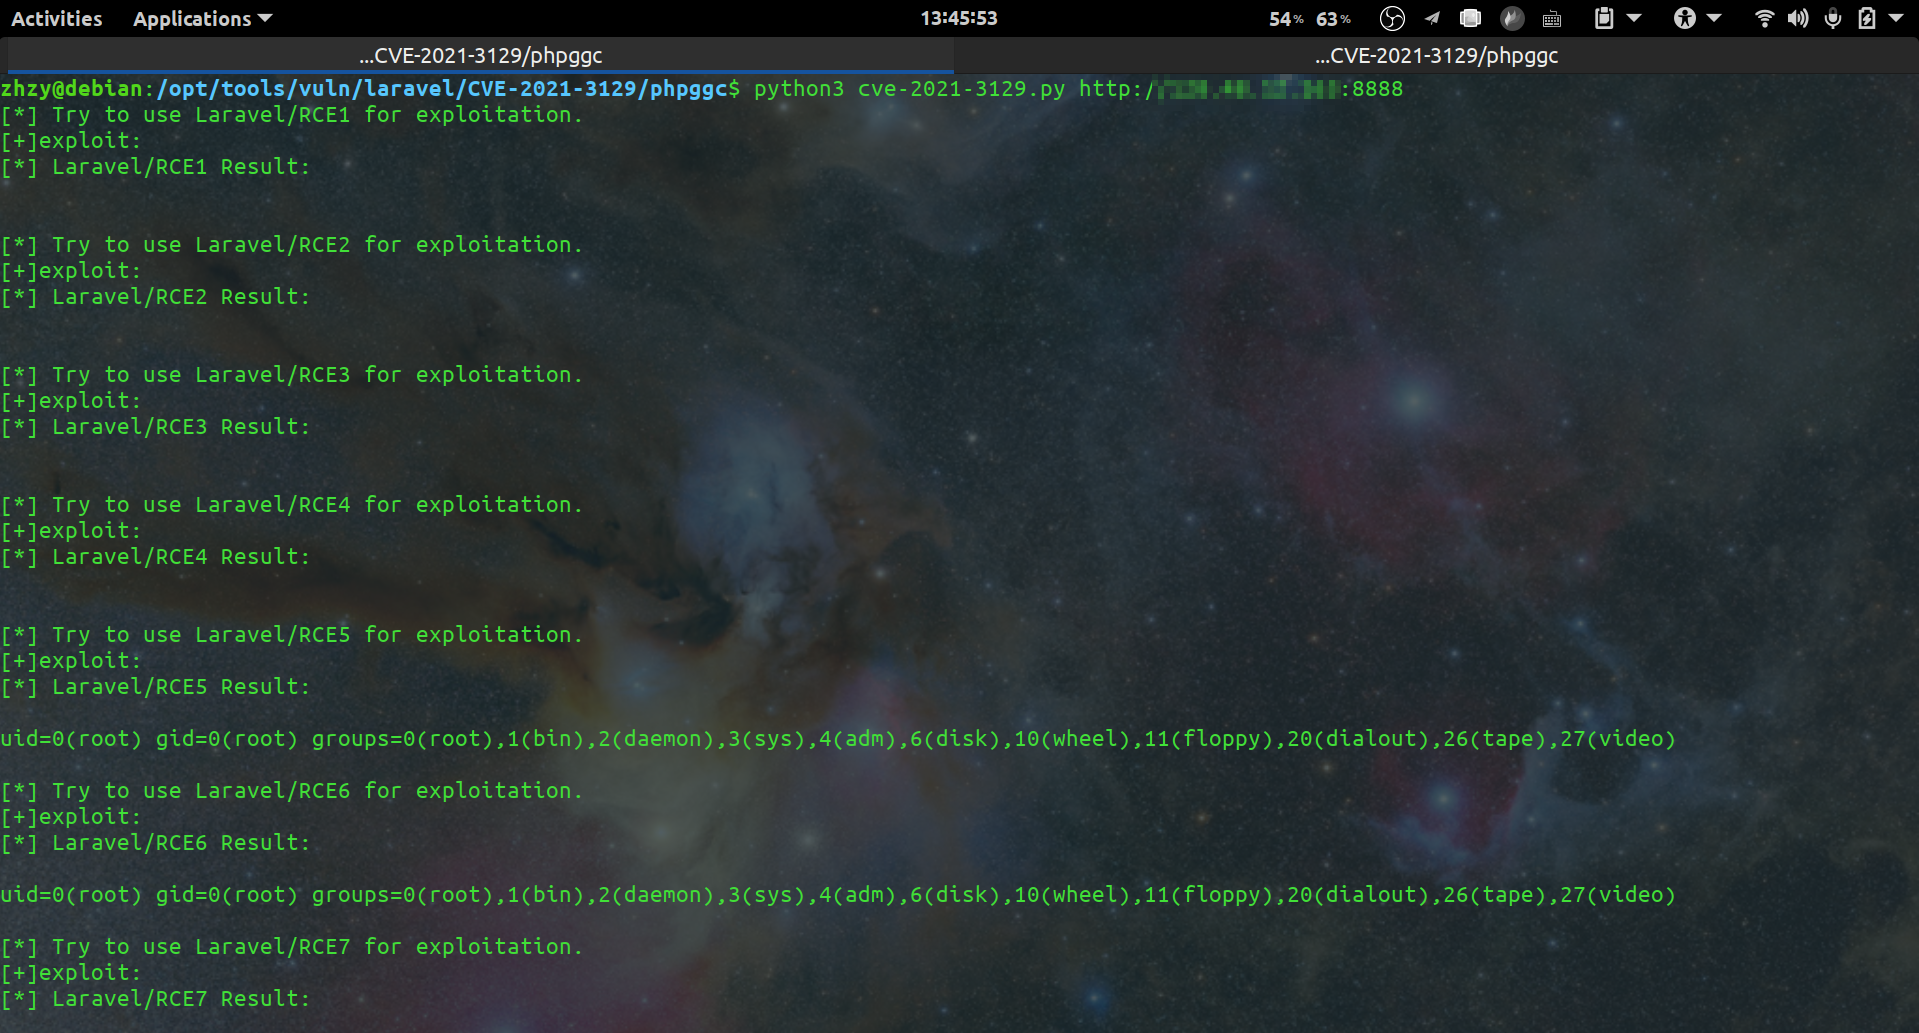 zhzyker/cve-2021-3129
Laravel <= v8.4.2 debug mode: Remote code execution (CVE-2021-3129)
 owasp/serverless-top-10-project
OWASP Serverless Top 10