
 #1
Tools for testing, exploiting, and securing web applications and APIs.
Kitploit recommended

 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
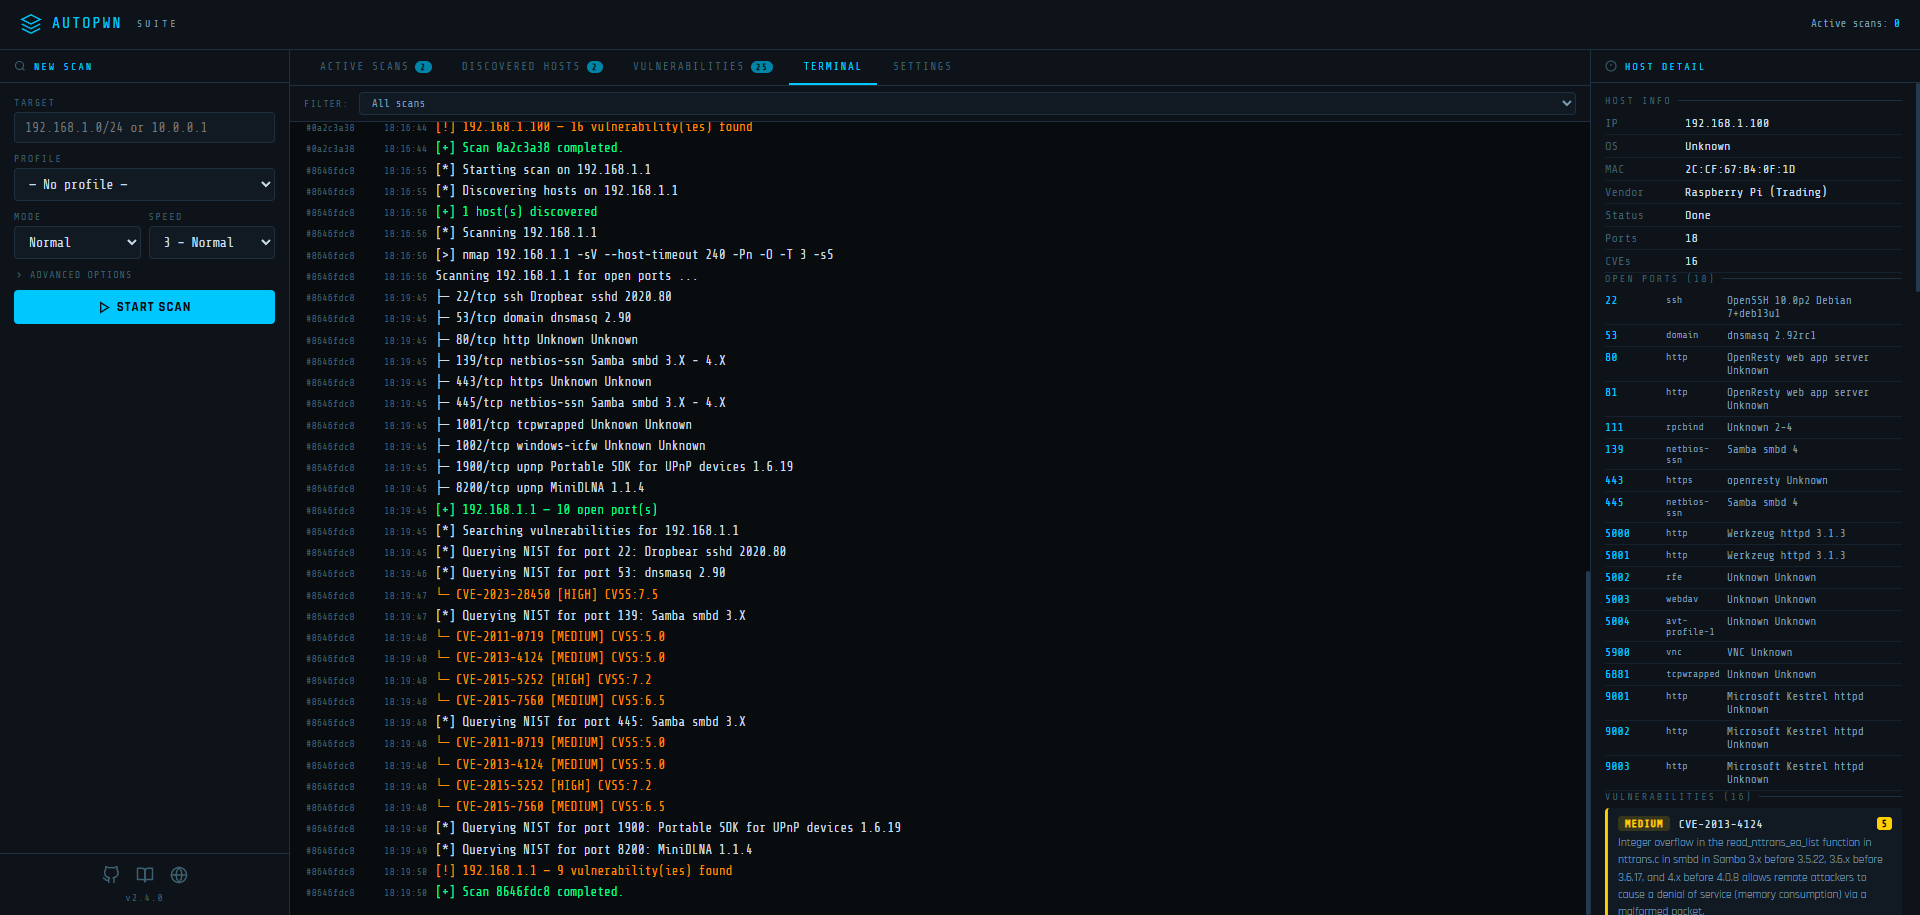 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 stevoisiak/stevos-ai-blocklist
A filter list that hides website features which use Generative AI & content labeled as AI Generated.
 nilsteampassnet/teampass
Collaborative Passwords Manager
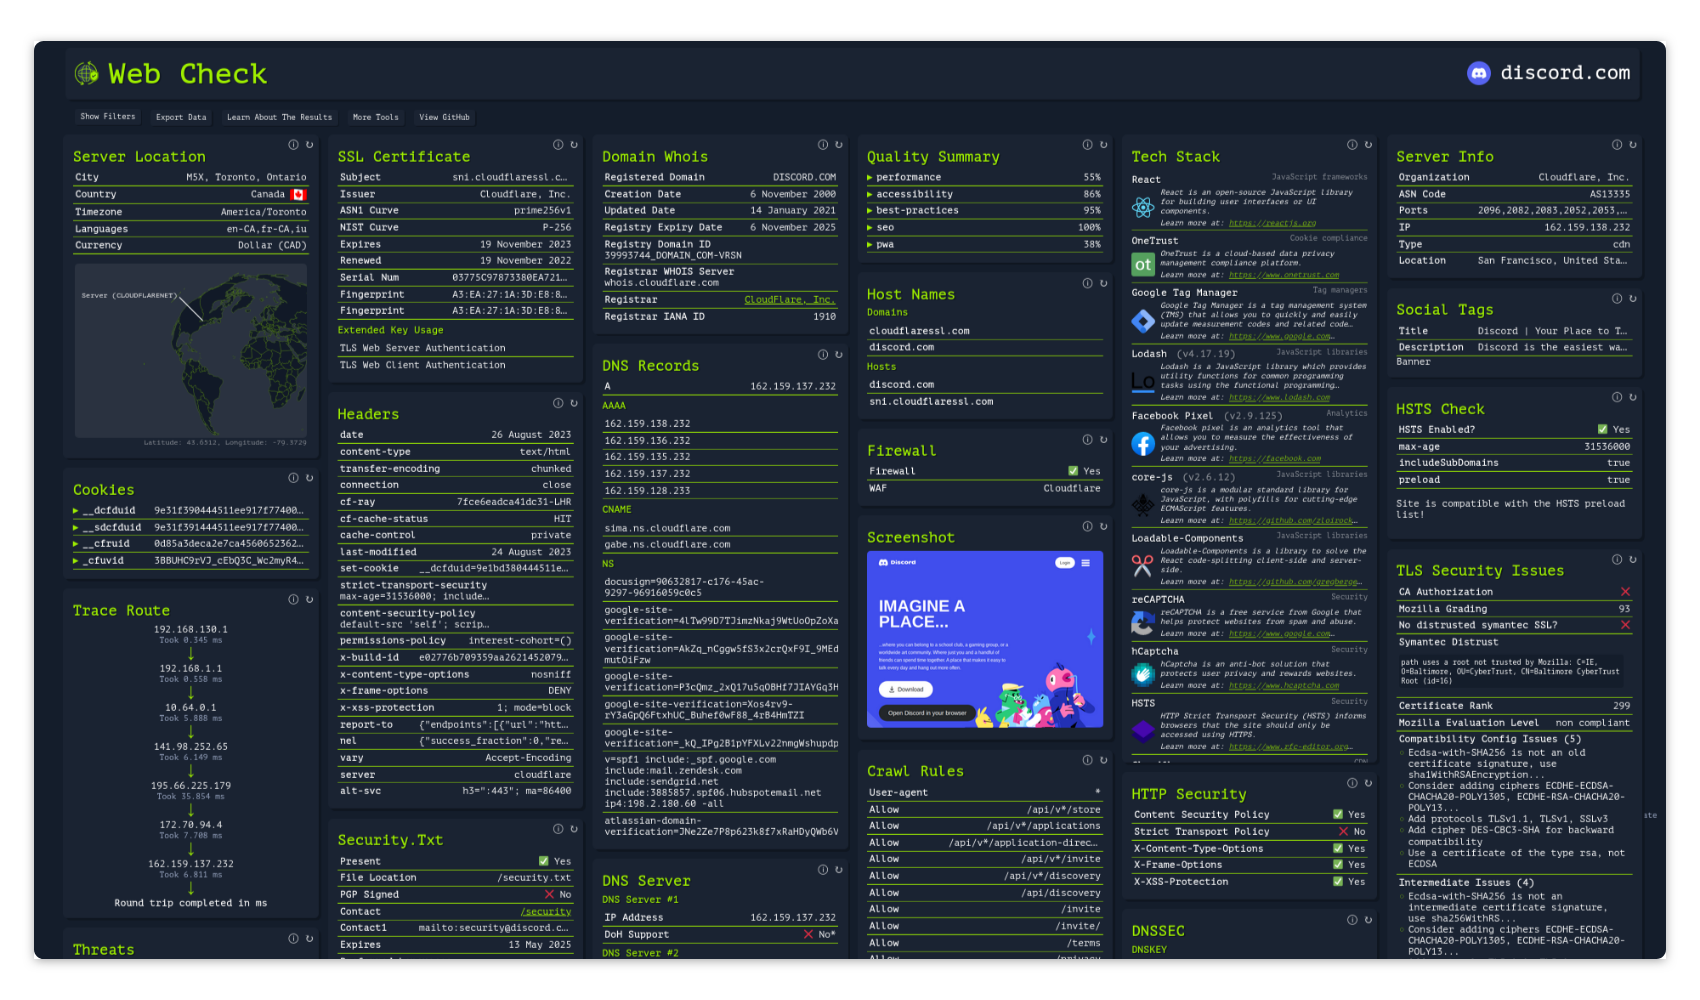 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
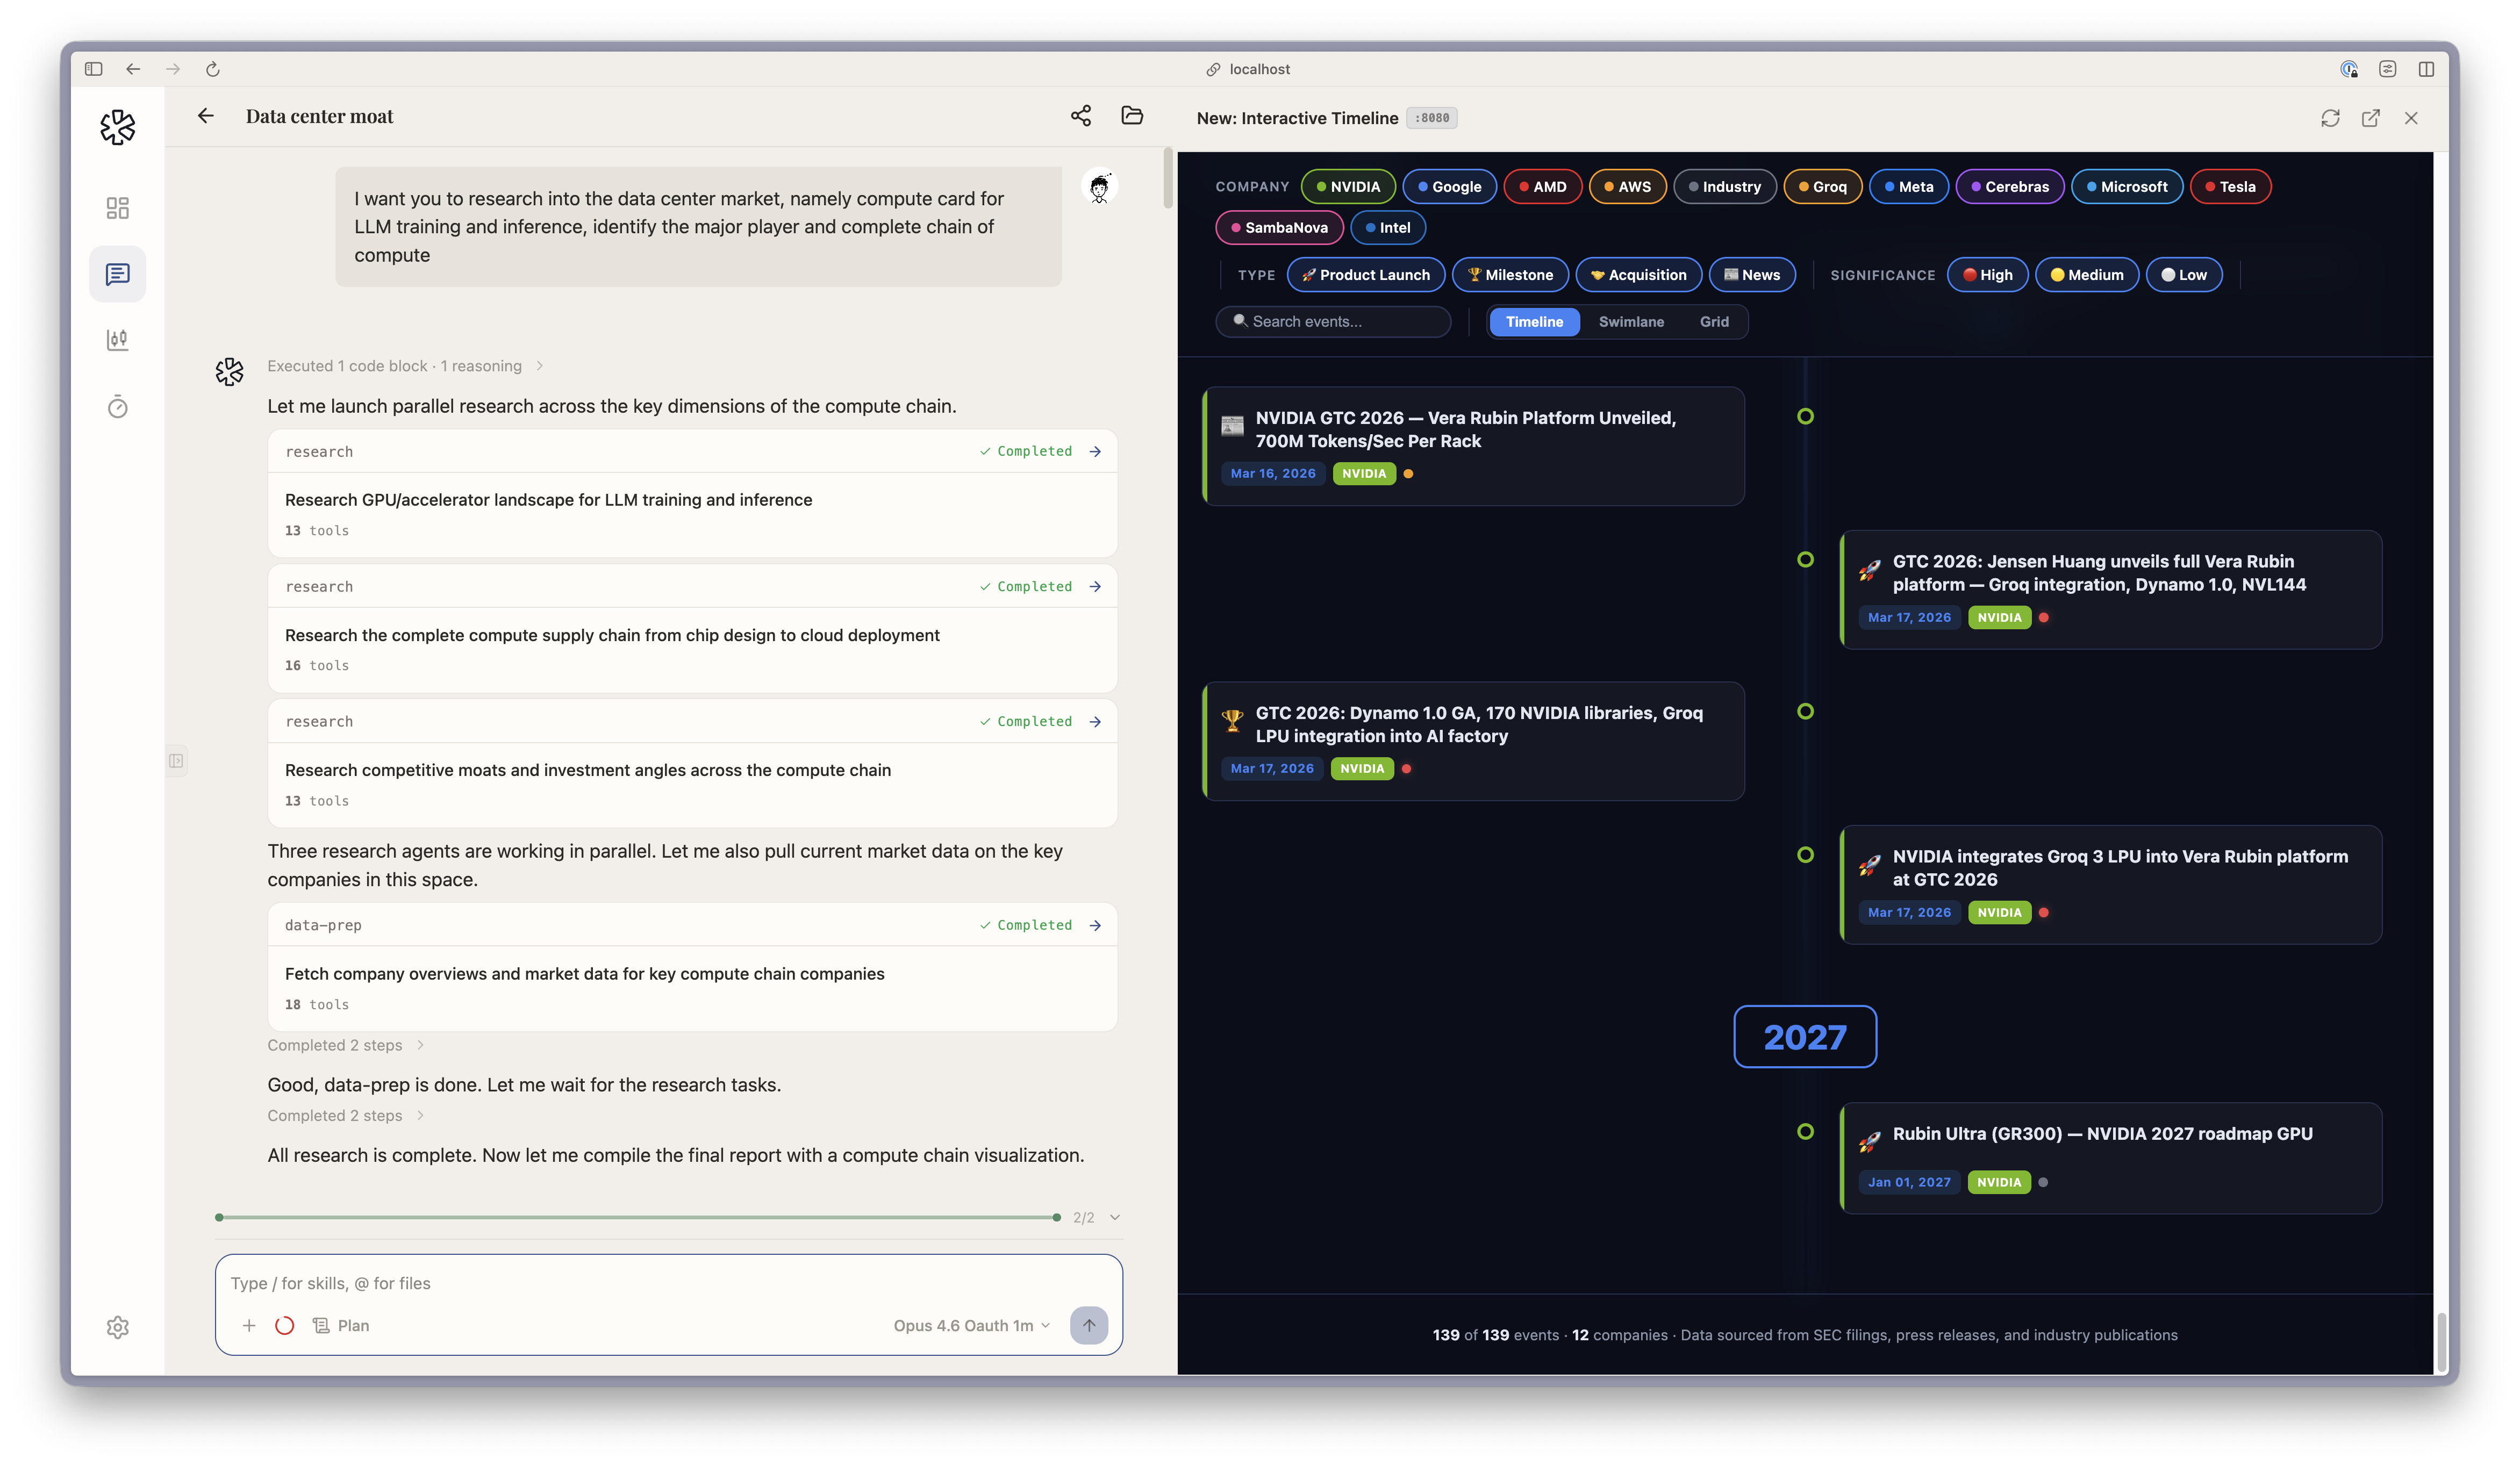 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 opnsense/core
OPNsense GUI, API and systems backend
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 garrytan/gstack
Use Garry Tan's exact Claude Code setup: 23 opinionated tools that serve as CEO, Designer, Eng Manager, Release Manager, Doc Engineer, and QA
 freelabz/secator
secator - the pentester's swiss knife
 yukibtc/redknife
A Swiss Army knife for offensive security.
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.








