
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP behavior, and rates confidence.
Exhaust every possible means, strip the CDN down to its underwear, and find the real IP.
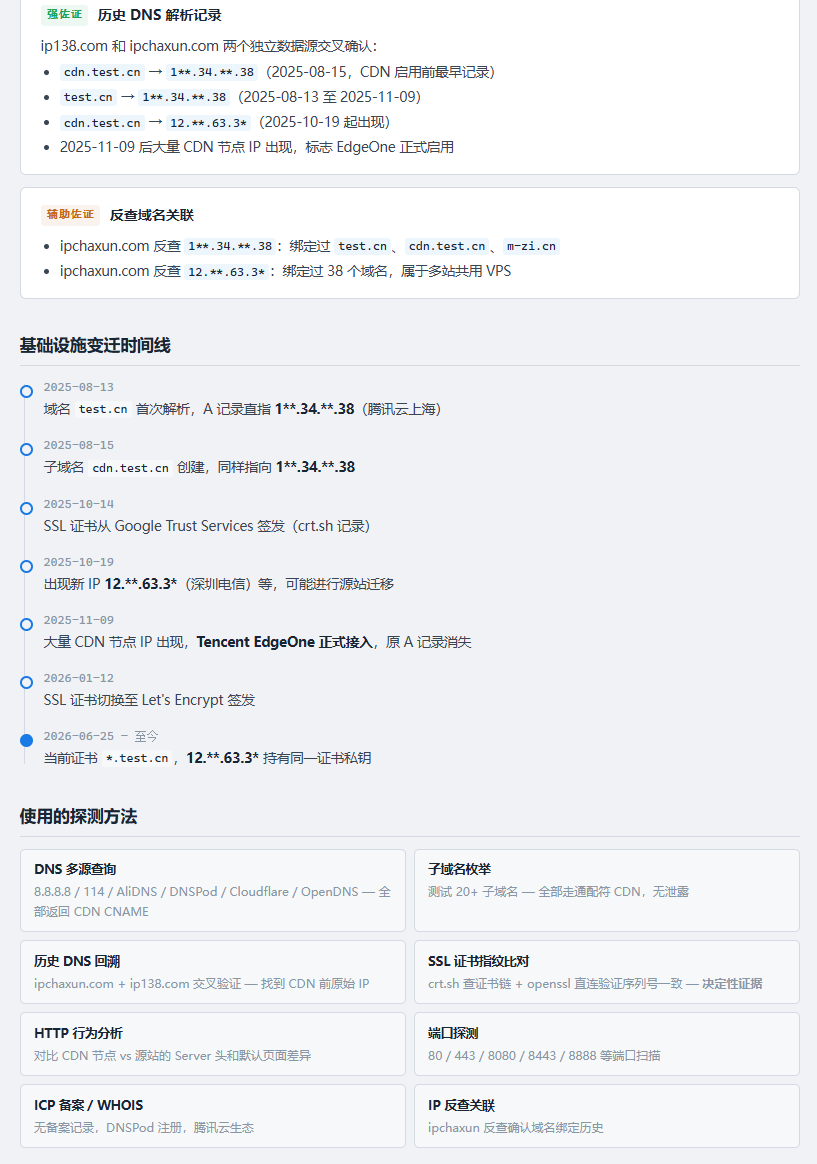
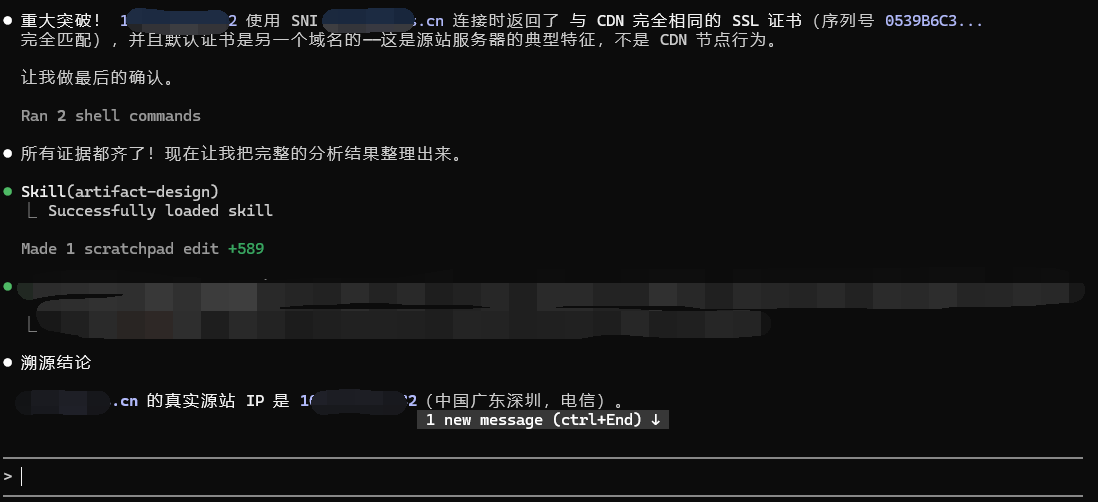
An automated CDN origin server tracing skill built for Claude Code. Input a target domain, and it automatically executes 40+ OSINT methods in priority order, builds an evidence chain, and outputs a final determination.
╔══════════════════════════════════════════════════╗
║  Real IP:  103.***.**.32                        ║
║  Confidence:  Confirmed (95%+)                            ║
║  Location:  Shenzhen, Guangdong, China · Telecom                     ║
║  Evidence chain:  [S] Exact SSL certificate match                    ║
║          [A] Historical DNS record confirmation                     ║
║          [A] HTTP behavior difference verification                     ║
╚══════════════════════════════════════════════════╝
No matter which CDN the target is hiding behind—Cloudflare, Tencent EdgeOne, Alibaba Cloud, AWS CloudFront, Akamai, Fastly, Azure, Imperva, Sucuri, Huawei Cloud, Wangsu, Baidu Cloud, or even any unknown CDN not on the list—FUCK-CDN will try methods in order from lowest to highest cost:
| Priority | Method | Token Cost |
|---|---|---|
| P0 | SPF/MX/TXT record leakage, IPv6 direct connection, historical DNS backtracking | Extremely low |
| P1 | Exact SSL certificate serial number comparison, subdomain enumeration, HTTP Server header behavior difference analysis | Medium |
| P2 | Shodan / FOFA / Censys / ZoomEye / Quake / Hunter cyberspace search, Favicon Hash, full port scan | Relatively high |
| P3 | Email header tracing, JS source code audit, same-organization domain correlation, GA/AdSense ID reverse lookup, CDN-specific bypass | High |
| P4 | Deep mining: Web Archive archaeology, source code configuration audit, passive intelligence, cloud provider metadata, WAF bypass, time-dimension attacks, social engineering assistance, network topology inference | Extremely high |
If P0 hits, stop immediately—don't waste a single Token. Only escalate to the next level if it doesn't hit. P0-P3 + all CDN-specific/generic bypasses failed? P4 will exhaust every unconventional means and fight to the end. After finding candidate IPs, it automatically enters the verification phase—SSL certificate comparison + HTTP behavior comparison + IP reverse lookup—triple cross-verification, giving a confidence rating.
git clone <repo_url> FUCK-CDN
cd FUCK-CDN
claude
After cloning, start Claude Code directly in the project directory, and the skill loads automatically.
If you already have your own project, just copy the skill file into it:
# Execute in your project root directory
mkdir -p .claude/skills
curl -o .claude/skills/fuck-cdn.md \
  <repo_raw_url>/.claude/skills/fuck-cdn.md
Or do it manually:
.claude/skills/fuck-cdn.md.claude/skills/ directory (create it if it doesn't exist)# Place in the user-level skills directory, shared by all projects
mkdir -p ~/.claude/skills
cp .claude/skills/fuck-cdn.md ~/.claude/skills/
After starting Claude Code, type / to view the list of available skills, and you should see fuck-cdn.
Call it directly in Claude Code:
/fuck-cdn example.com
Or use natural language:
Help me find the real IP of example.com
There are two ways to configure API Keys:
Open .claude/skills/fuck-cdn.md, find the API Key configuration section at the top, and fill in your Keys:
SHODAN_API_KEY     = "your Key"
FOFA_EMAIL         = "your email"
FOFA_API_KEY       = "your Key"
CENSYS_API_ID      = "your ID"
CENSYS_API_SECRET  = "your Secret"
SECURITYTRAILS_KEY = "your Key"
ZOOMEYE_API_KEY    = "your Key"
QUAKE_API_KEY      = "your Key"
HUNTER_API_KEY     = "your Key"
VIRUSTOTAL_KEY     = "your Key"
Once filled in, it will be used automatically on every call, with no need to re-enter.
Security tip: If your project is a public repository, do not commit the skill file containing Keys. It is recommended to add
.claude/skills/fuck-cdn.mdto.gitignore, or only fill in Keys in a local / global installation (~/.claude/skills/).
Tell Claude your Keys directly in the conversation; they will only be used in the current session memory and will not be written to any file:
My Shodan key is xxxx, FOFA email is xxx key is xxx
Help me find the real IP of example.com
| Platform | Key format | Free quota | Purpose |
|---|---|---|---|
| Shodan | SHODAN_API_KEY | Available upon registration | Search for IPs with the same certificate/favicon/title characteristics |
| FOFA | FOFA_EMAIL + FOFA_API_KEY | Available upon registration | icon_hash, certificate, body keyword search |
| Censys | CENSYS_API_ID + CENSYS_API_SECRET | Available upon registration | Exact certificate fingerprint SHA256 search |
| SecurityTrails | SECURITYTRAILS_KEY | Free 50 times/month | Historical DNS records, subdomain enumeration |
| ZoomEye | ZOOMEYE_API_KEY | Available upon registration | Certificate, title search |
| 360 Quake | QUAKE_API_KEY | Available upon registration | Certificate search |
| Hunter | HUNTER_API_KEY | Available upon registration | Certificate search |
| VirusTotal | VIRUSTOTAL_KEY | Free 500 times/day | Resolution history, subdomain enumeration |
It works even without any Key. All methods in the P0 and P1 phases (historical DNS, certificate comparison, subdomain enumeration, HTTP behavior analysis) do not require a Key, and the hit rate is already very high. The value of Keys lies in the P2 phase—cyberspace search engines can greatly improve the hit rate against heavily protected targets.
Not just identification—each CDN has dedicated bypass methods:
