
 #1
Security papers, research projects, technical references, and reproducible material for defensive or authorized analysis.
Kitploit recommended
 punksitr-sys/cve-2026-16723
Research & reproduction for fastjson deserialization vulnerability (1.2.68–1.2.83).
 jamir0quai/cve-2026-16444
Technical write-up of CVE-2026-16444, a path traversal in TeamViewer Classical File Transfer that lets a controlled endpoint write arbitrary files on…
 hidra0x/hidra
Research jailbreak project for A12 iOS 18.7.2 devices, chaining the AppleJPEGDriver UAF (CVE-2026-20687) toward a kernel read/write primitive. No…
 ashrafzaryouh/cve-2026-20841
Research and analysis repository for CVE-2026-20841, a Windows Notepad Markdown remote code execution flaw, with PoC scripts, attack flow details,…
 syrex1013/cve-2026-2031226
Proof-of-concept exploits for a PHP Fiber callable use-after-free (CVE-2026-2031226) enabling heap reclaim, type confusion, info leak, and…
 ashrafzaryouh/cve-2026-20079
Advisory and research write-up on CVE-2026-20079, a critical authentication bypass in Cisco Secure Firewall Management Center enabling…
 tianlansedexiaoniu/cve-2026-19971_guest
LB-LINK WR1210M (CVE-2026-19971) 未授权配置泄露漏洞与访客网络扩展攻击链分析
 crypt0p3g/pass-the-device
Recon tools and Sigma/KQL detections for testing whether VPN/SASE device trust can be transplanted after endpoint compromise, with conference slides.
 c3viche/cve-2026-18649
GStreamer RTP Depayloader Memory Exhaustion Analysis
 mattifinder/rpmc_attacks
Research code and hardware for RPMC attacks: voltage glitching, SPI interposer firmware, and NV-state rollback to brute-force Windows Hello and…
 ashrafzaryouh/cve-2026-21589
Technical analysis of CVE-2026-21589, a pre-auth path traversal arbitrary file read in Atlassian Data Center products, with root cause, detection…
 unsignedchad/cve-2026-21155-sve-2026-3546
Technical writeup and PoC for CVE-2026-21155 (SVE-2026-3546): fail-open signature checks and an unbounded boot-logo JPEG decode in Samsung Exynos…
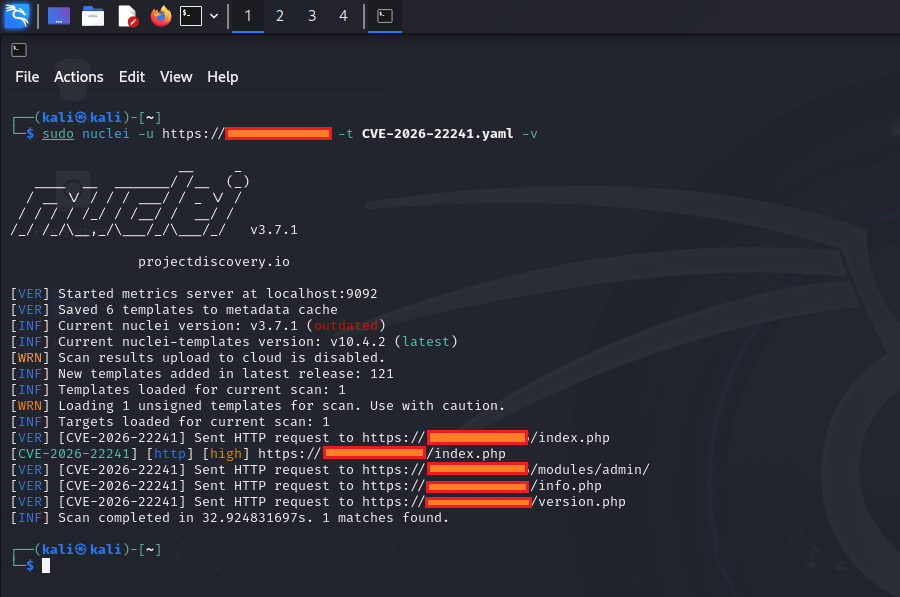 ashrafzaryouh/cve-2026-22241
Advisory and technical analysis of CVE-2026-22241, an unrestricted ZIP upload in Open eClass theme import (pre-4.2) enabling authenticated admin…
 psm-defense/psm
A black-box optimization approach for protecting Large Language Model (LLM) system prompts against adversarial extraction attacks.
 dtc7w3pq/visco-attack
Research pipeline implementing a visual-contextual jailbreak against multimodal LLMs: T2I prompt extraction, SD3.5 image rendering, multi-round spoof…
 rahulreddykarne/ark-wp-scanner
Scans WordPress plugins for missing-guard vulnerabilities using ripgrep signatures, Semgrep rules, attack-surface mapping, and an LLM review cascade…
 ashrafzaryouh/cve-2026-23111
Advisory write-up of CVE-2026-23111, a Linux kernel nf_tables use-after-free in catch-all map rollback, covering root cause, impact, detection and…
 techosystem/iomt_secalarmbench
A standardized benchmark for evaluating security alarm systems in Internet of Medical Things (IoMT) - attacks, detection, false-alarm resilience, and…








