
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-22241 β€” Advisory and technical analysis of CVE-2026-22241, an unrestricted ZIP upload in Open eClass theme import (pre-4.2) enabling authenticated admin remote code execution, with root cause and mitigation. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-22241
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPapers & ResearchLearning & Education
GitHubashrafzaryouh/cve-2026-22241

CVE-2026-22241

Advisory and technical analysis of CVE-2026-22241, an unrestricted ZIP upload in Open eClass theme import (pre-4.2) enabling authenticated admin remote code execution, with root cause and mitigation.

View Repository
17 months agoNot yet reviewed
Share

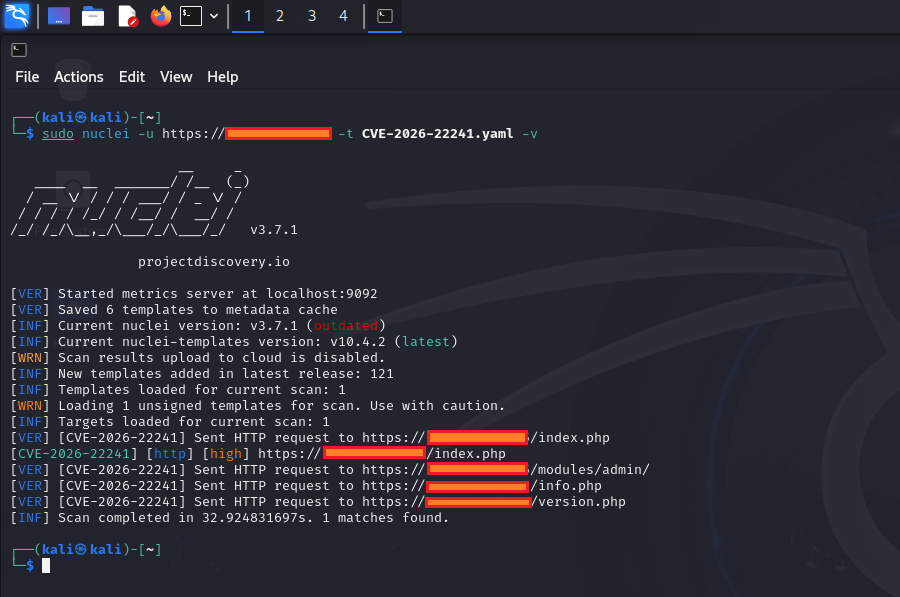
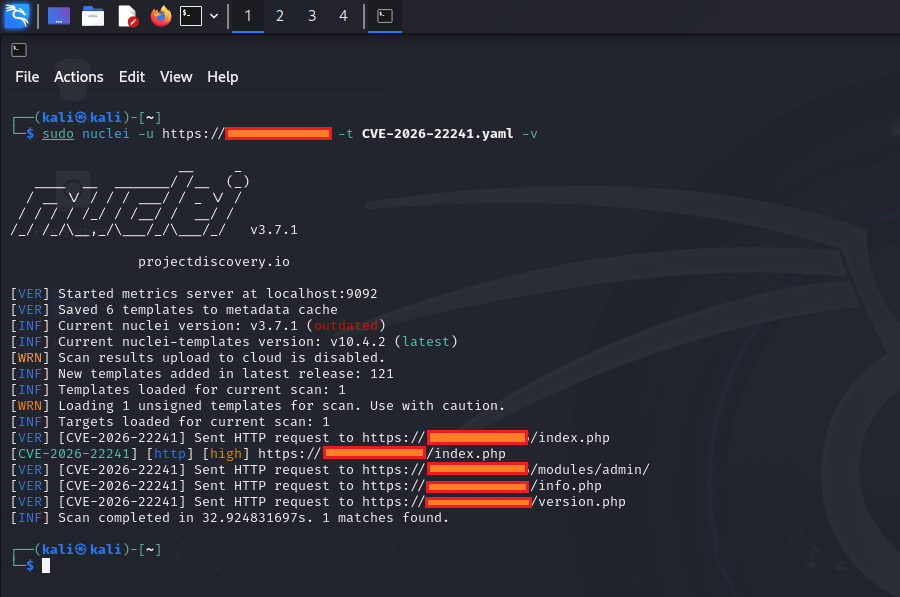
🚨 CVE-2026-22241 - Open eClass Theme Import Remote Code Execution

1768551798083
Severity Affected

πŸ“Œ Vulnerability Summary

Open eClass (also known as GUnet eClass), a widely used open-source Learning Management System (LMS), contains a critical Unrestricted File Upload vulnerability in its Theme Import feature.

An authenticated administrator can upload a malicious ZIP file, leading to Remote Code Execution (RCE) on the server.


⚠️ Affected Versions

VersionStatus
Open eClass < 4.2Vulnerable
Open eClass β‰₯ 4.2Patched

πŸ› οΈ Vulnerability Details

  • CVE ID: CVE-2026-22241
  • Severity: High (CVSS 7.3)
  • Type: Unrestricted File Upload (CWE-434)
  • Attack Vector: Theme Import functionality in the admin panel
  • Required Privilege: Administrator account
  • Impact: Remote Code Execution (RCE)
CVE-2026-22241

πŸ” Root Cause

The vulnerability exists due to insufficient validation and sanitization of uploaded ZIP archives during the theme import process. Malicious files (such as PHP webshells) can be written to the web-accessible directory.


πŸ›‘οΈ Mitigation & Fix

  • Upgrade immediately to Open eClass 4.2 or newer.
  • Disable the Theme Import feature if not required.
  • Restrict administrative access and implement strict file upload validation.
  • Monitor server logs for suspicious theme upload activity.

πŸ“š References

  • Official Security Advisory
  • NVD Entry
  • TwelveSec Analysis

⚠️ Legal Disclaimer

This repository is intended for educational and research purposes only.
The information provided is for helping security researchers and system administrators understand and patch the vulnerability.

Unauthorized exploitation against systems you do not own is illegal.


Made for Security Awareness & Research

⭐ If this helped you, please star the repository!

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

No popularity data yet.

Explore all tools

Browse our collection of tools

View all tools β†’