
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 jas502n/cve-2019-12384
Jackson Rce For CVE-2019-12384
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
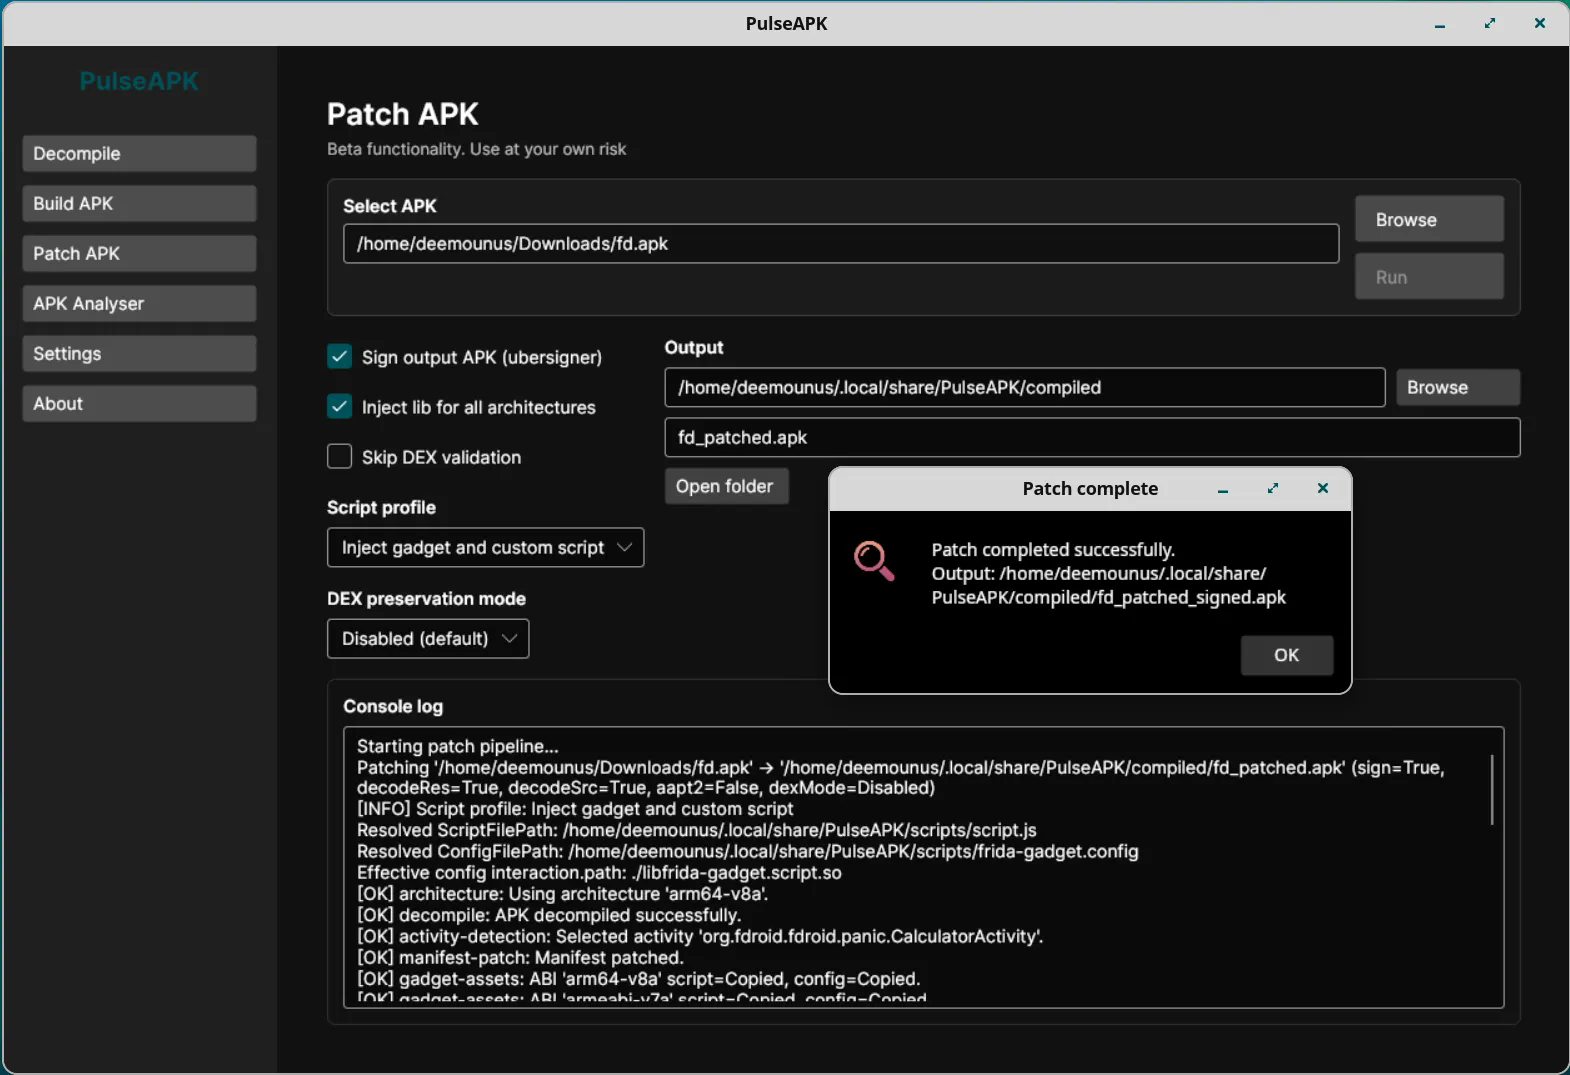 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 9aylas/shortcut-payload-generator
AutoIt HackTool, Shortcuts .lnk Payloads Generator As LNK-KISSER.
 rbmm/ntdetours
Detours implementation (x64/x86) which used only ntdll import
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
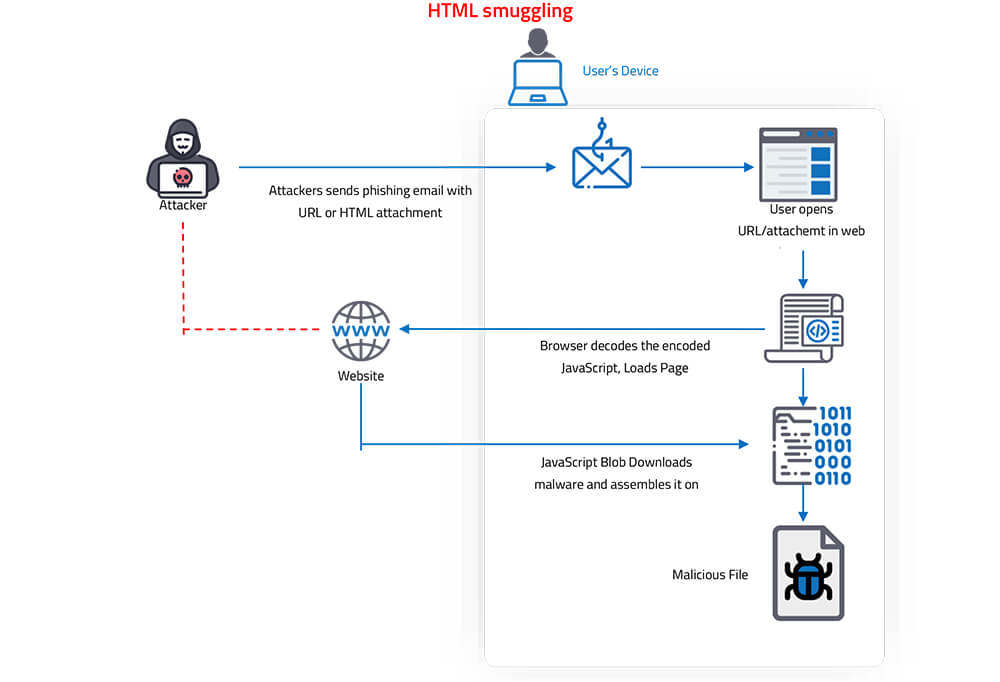 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 lt-asset/resym
For our CCS24 paper 🏆 "ReSym: Harnessing LLMs to Recover Variable and Data Structure Symbols from Stripped Binaries" by Danning Xie, Zhuo Zhang, Nan…
 live-ctf/livectf-defcon30
Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
 mindcrypt/covertchannels-steganography
A list of covert channels and steganography/steganalysis resources (books, papers & tools)
 nccgroup/frisbeelite
A GUI-based USB device fuzzer
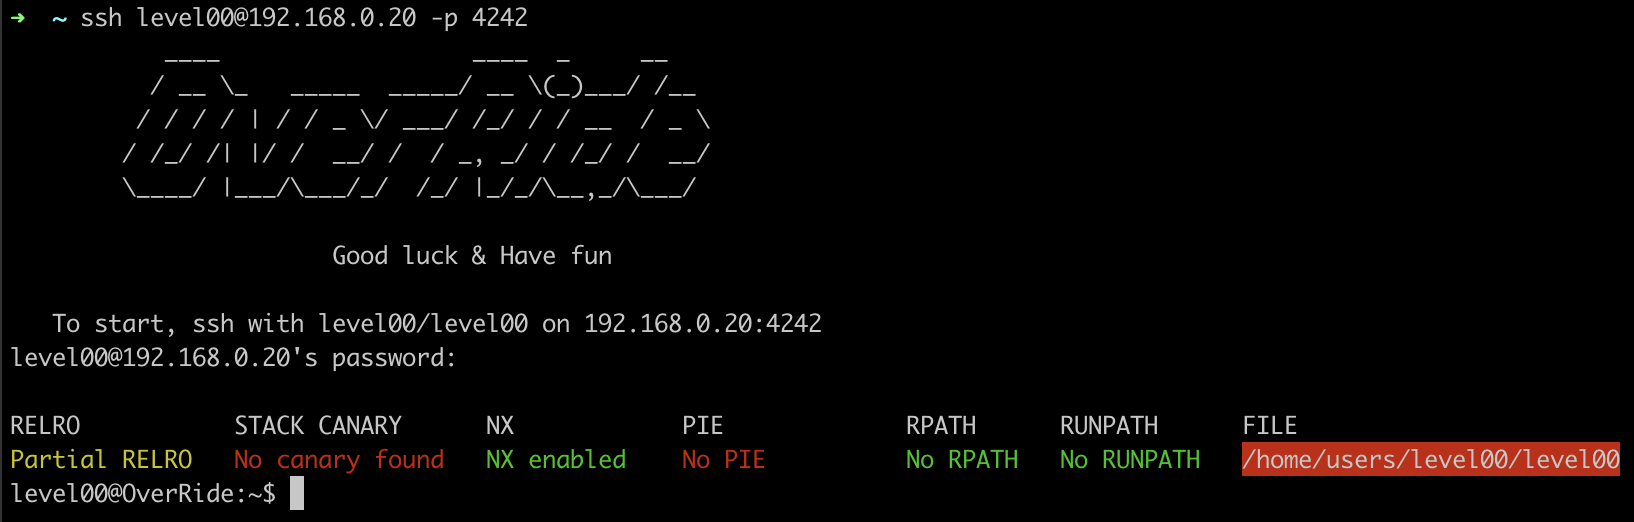 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
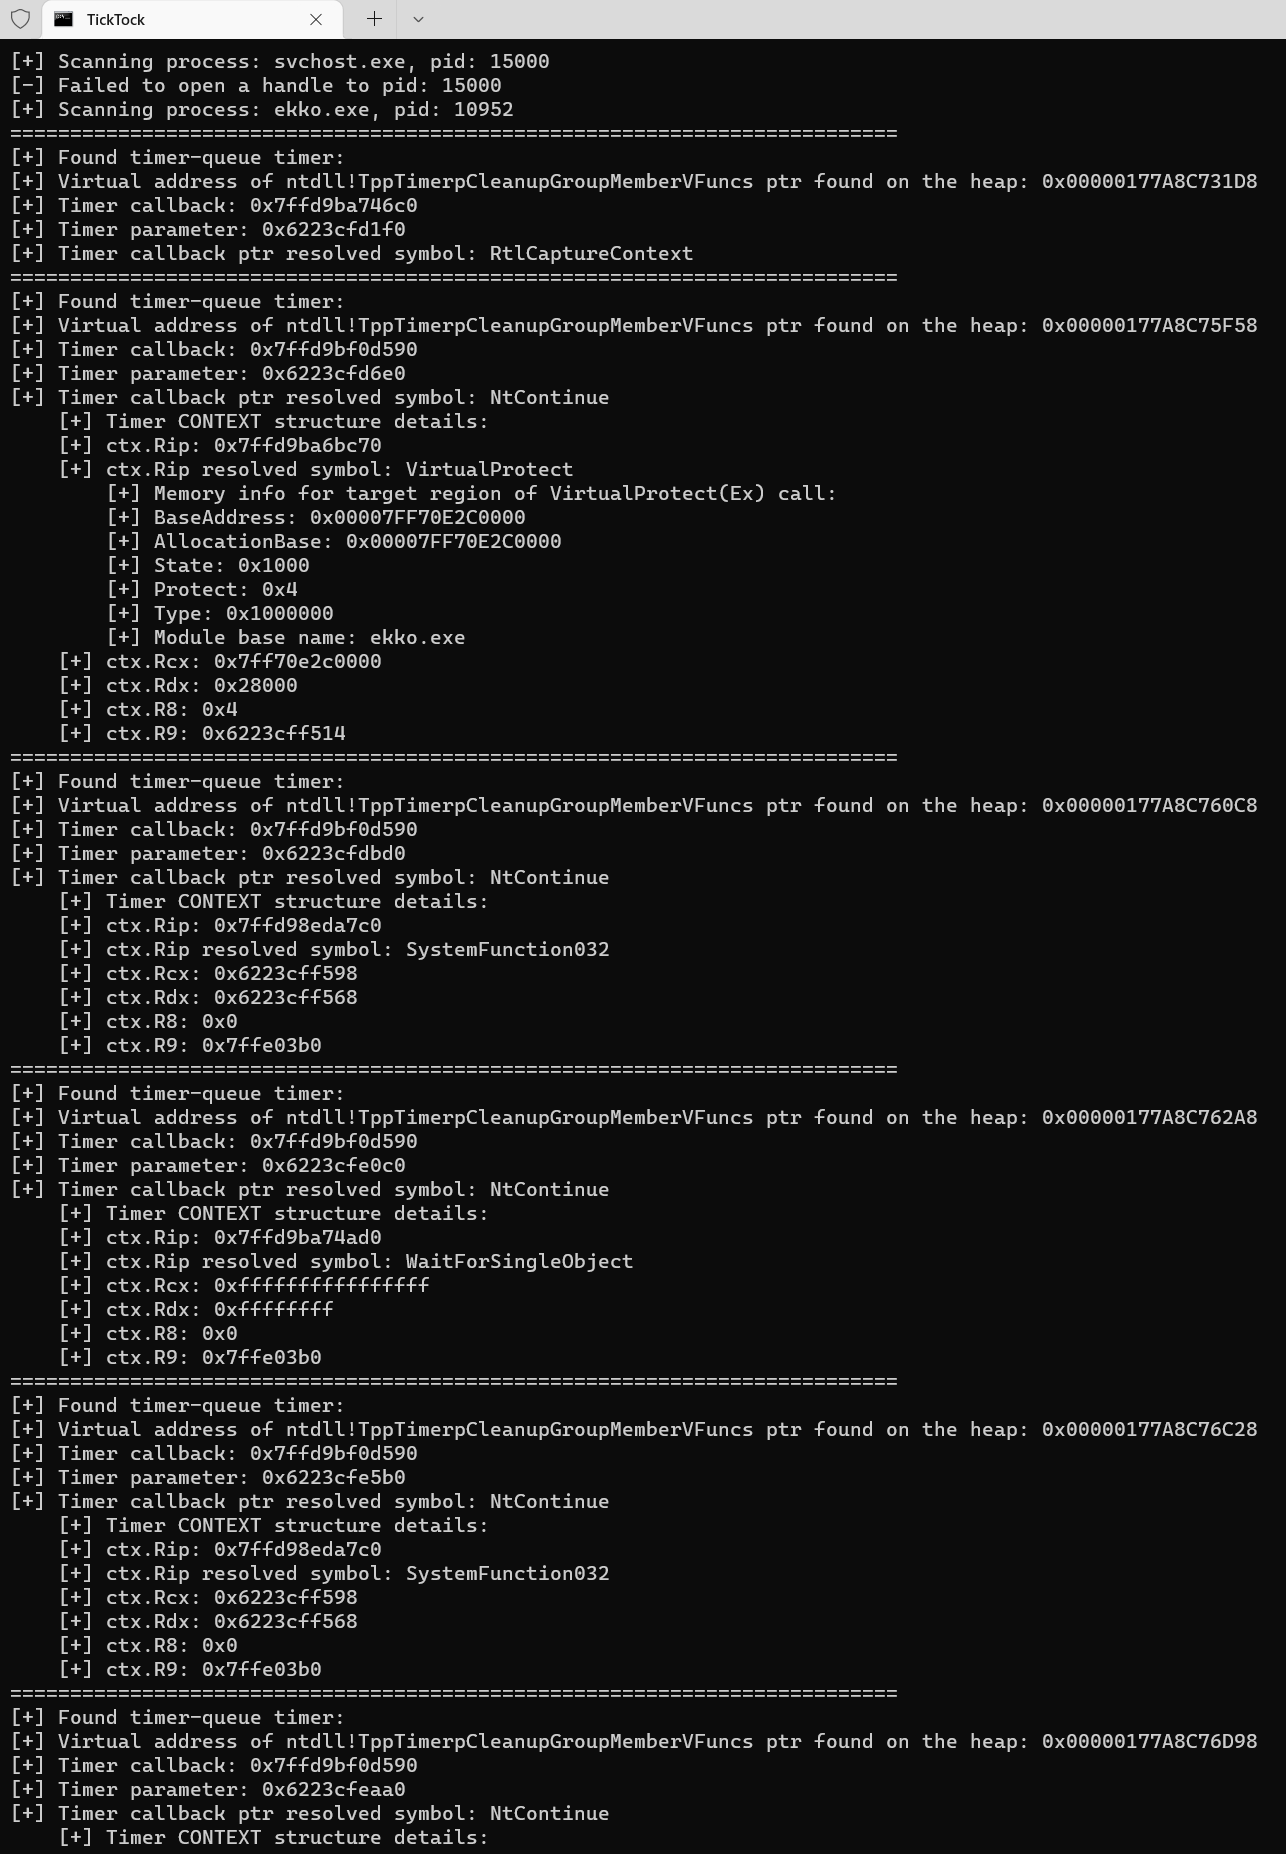 withsecurelabs/ticktock
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…
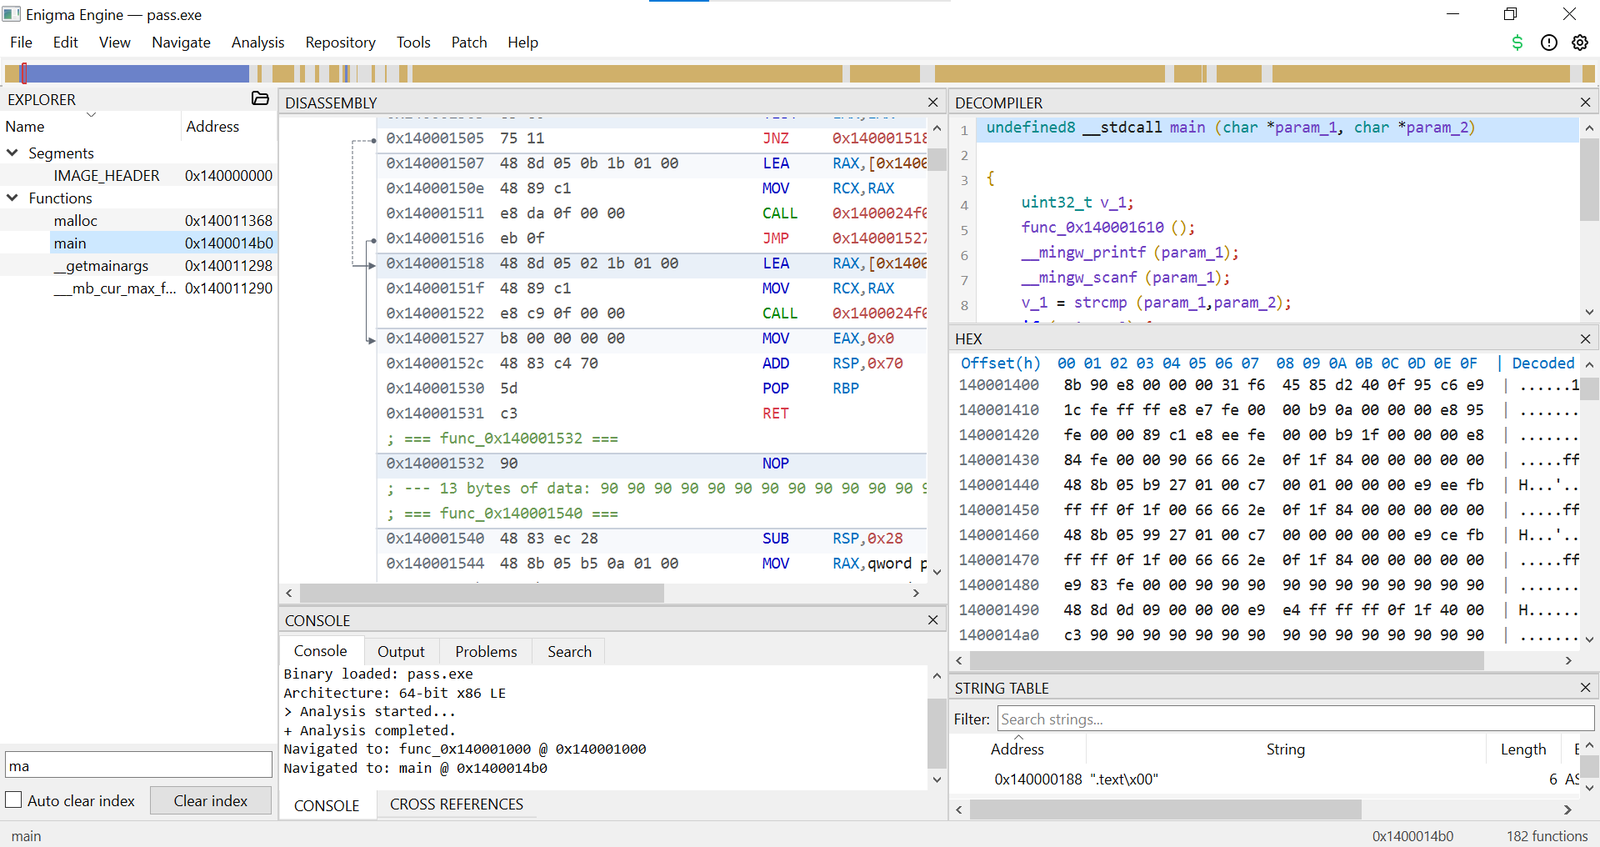 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.








