#1

 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
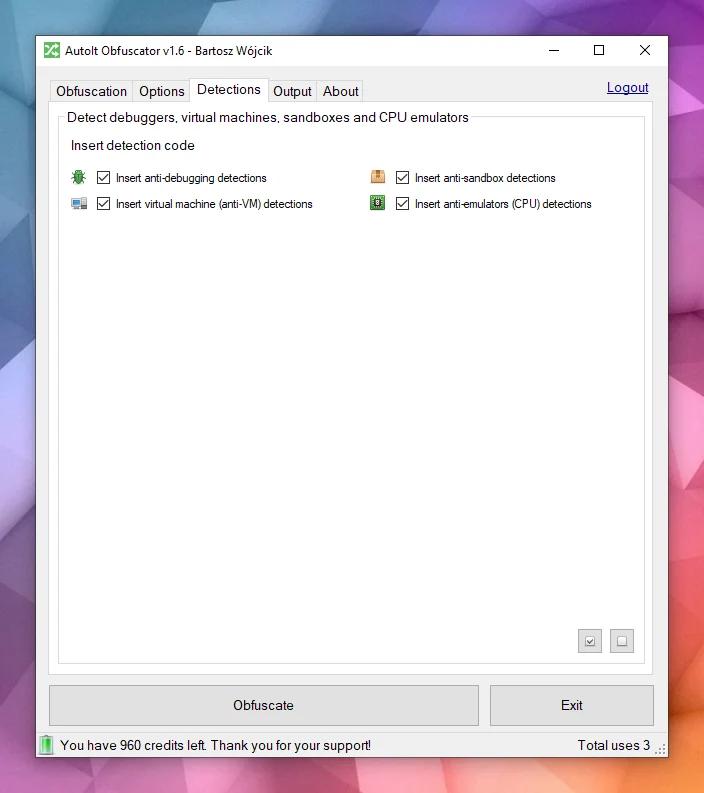 pelock/autoit-obfuscator
Obfuscates AutoIt scripts to protect source code from analysis, reverse engineering, and decompilation using advanced obfuscation and polymorphic…
 yuting-huang0/spring4shell-ctf
Spring4Shell (CVE-2022-22965) 漏洞環境搭建與 CTF 題目
 zodiacon/alltools
All reasonably stable tools
 probnotanexploiter/cve-2024-26170-extended
researching for CVE-2024-26170 or cimfs.sys to find overflows or bugs that is considered a zero-day
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 sidenai/hyperion-disassembler
Native multi-arch disassembler & decompiler - PE/ELF/Mach-O, x86/x64/ARM64, Lua scripting, RTTI recovery
 sirredbeard/cve-2025-60876
Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 getagentseal/agentseal
Security toolkit for AI agents. Scan your machine for dangerous skills and MCP configs, monitor for supply chain attacks, test prompt injection…
 alejandro609x/jefazo-cve-2025-55182-checker
Escáner pasivo de seguridad para CVE-2025-55182 que identifica indicadores públicos asociados a Next.js y React Server Components. Realiza…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 g0thamrabb1t/cve-2026-50656-rogueplanet-validation
Validation report for the RoguePlanet Microsoft Defender PoC in a controlled Windows 11 lab environment, including build notes, Defender detection…
 welfordian/mitm-proxy
Go-based MITM HTTP/HTTPS proxy with HTTP/2 and HTTP/1.1 interception, local CA/per-host cert generation, CONNECT/WebSocket tunneling, disk caching,…