#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 google/kafel
A language and library for specifying syscall filtering policies.
 blackorbird/apt_report
Interesting APT Report Collection And Some Special IOCs
 z3prover/z3
High-performance SMT solver for automated theorem proving, constraint solving, and program verification. Supports multiple theories and language…
 santhreal/keyhog
Open-source secret scanner in Rust
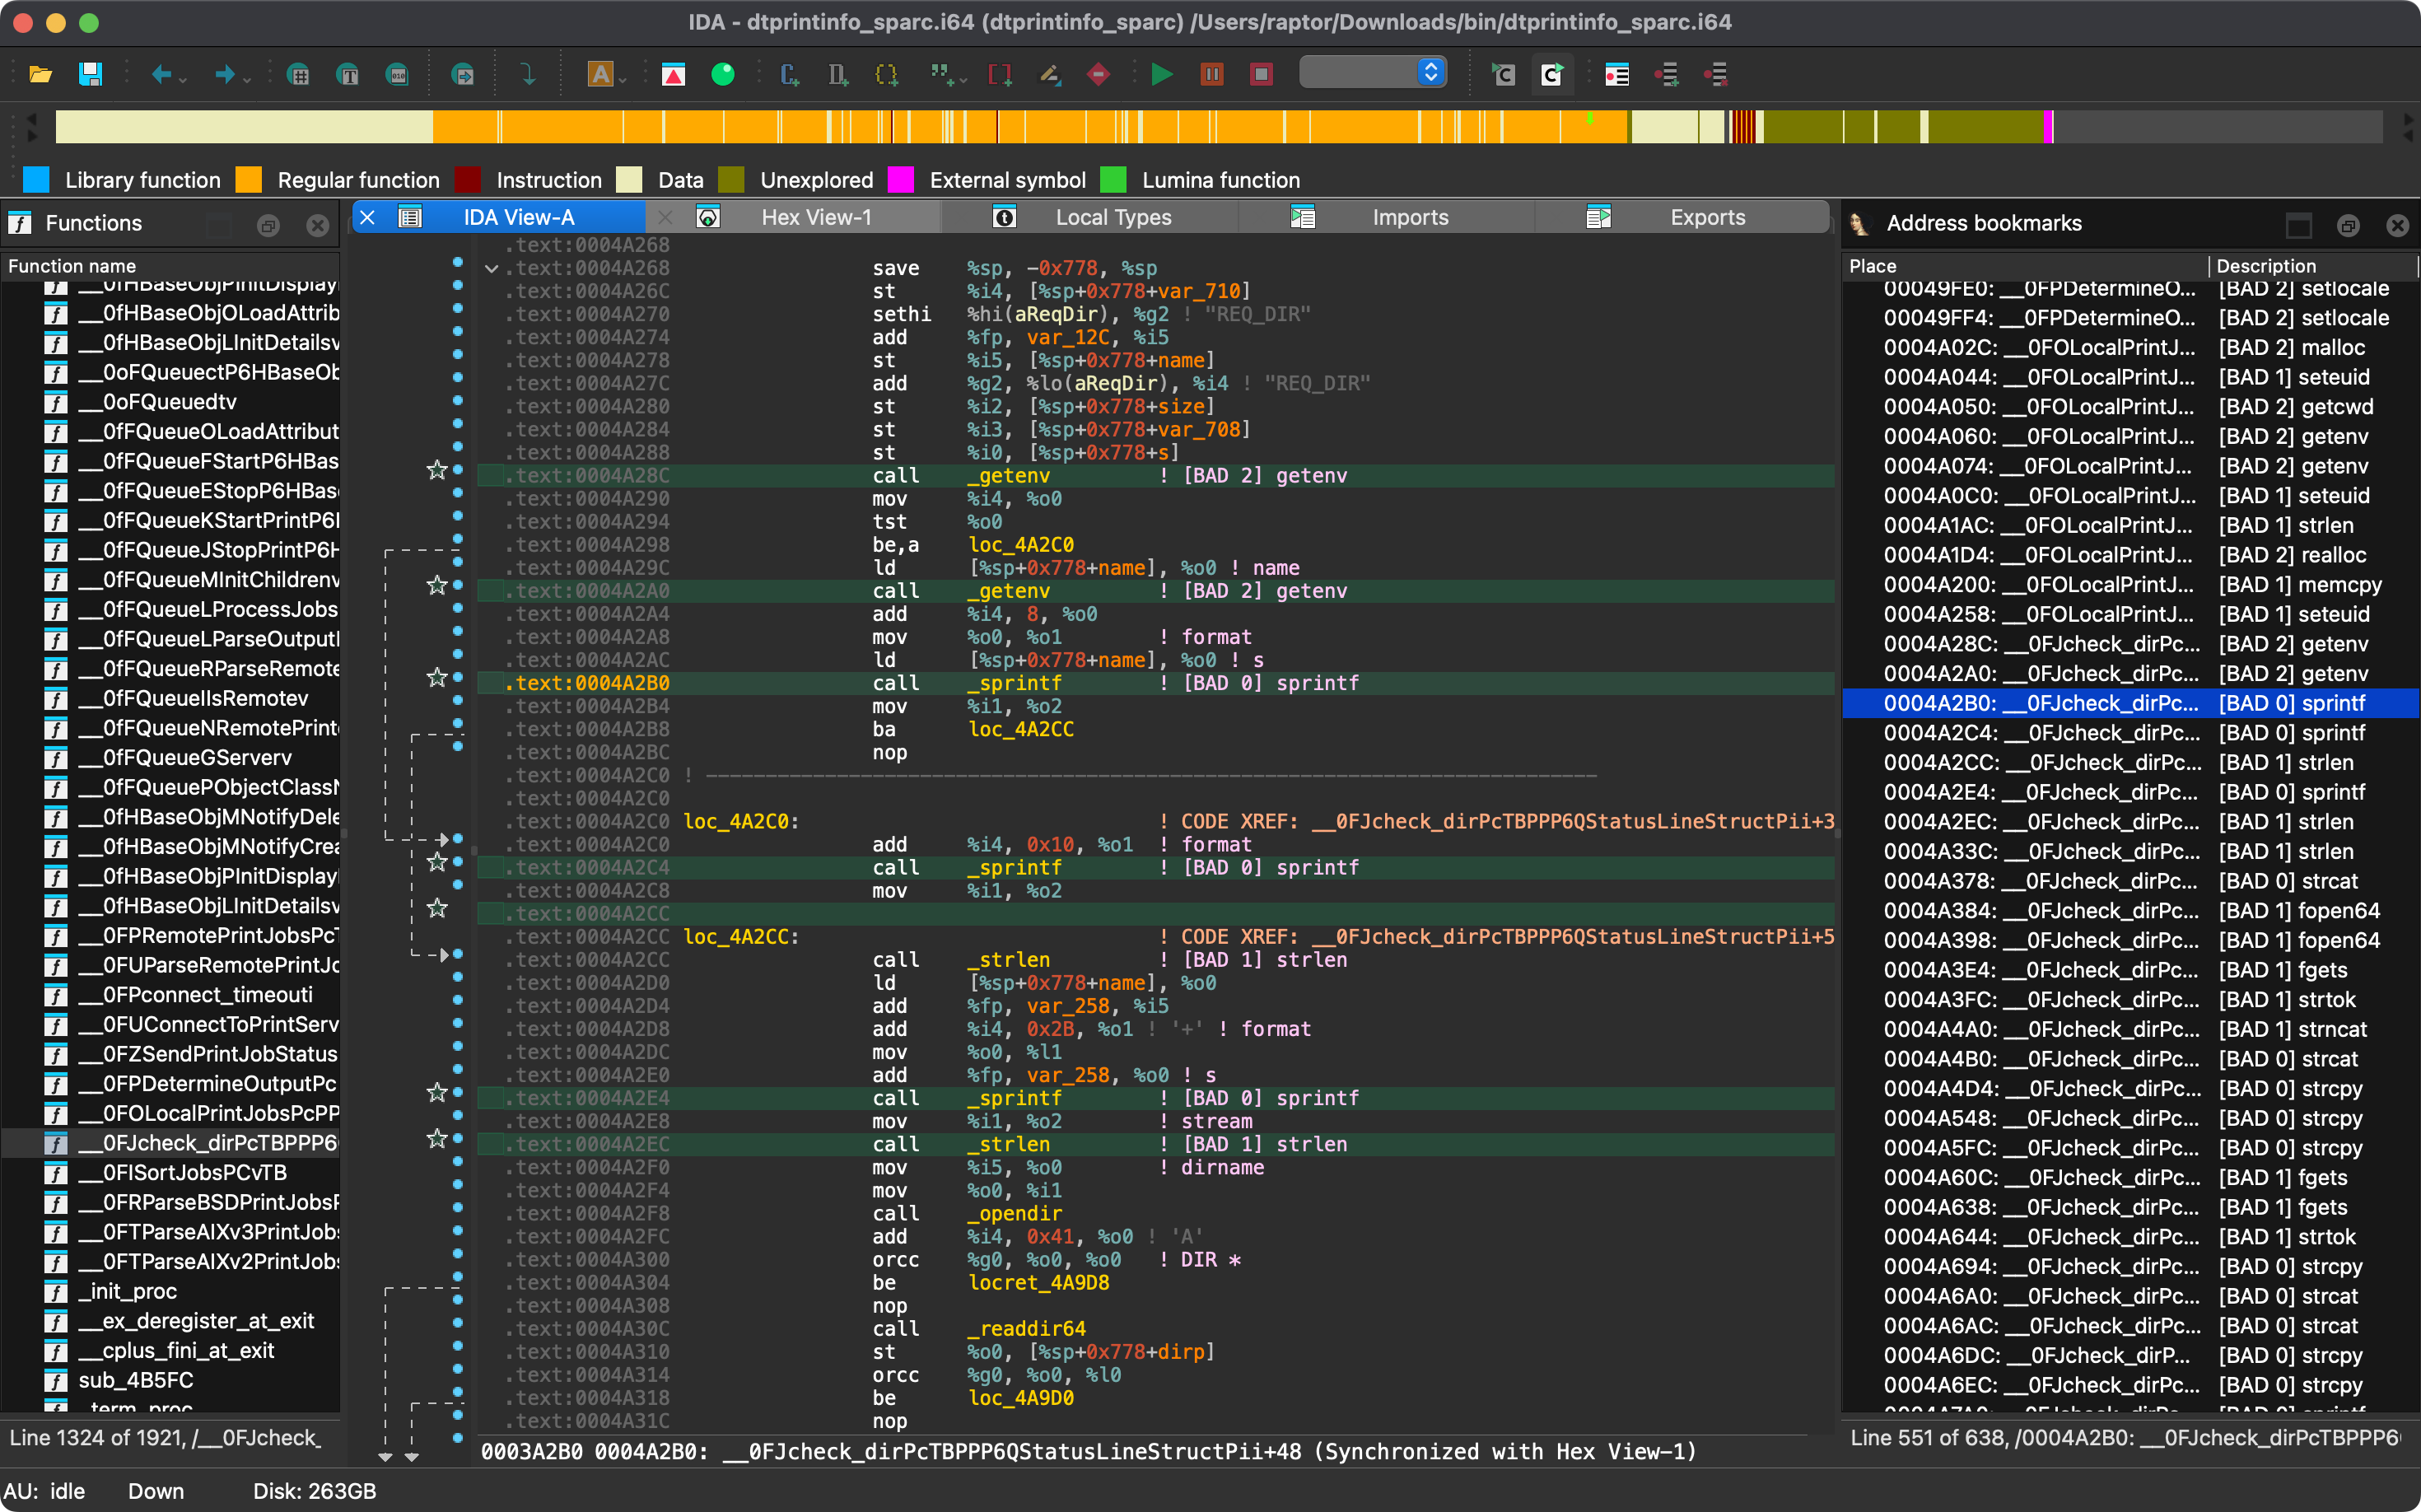 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
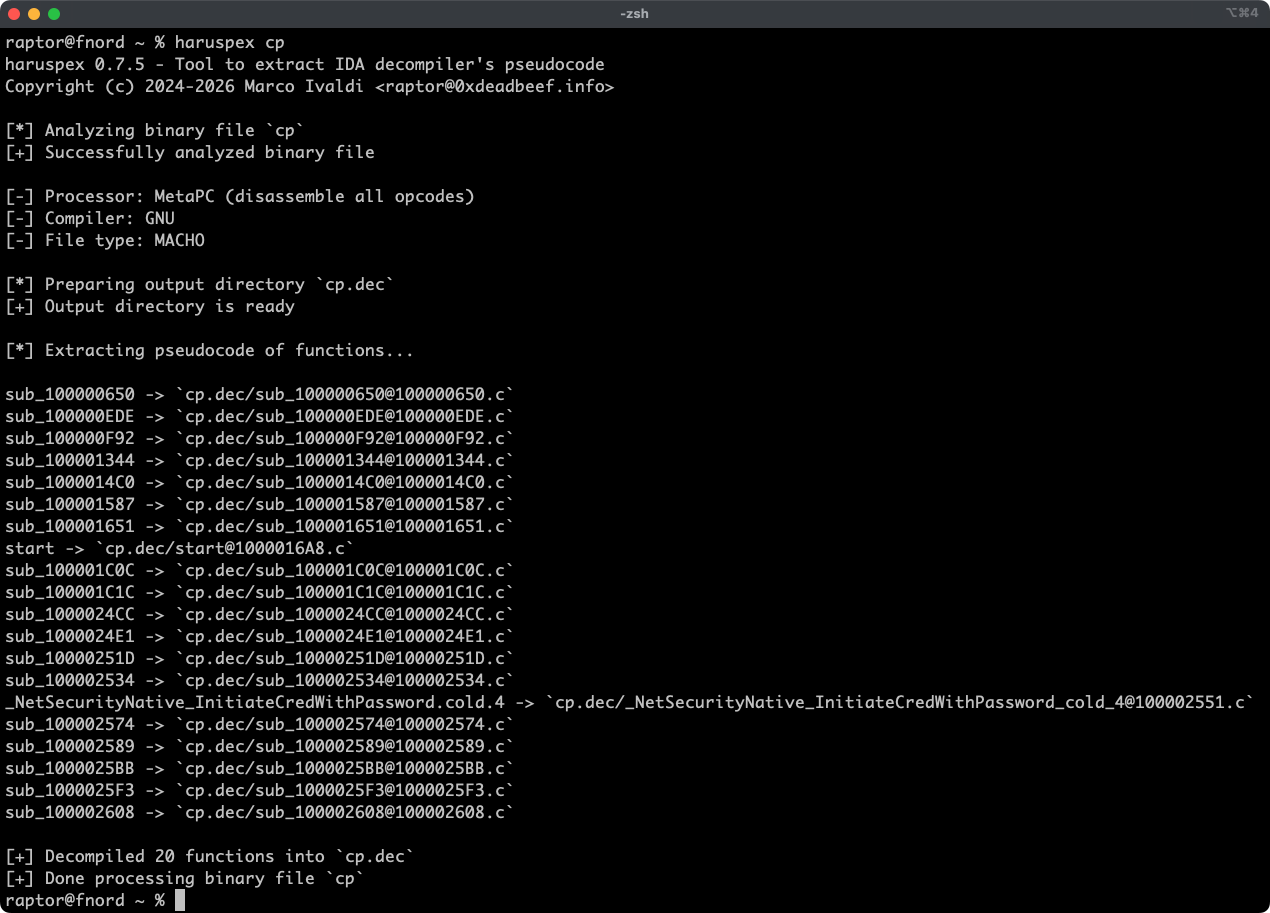 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 angr/angr
A powerful and user-friendly binary analysis platform!
 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
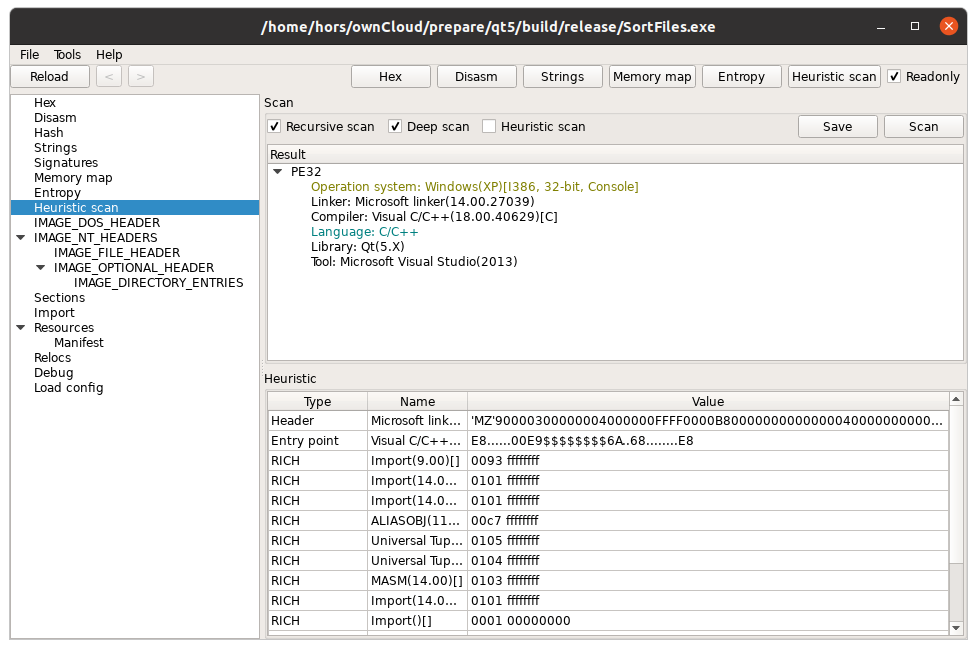 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
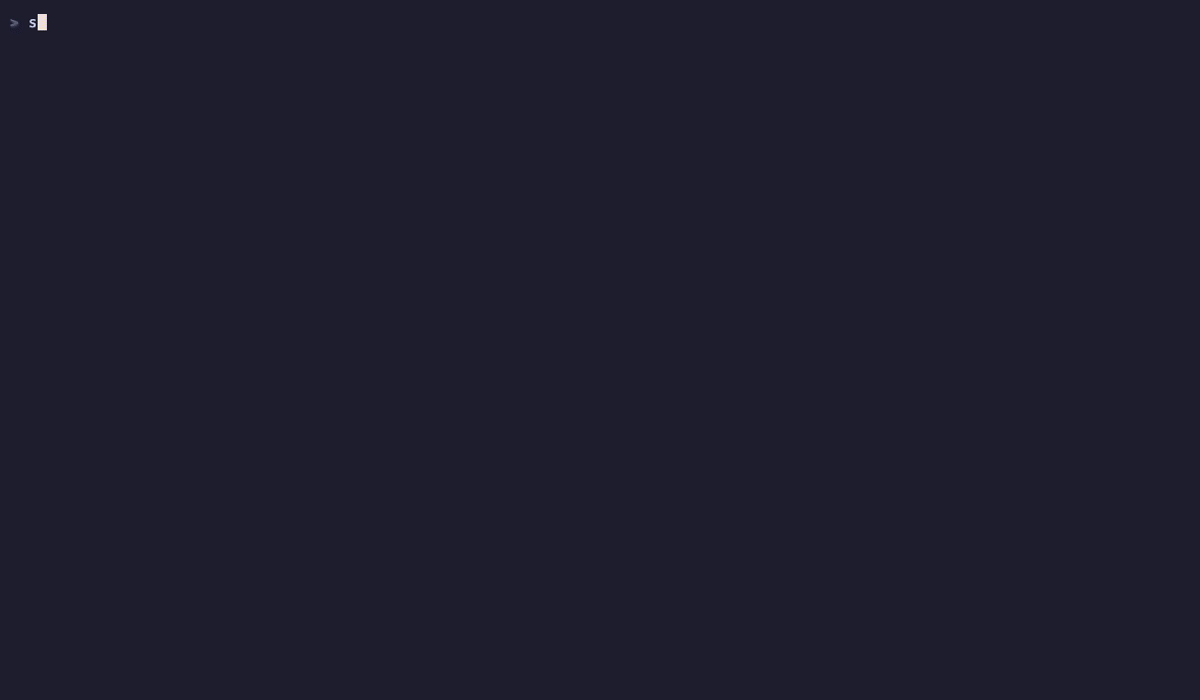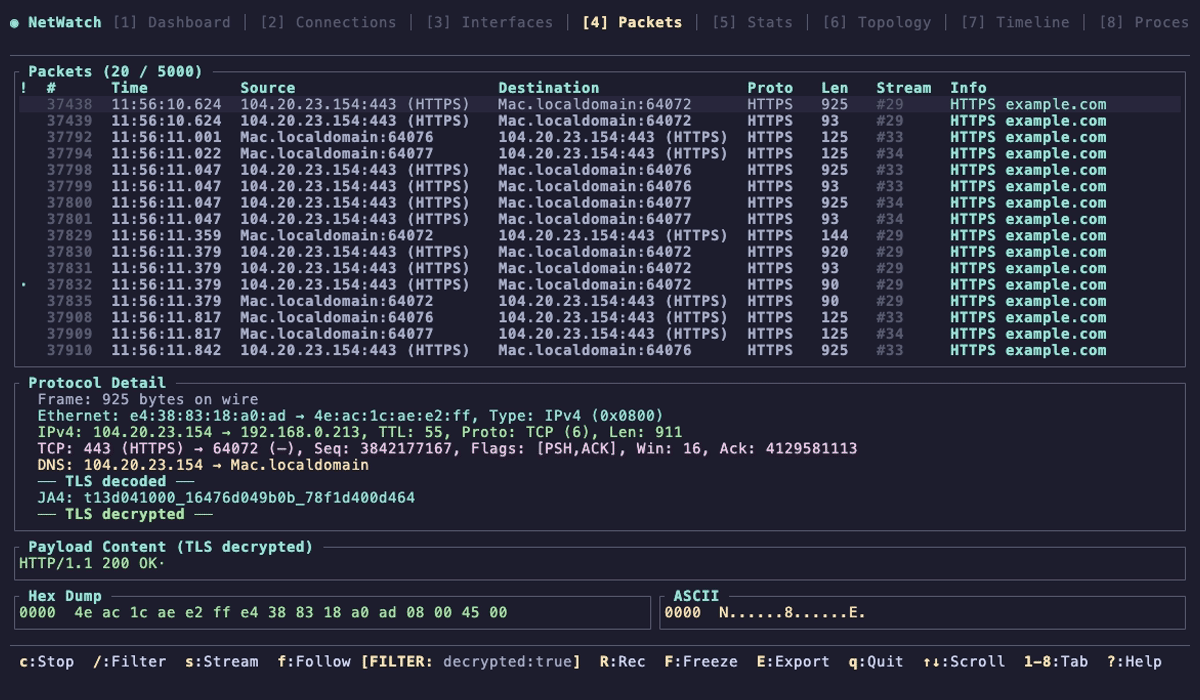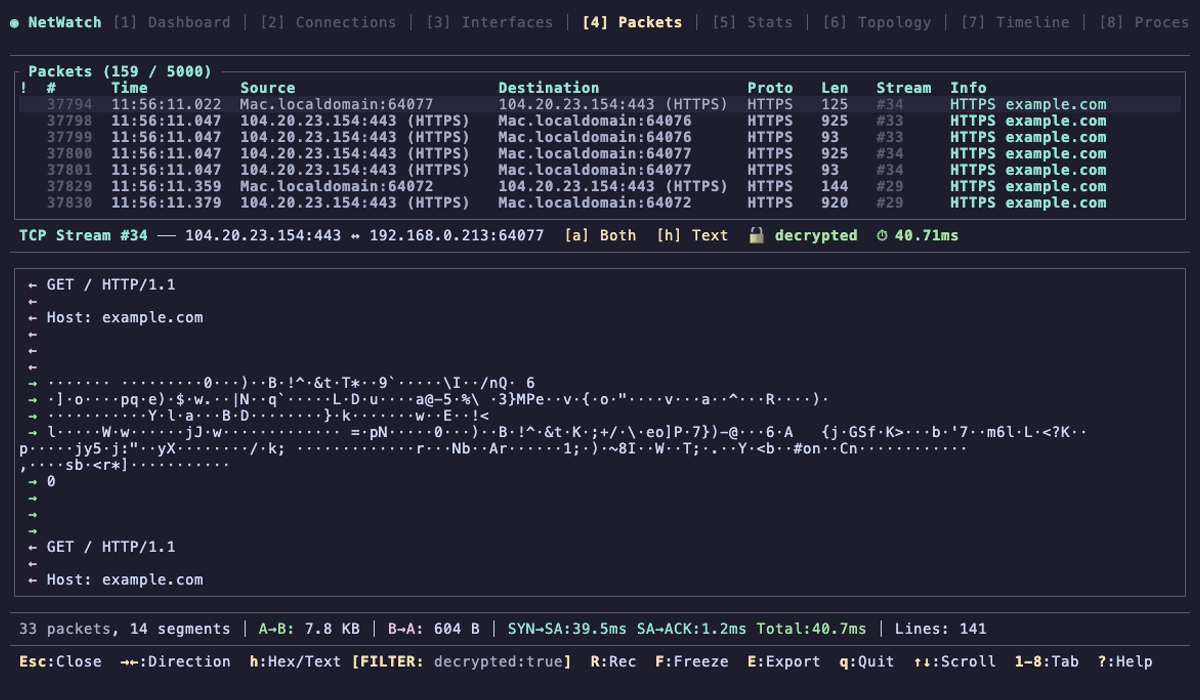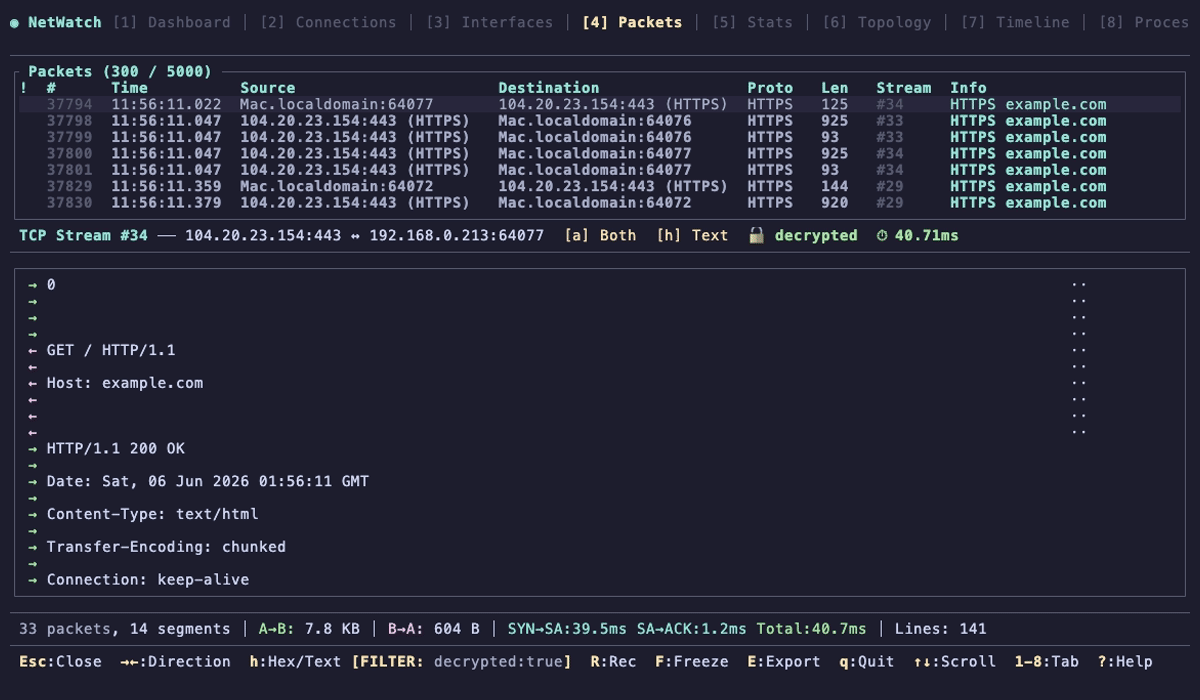 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
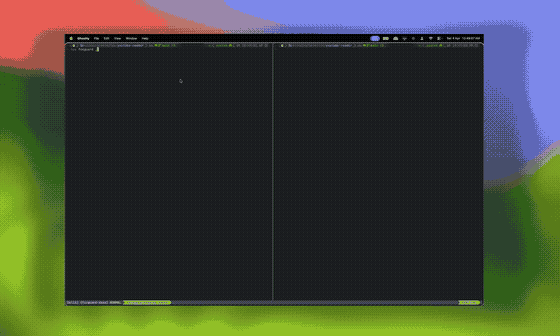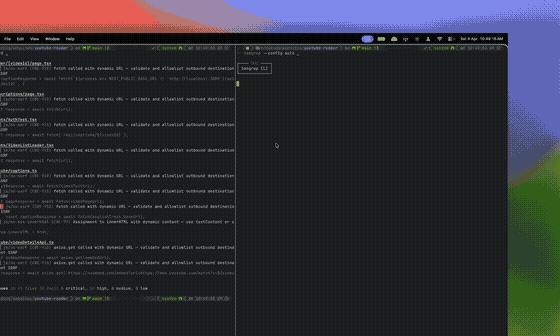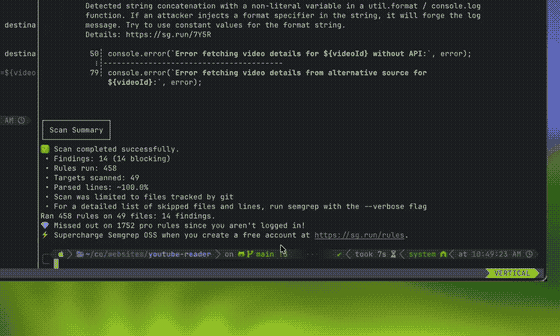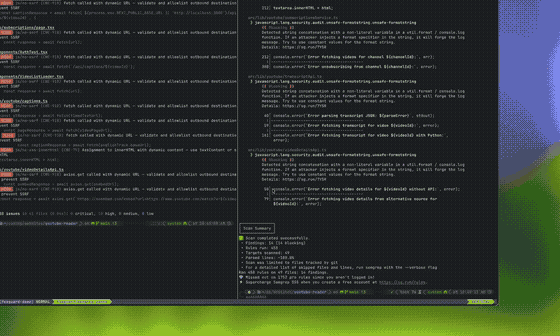 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…