#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
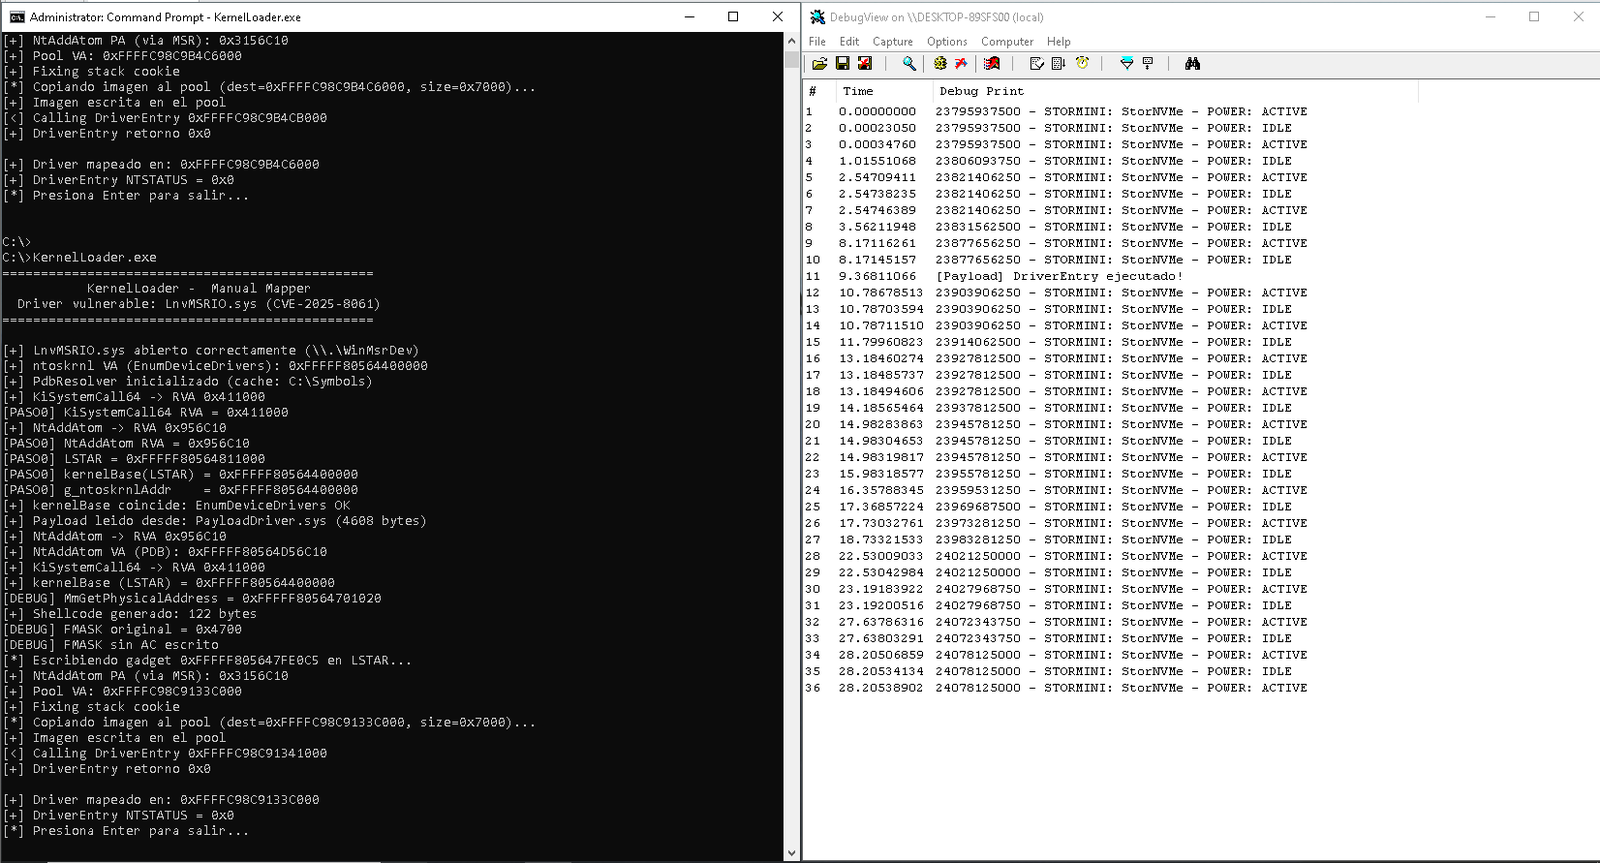 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
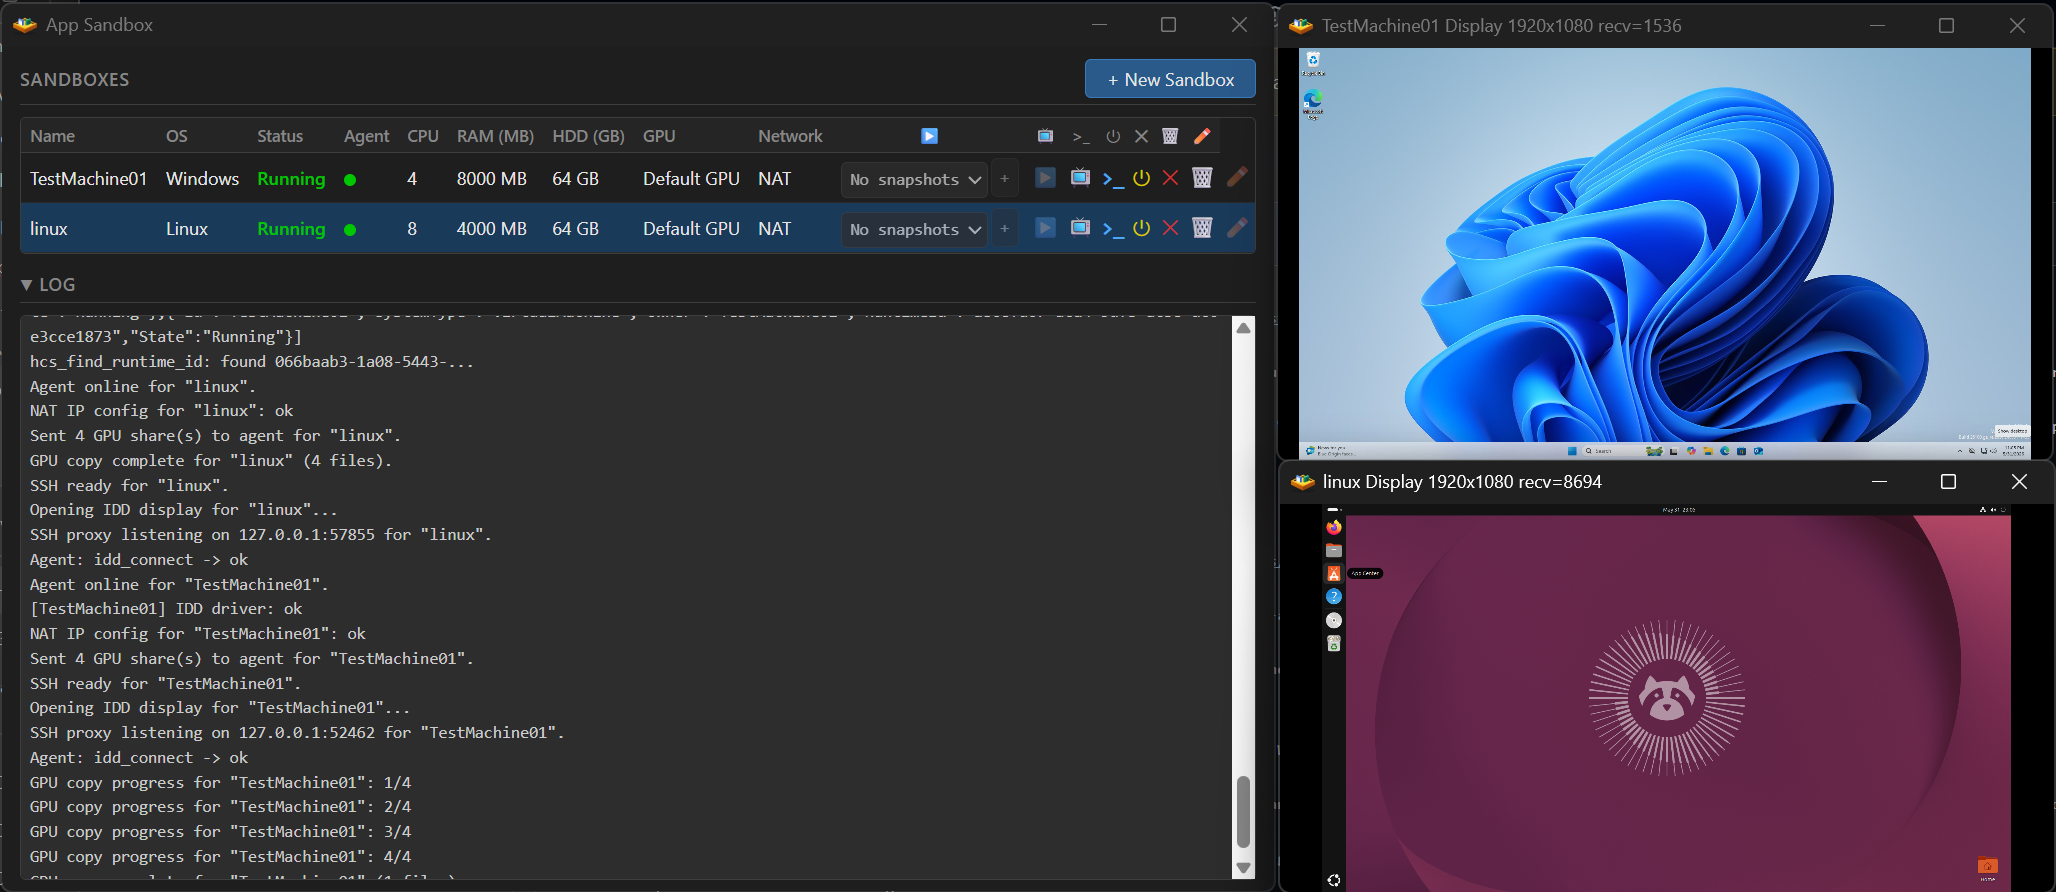 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 owasp/ocsd
OWASP Certified Secure-Software Developer
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 nowsecure/r2frida
Radare2 and Frida better together.
 go-delve/delve
Source-level debugger for Go with CLI, API, and headless modes; supports breakpoints, variable inspection, and execution tracing for efficient…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 frack113/malwaretracesgenerator
Generate malware traces for detection tests
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 frida/frida
Main repo for hosting release binaries