

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Malware Analysis — Page 85 | Kitploit
Categories

Malware Analysis

Tools for dissecting, understanding, and reverse engineering malicious software behavior.

Kitploit recommended
Top tools

10 selected
yara-x preview#1

yara-x

GitHubvirustotal/yara-x
1.2k19h 19m ago
capa preview#3

capa

GitHubmandiant/capa
6.1k11 days ago
flare-floss preview#4

flare-floss

GitHubmandiant/flare-floss
4.1k1 month ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k3 days ago
radare2 preview#6

radare2

GitHubradareorg/radare2
24.5k9h 1m ago
ghidra preview#7

ghidra

GitHubnationalsecurityagency/ghidra
71.1k20h 10m ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k8h 26m ago
theZoo preview#9

theZoo

GitHubytisf/thezoo
13.3k2 months ago
flare-vm preview#10

flare-vm

GitHubmandiant/flare-vm
8.9k1 month ago
IntelOwl preview#11

IntelOwl

GitHubintelowlproject/intelowl
4.7k2 months ago
NewestRelevanceMost popularRecently updated
4071 results
windows-x86-shellcode-poc preview

windows-x86-shellcode-poc

GitHubnataliadiak/windows-x86-shellcode-poc

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.

vulnerability-analysisreverse-engineeringshellcode+3
86 months ago
Scripts-With-Malware-Analysis preview

Scripts-With-Malware-Analysis

GitHubmalgamy/scripts-with-malware-analysis
reverse-engineeringmalware-analysisdigital-forensics
62 years ago
spd_flasher preview

spd_flasher

GitHubleochen-coremind/spd_flasher

CVE-2022-38694 Hardened Exploit - RP2350 USB Host Auto Flasher for Unisoc devices

embedded-systems-securityexploitationreverse-engineering+3
33 months ago
CVE-2026-57821-PoC-Exploit preview

CVE-2026-57821-PoC-Exploit

GitHubtc4dy/cve-2026-57821-poc-exploit

🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…

static-analysisvulnerability-analysiscode-analysis+5
31 month ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

privilege-escalationpersistence-mechanismsvulnerability-analysis+7
34 months ago
CVE-2025-61155 preview

CVE-2025-61155

GitHubsf0rzin/cve-2025-61155

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…

privilege-escalationvulnerability-analysisexploitation+7
24 months ago
Komfy-Switch-Wifi-Password-Disclosure preview

Komfy-Switch-Wifi-Password-Disclosure

GitHubjasondoyle/komfy-switch-wifi-password-disclosure

Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…
bluetooth-securityiot-securityvulnerability-analysis+3
110 years ago
CVE-2002-1120 preview

CVE-2002-1120

GitHubthemalwareguardian/cve-2002-1120

Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.

vulnerability-analysisexploitationreverse-engineering+8
18 months ago
xz-cve-2024-3094 preview

xz-cve-2024-3094

GitHubhackura/xz-cve-2024-3094

Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.

vulnerability-analysisforensicsmalware-analysis+6
9 months ago
tcl-androidtv-root-attempts preview

tcl-androidtv-root-attempts

GitHub4onurdemir/tcl-androidtv-root-attempts

Documents reverse engineering of a TCL Android TV factory layer: 56 kHz IR protocol, tclfactoryos daemon, kernel IR driver, and evidence that…

android-securityembedded-systems-securityprivilege-escalation+8
117 days ago
frida-medit preview

frida-medit

GitHubgmh5225/frida-medit

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

dynamic-analysis-sandboxingmemory-forensicsreverse-engineering+3
3 years ago
zte-smartlife-app-pwned preview

zte-smartlife-app-pwned

GitHubminanagehsalalma/zte-smartlife-app-pwned

ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.

android-securityvulnerability-analysisexploitation+7
2 months ago
CVE-2022-34302 preview

CVE-2022-34302

GitHubthemalwareguardian/cve-2022-34302

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

embedded-systems-securitypersistence-mechanismsvulnerability-analysis+7
2 months ago
block-copyfail preview

block-copyfail

GitHubatgreen/block-copyfail

BPF LSM blocker for CVE-2026-31431 (Copy Fail) — blocks authencesn AF_ALG binds at runtime without rebooting

defensive-toolsdynamic-analysis-sandboxingvulnerability-analysis+1
76 months ago
log4jhound preview

log4jhound

GitHubmebibite/log4jhound

Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
static-analysisvulnerability-scannerscode-analysis+2
4 years ago
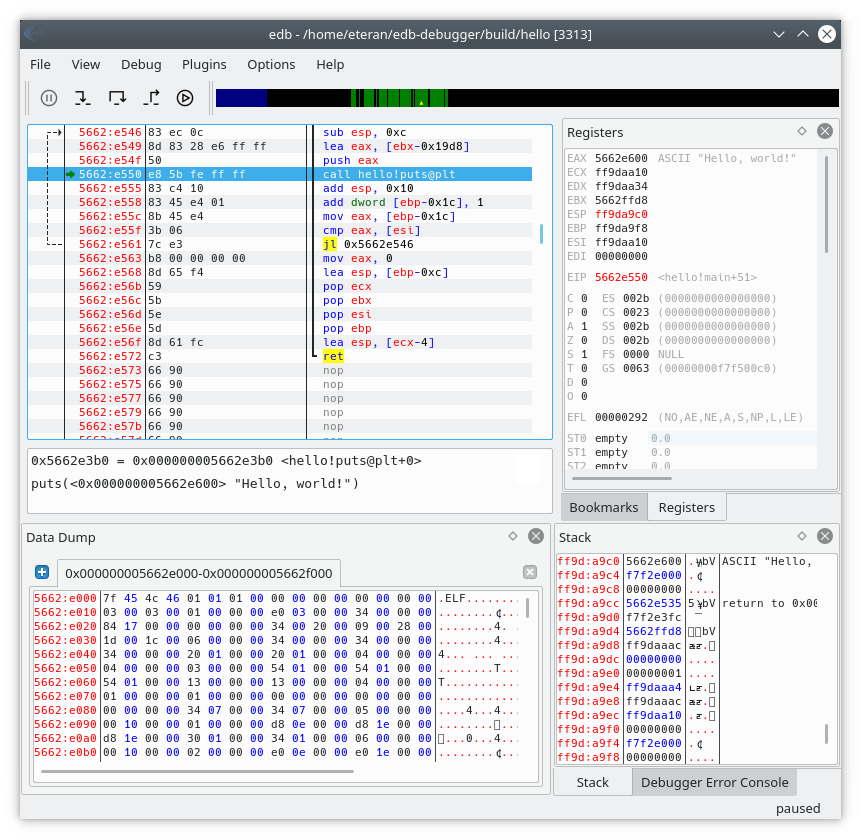
edb-debugger preview

edb-debugger

GitHubeteran/edb-debugger

edb is a cross-platform AArch32/x86/x86-64 debugger.

reverse-engineeringdebuggersbinary-analysis
3.0k3 days ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

memory-forensicspersistence-mechanismsreverse-engineering+4
13 months ago
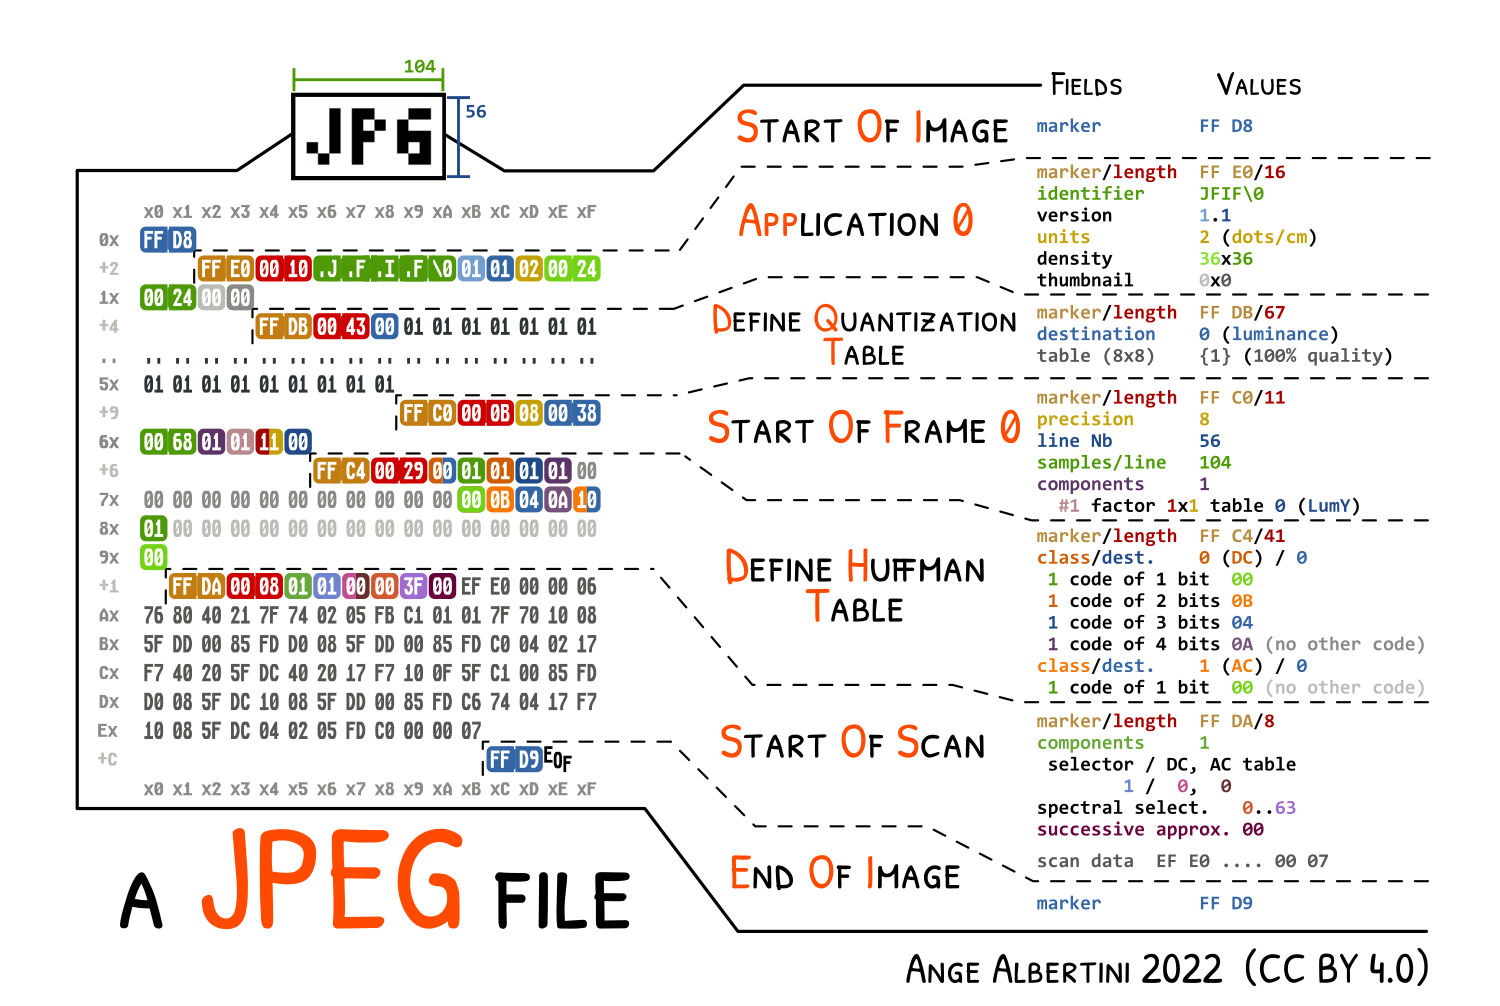
pics preview

pics

GitHubcorkami/pics

File formats dissections and more...

reverse-engineeringbinary-analysiseducation+1
11.5k2 years ago
Previous1…848586…100Next









