
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 avilum/secimport
Library-Level eBPF Sandbox for Python (Linux & macOS): syscall-level control per module.
 securagenai/signed-but-steerable
Measuring and closing the text–vector integrity gap in offline RAG: margin law, vector-database audits and code-level verification.
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 oddcod3/phantom-evasion
Python antivirus evasion tool
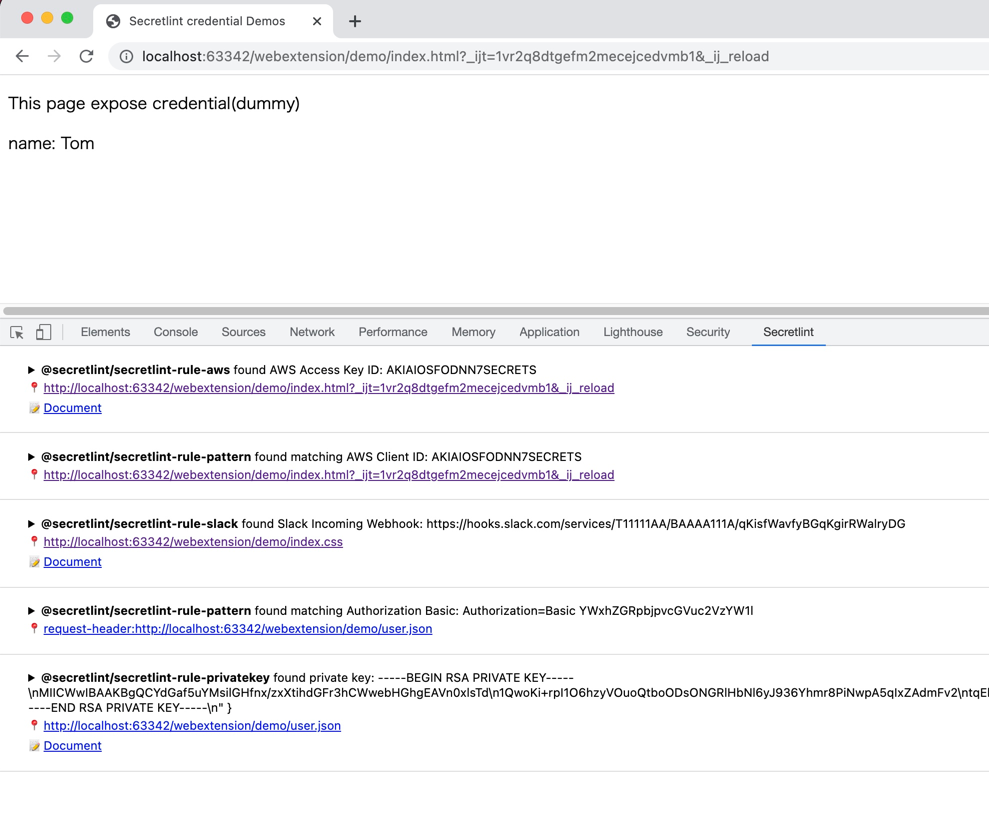 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 tomchop/malcom
Malcom - Malware Communications Analyzer
 sonyxperiadev/apkanalyser
Static analysis tool for Android APKs that inspects Dalvik bytecode, decodes XML resources, and detects potential issues. Supports binary…
 openedx/codejail
Secure code execution
 leochen-coremind/vmpacker
ARM64 ELF Virtual Machine Protection System
 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 akustikrausch/yamaha-smaf-player
A dependency-free C++ PLAYER for Yamaha SMAF (.mmf) ringtones: the polyphonic-ringtone format of the 2000s MA-3 / MA-5 phone chips, rebuilt with its…








