

ARM64 ELF Virtual Machine Protection System
ARM64 ELF Virtual Machine Protection System
Translate ARM64 native instructions into custom VM bytecode for function-level code protection
🇨🇳 中文文档 • Features • Architecture • Quick Start • Usage • License
VMPacker is a Virtual Machine Protection (VMP) system for ARM64 (AArch64) Linux ELF binaries. It decodes target function's native ARM64 instructions into an intermediate representation, translates them into custom VM bytecode, and injects an embedded VM interpreter into the ELF file. At runtime, protected functions are executed by the VM interpreter instead of natively.
ARM64 Native Code  →  Decode  →  Translate  →  Custom VM Bytecode
                                                      ↓
                    Original ELF  ←  Inject  ←  VM Interpreter Stub
| Layer | Technique | Description |
|---|---|---|
| VM Protection | Custom ISA | Randomly mapped opcodes — reverse engineers cannot directly identify instruction semantics |
| OpcodeCryptor | Per-instruction opcode encryption | enc[pc] = op[pc] ^ (key ^ (pc * 0x9E3779B9)) |
| Bytecode Reversal | Execution order reversal | Instructions stored in reverse order; interpreter traverses backwards |
| Token Entry | 3-instruction trampoline | Original function replaced with tokenized entry, hiding actual bytecode location |
| Indirect Dispatch | Function pointer jump table | Filled at runtime on the stack, breaking IDA cross-references |
 |
 |
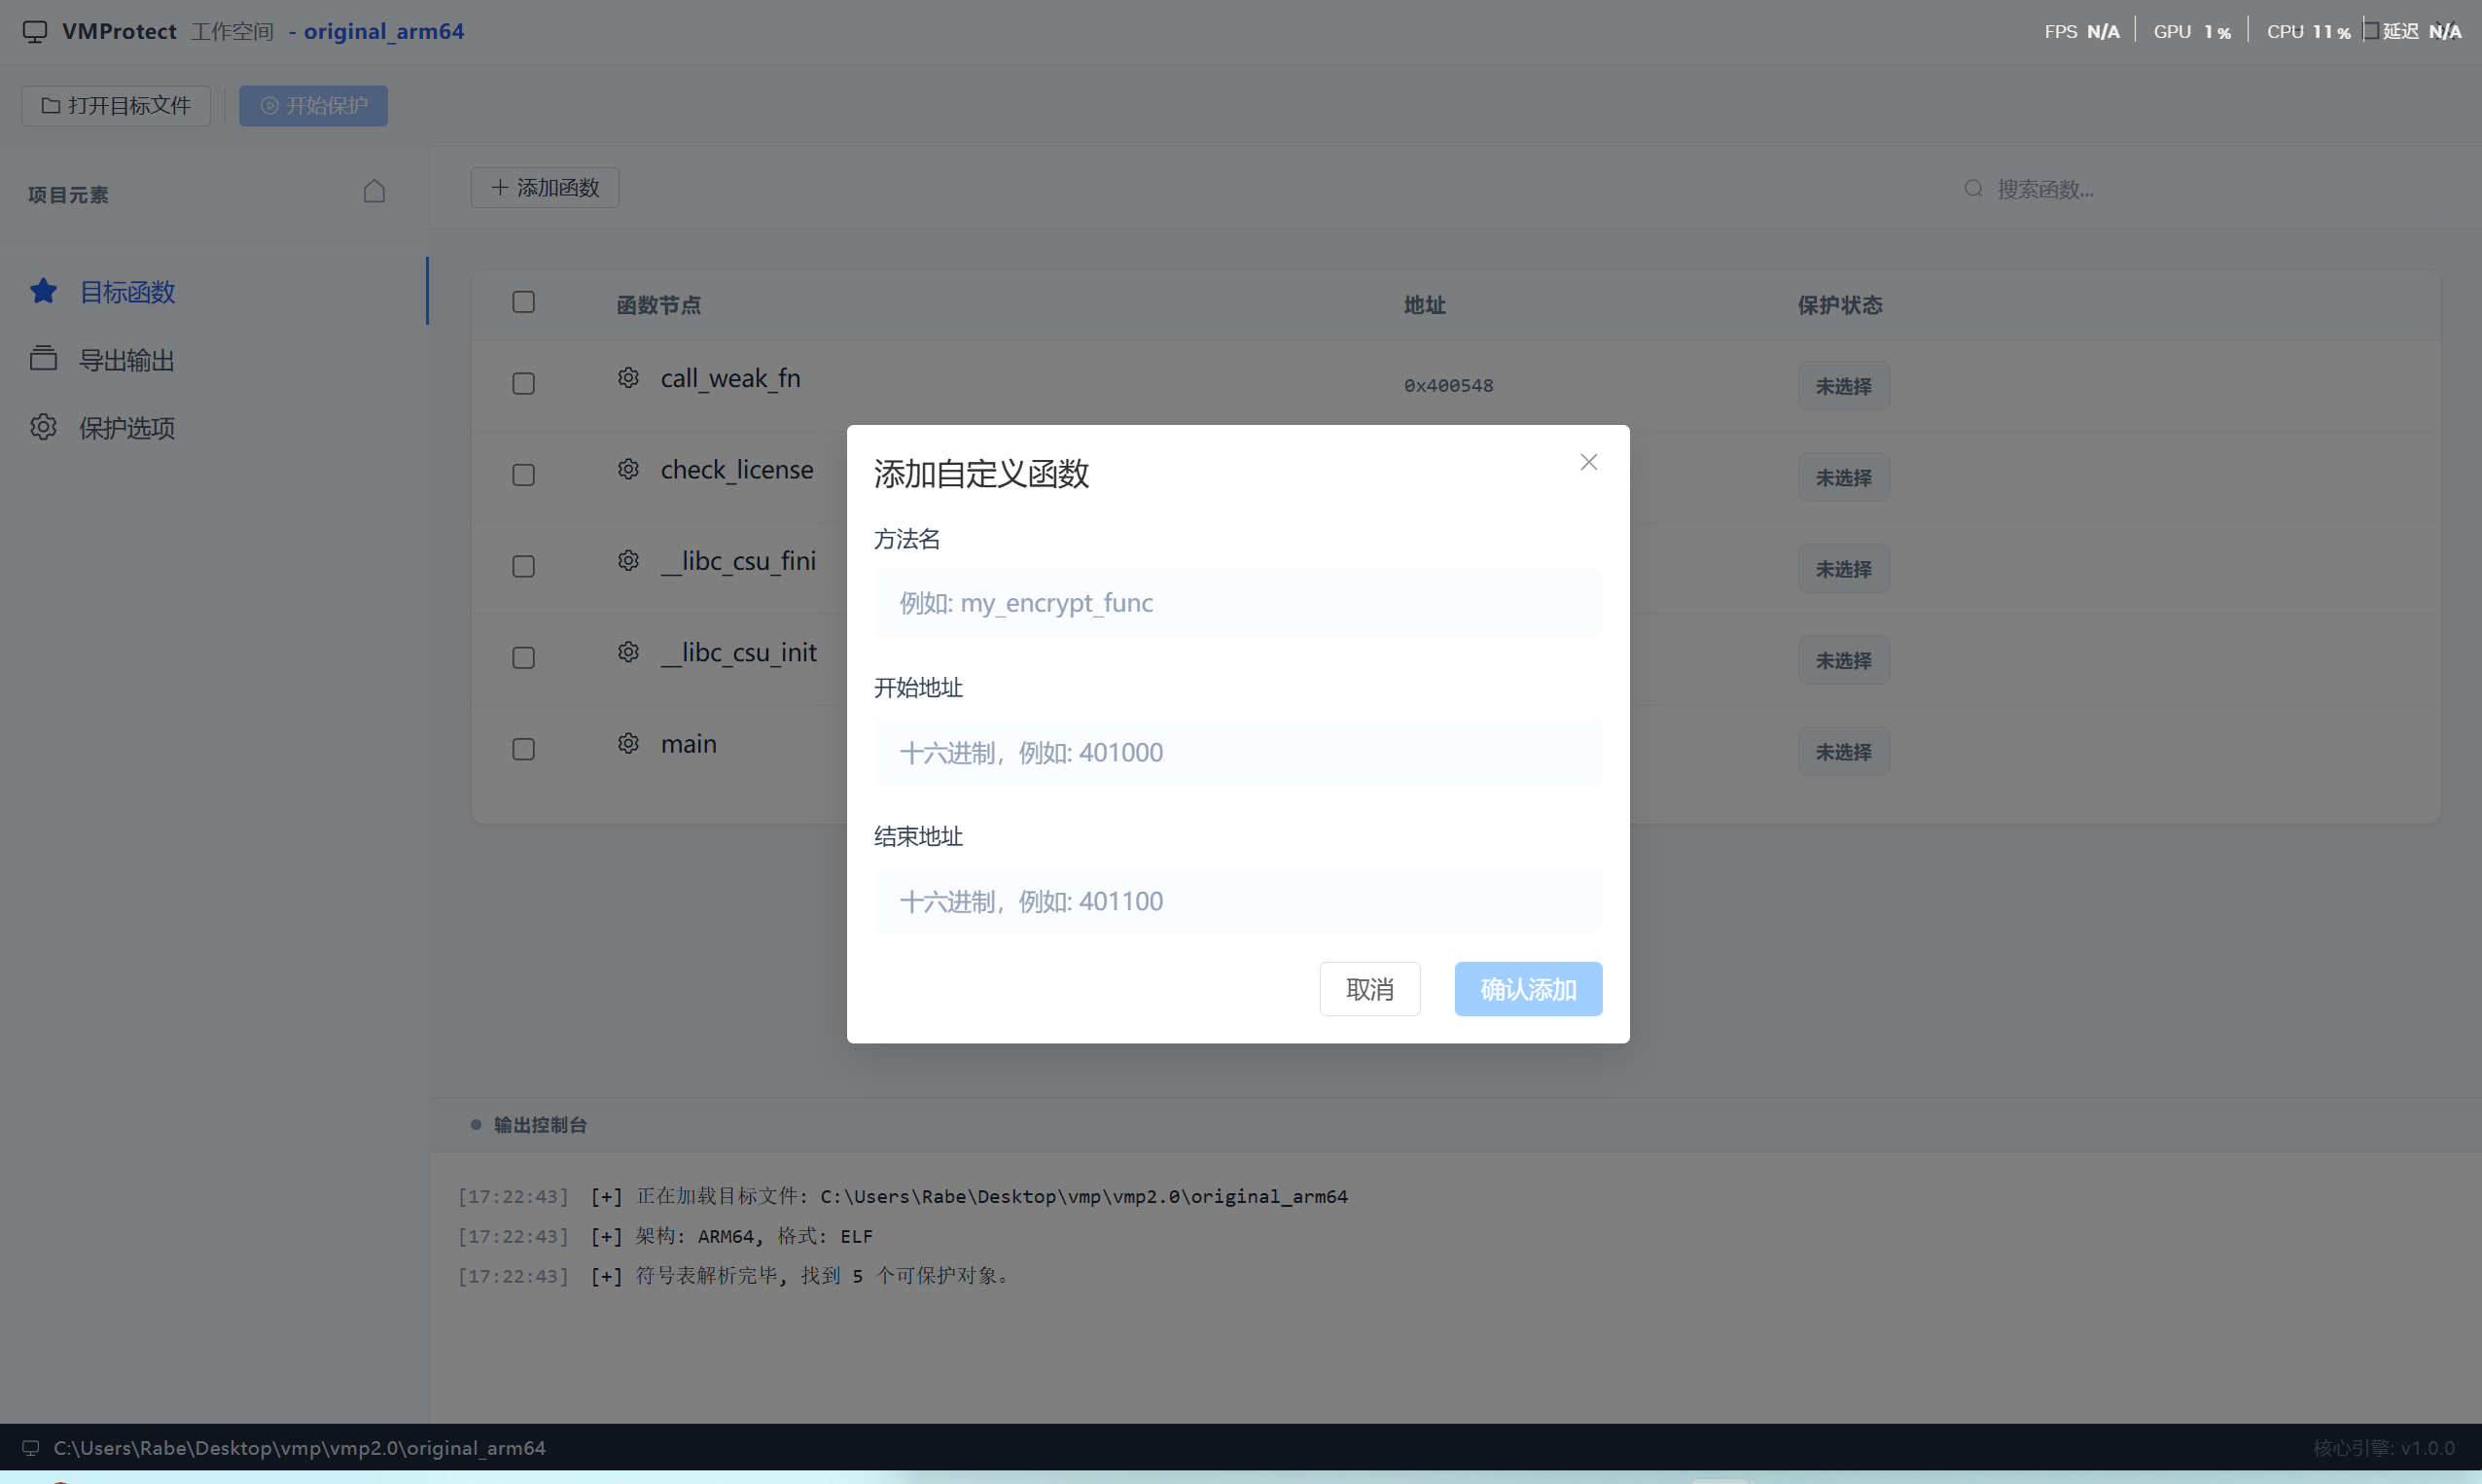 |
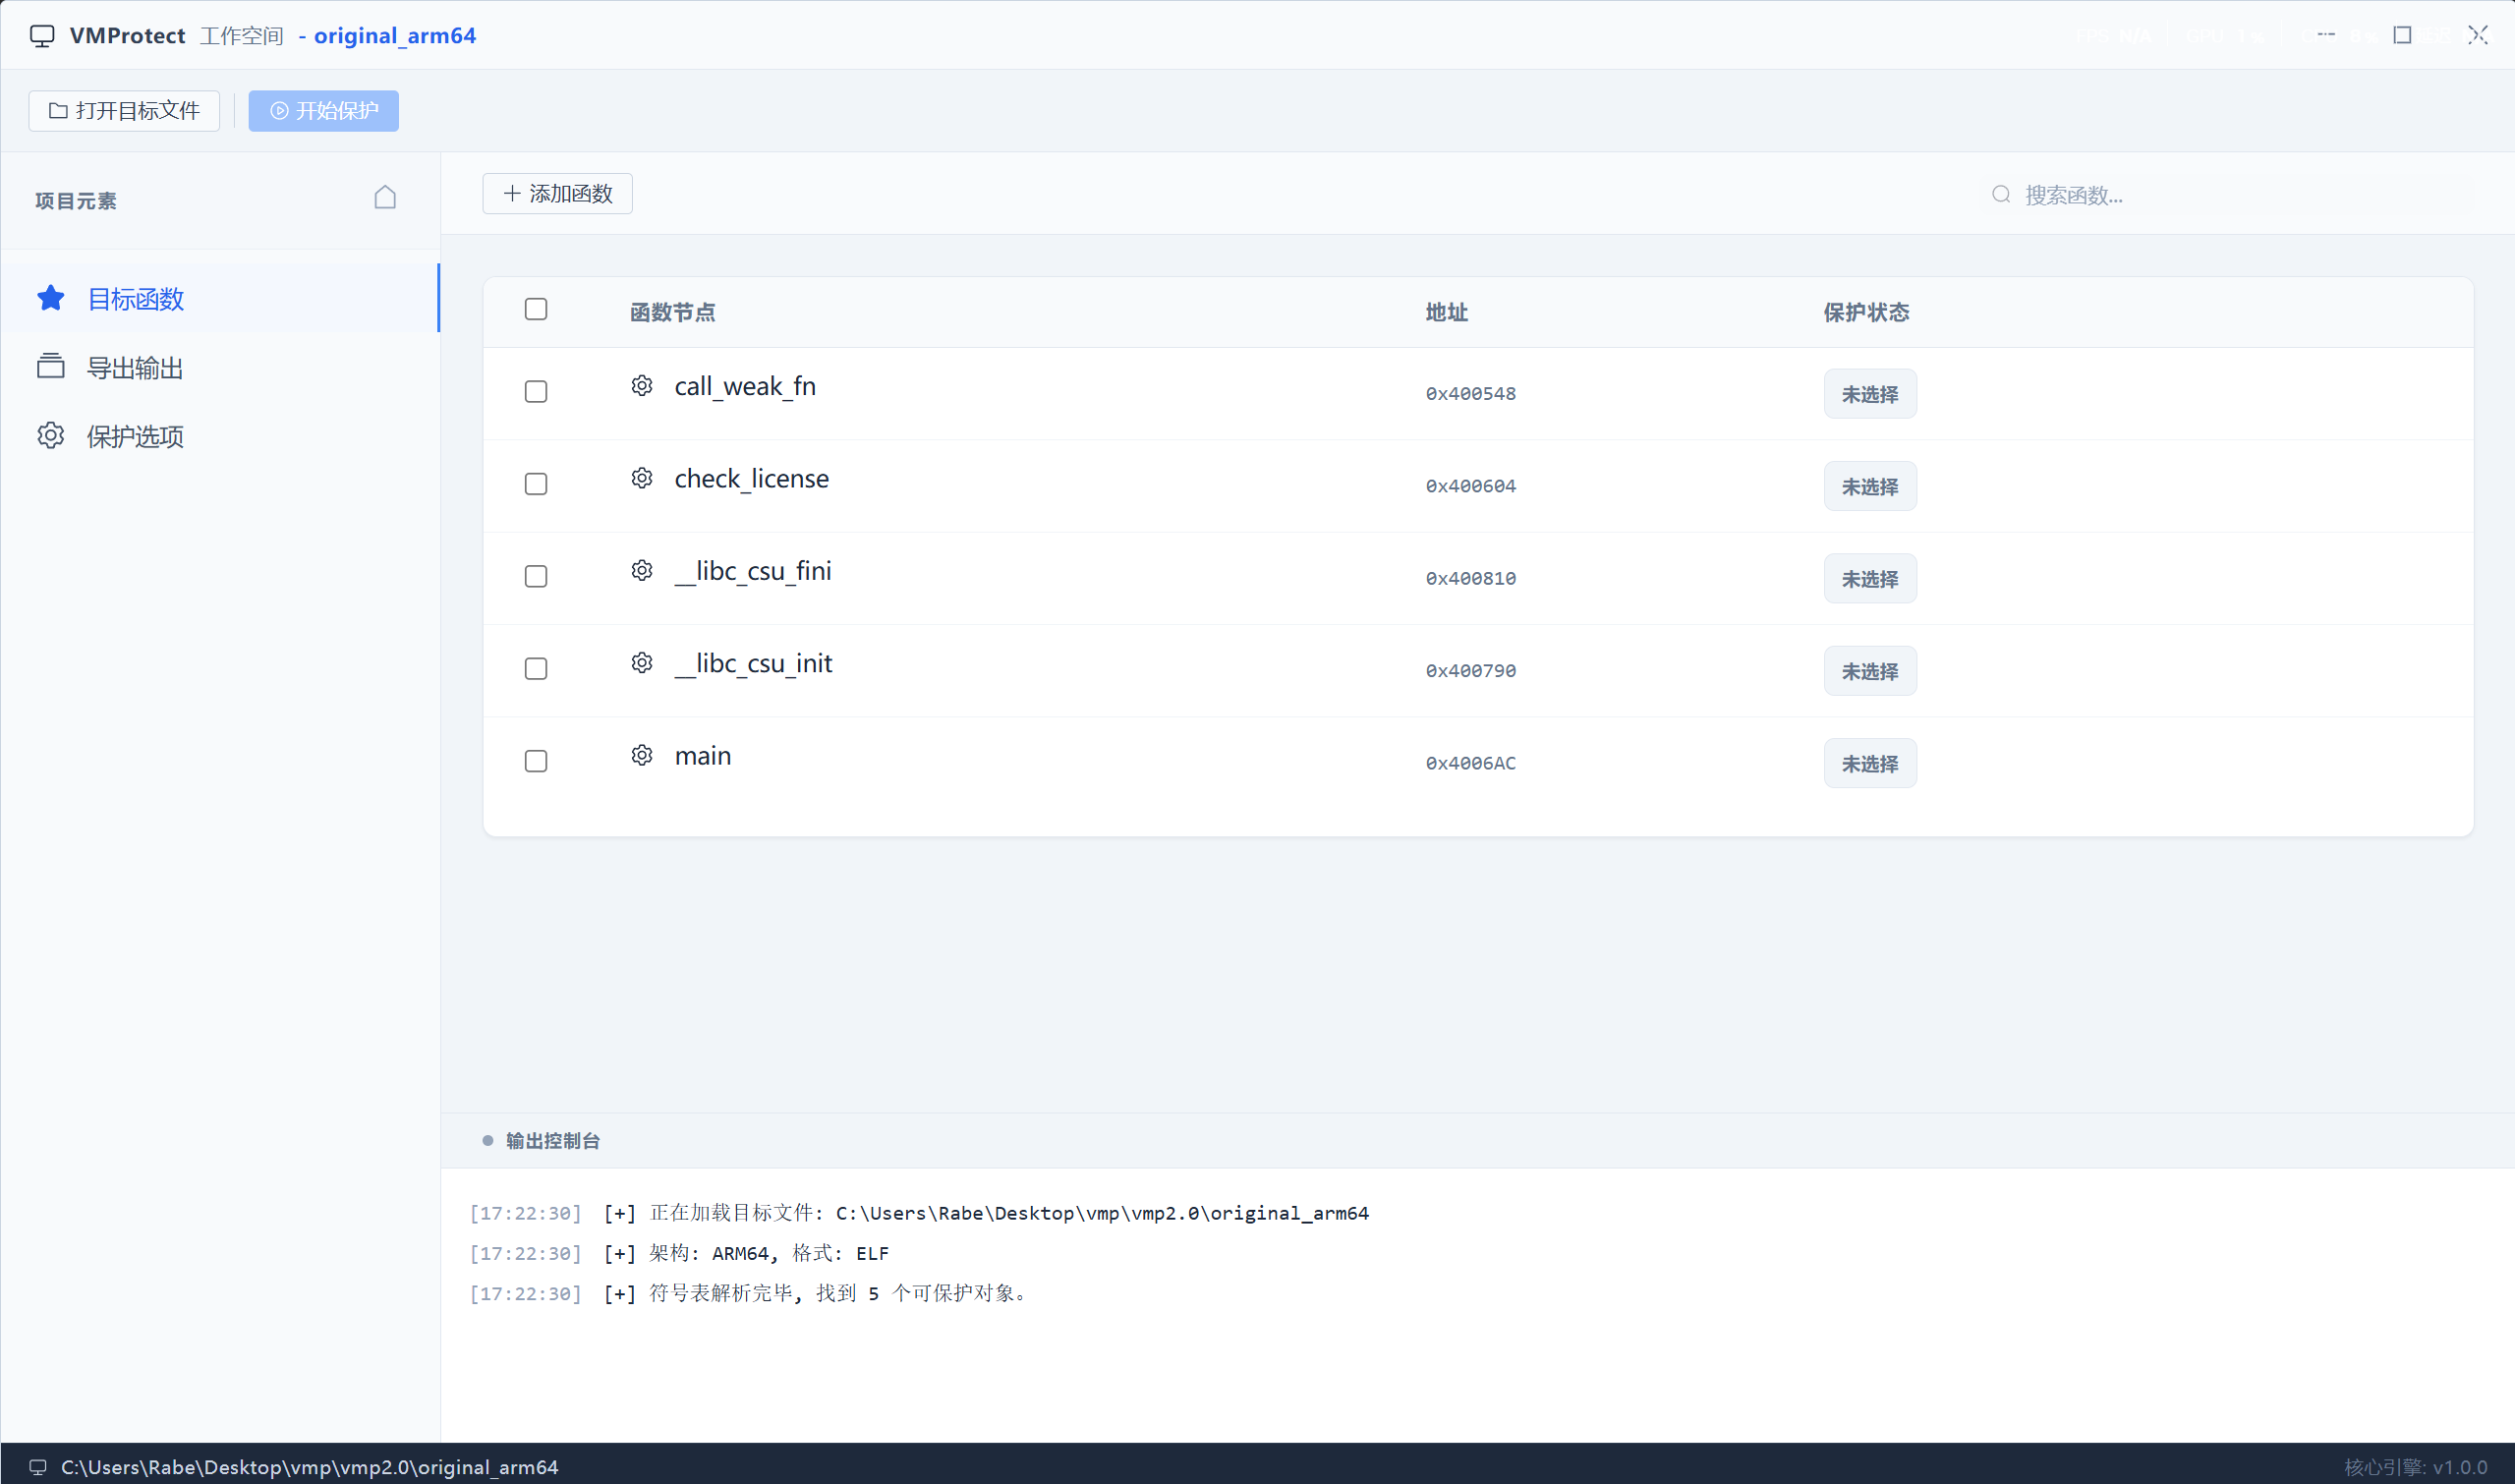
| Function List | Analysis & Selection | Protection Options |
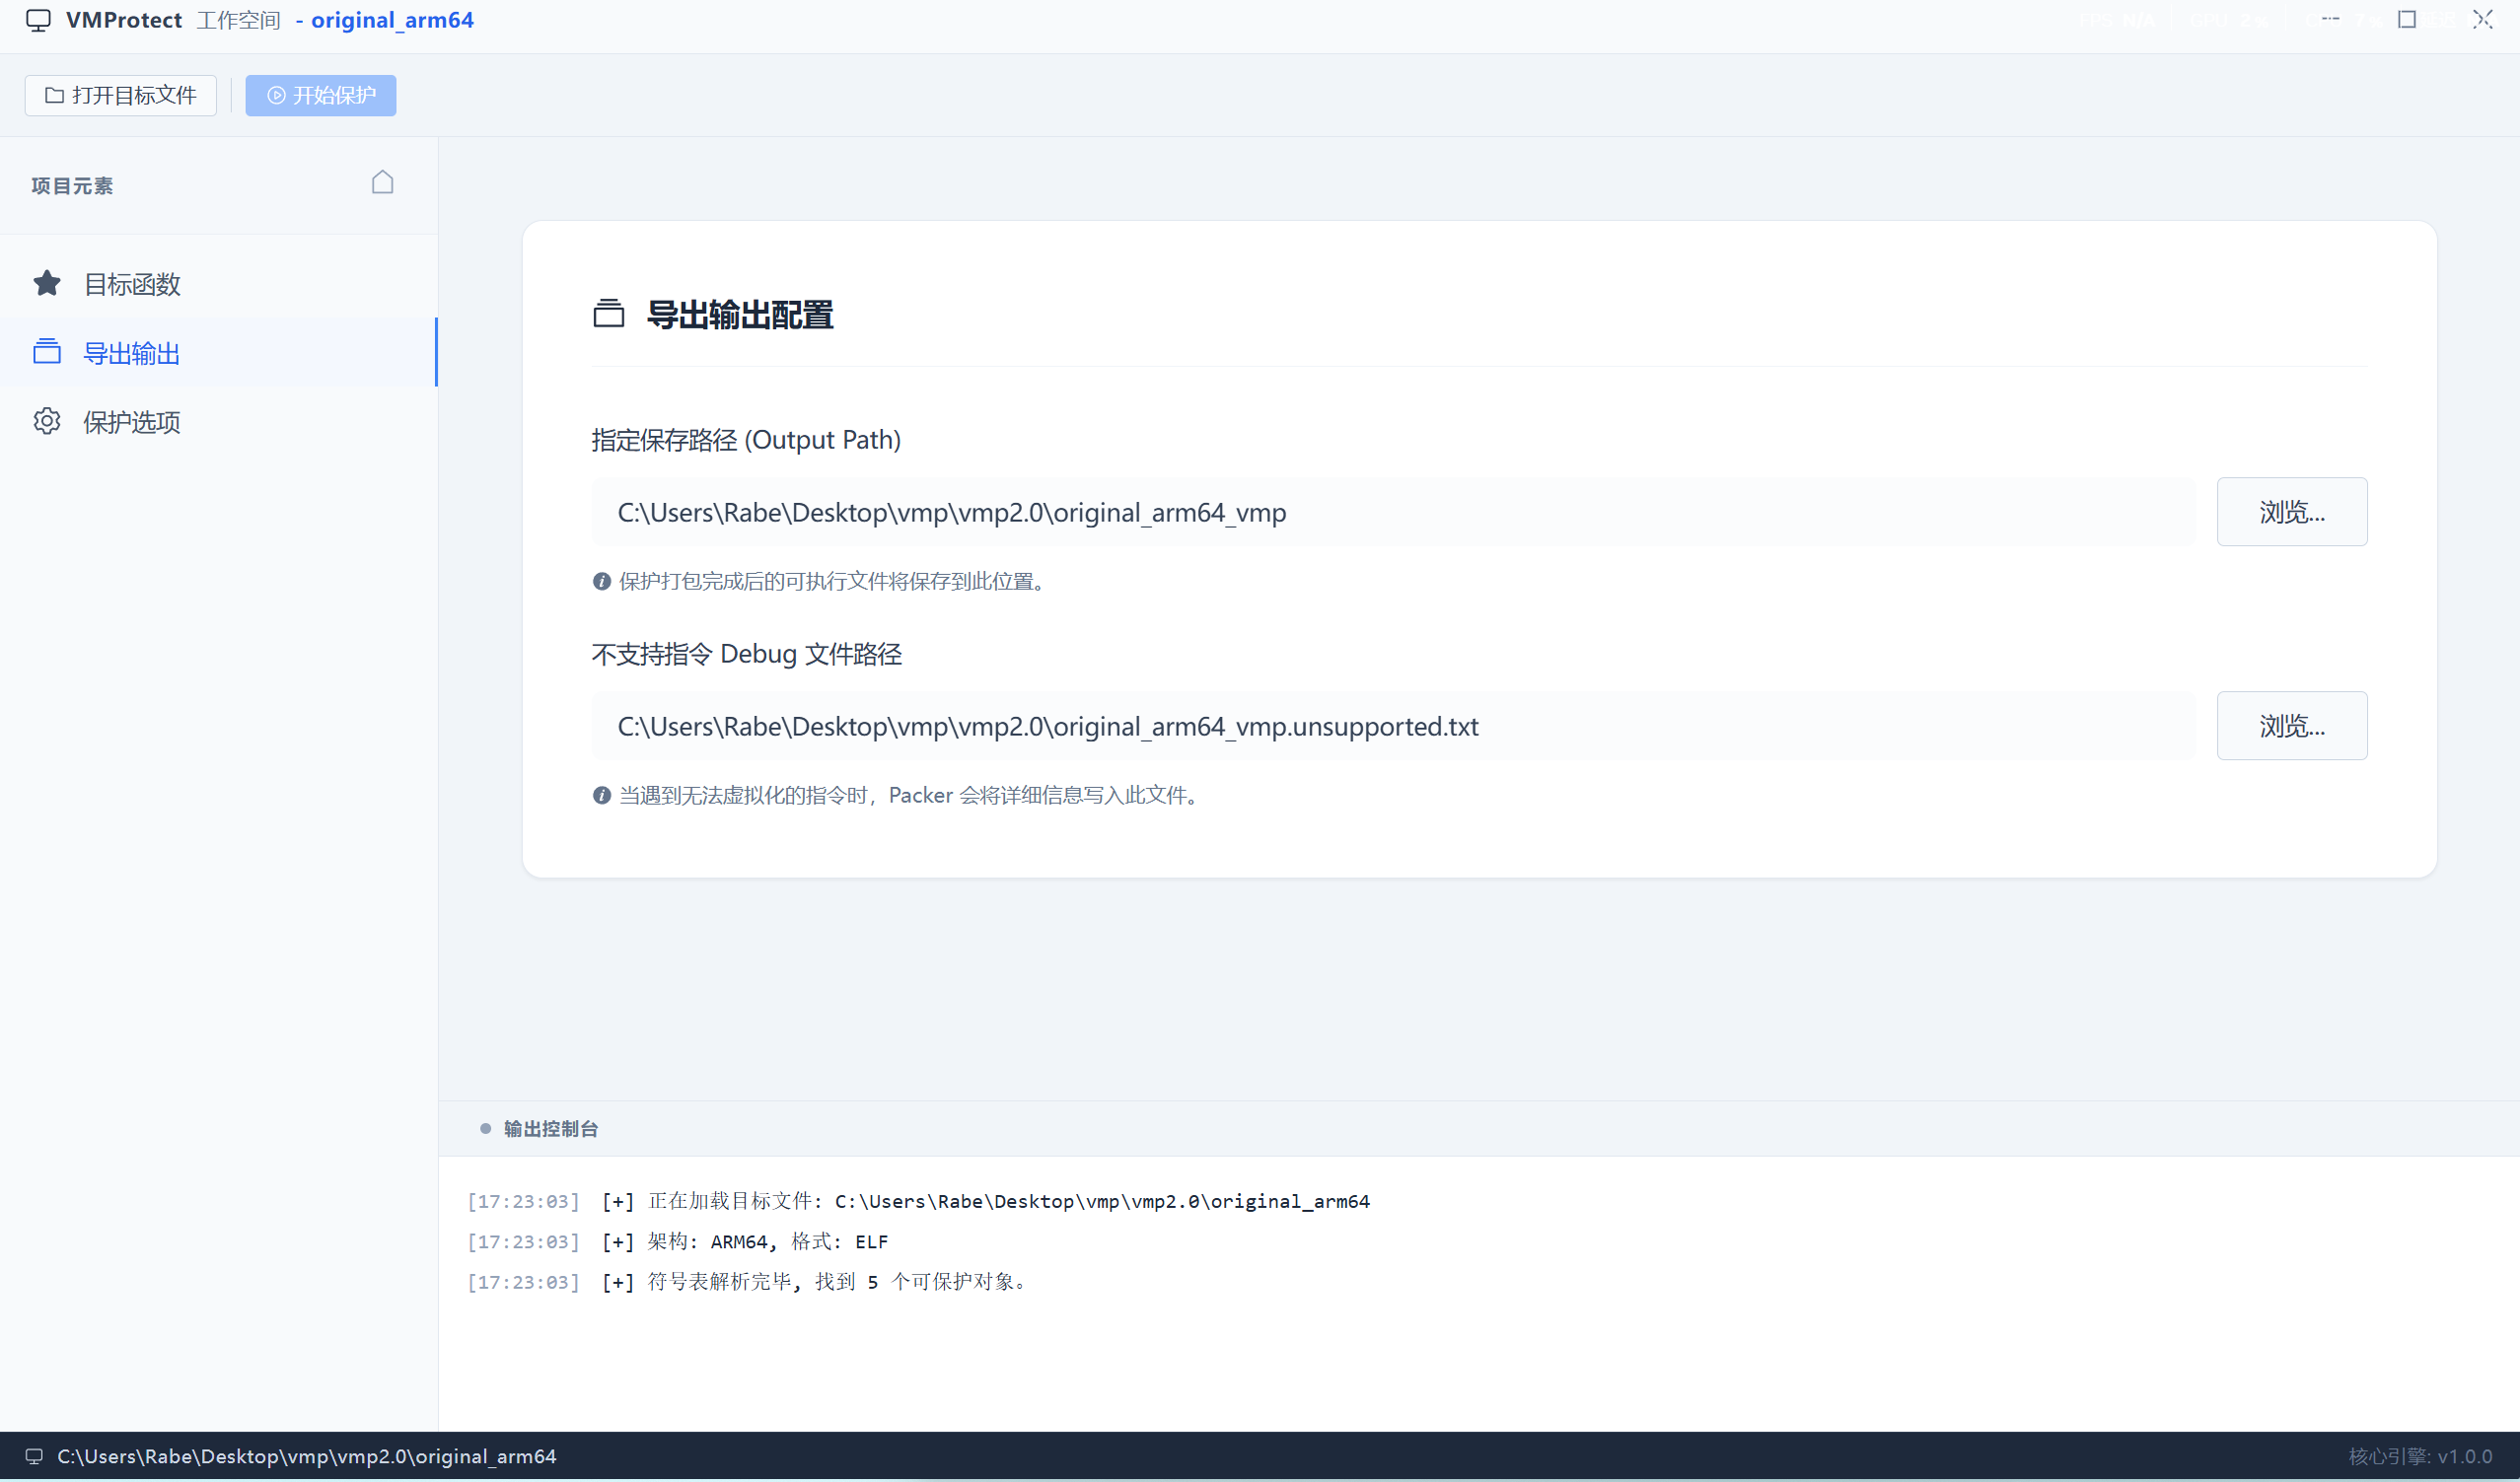 |
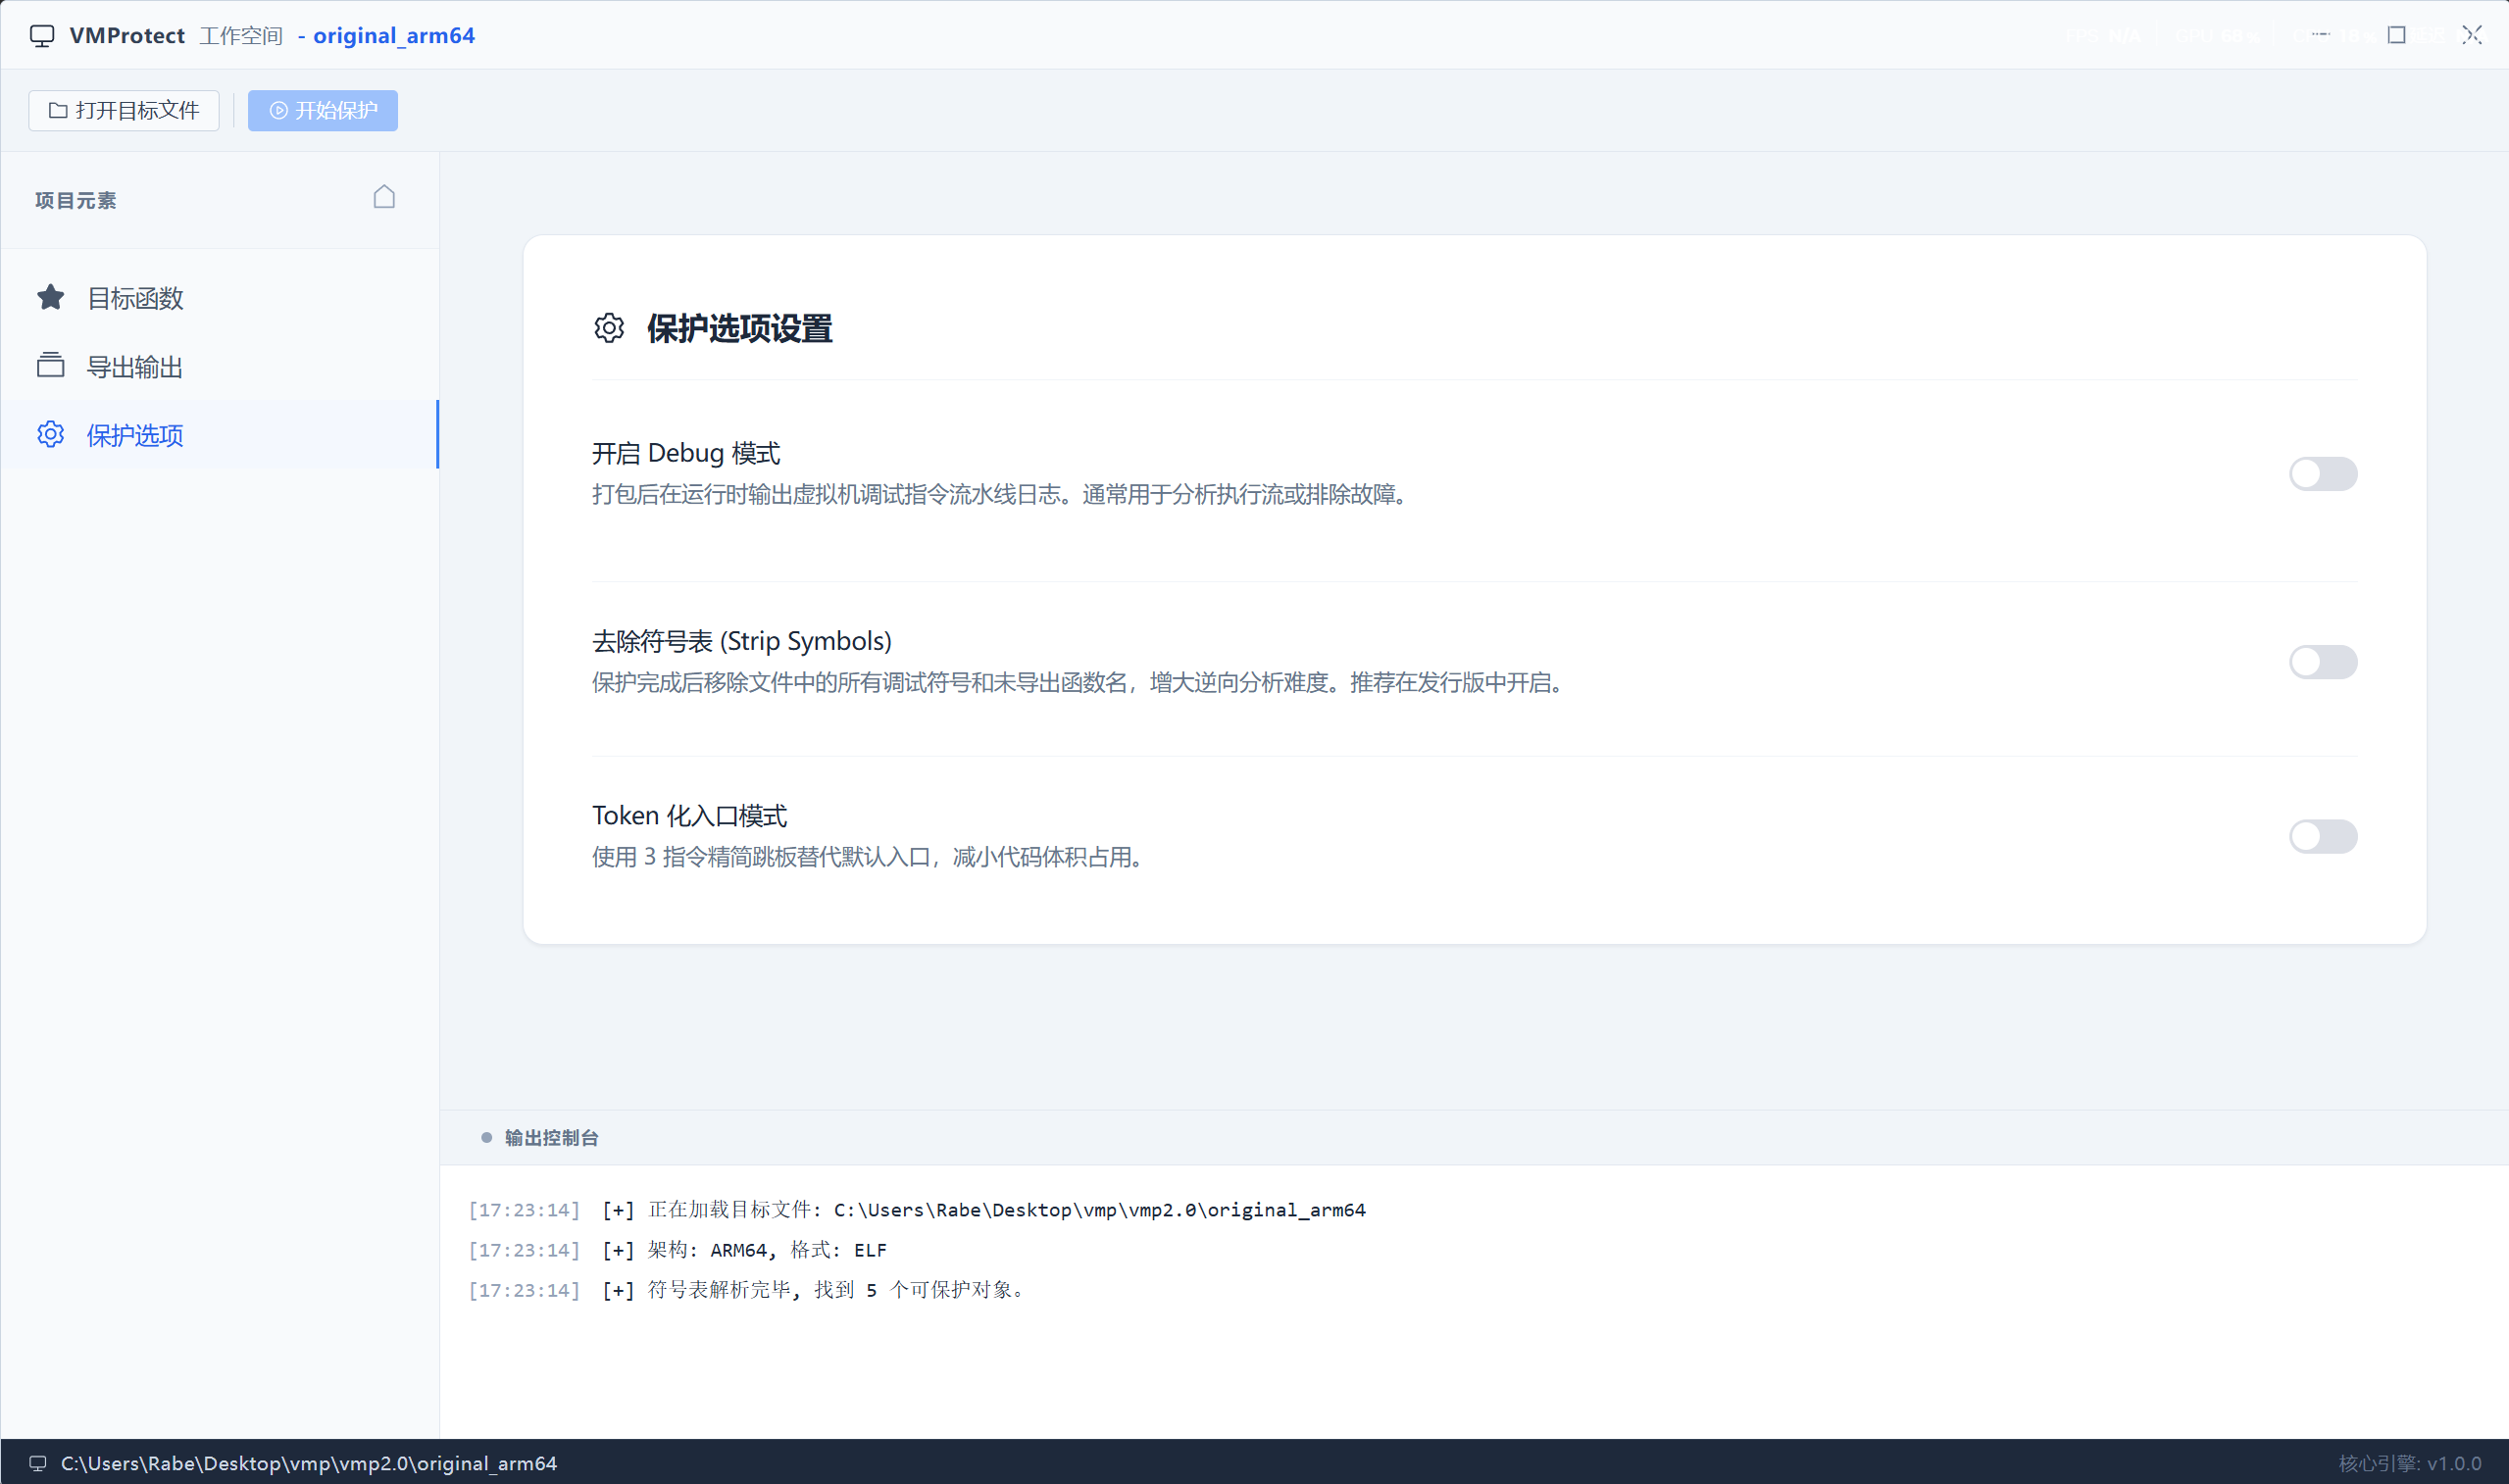 |
|
| Real-time Logs | Protection Complete |
vmp/
├── cmd/vmpacker/          # CLI entry point
│   ├── main.go            # CLI argument parsing + orchestration
│   └── vm_interp.bin      # Compiled VM interpreter (GCC, go:embed)
│
├── pkg/                   # Go core library
│   ├── arch/arm64/        # ARM64 architecture support
│   │   ├── decoder.go     # Table-driven instruction decoder (implements vm.Decoder)
│   │   ├── decode_*.go    # Decode pattern tables (DP-IMM/DP-REG/Branch/LdSt)
│   │   ├── translator.go  # ARM64 → VM bytecode translator
│   │   ├── tr_alu.go      # ALU instruction translation
│   │   ├── tr_branch.go   # Branch instruction translation
│   │   ├── tr_loadstore.go # Memory instruction translation
│   │   ├── tr_bitfield.go # Bitfield instruction translation
│   │   └── tr_special.go  # Special instructions (ADRP/ADR)
│   ├── vm/                # VM ISA definitions
│   │   ├── types.go       # Shared types + interfaces (Decoder/Translator/Packer)
│   │   ├── opcodes.go     # 58+ VM opcode definitions (randomly mapped values)
│   │   └── disasm.go      # VM bytecode disassembler
│   └── binary/elf/        # ELF binary manipulation
│       ├── packer.go      # ELF VMP injection (PT_NOTE hijack, trampoline generation)
│       └── trampoline.go  # Trampoline code generation
│
├── stub/                  # C VM interpreter (compiled to PIC flat binary)
│   ├── vm_interp_clean.c  # Interpreter main loop + entry points
│   ├── vm_types.h         # VM CPU context (vm_ctx_t)
│   ├── vm_opcodes.h       # C-side opcode definitions (synced with opcodes.go)
│   ├── vm_decode.h        # Bytecode read utilities
│   ├── vm_token.h         # Token encode/decode + descriptor table
│   ├── vm_dispatch.h      # Indirect dispatch jump table
│   ├── vm_crc.h           # CRC32 integrity check
│   ├── vm_sections.h      # Handler section scattering macros
│   ├── vm_interp.lds      # Linker script
│   └── vm_handlers/       # Modular instruction handlers
│       ├── h_alu.h        # Arithmetic/logic operations
│       ├── h_mem.h        # Memory access
│       ├── h_branch.h     # Branch/jump
│       ├── h_cmp.h        # Compare/conditional
│       ├── h_mov.h        # Data movement
│       ├── h_stack.h      # Stack (PUSH/POP)
│       └── h_system.h     # System (SVC/MRS/BLR/BR/RET)
│
├── vmp-gui/               # Wails GUI frontend
│   ├── frontend/          # Vue 3 + Element Plus
│   └── backend/           # Go backend bindings
│
└── build/                 # Pre-compiled tools + test artifacts
The project uses an interface-driven modular architecture, making it easy to extend to new ISAs and binary formats:
// Architecture decoder interface — extensible to x86, RISC-V
type Decoder interface {
    Decode(raw uint32, offset int) Instruction
    InstName(op int) string
}

// Bytecode translator interface
type Translator interface {
    Translate(instructions []Instruction) (*TranslateResult, error)
}

// Binary format injector interface — extensible to PE, Mach-O
type Packer interface {
    Process() error
}
graph LR
    A[Input ELF] --> B[Locate Target Function]
    B --> C[Extract ARM64 Instructions]
    C --> D[Decode ARM64]
    D --> E[Translate to VM Bytecode]
    E --> F[XOR Encrypt Bytecode]
    F --> G[Inject VM Interpreter]
    G --> H[Generate Trampoline]
    H --> I[Replace Function Entry]
    I --> J[Output Protected ELF]
