
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 withsecureopensource/see
Sandboxed Execution Environment
 taviso/avscript
Avast JavaScript Interactive Shell
 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
 a-yatta/amdh
Android Mobile Device Hardening
 heathen42/ctf
Curated collection of CTF challenge solutions covering binary exploitation, reverse engineering, and system security with detailed write-ups.
 commit-regrets/samsung_tizen_tv_root
Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…
 vahpem/rust-deobf
Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
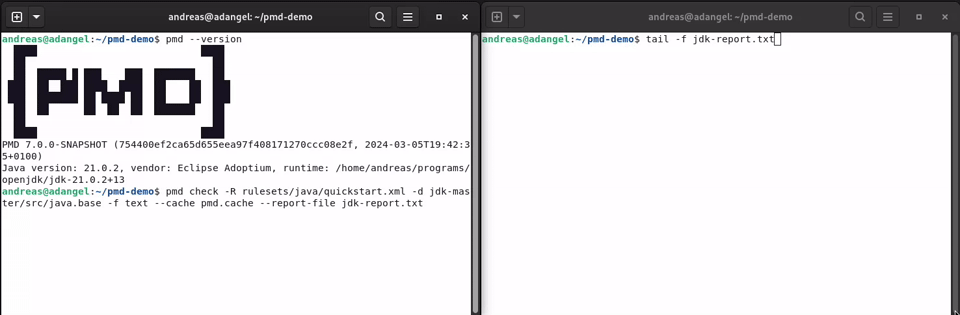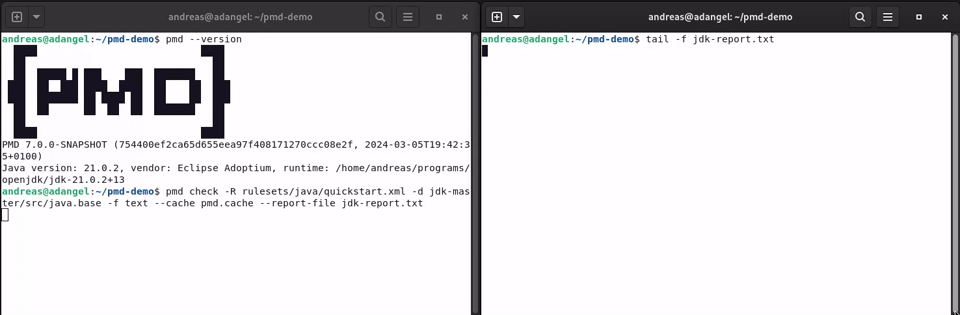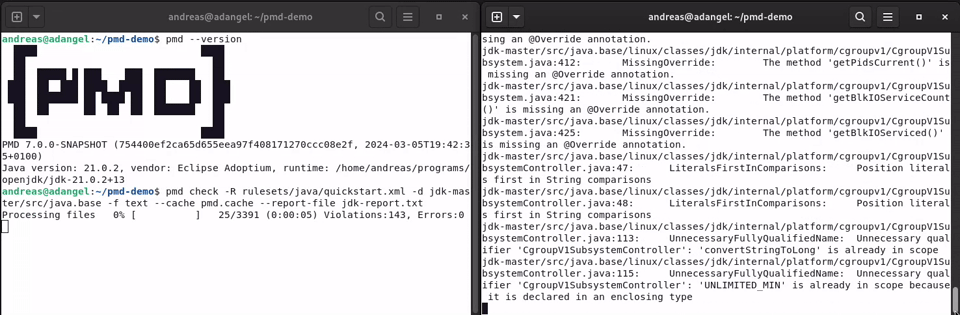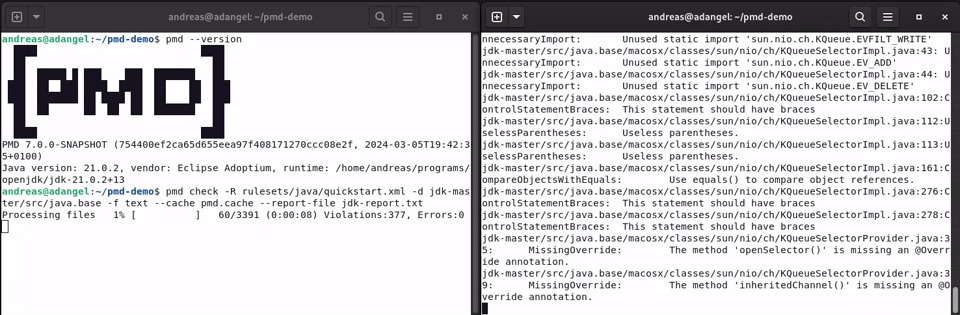 pmd/pmd
An extensible multilanguage static code analyzer.
 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 malwarecantfly/vba2graph
Vba2Graph - Generate call graphs from VBA code, for easier analysis of malicious documents.
 monkeylord/xposedfridabridge
A frida script implement XposedBridge & load xposed modules, without installing xposed framwork.








