

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CrackMeZ3S-CTF-CrackMe-Tutorial — How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks. | Kitploit
Tools/GitHubGitHub/pelock/crackmez3s-ctf-crackme-tutorial
ExploitationReverse EngineeringCTFBinary AnalysisLearning & Education
GitHubpelock/crackmez3s-ctf-crackme-tutorial

CrackMeZ3S-CTF-CrackMe-Tutorial

How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.

View Repository
Website
4812953 years agoReviewed by Kitploit
Share

How to write a CrackMe for a CTF competition

With the growing popularity of CTF (capture the flag) competitions, and the excellent performance of Polish teams like Dragon Sector in this area, I thought it would be interesting to demonstrate the construction of a simple CrackMe, using some creative techniques which make it difficult to crack and analyse.
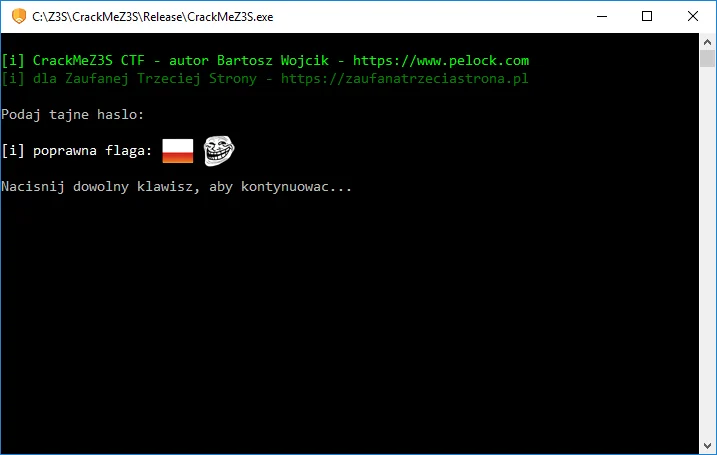
Can you find the flag?

If you have ever been curious about reverse engineering, entered a CTF competition, or wanted to create your own CrackMe and drive other contestants crazy, this is for you.

Full article in English

You can find an article about the crackme with detailed technical description and source code commentary (in english) at:

https://www.pelock.com/articles/how-to-write-a-crackme-for-a-ctf-competition

Original article in polish for Zaufana Trzecia Strona site

https://zaufanatrzeciastrona.pl/post/jak-napisac-ciekawe-crackme-na-ctf-instrukcja-krok-po-kroku/

Compiled CrackMe

If you already have some reversing skills, and would like to try your hand at the CrackMe I am about to describe in detail, put this article aside, get the compiled executable, and try to find the flag!
Listen to Mr Burns

Once you've made your best attempt at it, you can come back to the article and compare what you discovered against the full story. This CrackMe has a medium level of difficulty.

https://www.pelock.com/download/CrackMeZ3S.zip

To run the CrackMe executable you may need the Visual C++ Redistributable Packages for Visual Studio 2013.

Got the CrackMe? Don't cheat by reading any further - get cracking! ;)

Otherwise, if you want to learn how to build your own CrackMe, I invite you to keep reading...

Bartosz Wójcik

  • Visit my site at — https://www.pelock.com
  • Twitter — https://twitter.com/PELock
  • GitHub — https://github.com/PELock
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    867
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    544
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    385
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    302
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    279

Explore all tools

Browse our collection of tools

View all tools →





