
 #1
Binary reverse engineering, disassembly, decompilation, and patching tools.
Kitploit recommended
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 michalmalik/osx-re-101
A collection of resources for OSX/iOS reverse engineering.
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
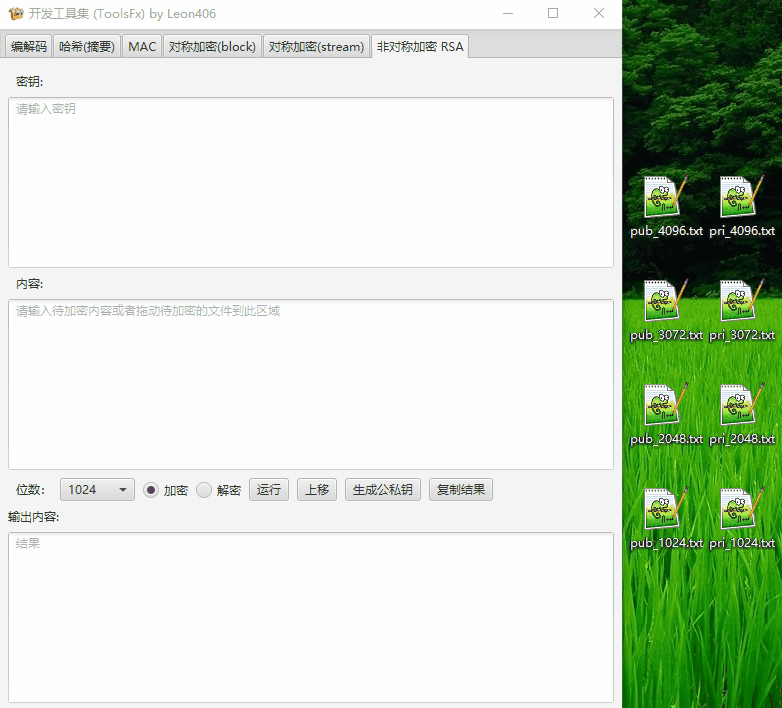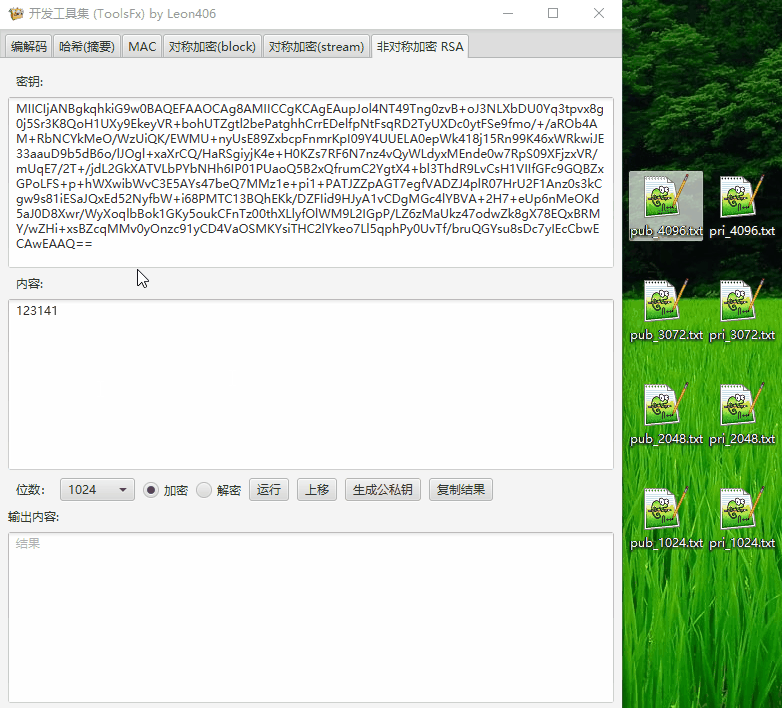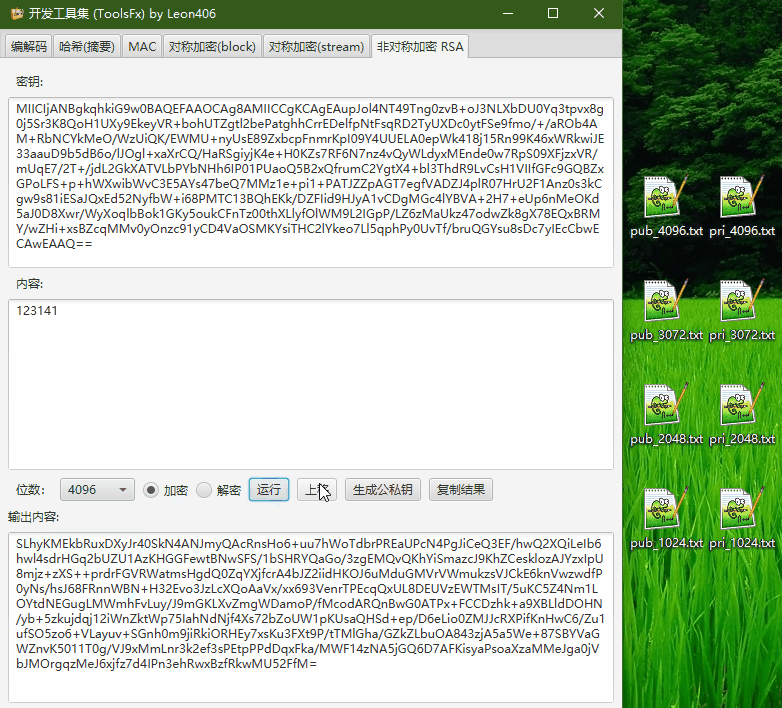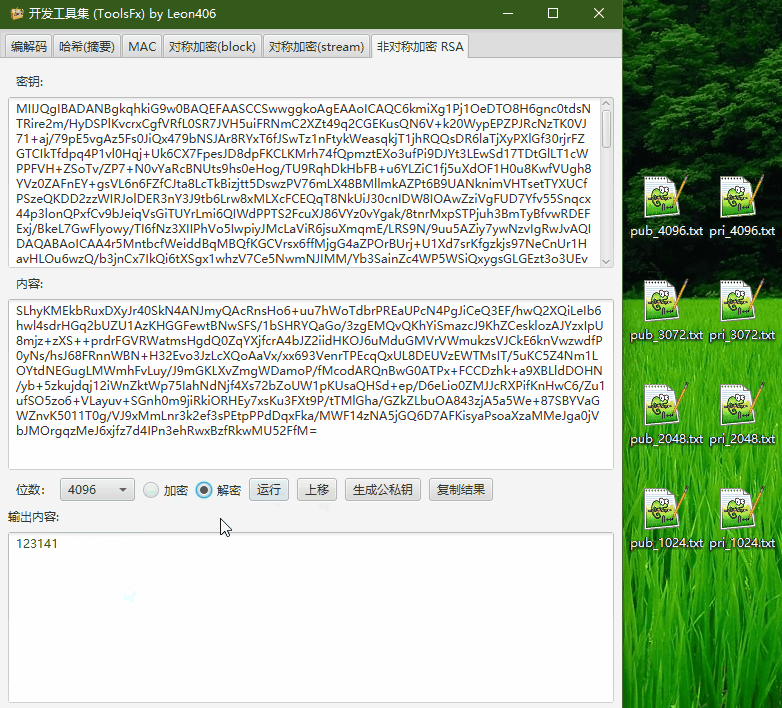 leon406/toolsfx
跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 fr0gger/awesome-ida-x64-olly-plugin
A curated list of IDA x64DBG, Ghidra and OllyDBG plugins.
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…








