#1
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 lauriewired/malimite
iOS and macOS Decompiler
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
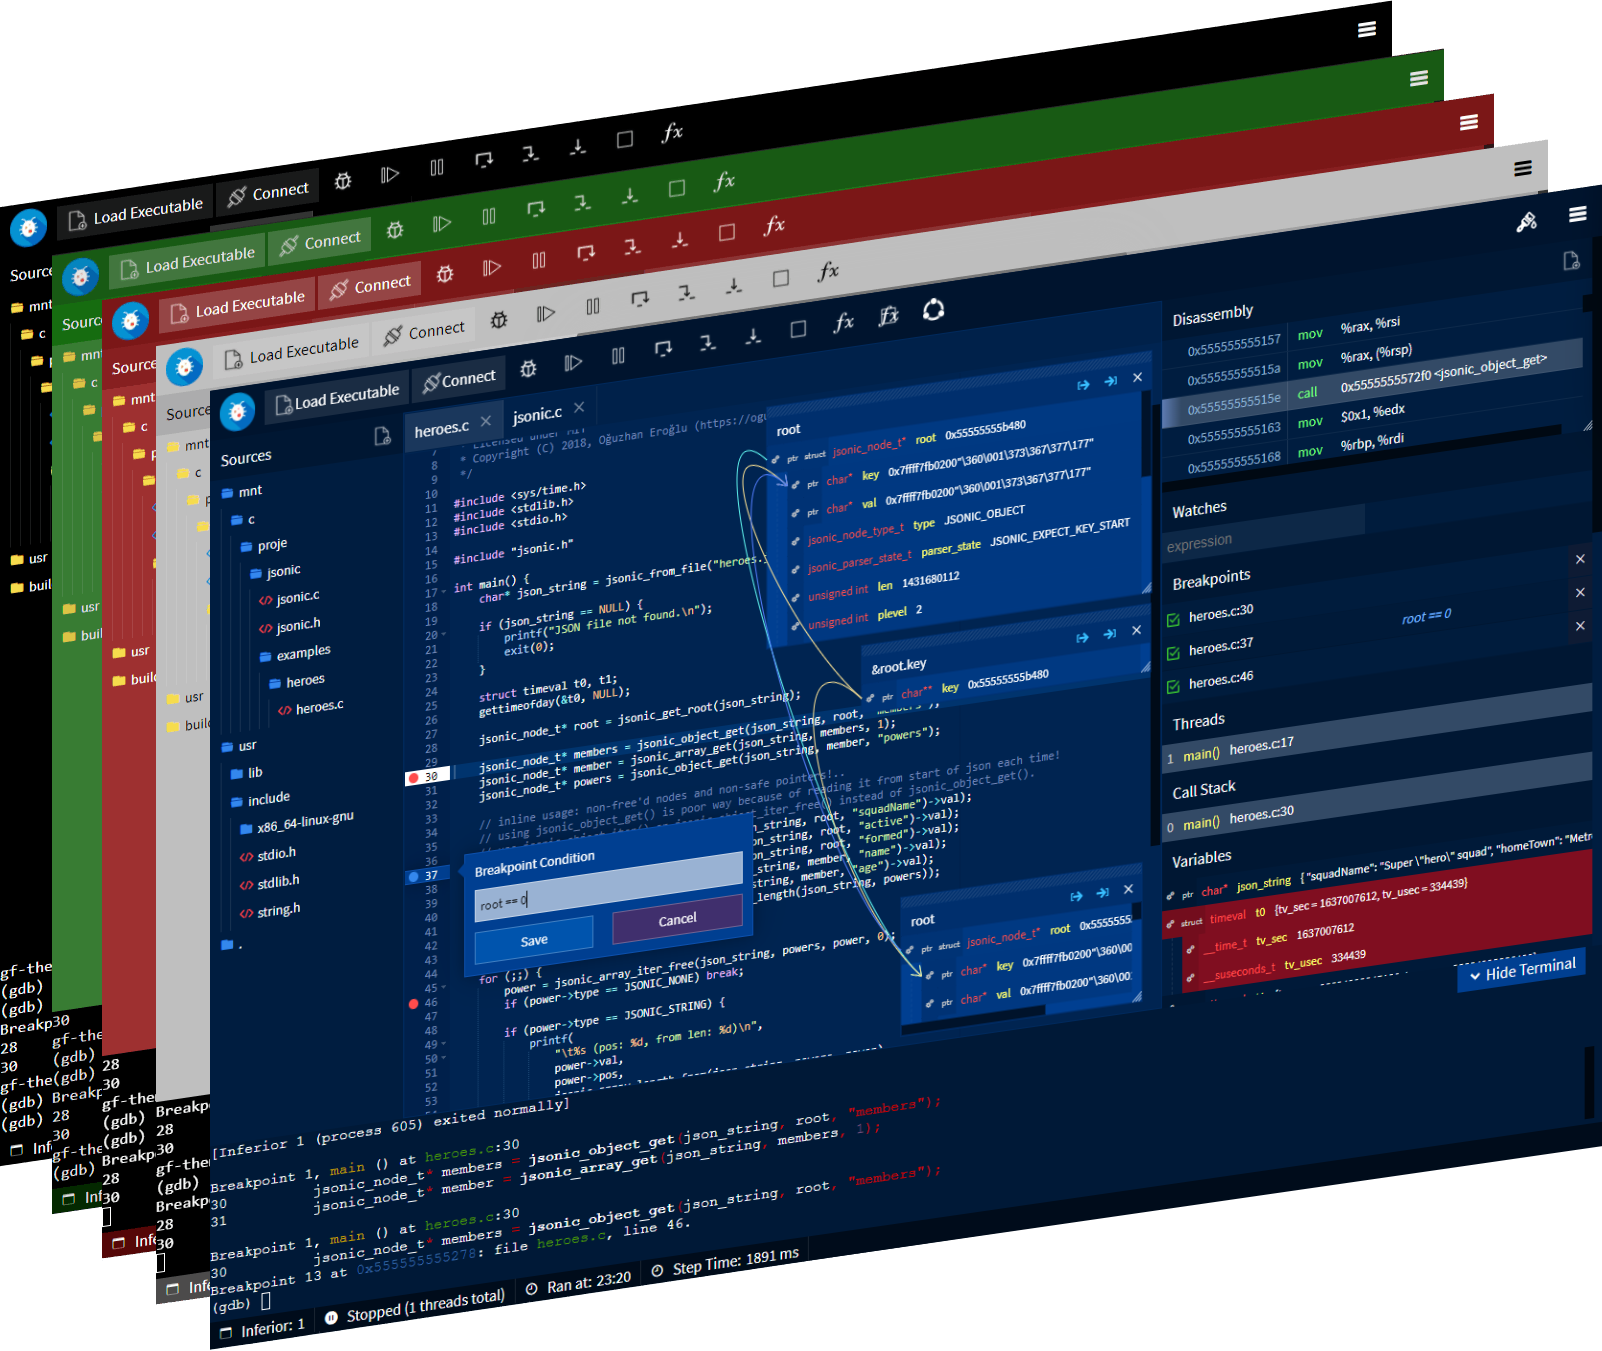 rohanrhu/gdb-frontend
☕ GDBFrontend is an easy, flexible and extensible gui debugger.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
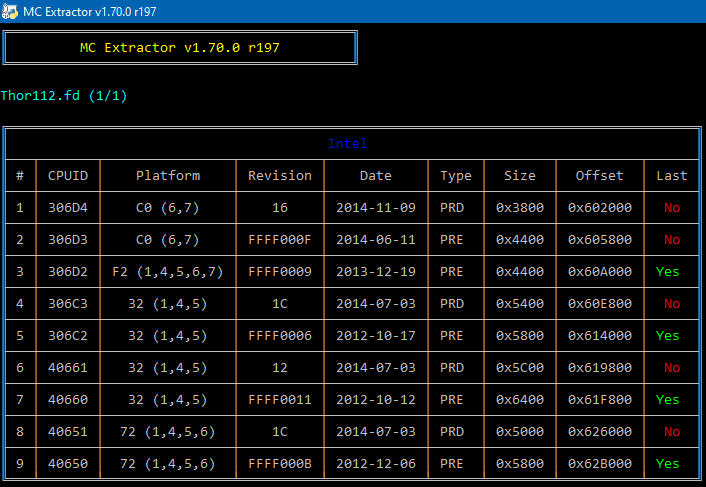 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
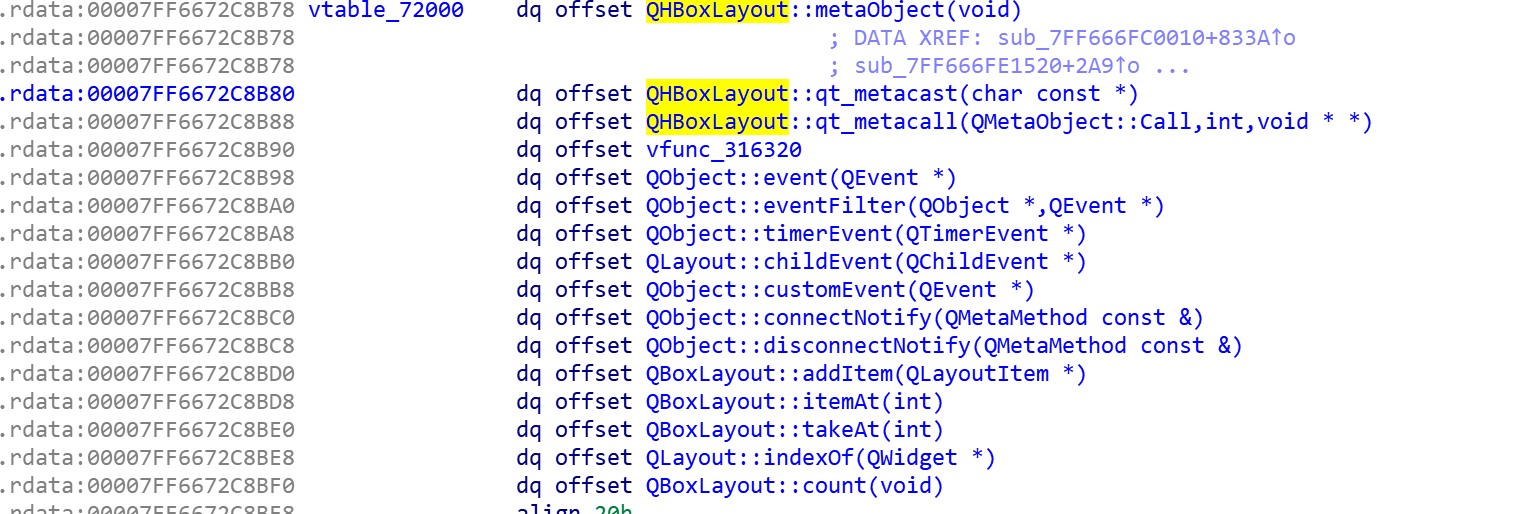 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…
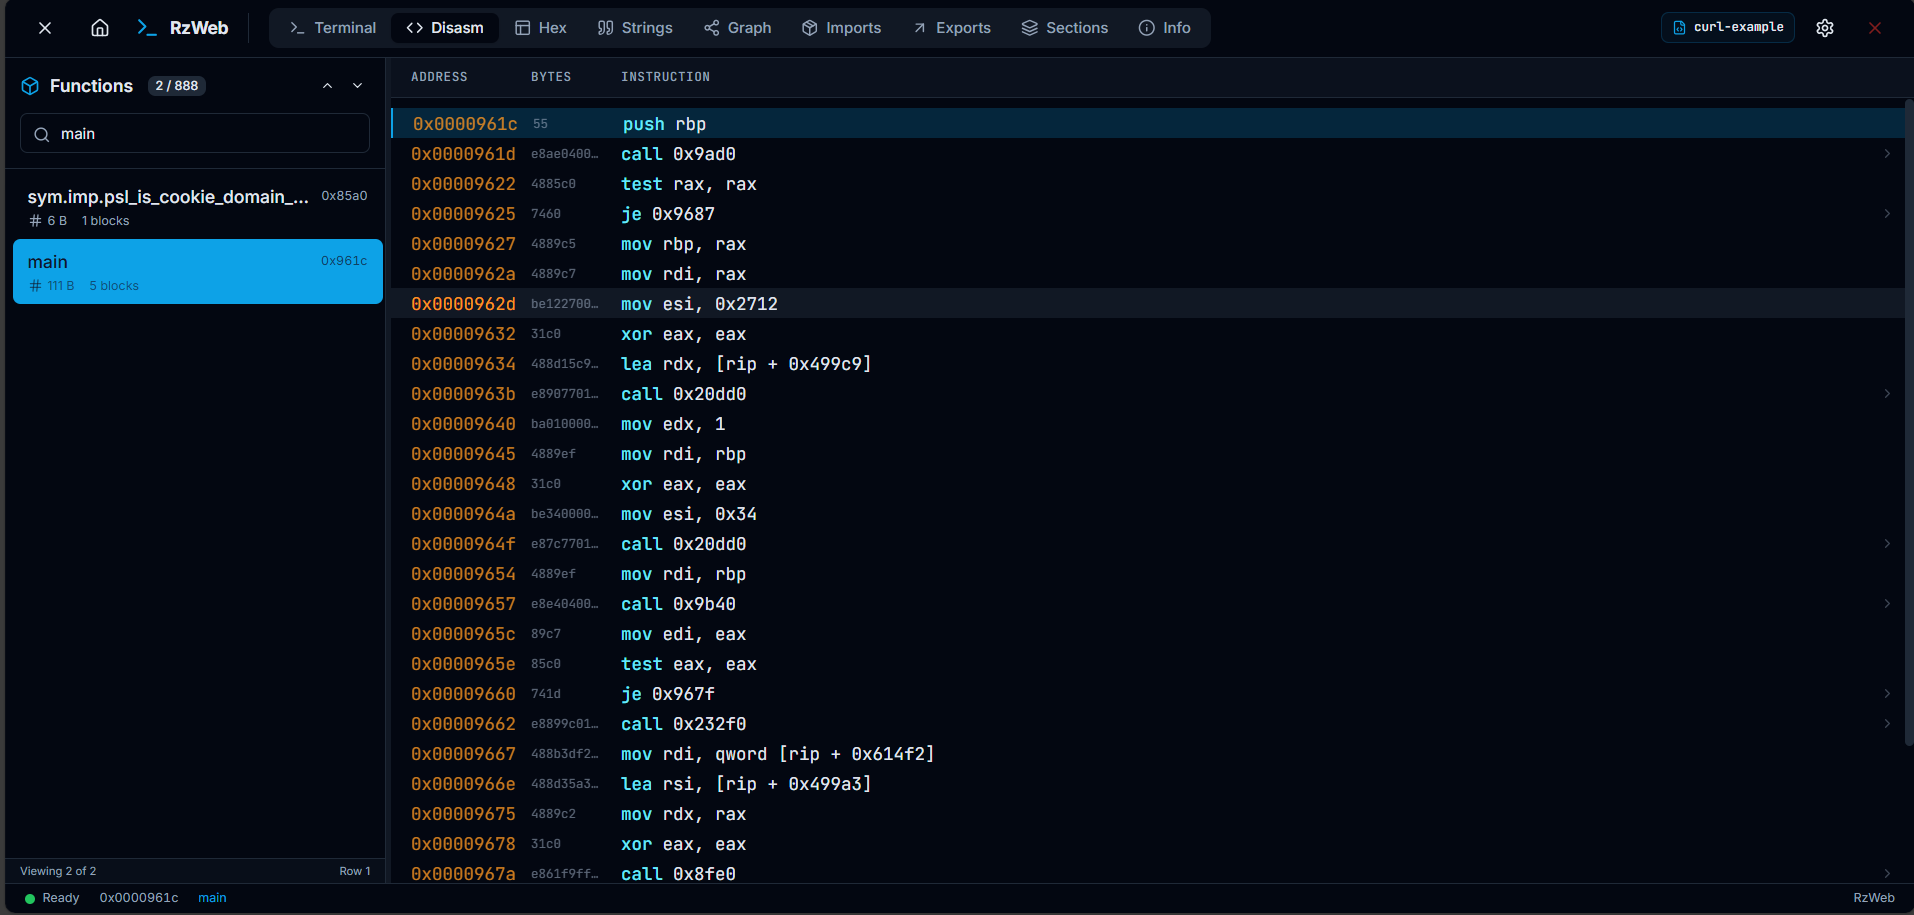 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…